
 #1
Automated tools for detecting known vulnerabilities in systems and applications.
Kitploit recommended
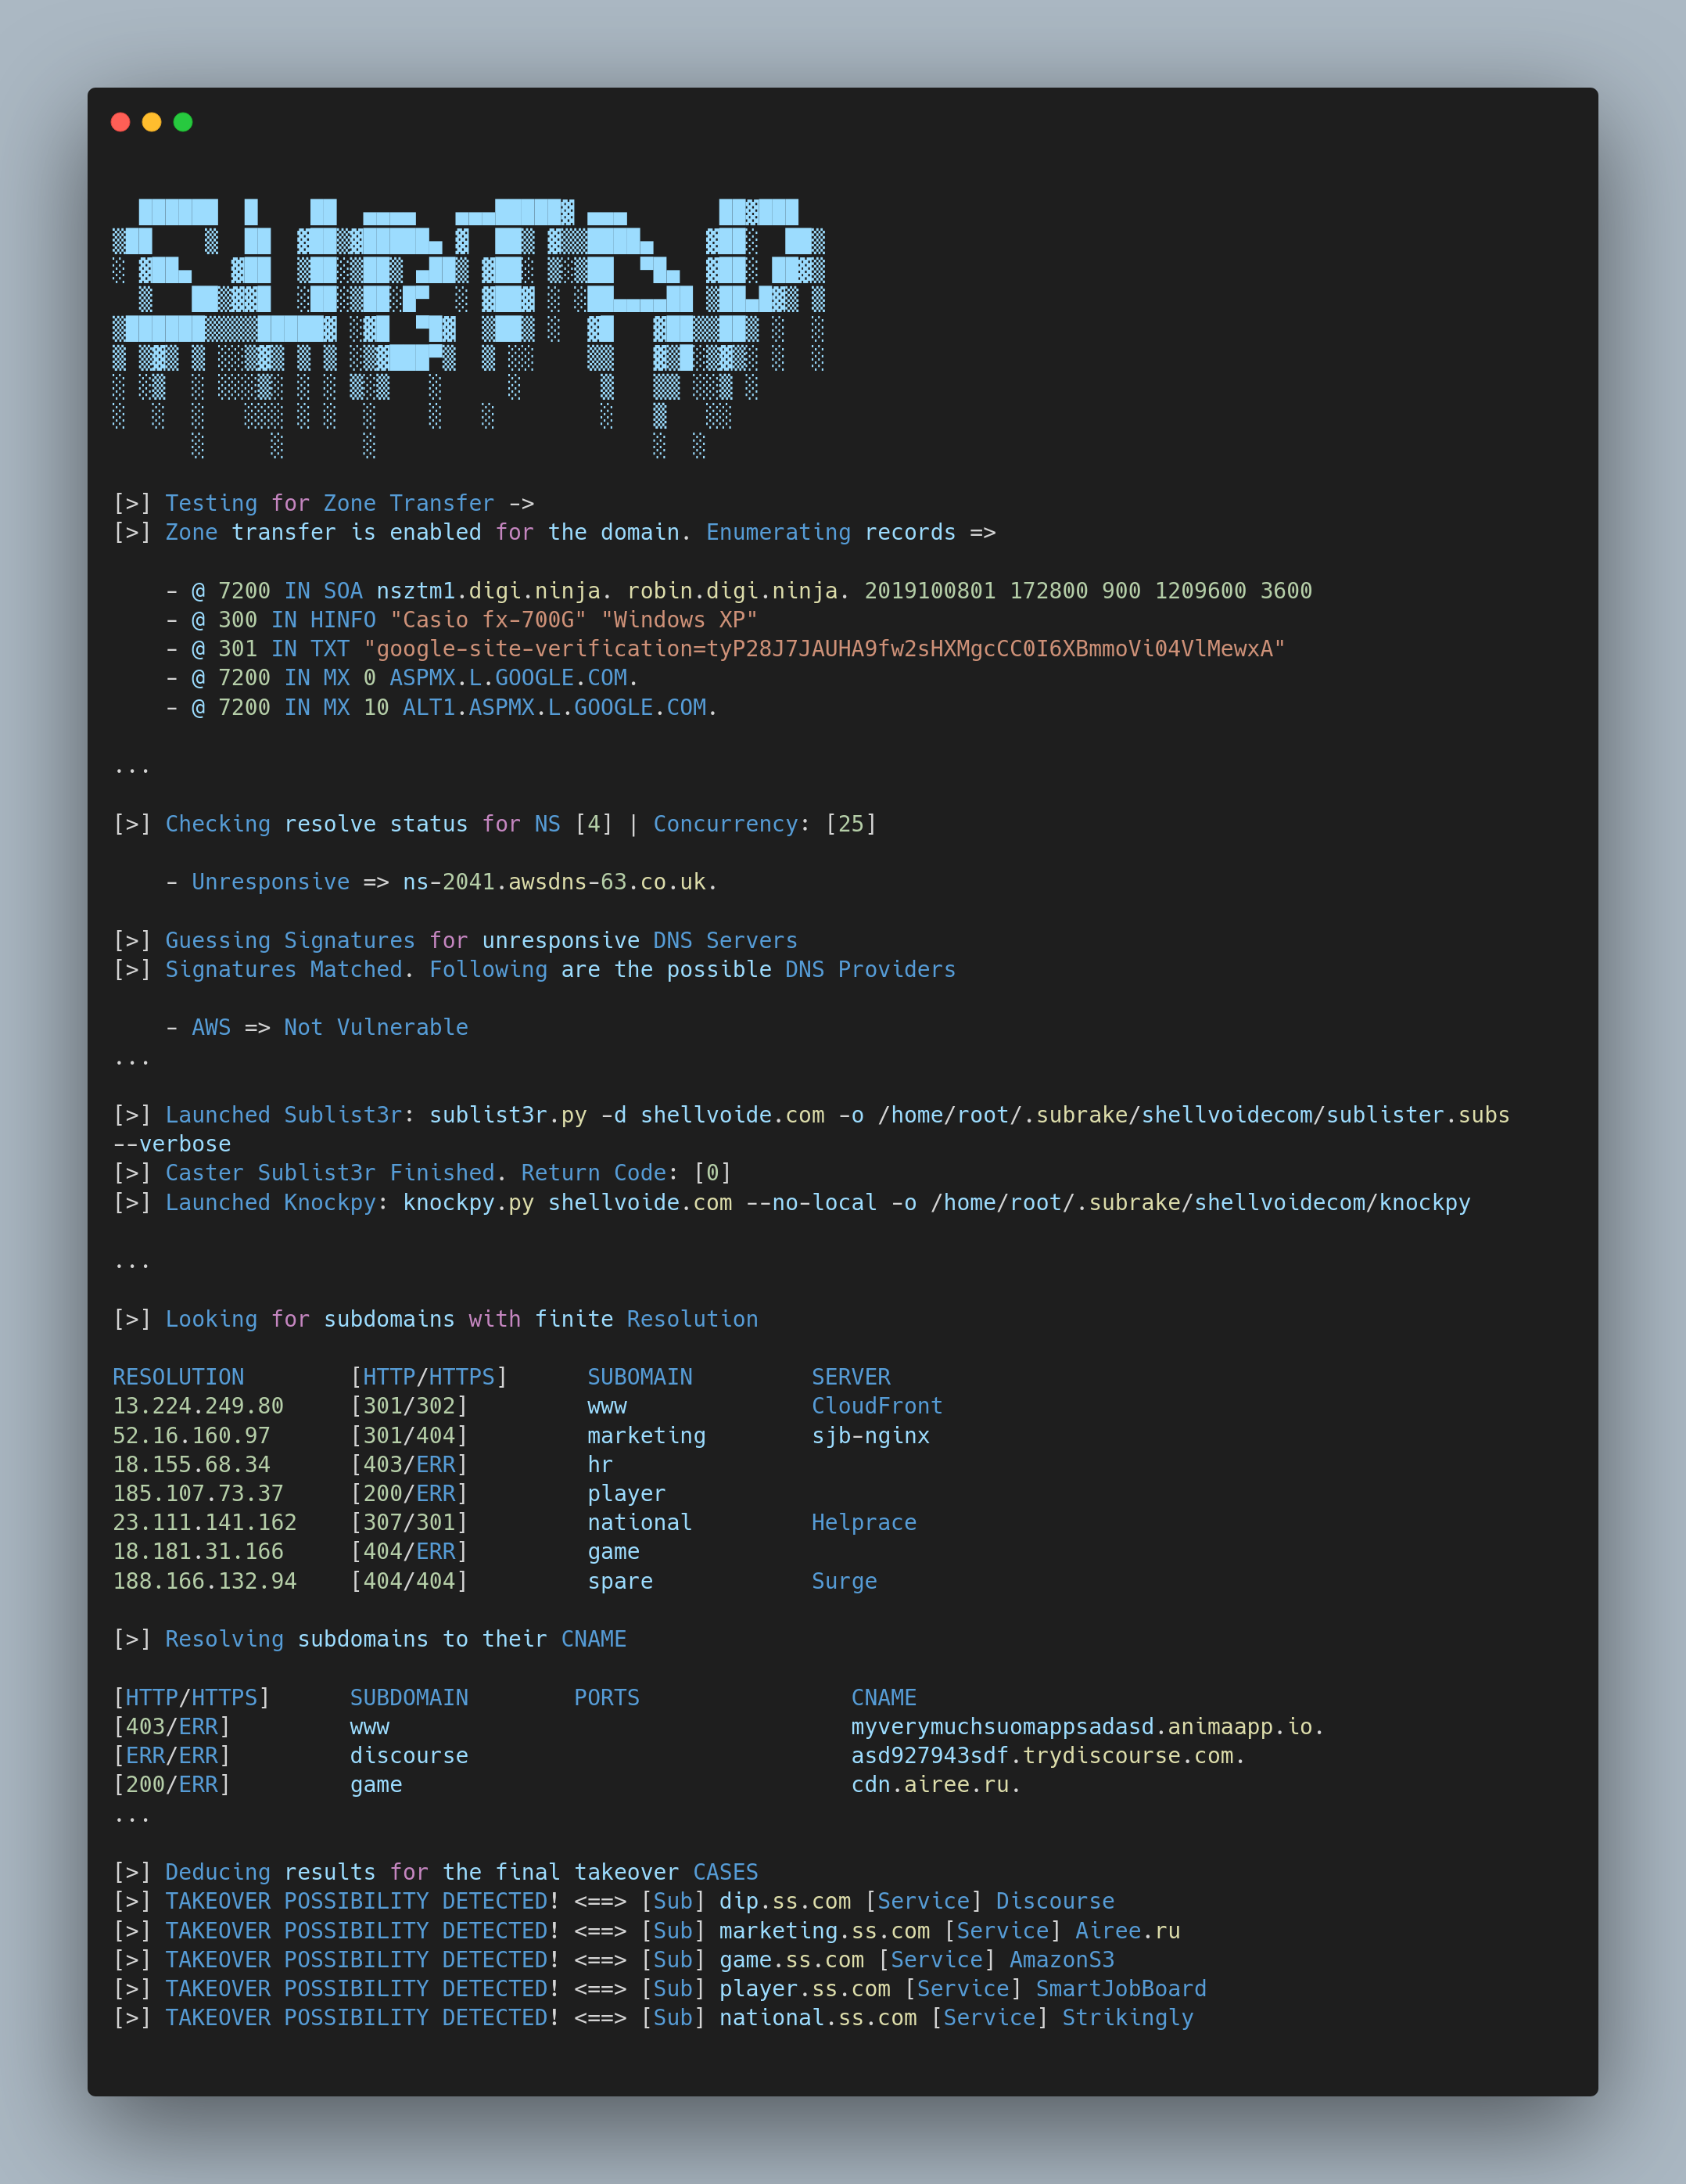
 hash3lizer/subrake
🚀 A DNS automated scanner and tool 🖱️ (Zone Transfer, DNS Zone Takeover, Subdomain Takeover).
 cckuailong/pocsploit
a lightweight, flexible and novel open source poc verification framework
 postmodern/ruby-nmap
A Ruby interface to nmap, the exploration tool and security / port scanner. Allows automating nmap and parsing nmap XML files.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 rapiddns/afuzz
Automated web path fuzzing tool that detects hidden directories, files, and endpoints using intelligent language detection, blacklist/whitelist…
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…
 rxerium/rxerium-templates
Nuclei scripts created by @rxerium for zero days / actively exploited vulnerabilities.
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
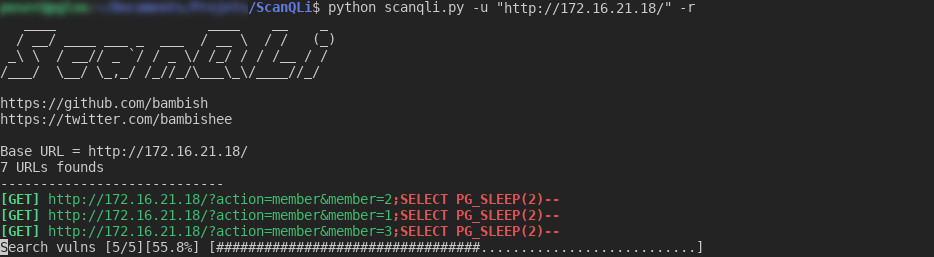 bambish/scanqli
SQLi scanner to detect SQL vulns
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
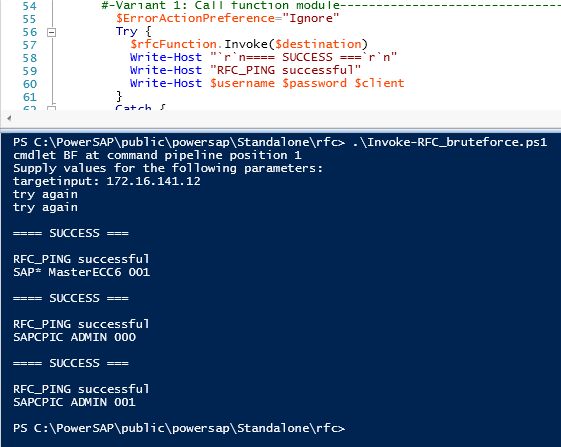 airbus-seclab/powersap
Powershell SAP assessment tool
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 sensepost/heartbleed-poc
Test for SSL heartbeat vulnerability (CVE-2014-0160)
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 karmakstylez/cve-2024-6387
Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387)
 botherder/kraken
Cross-platform Yara scanner written in Go
 preempt/ntlm-scanner
A simple python tool based on Impacket that tests servers for various known NTLM vulnerabilities








