
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended

 kh4sh3i/cve-2025-32463
Local Privilege Escalation to Root via Sudo chroot in Linux
 koczkatamas/cve-2016-0051
EoP (Win7) & BSoD (Win10) PoC for CVE-2016-0051 (MS-016)
 devops-kung-fu/bomber
Scans Software Bill of Materials (SBOMs) for security vulnerabilities
 hightechsec/git-scanner
A tool for bug hunting or pentesting for targeting websites that have open .git repositories available in public
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
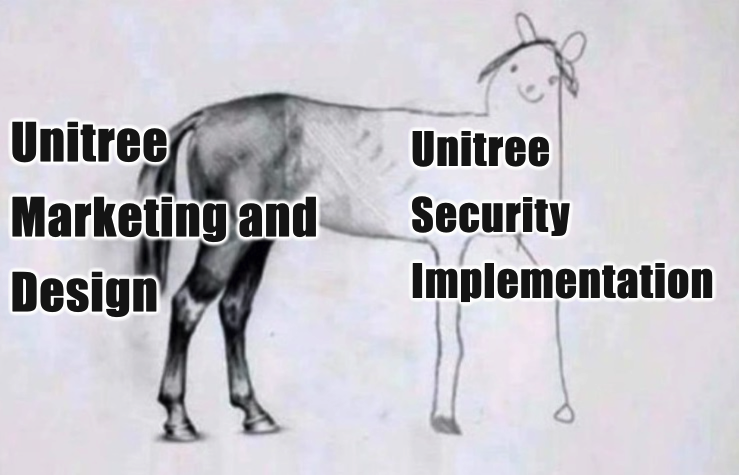 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 edwardzpeng/presentations
Slides and conference talks from security research covering Windows, virtualization, web, and blockchain exploit techniques, presented at Black Hat,…
 anlominus/bug-bounty
Bug Bounty ~ Awesomes | Books | Cheatsheets | Checklists | Tools | Wordlists | More
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 jimywork/djangohunter
Tool designed to help identify incorrectly configured Django applications that are exposing sensitive information.
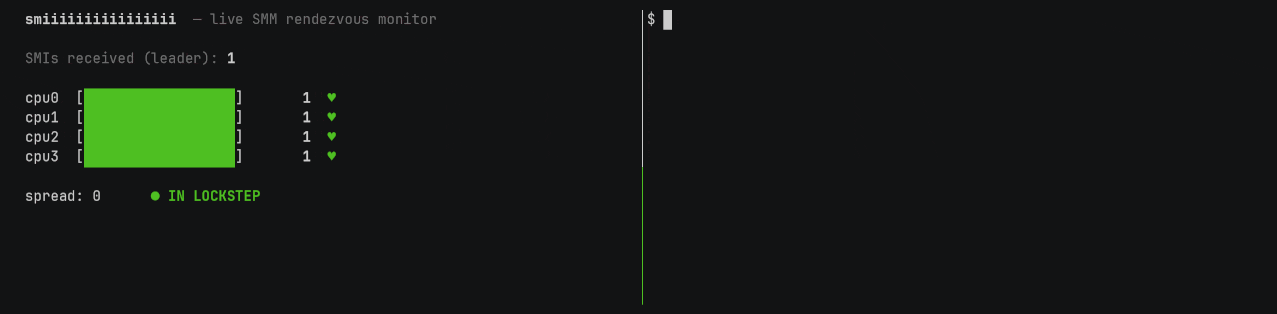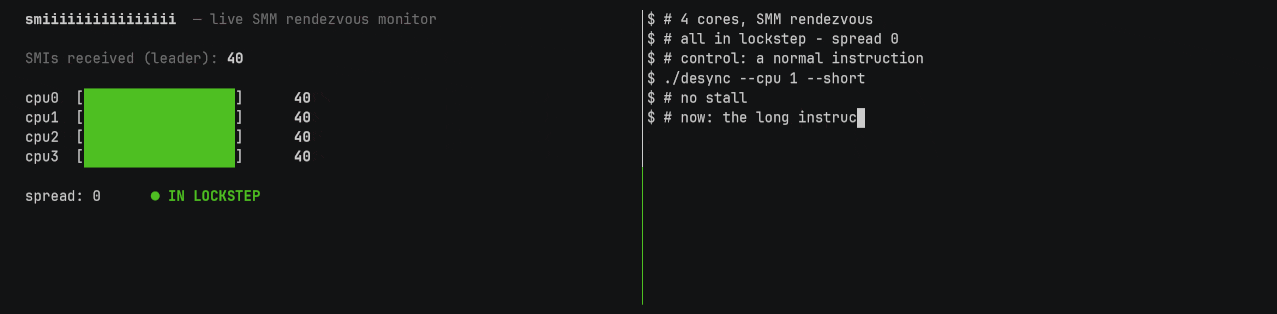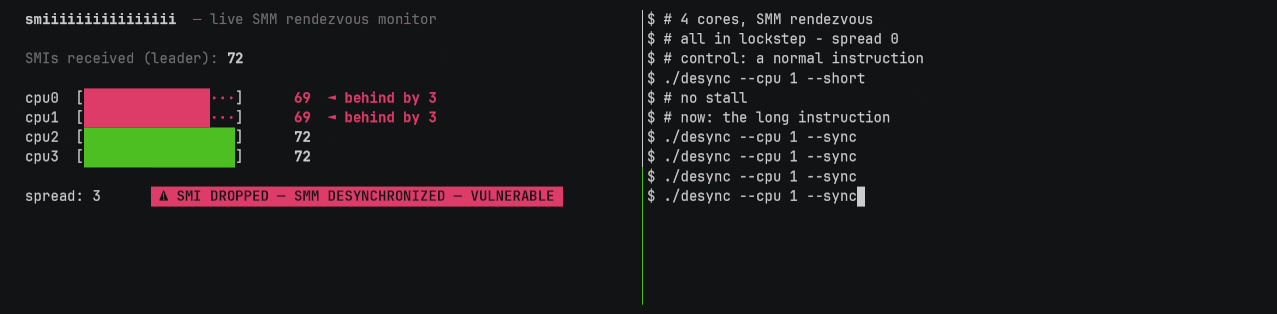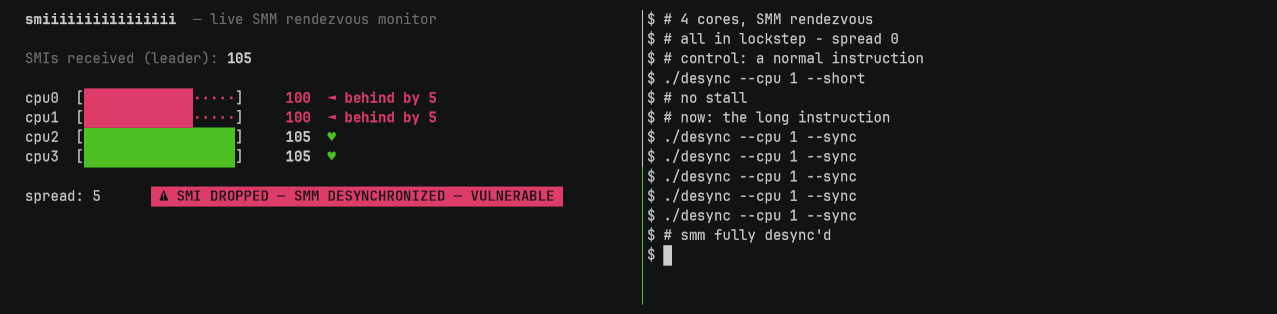 xoreaxeaxeax/smiiiiiiiiiiiiiiii
A very very very very very very very long interrupt
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 bdenneu/cve-2022-33679
One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 notsosecure/blacklist3r
Audits ASP.NET applications for pre-published machine keys to detect ViewState deserialization vulnerabilities and insecure forms authentication…
 odomojuli/regextokens
list of regex patterns for oauth / api tokens with provided source
 lekensteyn/pacemaker
Heartbleed (CVE-2014-0160) client exploit
 yunuscadirci/callstranger
Vulnerability checker for Callstranger (CVE-2020-12695)








