
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 outflanknl/wdtoggle
A Beacon Object File (BOF) for Cobalt Strike which uses direct system calls to enable WDigest credential caching.
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 prime-radiant-inc/superpowers-evals
Behavioral eval lab (Quorum) for the superpowers project that drives real coding-agent CLIs (Claude, Codex, Gemini, Kimi, and more) through a QA…
 snovvcrash/divideandscan
Divide full port scan results and use it for targeted Nmap runs
 penberg/chimera
Sandbox untrusted code with safe access to the host.
 trustedsec/the_shelf
Retired TrustedSec Capabilities
 joshuakasa/van-gonography
Hide 🕵️♂️ your files of any type inside a image of your choice using steganography
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 besser82/libxcrypt
Extended crypt library for descrypt, md5crypt, bcrypt, and others
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 usbarmory/gotee
Go Trusted Execution Environment (TEE)
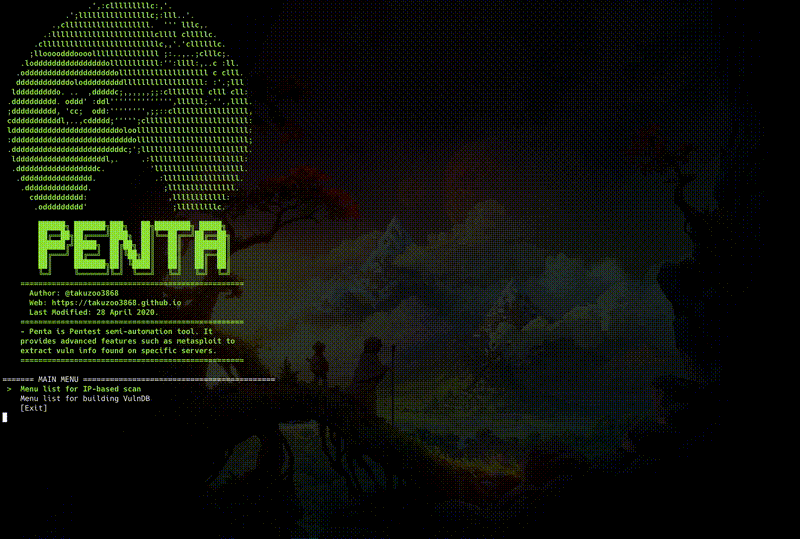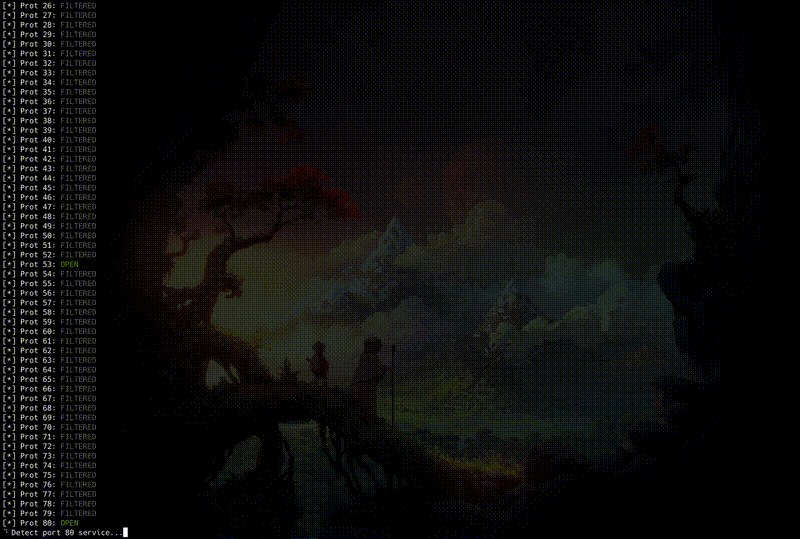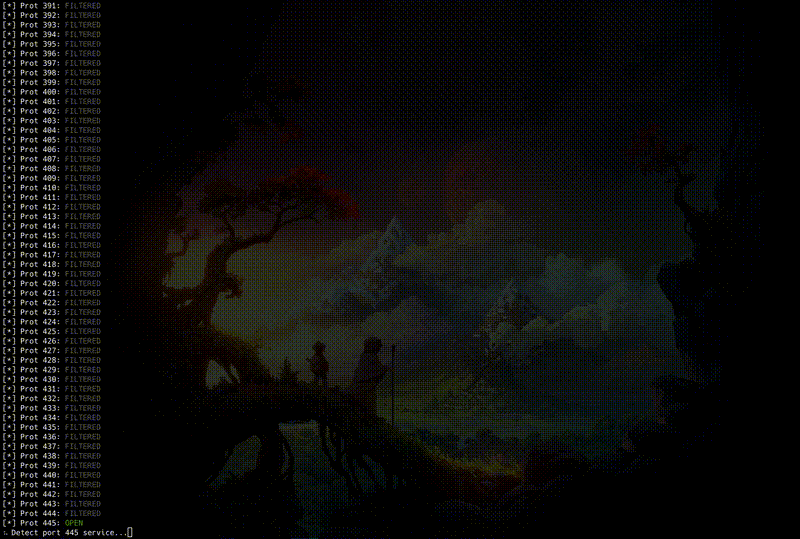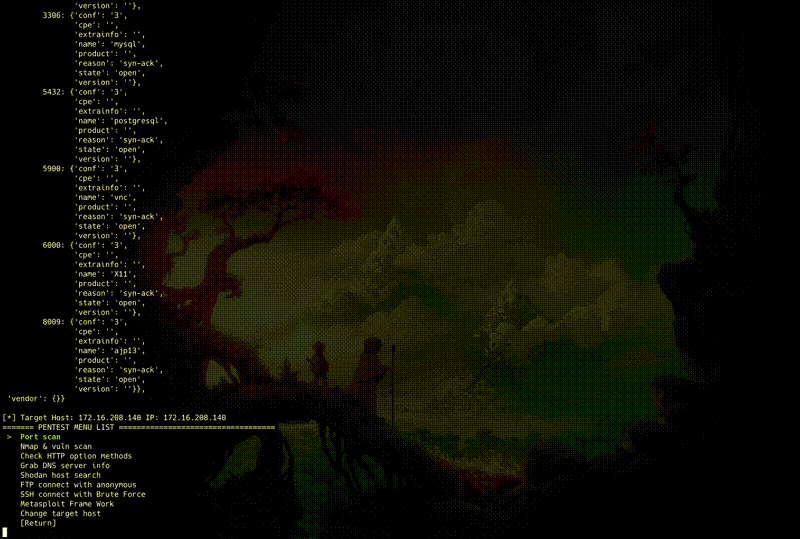 takuzoo3868/penta
Open source all-in-one CLI tool to semi-automate pentesting.
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…

 justmao945/mallory
HTTP/HTTPS proxy over SSH








