
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 industri4l-h3ll-xpl0it3rs/cve-2026-31431-copy-fail
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability, allowing unprivileged users to gain root access.
 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
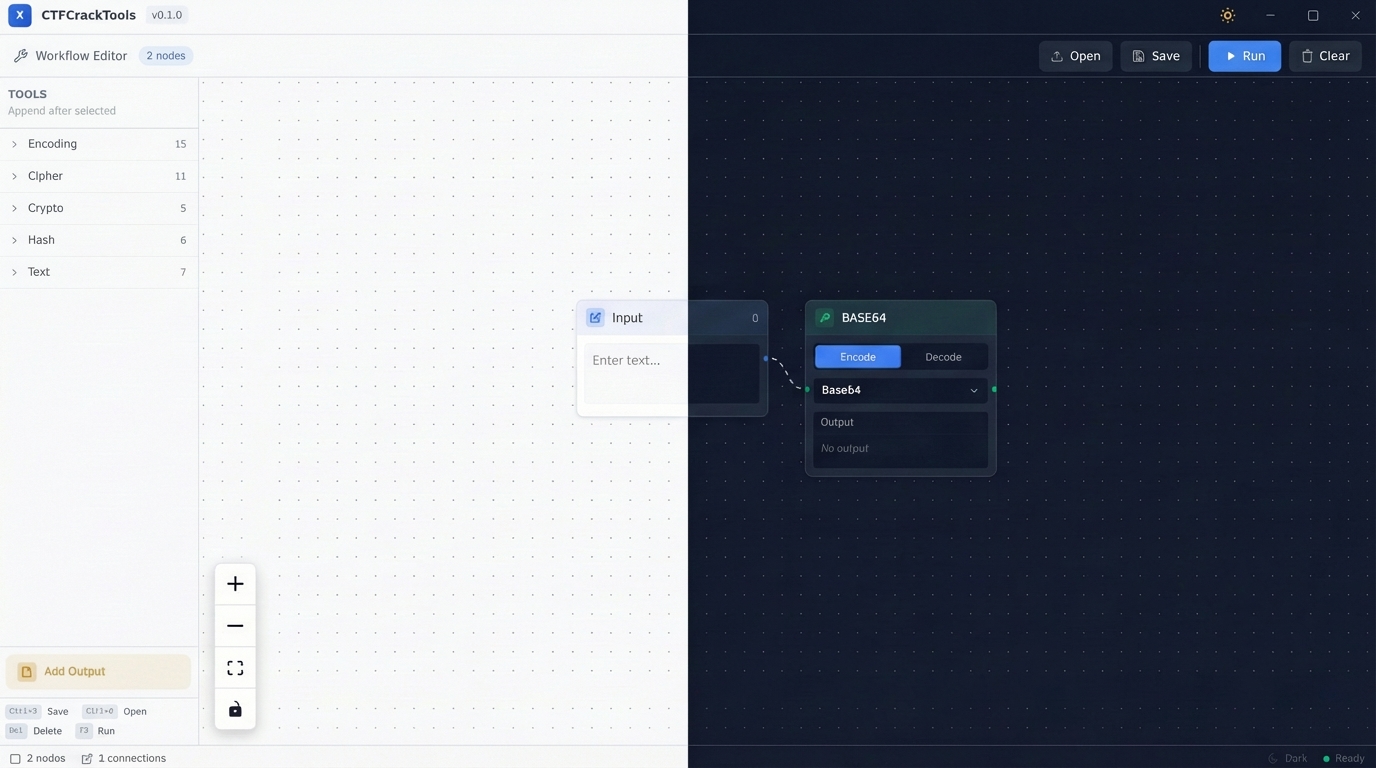 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 mfloresdacunha/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431 in Linux kernel's algif_aead, using splice to overwrite page cache and gain root. Includes a…
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
 g1nt0n1x/copy-fail-cve-2026-31431-shell
PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…
 nishantiyer/cve-2020-15215-discord-poc
Proof-of-concept validation harness for Electron boundary hardening, modeling renderer/main-process isolation, IPC policy enforcement, and navigation…
 xn0kkx/cve-2026-31431_copyfail_linuxkernel_lpe
Educational rewrite of the Copy Fail PoC (CVE-2026-31431) — Linux kernel LPE via algif_aead in-place crypto + splice() page-cache write
 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 kaleth4/cve-2026-31431
Exploit and detector for a Linux kernel local privilege escalation (CVE-2026-31431) that corrupts page cache to gain root, with mitigation guidance.
 mrarianet/cpanel-fix
One security-remediation.sh for CVE-2026-41940 (cPanel), CVE-2026-31431 (kernel "Copy Fail"), CSF, optional domain/proxy cleanup, and optional…
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.
 pyroceper/copy-fail-cve-2026-31431
C-based proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation vulnerability, providing root shell access on affected…
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…








