
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 f2u0a0d3/cve-2026-42945-nginx-rift-poc
PoC for CVE-2026-42945 (nginx Rift) — heap buffer overflow in ngx_http_rewrite_module. Includes detect/probe/exploit modes, dual-fixture Docker lab,…
 arnavps/ctf-web-exploitation
A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
 shoucheng3/testng-team__testng_cve-2022-4065_7-5
Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.
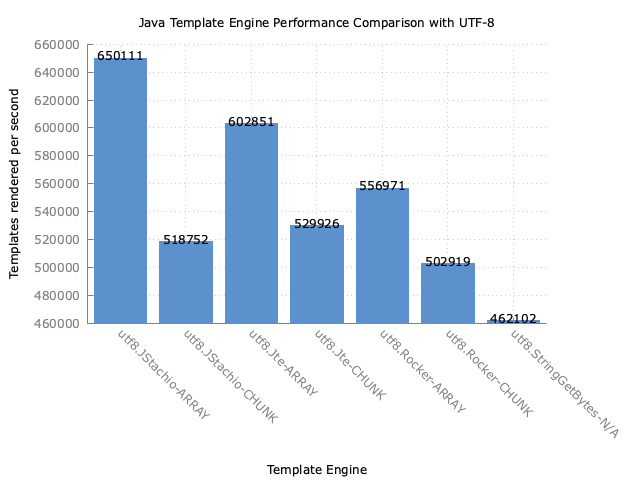 shoucheng3/jstachio__jstachio_cve-2023-33962_1-0-0
Type-safe Java Mustache templating engine with compile-time template validation, static value binding, and extensible escaping for HTML and other…
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
 borewit/svg-sanitizer
Java library that sanitizes SVG files by stripping JavaScript, inline event handlers, and script tags while blocking external resource loading to…
 teamn4c/sg-2026-0024
CVE-2026-43284 and CVE-2026-43500 Dirty Frag PoC and exploit
 db-ol/cuaharm
Benchmark for evaluating safety risks of computer-using agents, with 104 realistic misuse scenarios across seven malicious categories, supporting…
 victorns69/cve-2024-12381
Exploit for Chrome V8 type confusion (CVE-2024-12381) with JSPI sandbox bypass, delivering RCE via a Flask server that fingerprints browsers and…
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
 themursalin/cve-2026-31431
Python exploit for CVE-2026-31431, a Linux kernel LPE via AF_ALG null pointer dereference leading to heap OOB write and credential overwrite.…
 mrarianet/cpanel-fix
One security-remediation.sh for CVE-2026-41940 (cPanel), CVE-2026-31431 (kernel "Copy Fail"), CSF, optional domain/proxy cleanup, and optional…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 0xshe/cve-2026-31431
Kernel privilege escalation exploit for CVE-2026-31431, abusing AF_ALG interface to overwrite /bin/su and spawn a root shell. Includes C…
 timvisee/send
📬 Simple, private file sharing. Mirror of https://gitlab.com/timvisee/send








