
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 vincentkaufmann/noapi-google-search-mcp
MCP server for Google search and page fetching using headless Chromium
 zerobyte-id/secraper
Search engine scraper tool with BASH script.
 frogsnot/concryptor
A gigabyte-per-second, multi-threaded file encryption engine. Achieves extreme throughput using a lock-free, triple-buffered io_uring pipeline, Rayon…
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 eth0izzle/security-skills
A collection of Claude Code skills that help security teams stay secure
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 som3canadian/bloodhound_customqueries_toolset
Tool to import your custom queries from BloodHound "Legacy" to BloodHound "Community"
 khalidelborai/xtor
Python library for programmatic Tor instance management with SOCKS5 proxy, identity rotation, stream isolation, hidden services, circuit control, and…
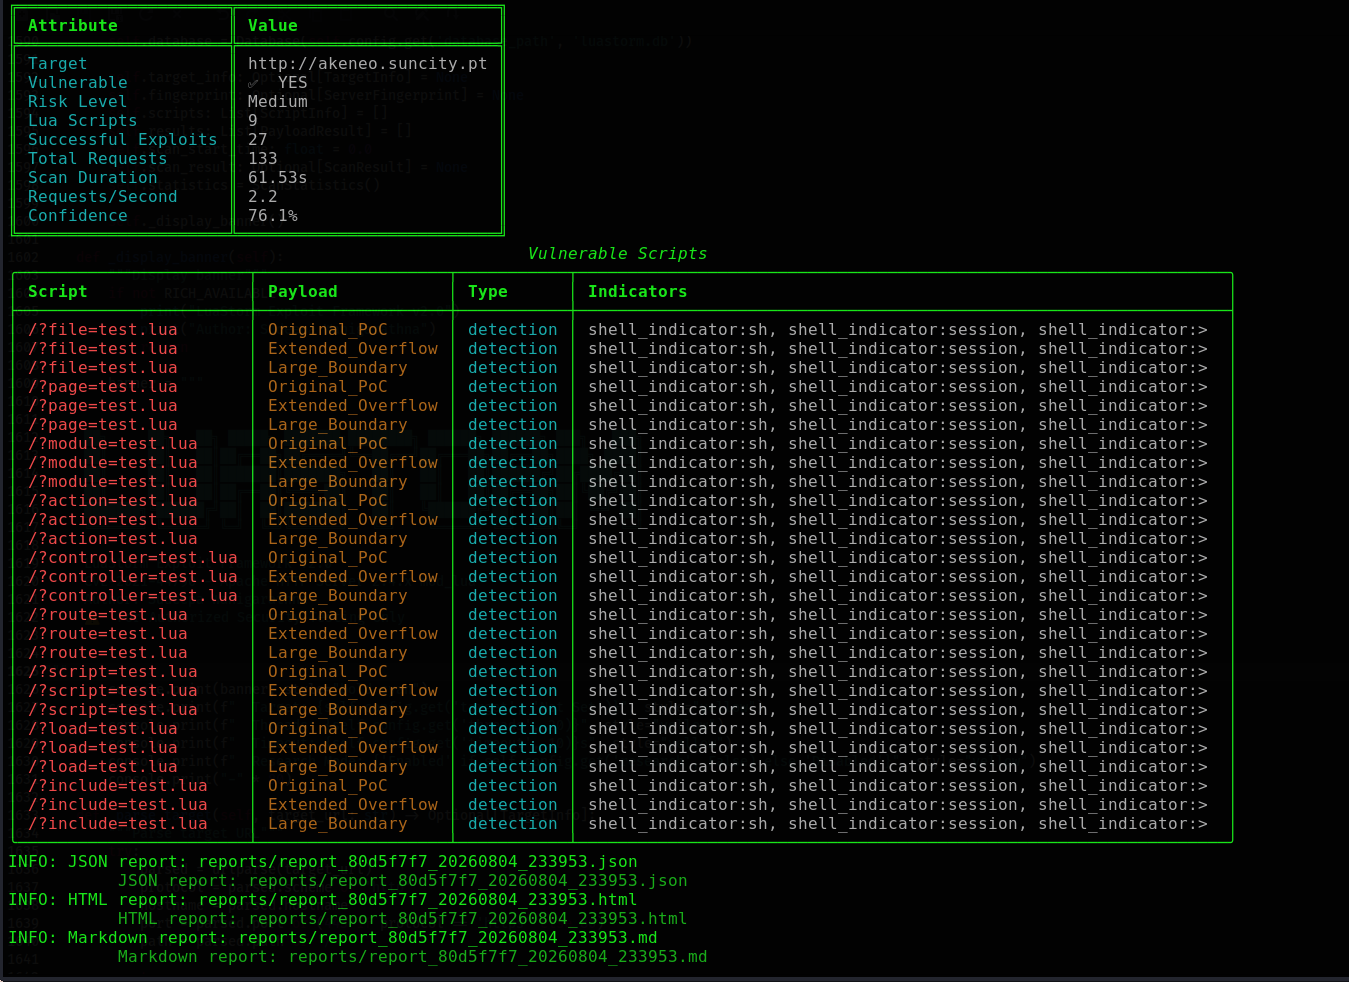 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 morpheuslord/cloudg
Map, graph and audit AWS, Azure and GCP from one CLI. Builds a topology graph, runs Prowler/Checkov/Trivy, tags findings against 28 compliance…
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
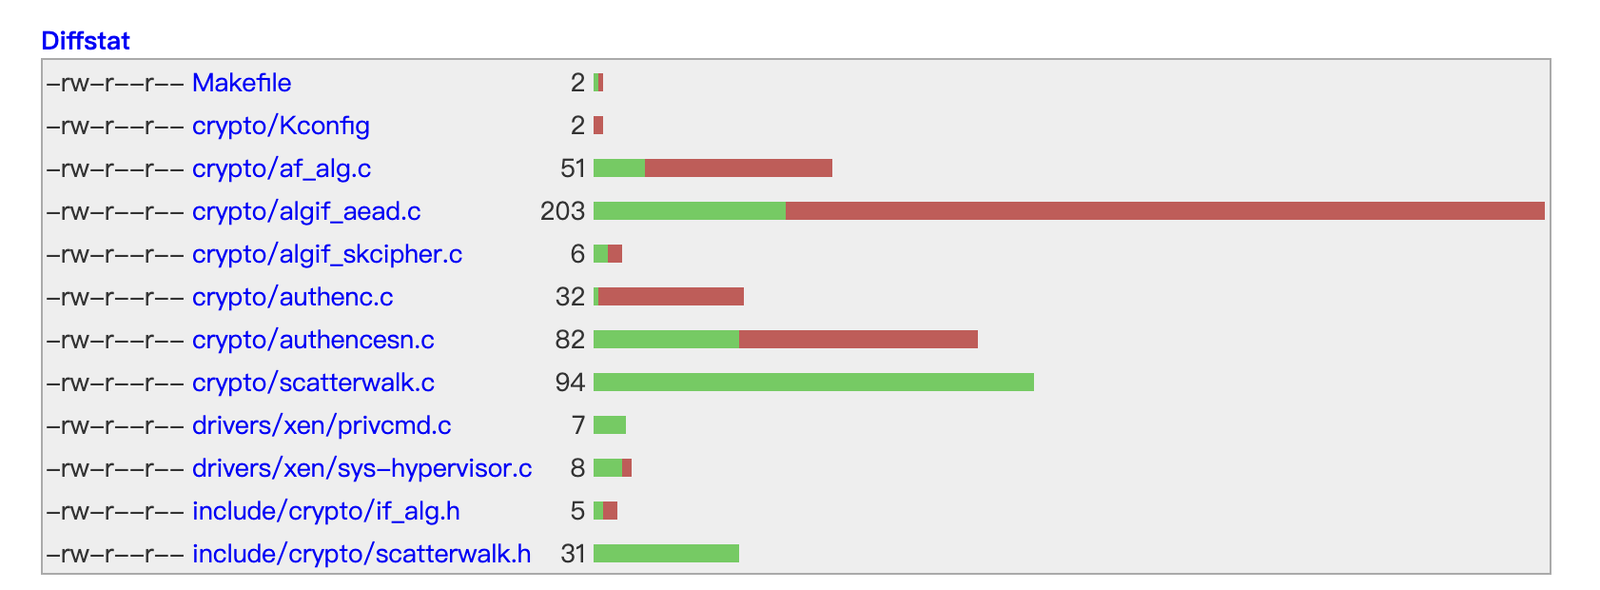 yuspring/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation via AF_ALG authenc length check bypass, achieving root by modifying…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
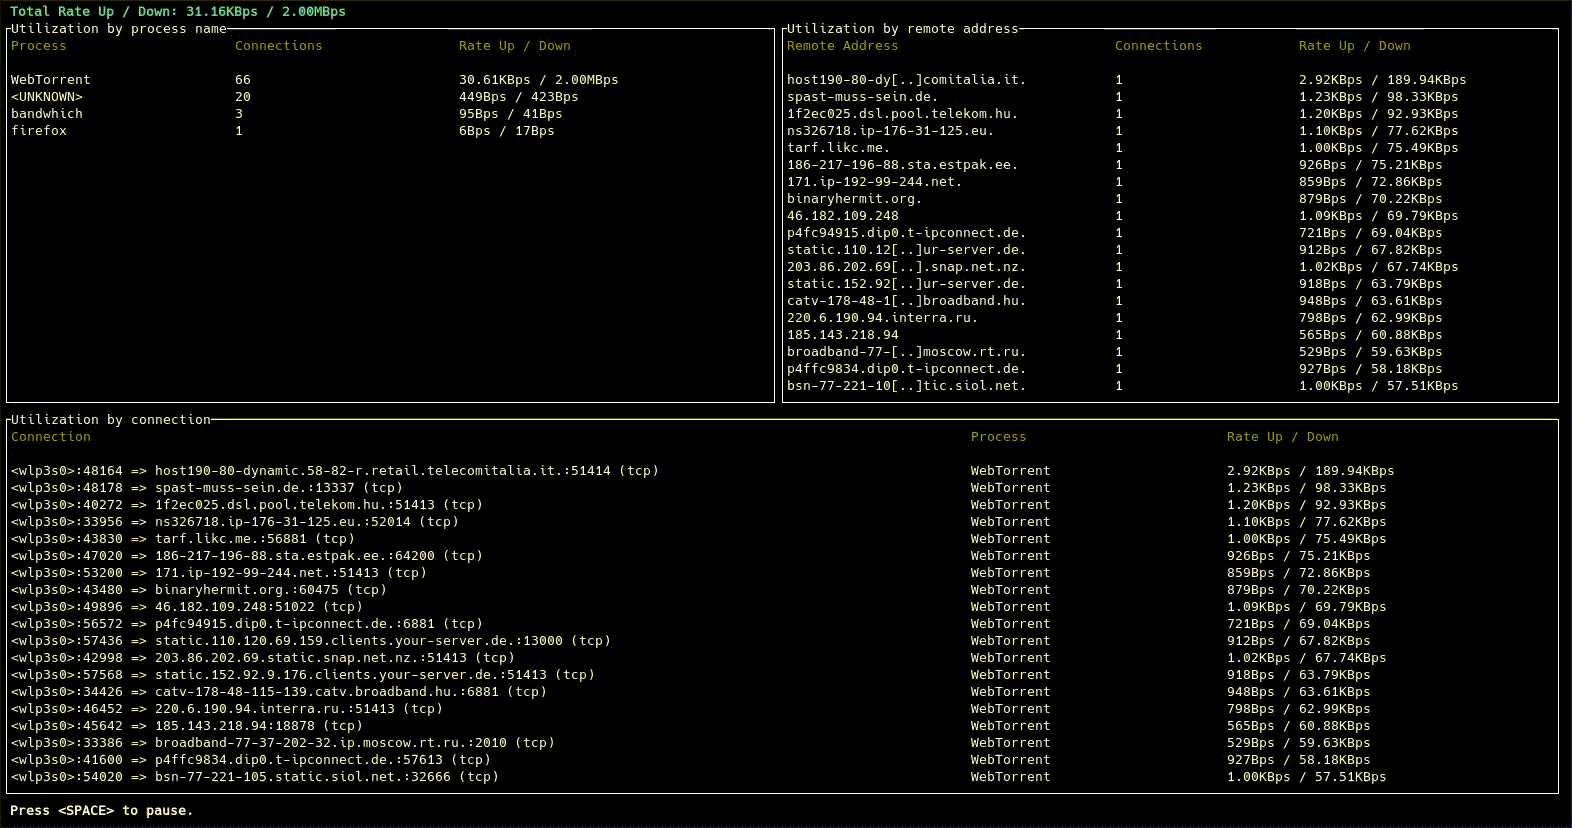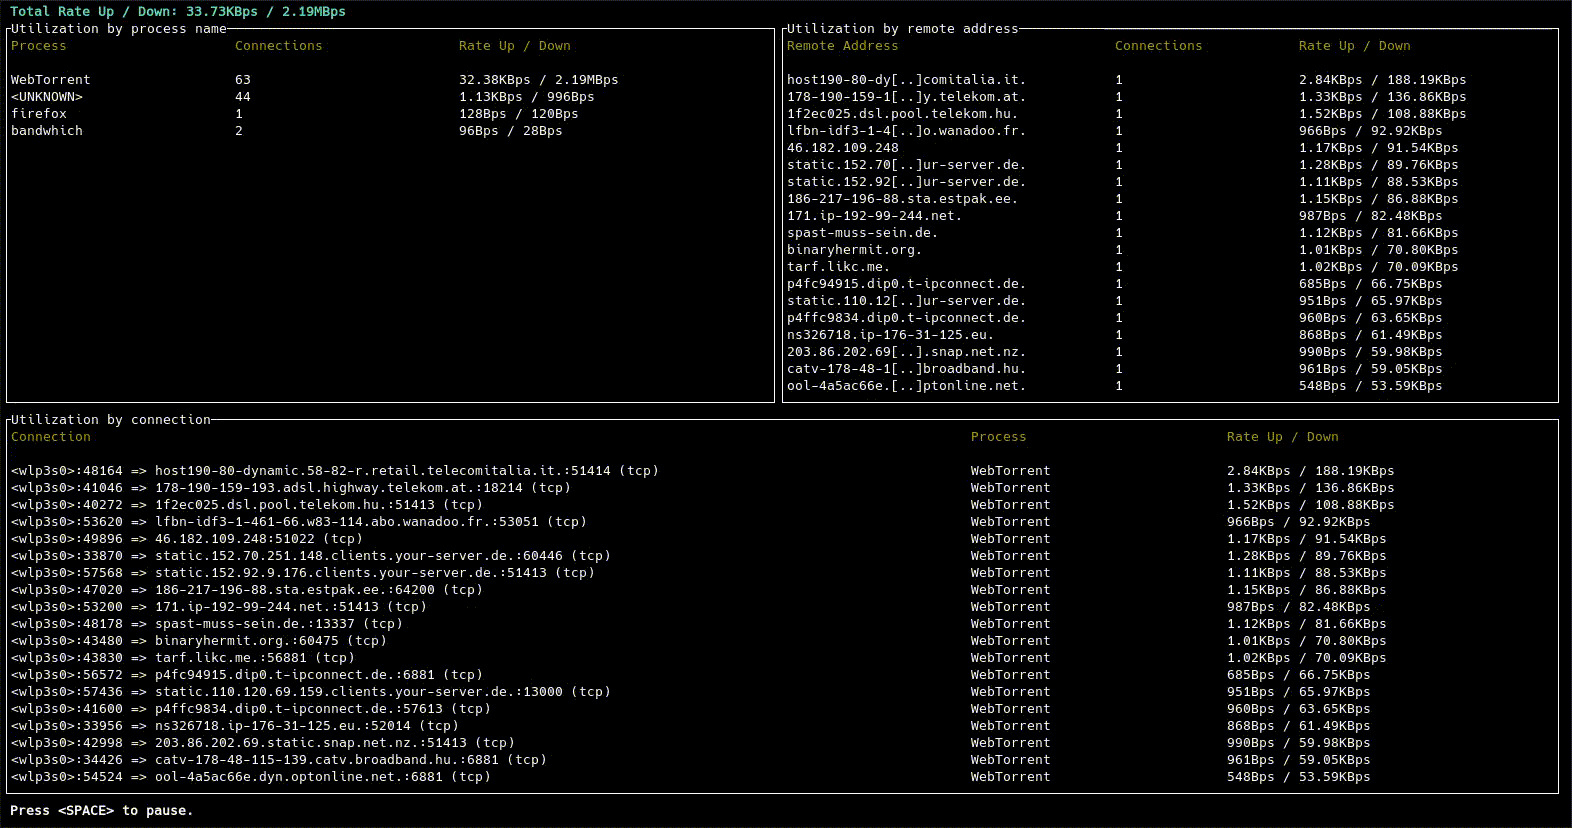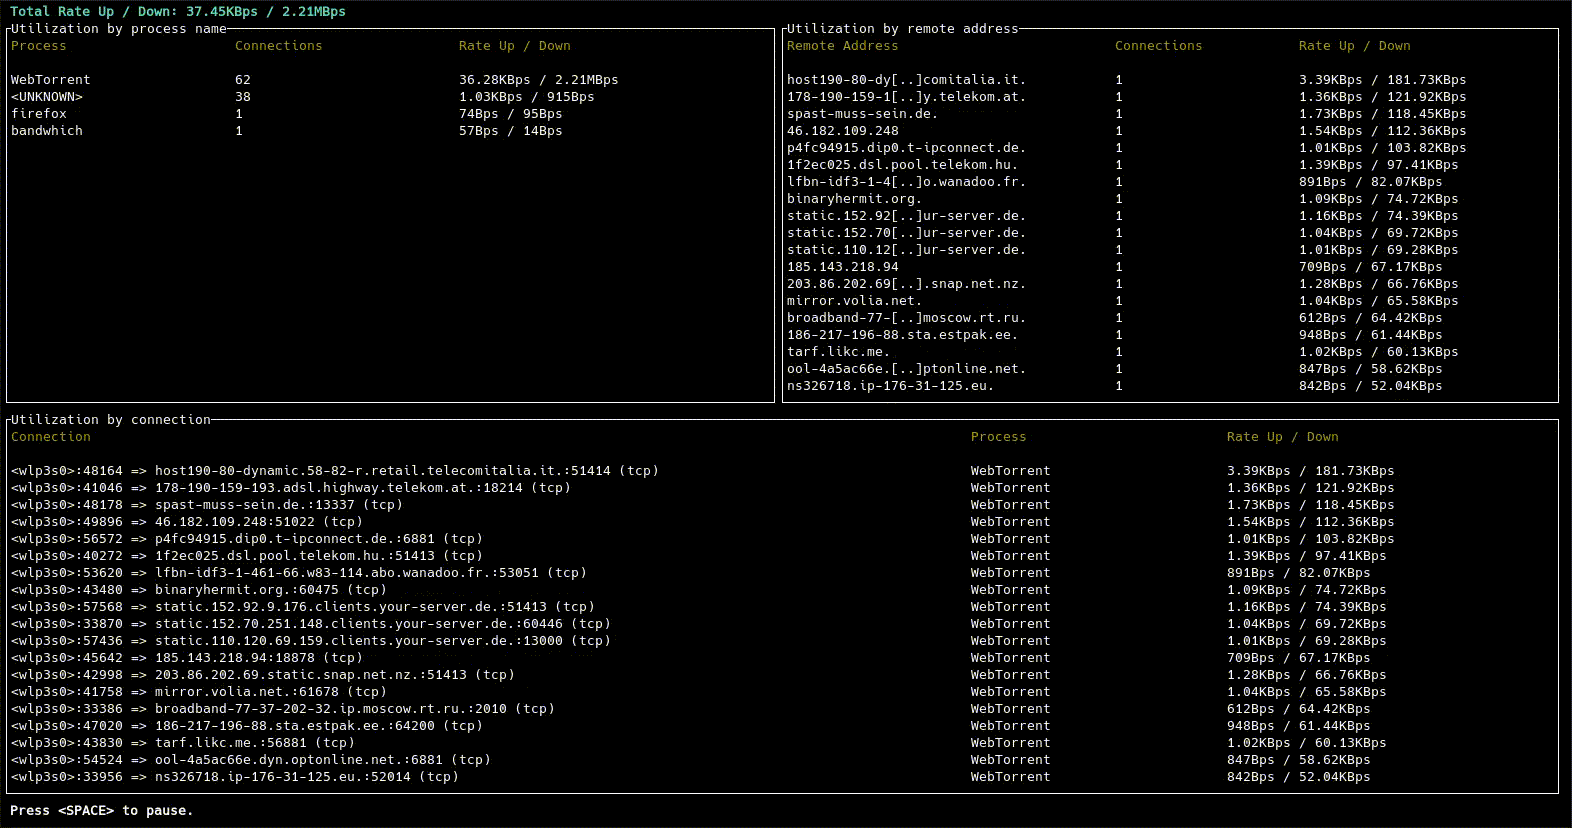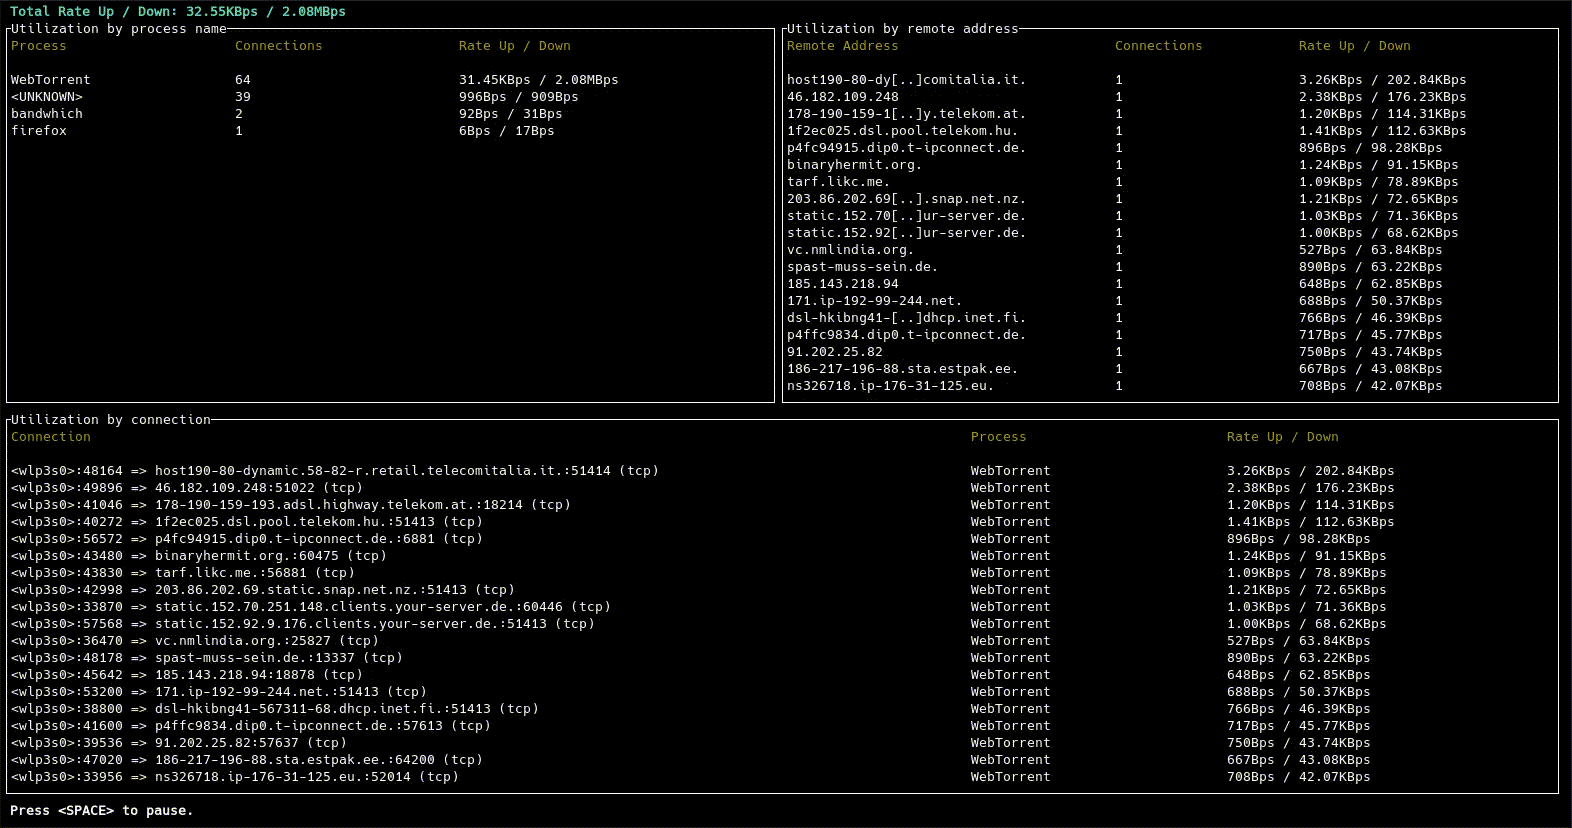 imsnif/bandwhich
Terminal bandwidth utilization tool
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform








