 #1

 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 dropbox/securitybot
Distributed alerting for the masses!
 toolswatch/vfeed
The Correlated CVE Vulnerability And Threat Intelligence Database API
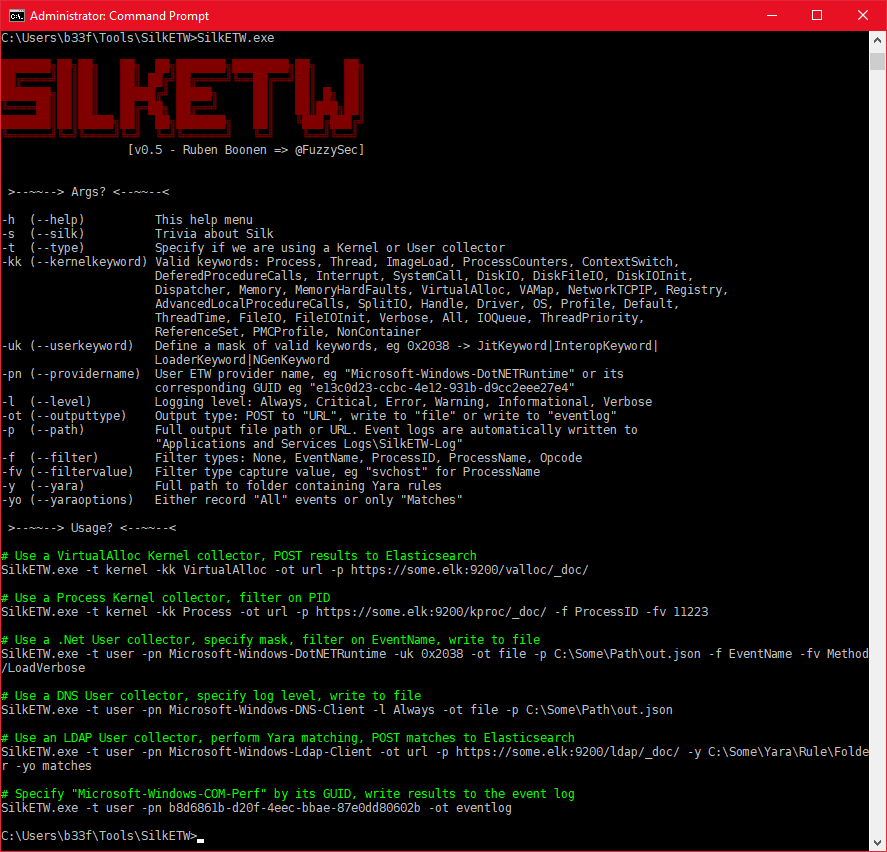 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 jerlendds/osintbuddy
Node graphs, OSINT data mining, and plugins. Connect unstructured and public data for transformative insights. The rewrite can be found @…
 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 grapl-security/grapl
Graph platform for Detection and Response
 t4d/stalkphish
StalkPhish - The Phishing kits stalker, harvesting phishing kits for investigations.
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.

 krmaxwell/maltrieve
A tool to retrieve malware directly from the source for security researchers.
 ciscocsirt/gosint
The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).
 chronicle/gcti
Detection signature repository providing YARA rules and threat-hunting content for identifying malware and malicious activity across enterprise…