 #1
Tools for collecting, analyzing, and operationalizing threat feeds, indicators of compromise (IOCs), and attack trends.
Kitploit recommended

 aditibv/moveit-cve-2023-34362
This repository investigates the exploitation of CVE-2023-34362 in the MOVEit file transfer server by the TA505 (Cl0p) ransomware group. It explores…
 aleongx/kql_sentinel_cve-2025-21333
KQL para deteccion de CVE-2025-21333 en Sentinel
 mikesxrs/cve-2023-21716_yara_results
Results of retrohunt for files matching YARA rules from https://github.com/AmgdGocha/Detection-Rules/blob/main/CVE-2023-21716.yar
 suominen/pppoeject
Patch-status tracker for the Linux kernel PPPoE sendmsg() use-after-free, recording affected versions, upstream fixes, and per-distribution patch…
 suominen/diagspill
Patch-status tracker for the Linux kernel SCTP sock_diag heap overflow (CVE-2026-74469), recording which distributions have shipped a fix.
 suominen/cve-2025-39964
Patch-status tracker for CVE-2025-39964, a Linux AF_ALG race condition enabling local privilege escalation, recording per-distribution fix…
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 soc-irdoc/irdoc-app
Incident Response Documentation Platform
 mcpmark-eval-liuhezi/log4shell-audit
Log4Shell (CVE-2021-44228) security review documentation and advisory triage
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 suominen/cve-2026-81642
Single-page tracker recording per-distribution patch status for CVE-2026-81642, the Unbound DNSSEC validator heap overflow and ReTrap complexity…
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
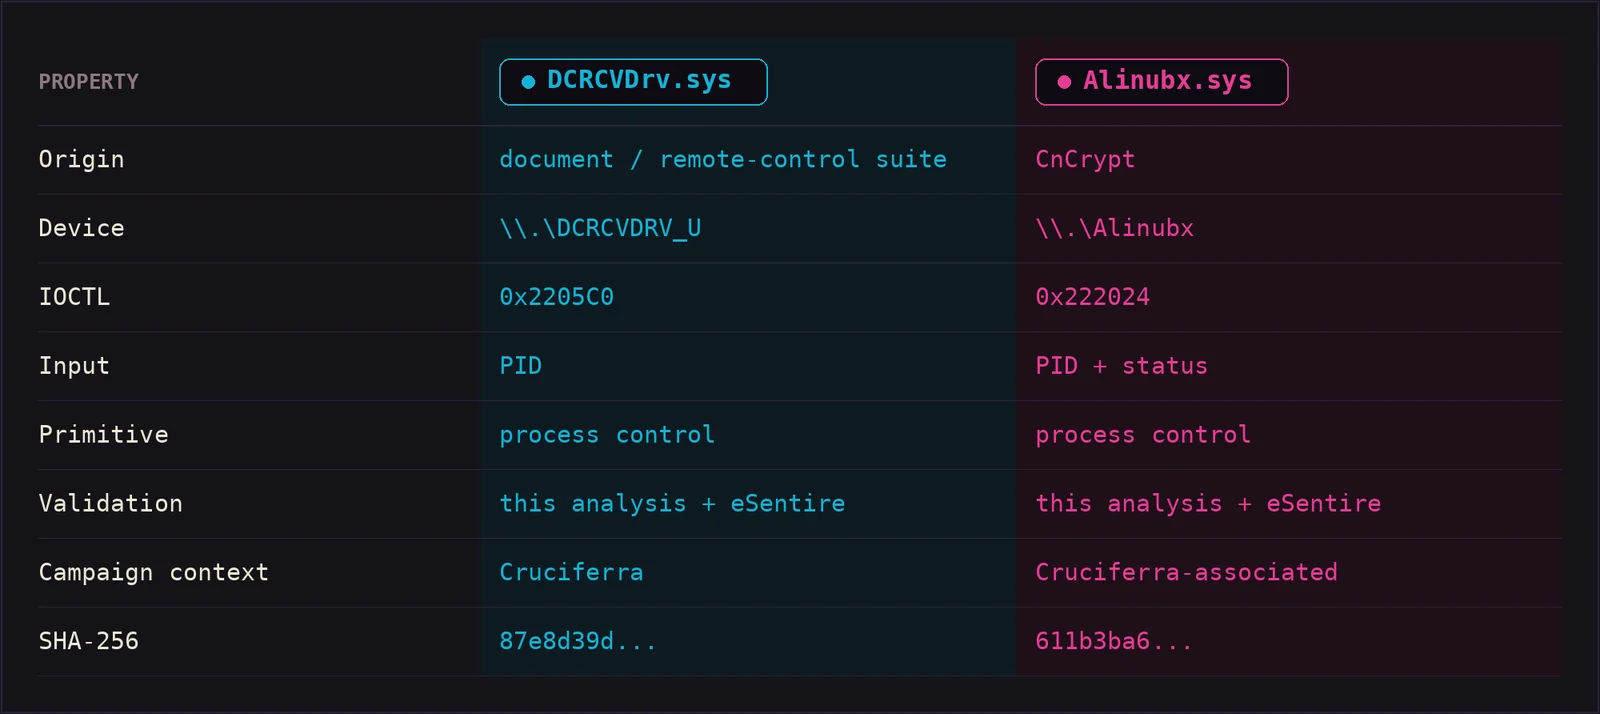 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
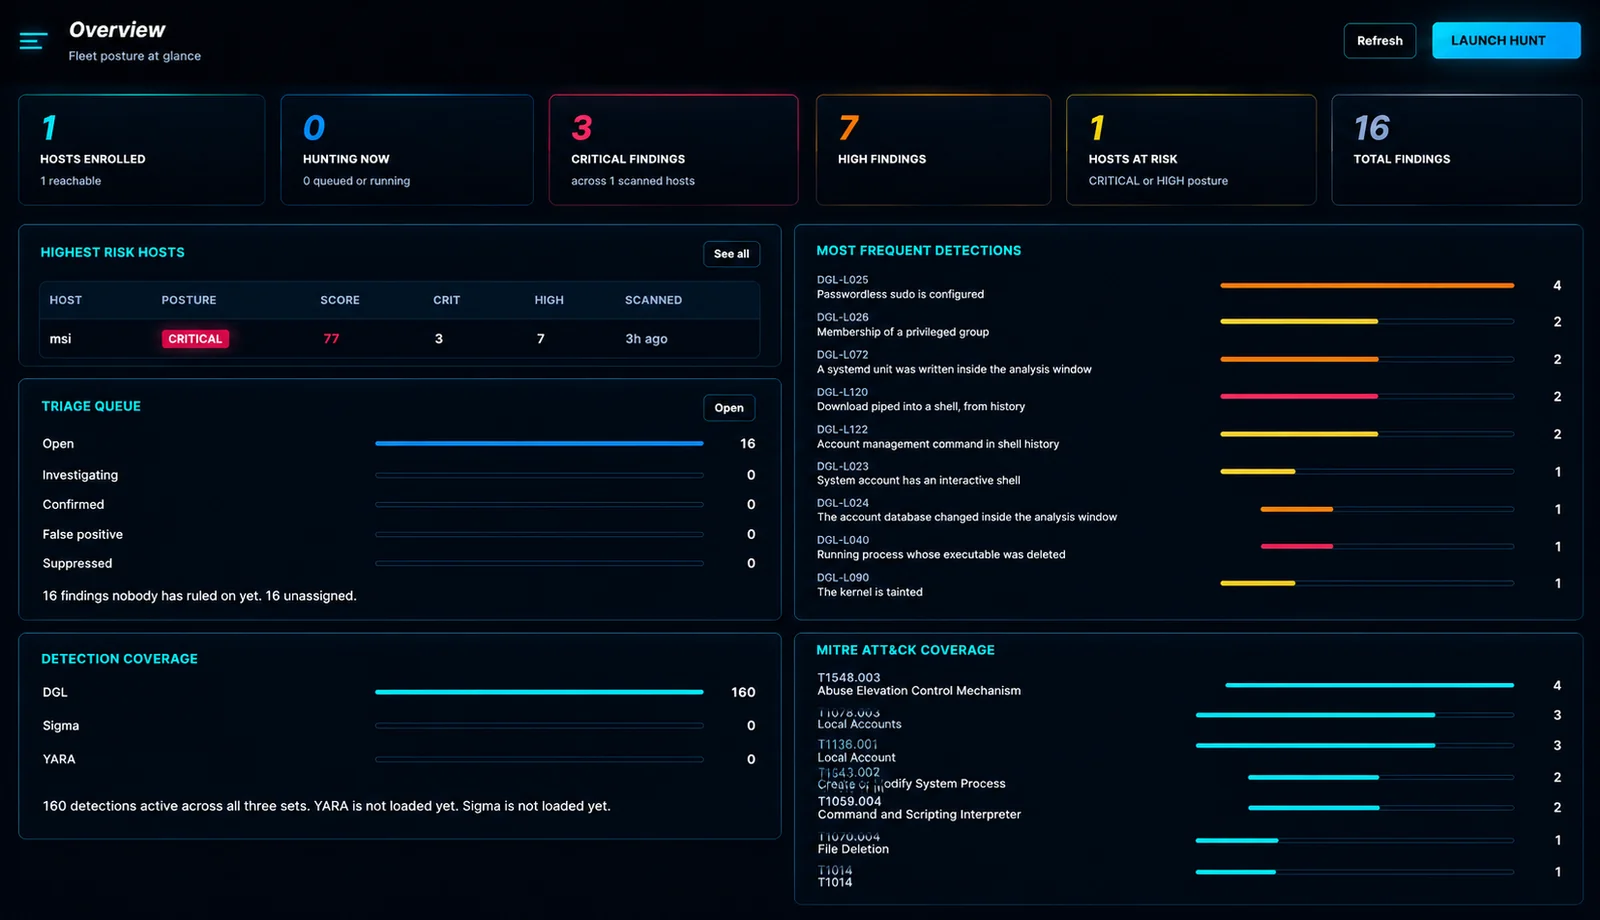 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…