
 #1
Tools for consuming, aggregating, and analyzing external threat intelligence feeds from various sources.
Kitploit recommended
 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN
 synacktiv/synacktiv-rules
Public repository of Sigma and YARA rules created by Synacktiv
 kaal22/darkgrid
3D threat intelligence dashboard that visualizes malicious infrastructure from OSINT sources like AbuseIPDB and OpenPhish, with a live threat feed,…
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 vulncheck-oss/jupyter-notebooks
Example Jupyter notebooks that query VulnCheck APIs to chart exploitation timelines, Known Exploited Vulnerabilities, and botnet data for threat…
 cybershujin/prompt-injection-in-the-wild
Tracker of publicly reported prompt-injection techniques, broken down by delivery method, encoding, and propagation behavior, with confirmed models,…
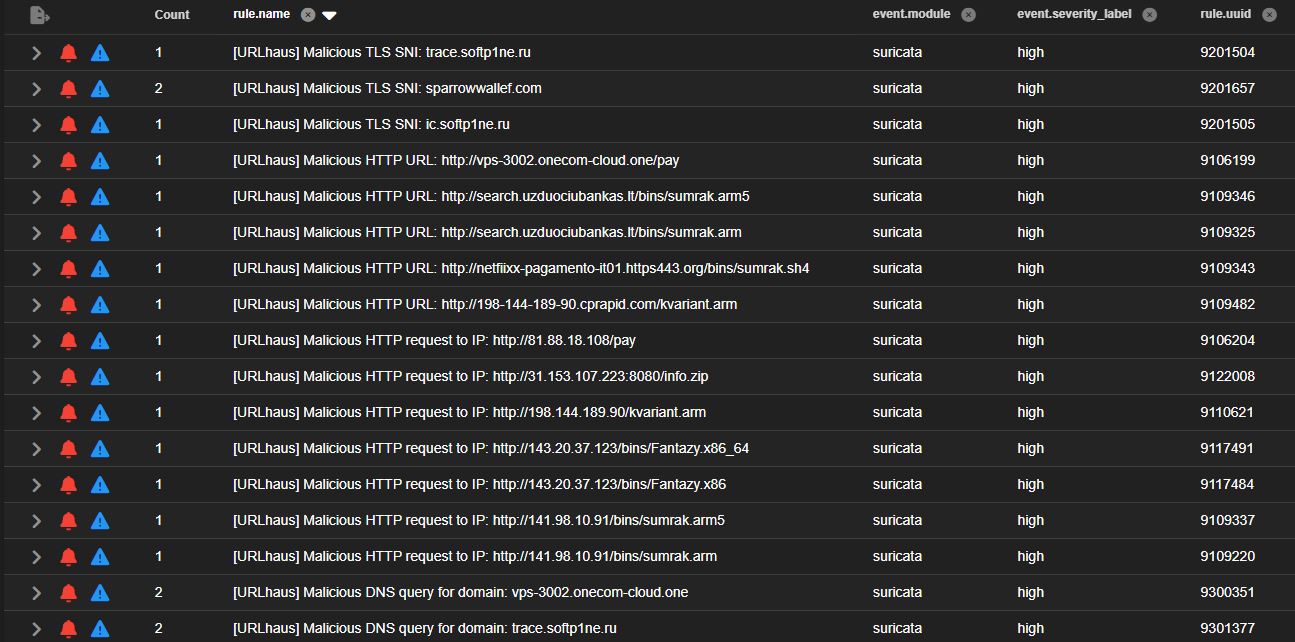 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 aquasecurity/vuln-list-aqua
Security advisories from Aqua Security
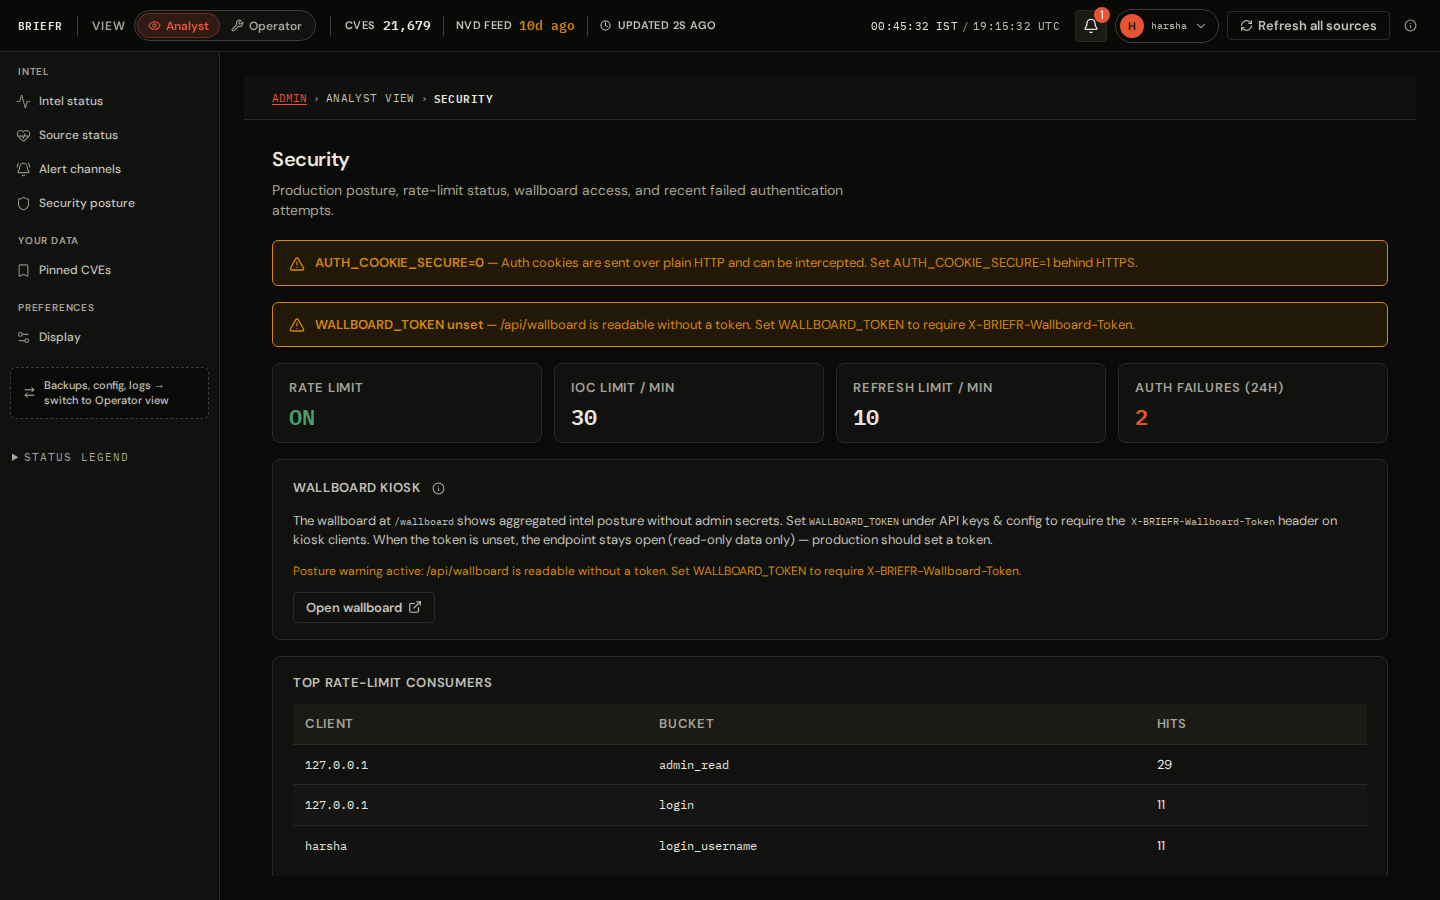 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 qbitseclabs/brintelcollector
Cyber Threat Intelligence (CTI) usando fontes e indicadores de ameaças nacionais, ou até globais, mas com evidencias ou indicadores nacionais do…








