
 #1
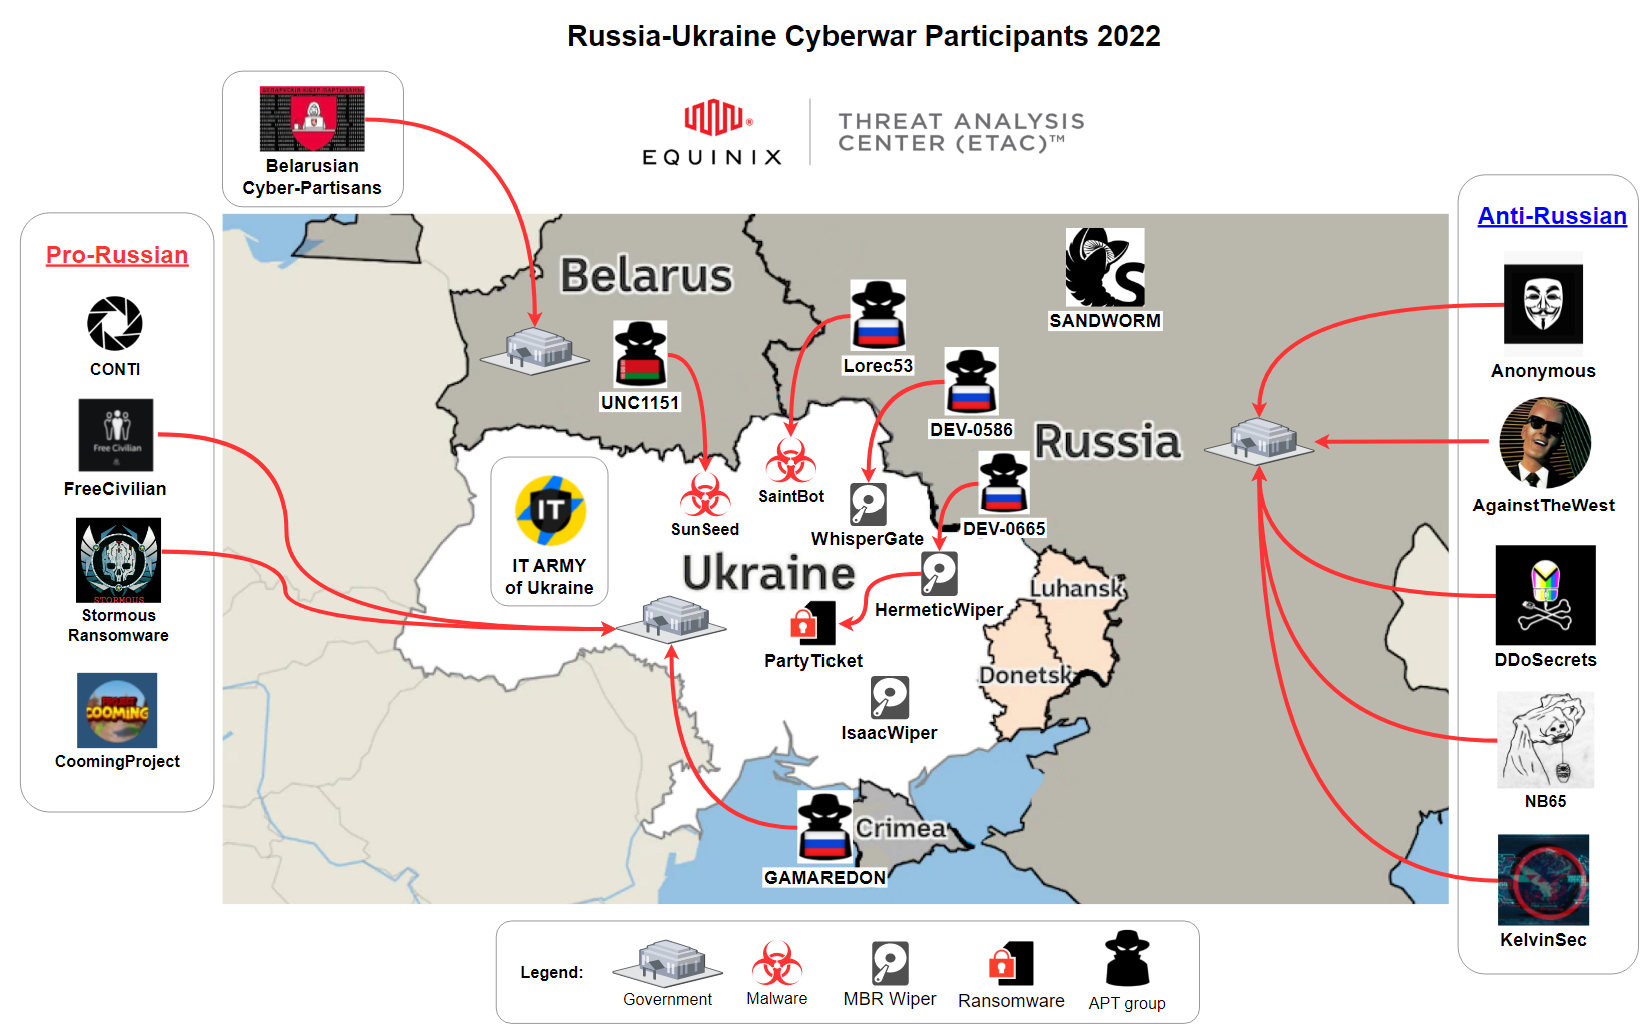
 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 knqyf263/vuln-list-backup
Collects vulnerability and advisory data from multiple public security feeds and stores it in a parsable, structured format for downstream security…
 ciscocsirt/gosint
The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).
 olafhartong/threathunting
A Splunk app mapped to MITRE ATT&CK to guide your threat hunts
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 grapl-security/grapl
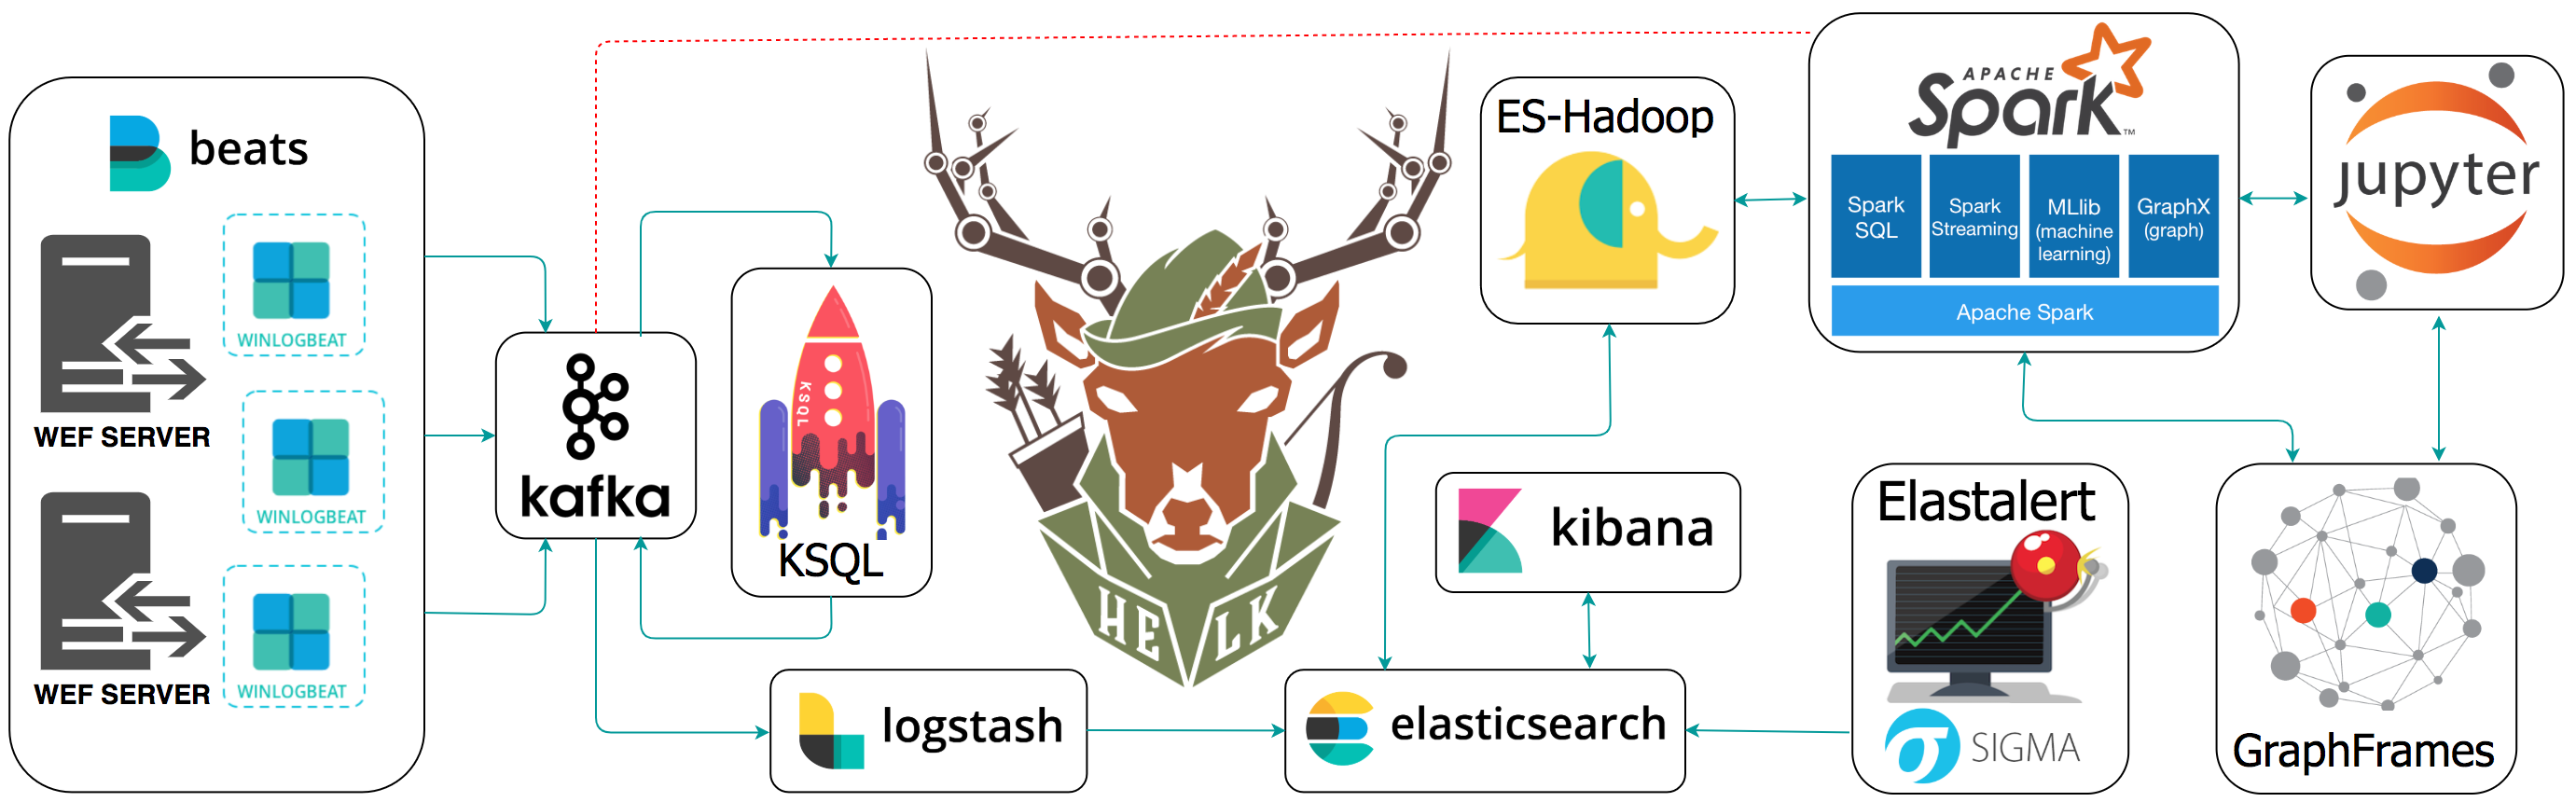
Graph platform for Detection and Response
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 guardicode/cve-2021-44228_iocs
Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 watchguard-threat-lab/log4shell-iocs
A collection of IOCs for CVE-2021-44228 also known as Log4Shell
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 jangeisbauer/gundog
gundog - guided hunting in Microsoft Defender









