
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
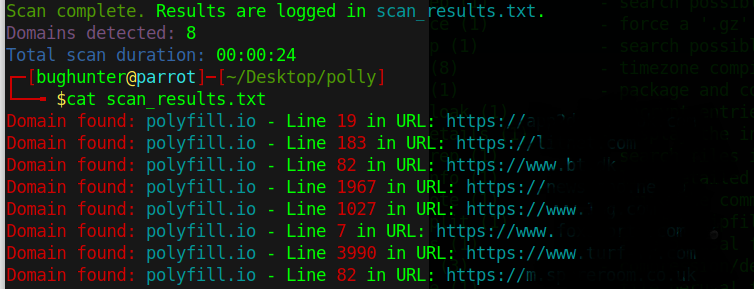 putget/cve-2024-38526
CVE-2024-38526 - Polyfill Scanner
 simplifi-ed/cve-2024-3094-patcher
Ansible playbook for patching CVE-2024-3094
 lukepasek/log4jjndilookupremove
A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.
 laxmikumari615/linux---security---detect-and-mitigate-cve-2024-3094
It was determined that malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. # It was determined that only…
 fractal-tess/cve-2024-3094
Bash script to detect and remediate vulnerable xz-utils versions (5.6.0/5.6.1) by replacing them with a stable, uncompromised build from source.
 roy-aladin/infratest
DO NOT FORK, DEPLOY, OR USE FOR ANYTHING BUT LEARNING. These requirements are vulnerable to CVE-2024-39689
 ronmadar/open-source-seal-security
Fix open source package uses tough-cookie 2.5.0 - CVE-2023-26136,
 isuruwa/cve-2024-3094
Minimal CVE-2024-3094 reference repository documenting the xz backdoor vulnerability, affected versions (5.6.0/5.6.1), and mitigation steps. Includes…
 andreacicca/sicurezza-informatica-presentazione
Presentazione per il corsi di sicurezza Informatica sulla vulnerabilità CVE-2024-3094
 dah4k/cve-2024-3094
Proof-of-concept and analysis tools for CVE-2024-3094, the XZ Utils backdoor vulnerability, including detection and exploitation scripts.
 ryancnelson/patched-bash-4.3
patched-bash-4.3 for CVE-2014-6271
 skulkarni-mv/goissue_dunfell
go CVE-2023-24538 patch issue resolver - Dunfell
 u-maxx/magento-swf-patched-cve-2011-2461
Patched version of the uploader.swf and uploaderSingle.swf to fix CVE-2011-2461
 scabench/l4j-fp1
jee web project with sanitised log4shell (CVE-2021-44228) vulnerability
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 mesutgungor/xz-backdoor-vulnerability
CVE-2024-3094
 agylabs/log4shell-remediation
Log4Shell (CVE-2021-44228) security remediation demo - Showcasing Antigravity's ability to identify and fix critical security vulnerabilities in Java…








