
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 wise-security/cve-2025-69599
Proof-of-concept exploit for CVE-2025-69599, demonstrating uncontrolled search path element in RayVentory Scan Engine's rvia and ndtrack binaries,…
 airineiandrei/tarmageddon-cve-2025-62518-
PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…
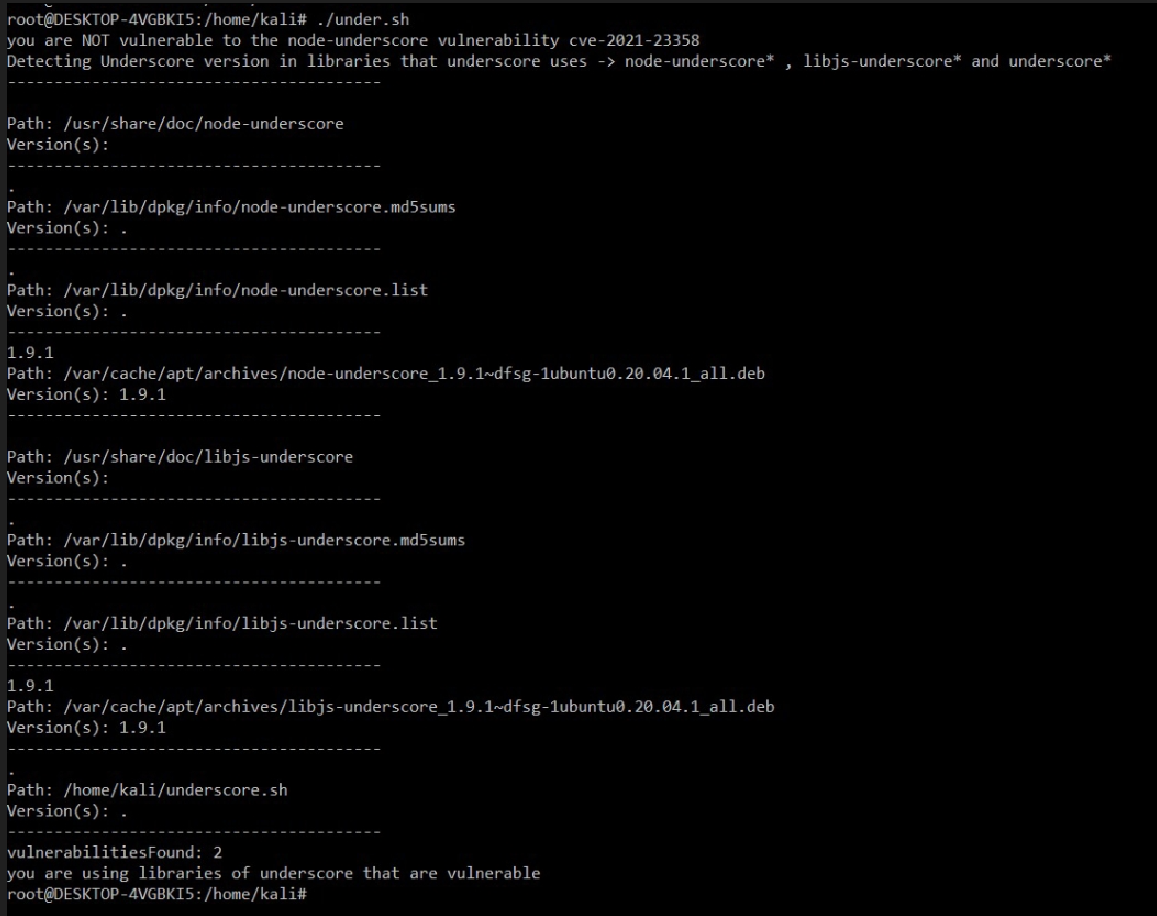 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
 hamm0nz/react2shell-audit
A lightweight, recursive Bash script to detect Next.js and React Server DOM versions vulnerable to CVE-2025-55182 (React2Shell) in local projects.
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
 3dluvr/new-lib3mf.dll-for-meshmixer
Precompiled lib3mf.dll for MeshMixer which includes a backported patch for CVE-2021-21772 and zlib 1.3.1
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation
 simoesctt/sovereign-echo-33017
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow 1.8.1 via the build_public_tmp endpoint, enabling Python code injection through…
 nn0nkey/repo
CVE-2025-65964 PoC - Malicious Git Hooks
 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
 hexbornestudio/atlas-tj-actions-poc
PoC for CVE-2025-54416 tj-actions/branch-names command injection
 ik-20211125/cve-2025-48384
CVE-2025-48384 PoC








