
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 sasairc/cve-2017-1000117_wasawasa
Minimal test repository demonstrating Git's CVE-2017-1000117 recursive clone vulnerability for educational exploitation verification.
 themcsam/cve-2024-12905-poc
tar-fs file write/overwrite vulnerability
 andalik/log4j-filescan
Scanner recursivo de arquivos desenvolvido em Python 3 para localização e varredura de versões vulneráveis do Log4j2, contemplando análise interna de…
 test-avm-714877d2df585126/c-test-2
Dependabot security automerge test - ejs CVE-2022-29078
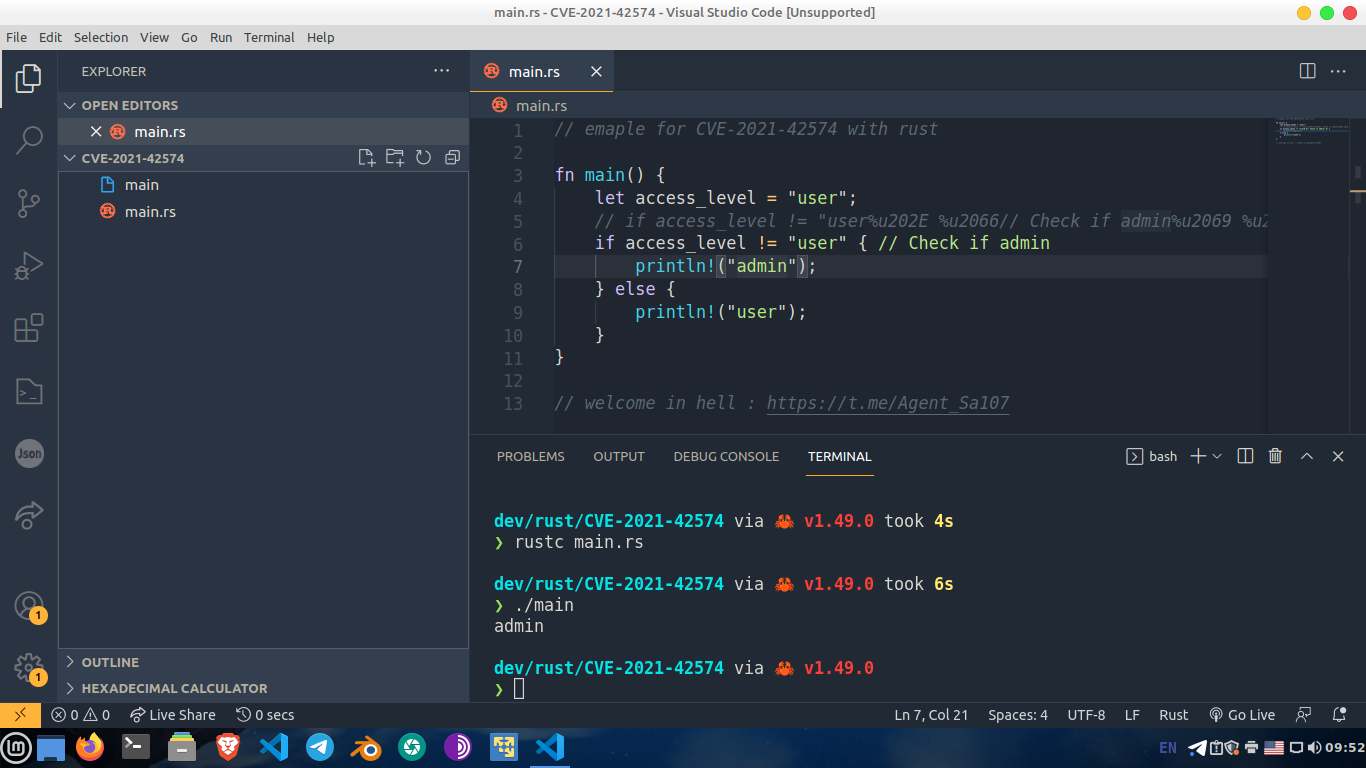 waseeld/cve-2021-42574
Demonstrates the Trojan Source vulnerability (CVE-2021-42574) by generating source code with invisible Unicode control characters that alter compiler…
 murataydemir/aws-tough-library-multiple-cves
Issue with tough, versions prior to 0.20.0 (Multiple CVEs)
 dpomnean/log4j_scanner_wrapper
log4j vulnerability wrapper scanner for CVE-2021-44228
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 gonsarrabia/minimus-junior-backend-exercise
Junior Backend Candidate Exercise: Packaging the dasel CLI (v3.3.1) with Melange, fixing CVE-2026-33320, and building a minimal container image using…
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 0xblackash/cve-2026-40175
CVE-2026-40175
 rusakovichma/cve-2019-10172
CVE-2019-10172 PoC and Possible mitigations
 comerc/cve-2025-68664
Detailed disclosure of CVE-2025-68664, a critical deserialization vulnerability in LangChain core allowing secret exfiltration and potential RCE via…
 graypixel2121/cve-2025-69604
Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability








