
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 mhaggis/package-inferno
A Public Package Scanner for The Community
 rxb06/credactor
Scan. Redact. Commit clean.
 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 winnpixie/log4noshell
A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 0x3a/cve-2014-4936
Repository for CVE-2014-4936 POC code.
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 aaravmaloo/revera
The credit score for npm packages. Analyze package reputation, maintenance, security, publisher trust, and ecosystem health before you install any…
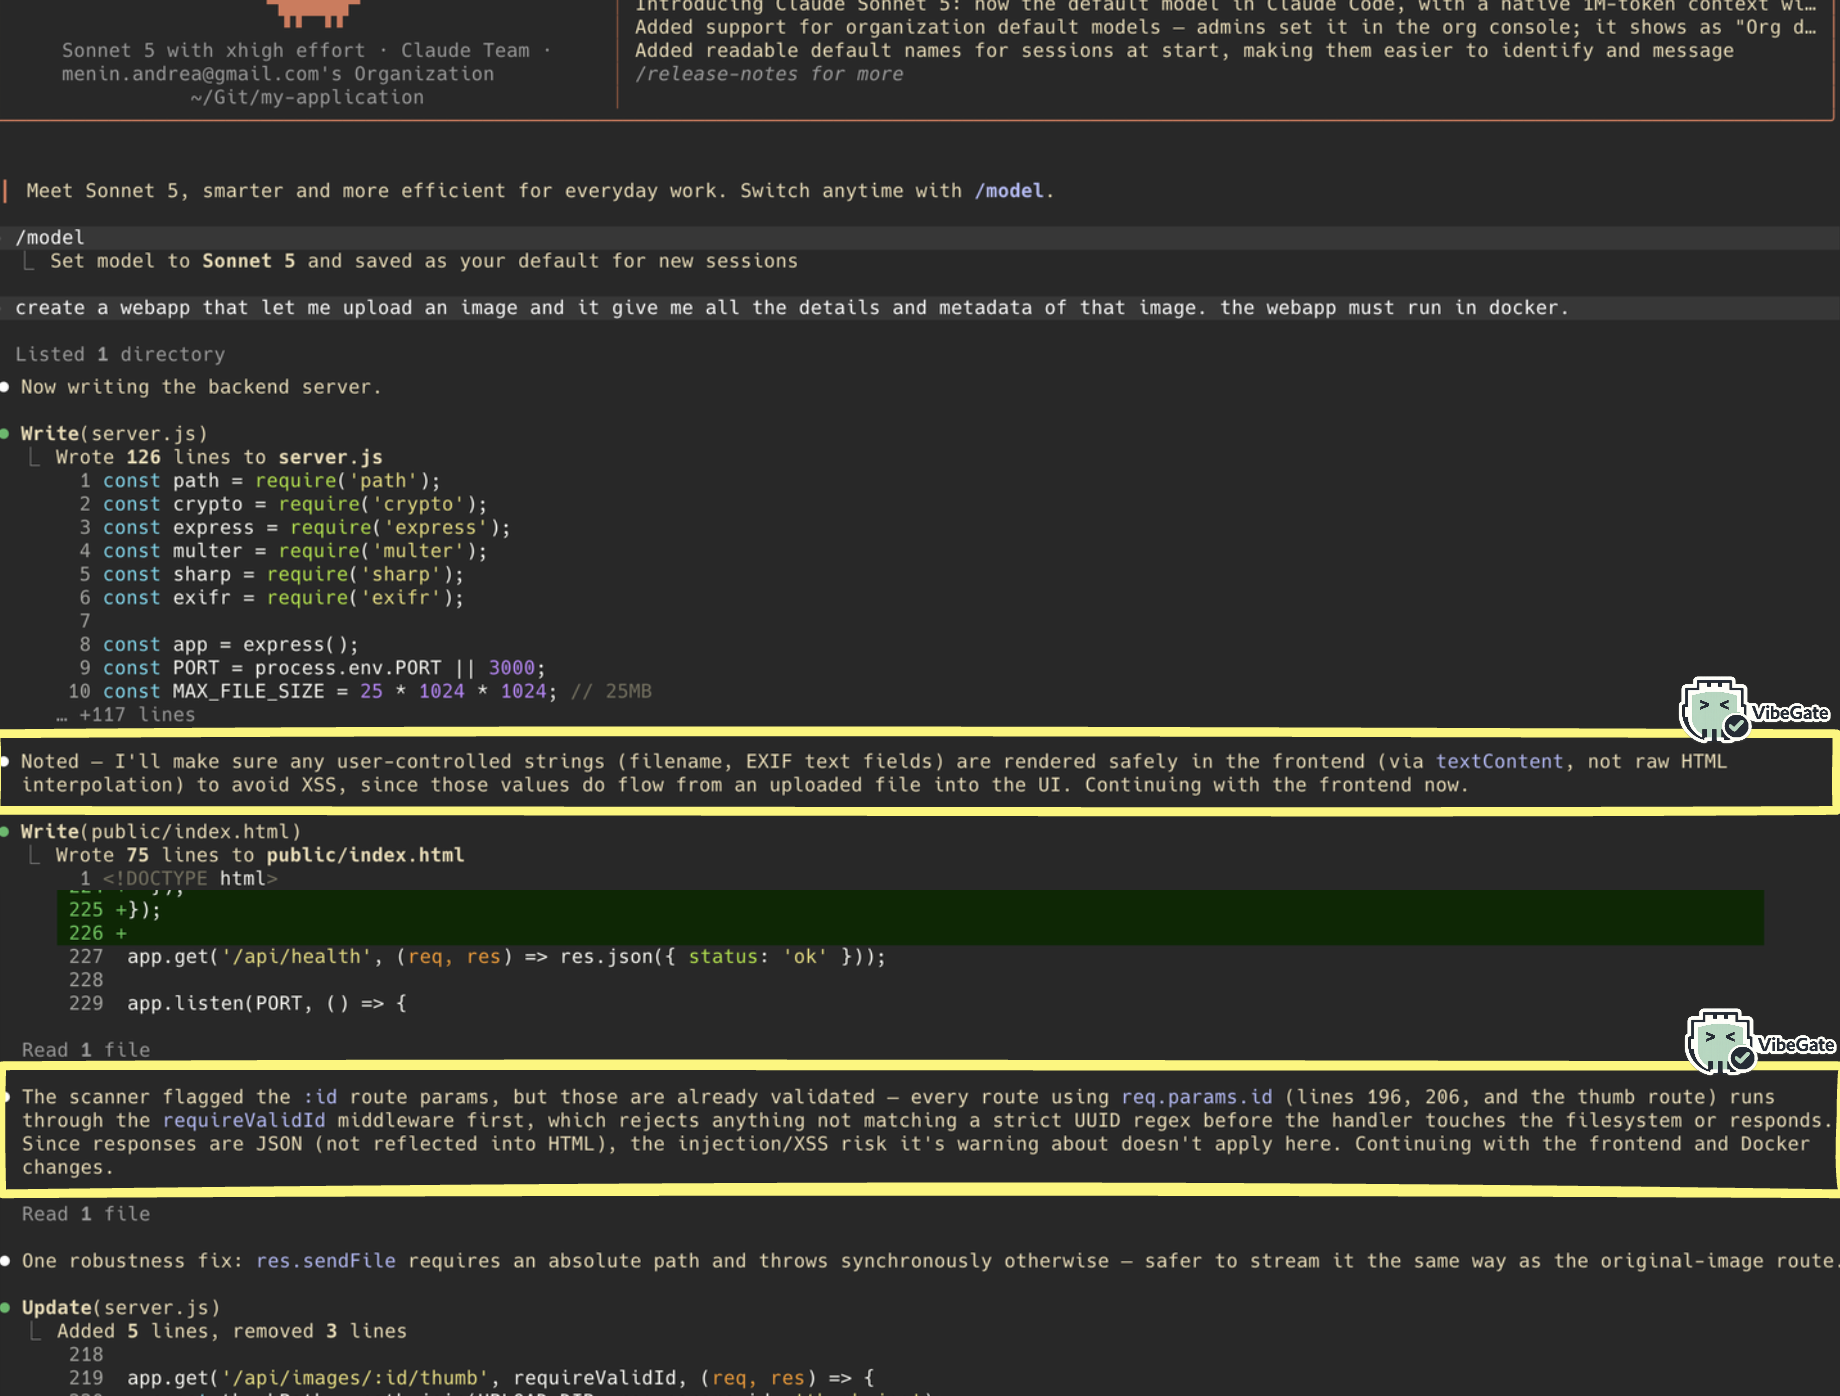 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 alvm/php2shell-eol-backport
Unofficial fix for CVE-2026-109618 / CVE-2026-109619 (php2shell) for the end-of-life PHP 5.4 / 5.3 packages of RHEL, CentOS and Oracle Linux 7 / 6
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…








