
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 ltmthink/cve-2023-51385_test
一个验证对CVE-2023-51385
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
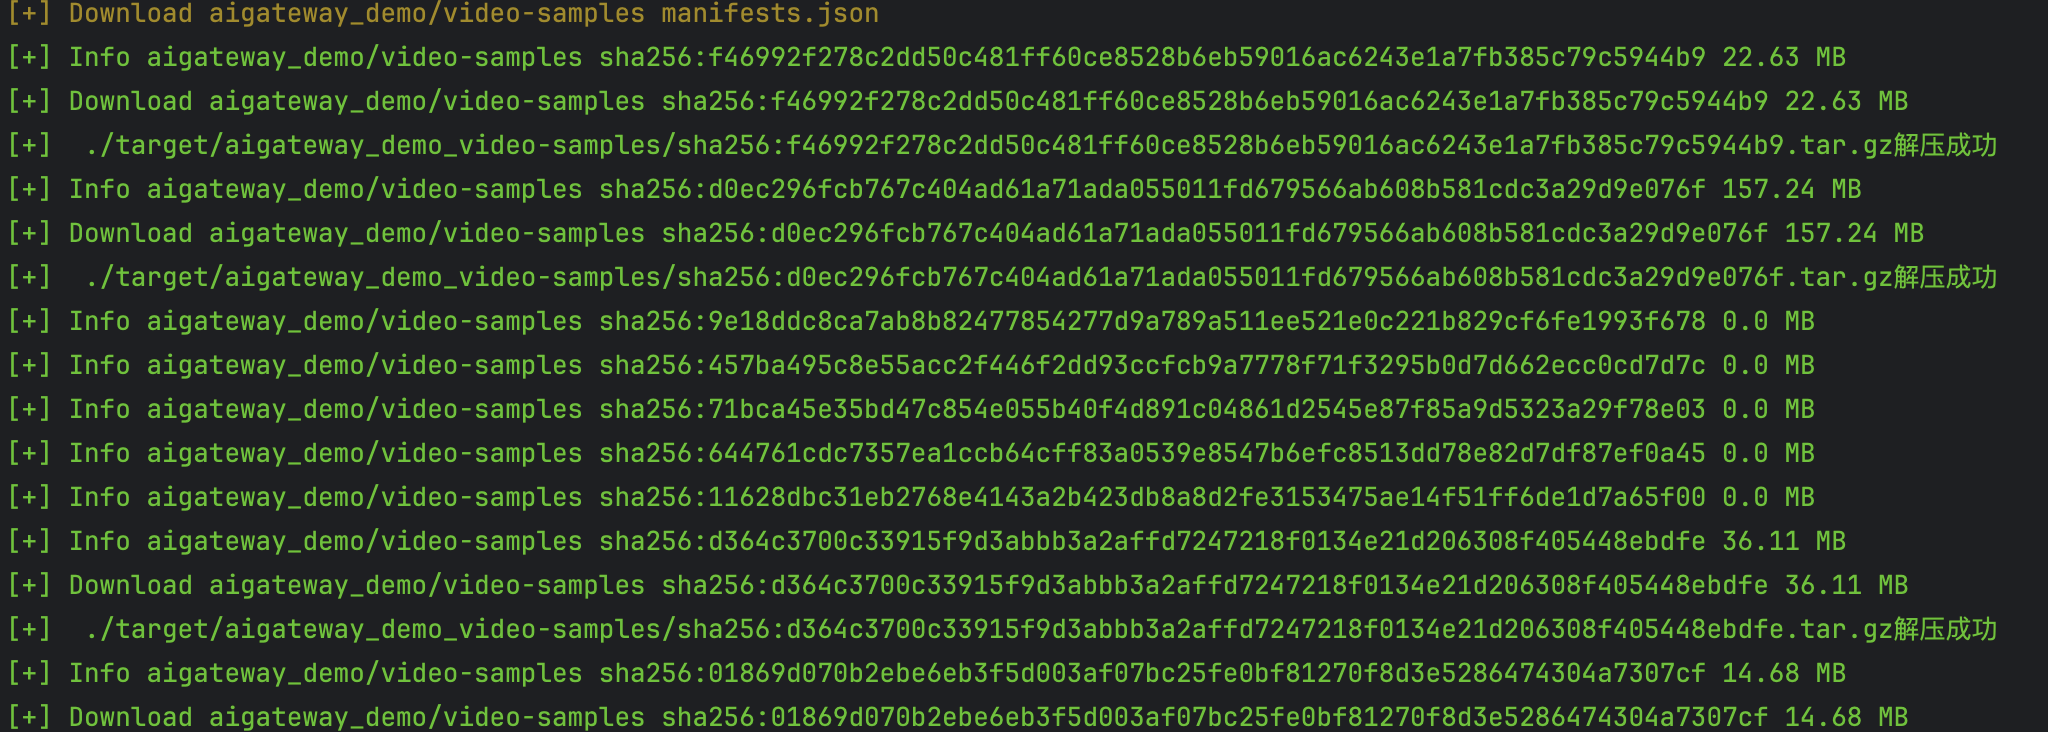 codesecurityteam/harbor
CVE-2022-46463 harbor公开镜像全自动下载脚本
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 tomjwxf/scopeblind-gateway
Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 emirkmo/xz-backdoor-github
History of commits related to the xz backdoor Discovered On March 29, 2024: CVE-2024-3094.
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 aquasecurity/binfinder
Find binary files not installed through package manager
 timwr/cve-2017-1000117
Proof of concept of CVE-2017-1000117
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
 mergebase/log4j-samples
Public testing data. Samples of log4j library versions to help log4j scanners / detectors improve their accuracy for detecting CVE-2021-45046 and…
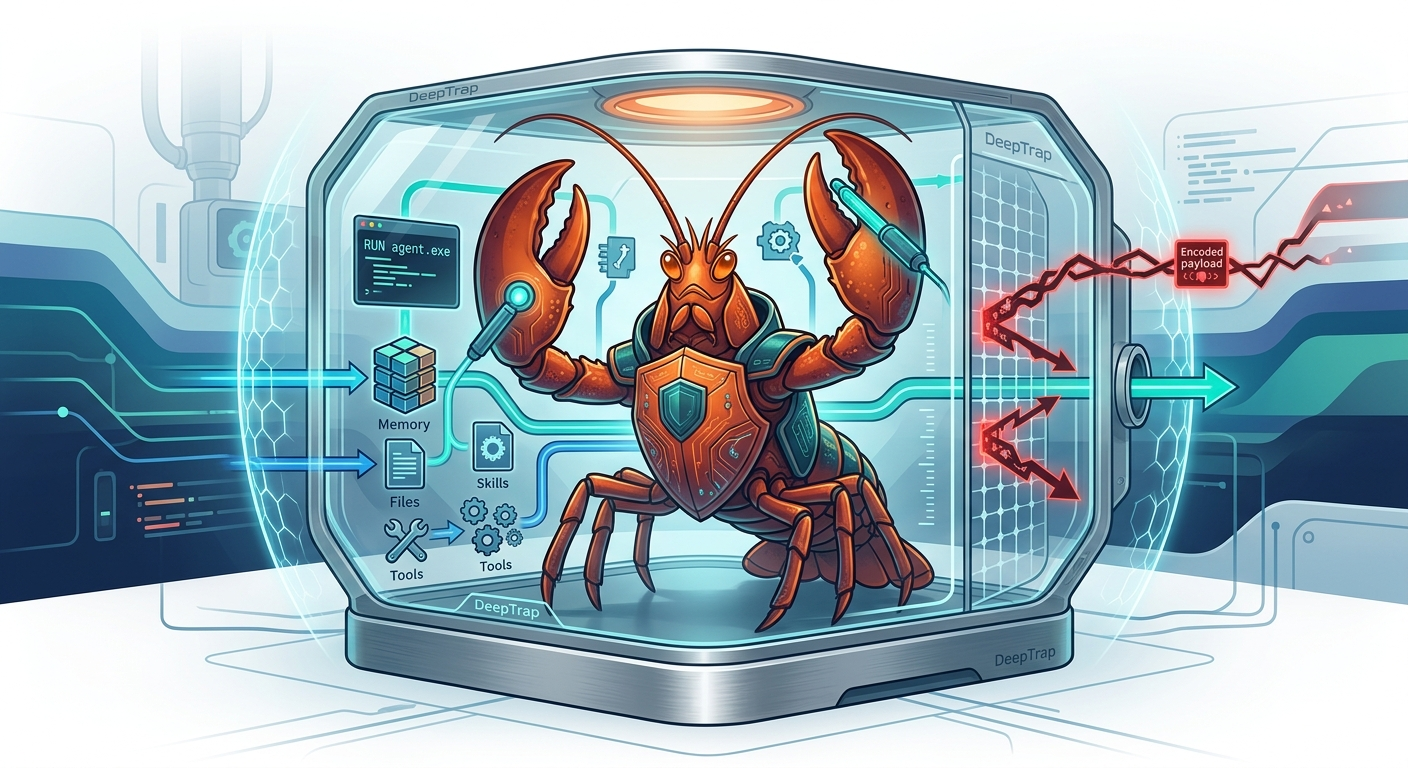 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 mhaggis/package-inferno
A Public Package Scanner for The Community
 rxb06/credactor
Scan. Redact. Commit clean.








