
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Supply Chain Security | Kitploit
Categories

Supply Chain Security

Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.

Kitploit recommended
Top tools

10 selected
osv-scanner preview#1

osv-scanner

GitHubgoogle/osv-scanner
10.8k15h 44m ago
trivy preview#2

trivy

GitHubaquasecurity/trivy
37.4k1 day ago
grype preview#3

grype

GitHubanchore/grype
12.7k2h 23m ago
syft preview#4

syft

GitHubanchore/syft
9.6k1 day ago
scorecard preview#5

scorecard

GitHubossf/scorecard
5.6k15 days ago
cosign preview#6

cosign

GitHubsigstore/cosign
6.2k5 days ago
in-toto preview#7

in-toto

GitHubin-toto/in-toto
1.0k27 days ago
python-tuf preview#8

python-tuf

GitHubtheupdateframework/python-tuf
1.7k2 days ago
securesystemslib preview#9

securesystemslib

GitHubsecure-systems-lab/securesystemslib
542 days ago
dependency-track preview#10

dependency-track

GitHubdependencytrack/dependency-track
4.1k1 day ago
NewestRelevanceMost popularRecently updated
778 results
advisory-database preview

advisory-database

GitHubpypa/advisory-database

Community-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…

vulnerability-analysisdevsecopsthreat-intelligence+2
3706 days ago
checkov preview

checkov

GitHubbridgecrewio/checkov

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
cloud-infrastructure-securitystatic-analysisvulnerability-scanners+12
8.9k6 days ago
wolfCOSE preview

wolfCOSE

GitHubwolfssl/wolfcose

A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
embedded-systems-securitystatic-analysisencryption-decryption-tools+7
766 days ago
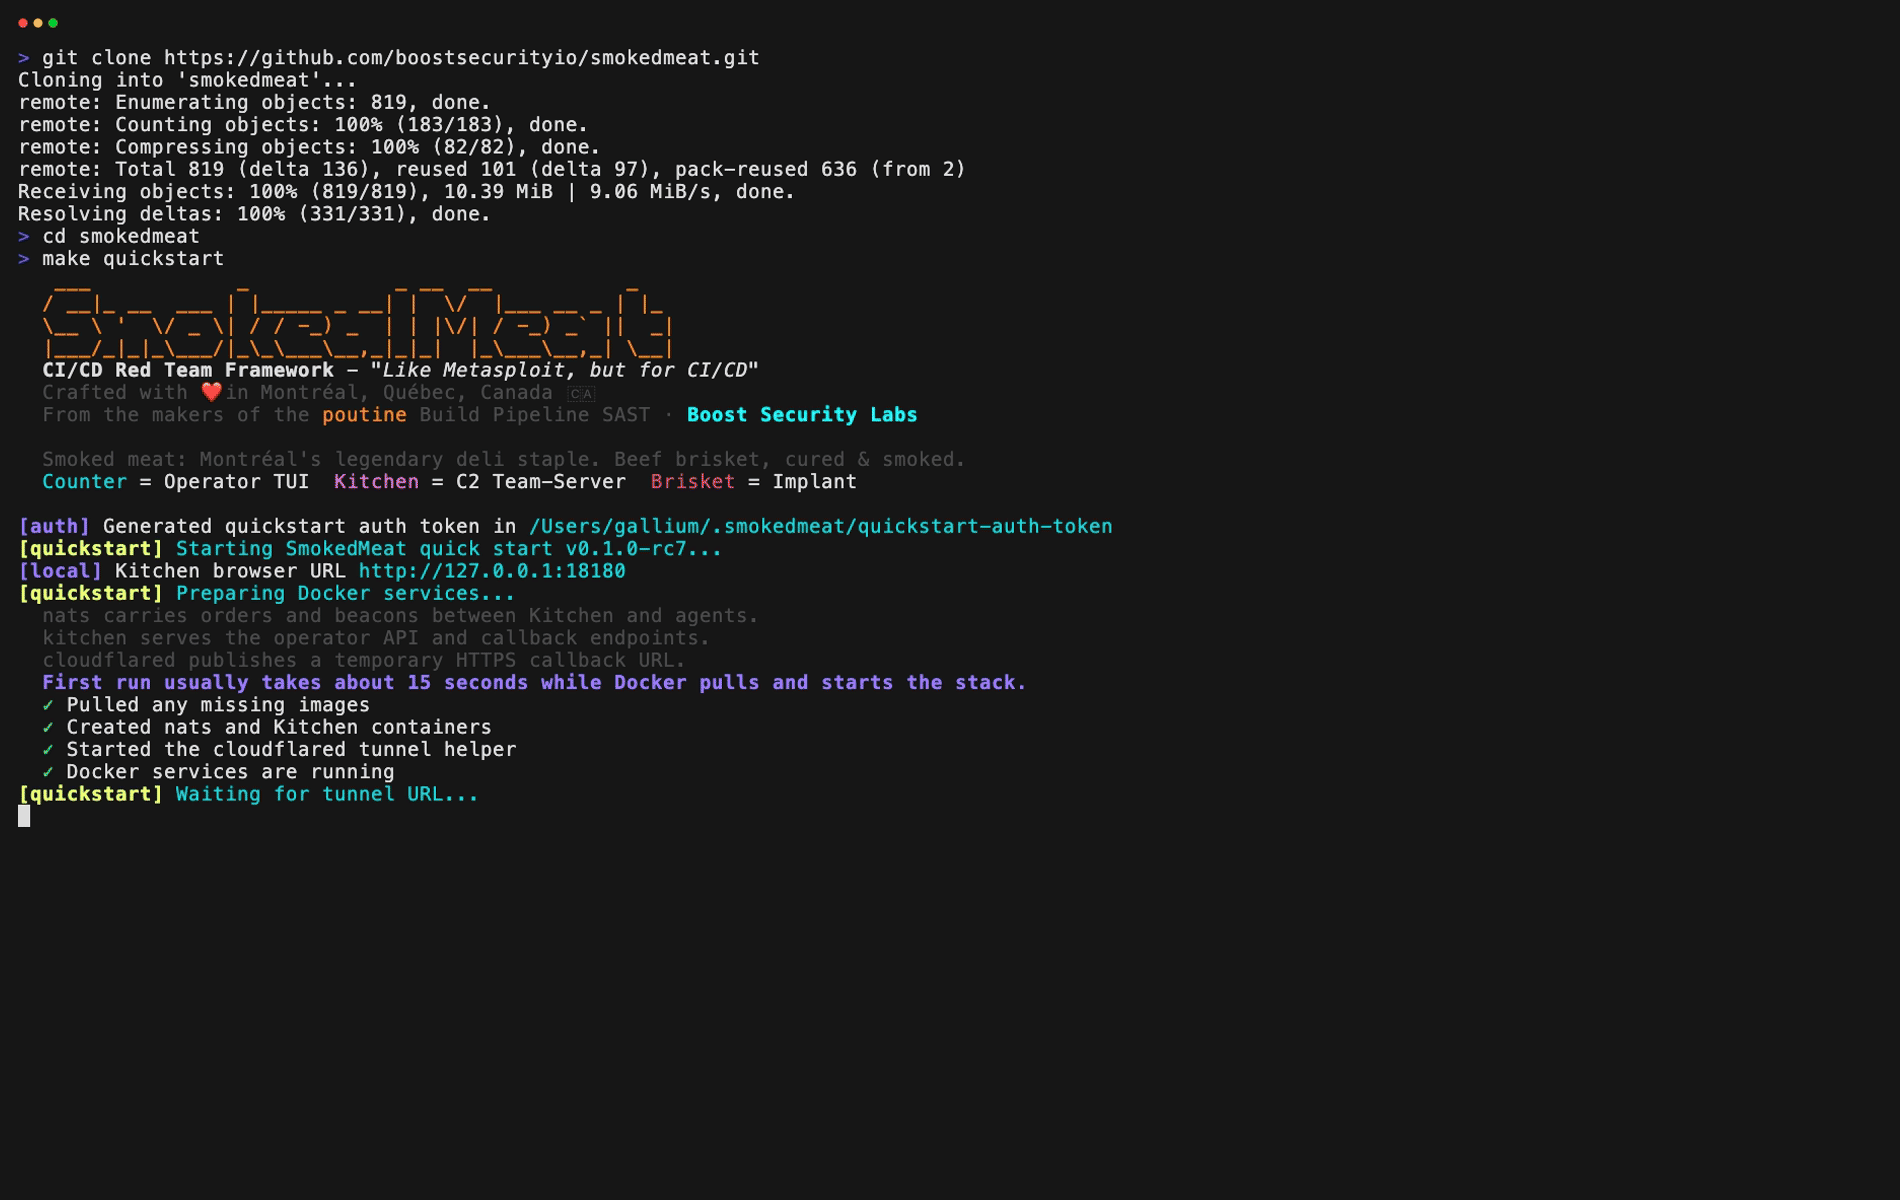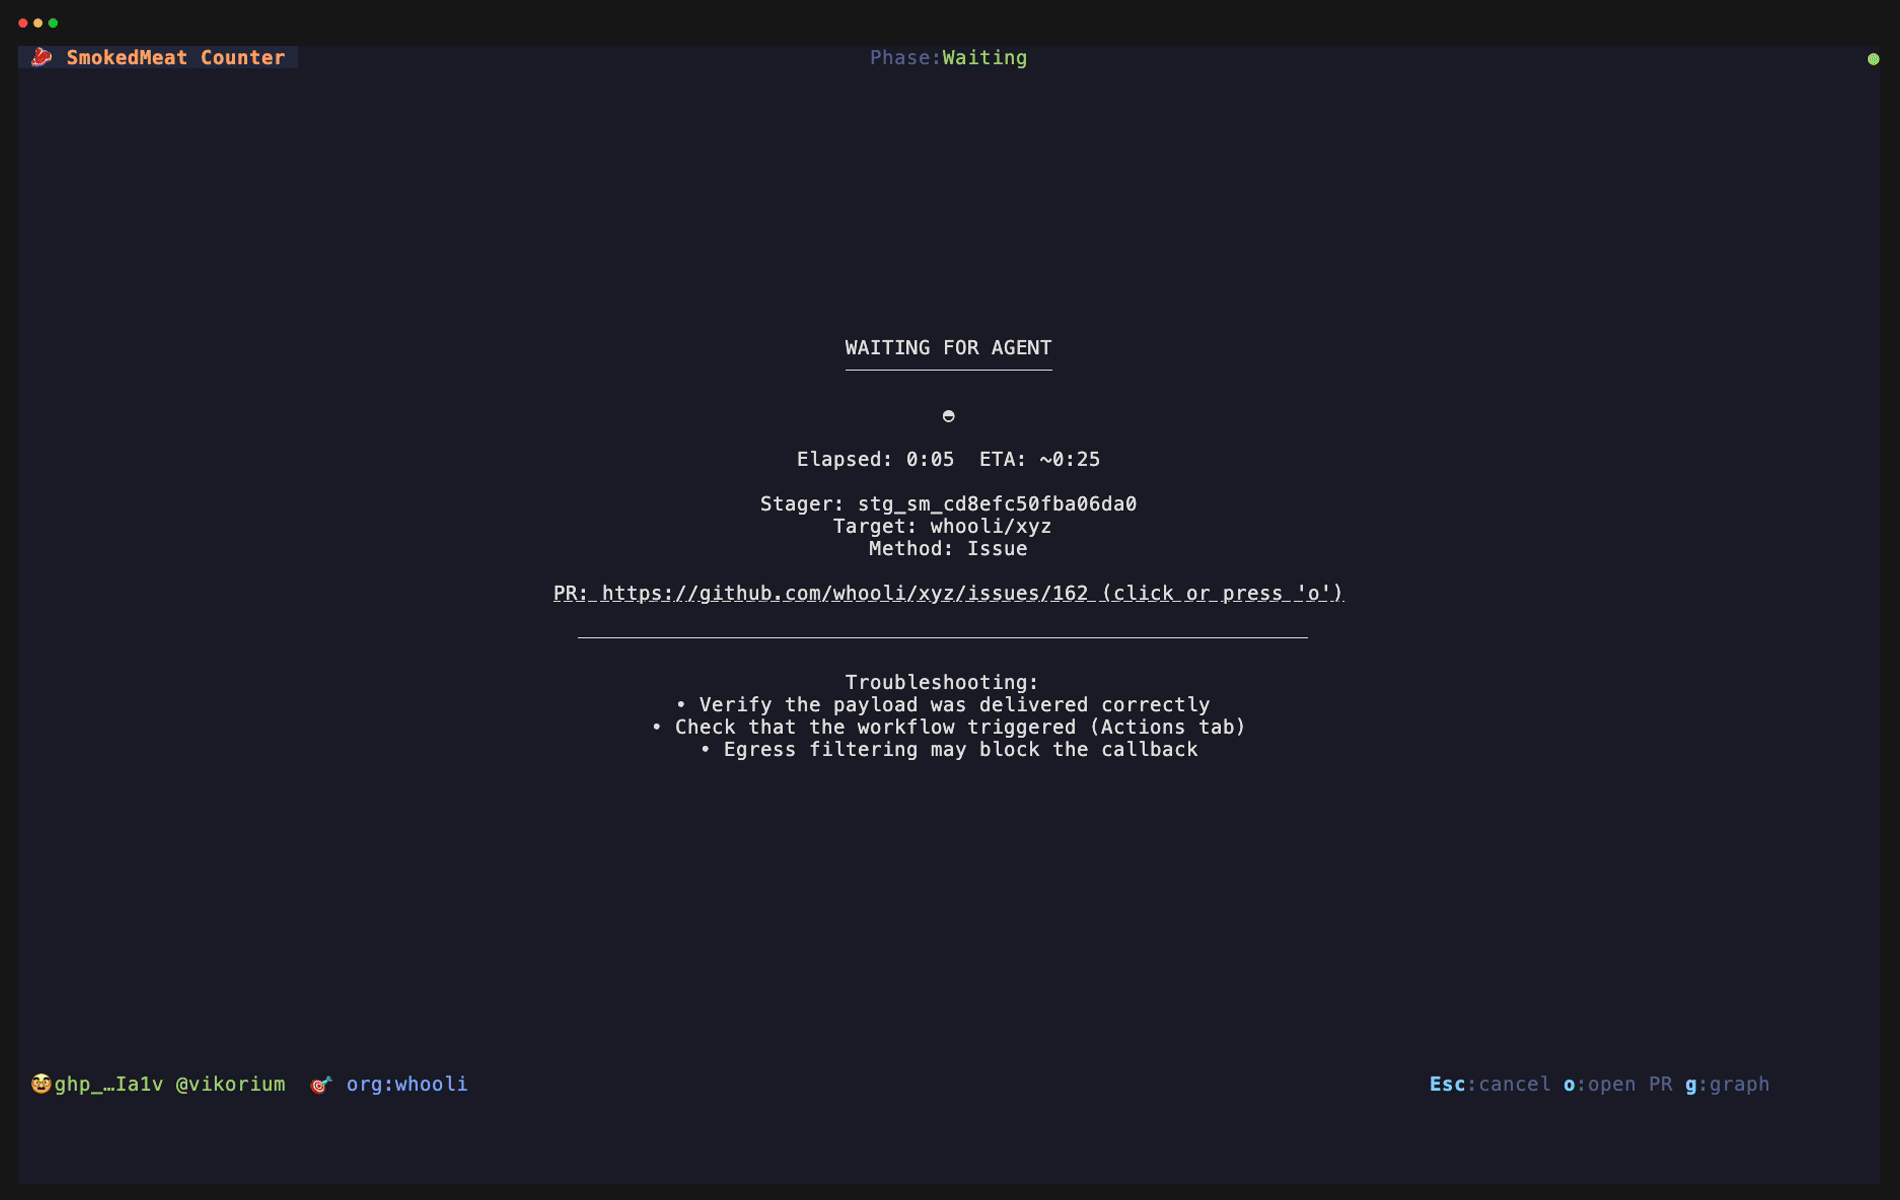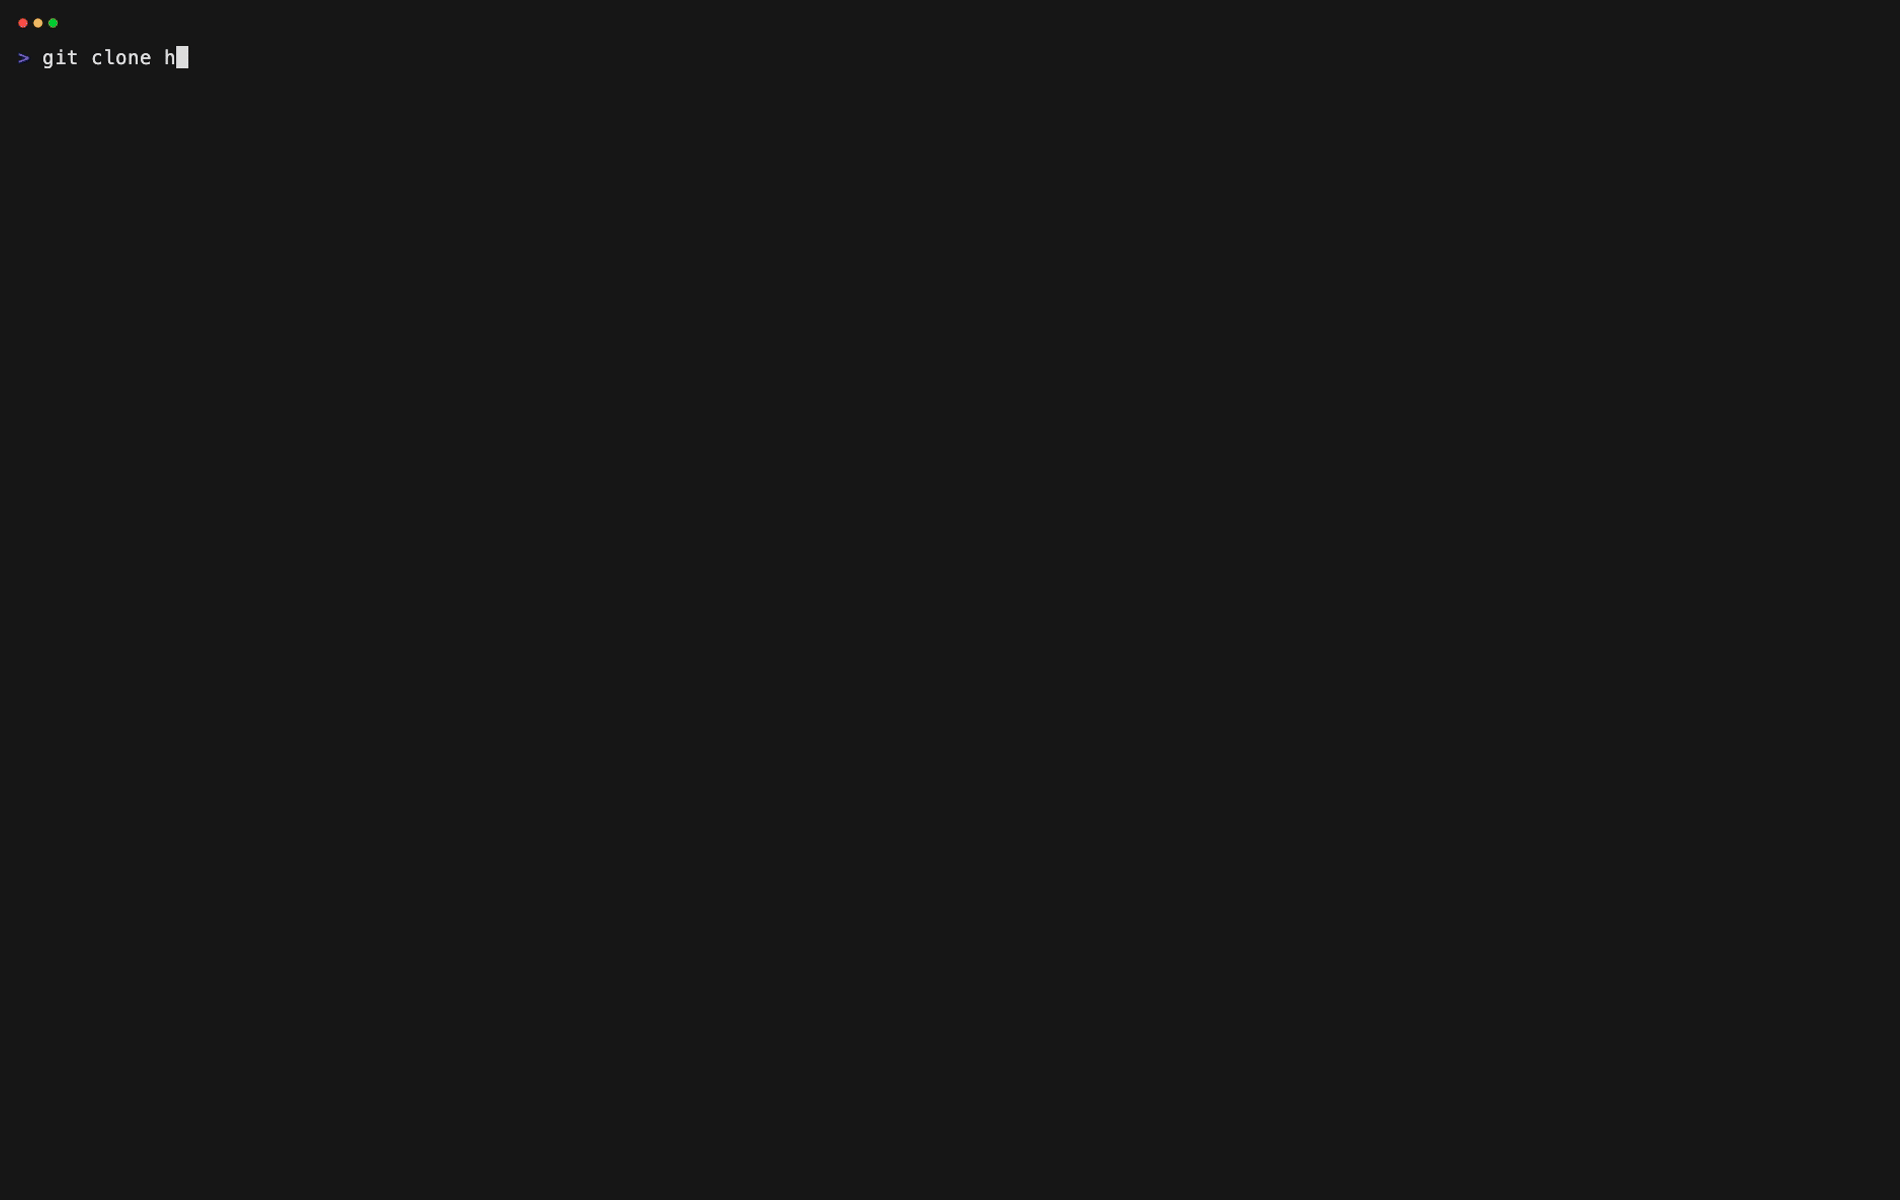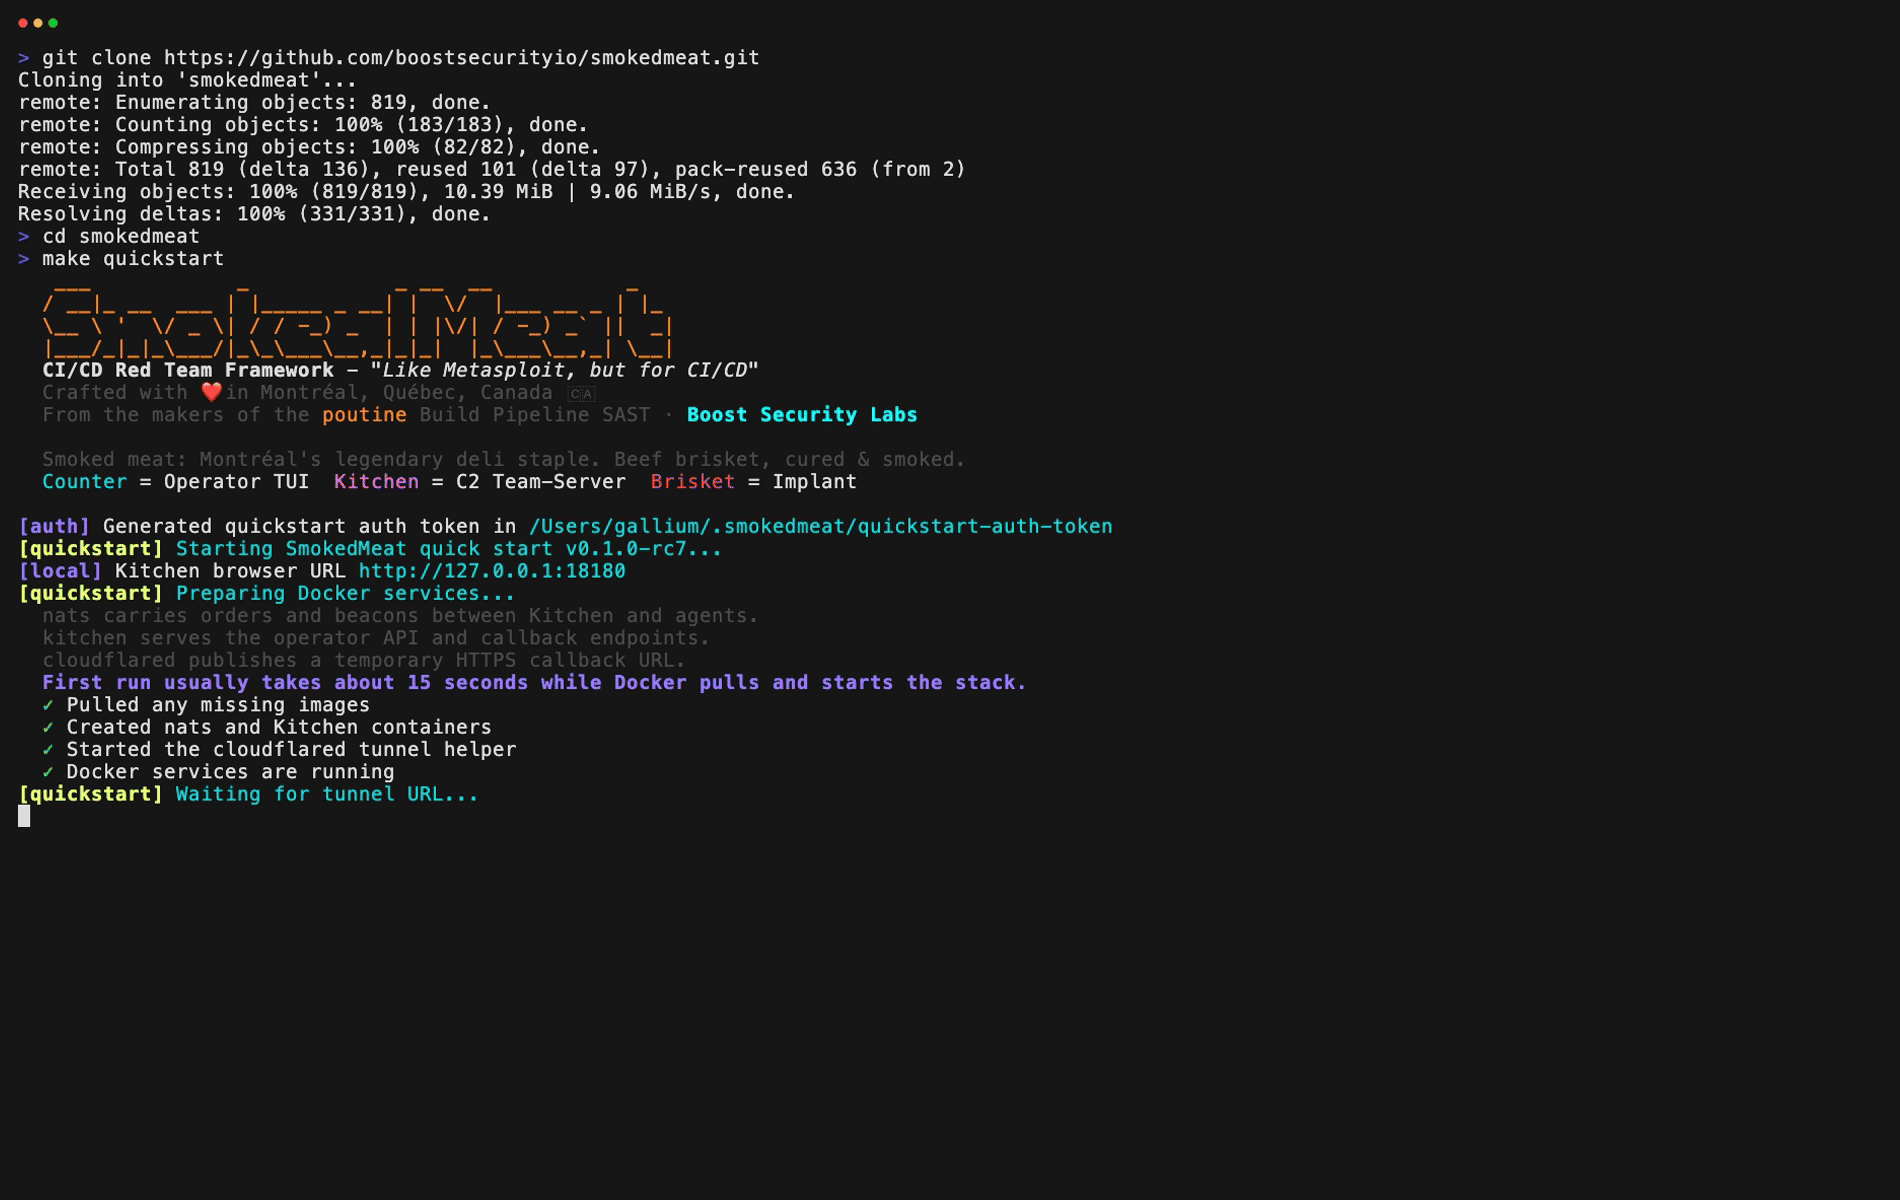
smokedmeat preview

smokedmeat

GitHubboostsecurityio/smokedmeat

A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
penetration-testing-frameworksprivilege-escalationexploit-frameworks+9
3736 days ago
cicd-sensor preview

cicd-sensor

GitLabcicd-sensor/cicd-sensor

eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
forensicscloud-securitydevsecops+3
17 days ago
bigint-buffer-js preview

bigint-buffer-js

GitHubdisley15-collab/bigint-buffer-js

Pure-JS drop-in for [email protected] without the vulnerable native binding (CVE-2025-3194)
defensive-toolsvulnerability-analysiscryptography+2
7 days ago
scopeblind-gateway preview

scopeblind-gateway

GitHubscopeblind/scopeblind-gateway

Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
authentication-authorizationencryption-decryption-toolscryptography+5
97 days ago
packj preview

packj

GitHubossillate-inc/packj

Static and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…
static-analysisvulnerability-scannersdynamic-analysis-sandboxing+3
6917 days ago
GoCD_PoC_Supply_Chain_Attack preview

GoCD_PoC_Supply_Chain_Attack

GitHubhigorgabrieldcf/gocd_poc_supply_chain_attack

CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
payload-generationvulnerability-analysisexploitation+7
7 days ago
tealtiger preview

tealtiger

GitHubagentguard-ai/tealtiger

Powerful protection for AI agents - Open-source security and cost tracking for AI applications

cloud-securitydevsecopsprivacy+8
218 days ago
slsa preview

slsa

GitHubslsa-framework/slsa

Supply-chain Levels for Software Artifacts
supply-chain-securitypapers-researcheducation+1
1.9k8 days ago
TraceTree preview

TraceTree

GitHubtejasprasad2008-afk/tracetree

Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
container-securitydynamic-analysis-sandboxingmalware-analysis+6
428 days ago
sage preview

sage

GitHubgendigitalinc/sage

Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
defensive-toolsphishing-toolsvulnerability-analysis+6
2628 days ago
wrongsecrets-binaries preview

wrongsecrets-binaries

GitHubowasp/wrongsecrets-binaries

Source code for the Binaries of OWASP WrongSecrets

static-analysisvulnerability-analysiscode-analysis+6
118 days ago
log4j-cve-code-search-resources preview

log4j-cve-code-search-resources

GitHubsourcegraph/log4j-cve-code-search-resources

Using code search to help fix/mitigate log4j CVE-2021-44228

vulnerability-analysiscode-analysisthreat-intelligence+3
18 days ago
trajan preview

trajan

GitHubpraetorian-inc/trajan

A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.

static-analysisvulnerability-scannerscode-analysis+7
1768 days ago
modelaudit preview

modelaudit

GitHubpromptfoo/modelaudit

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
static-analysisstatic-code-analysisvulnerability-analysis+8
738 days ago
halo-record preview

halo-record

GitHubbkuan001/halo-record

Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.


forensicssupply-chain-securityincident-response+1
638 days ago
Previous1…567…44Next







