
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 leetxyz/cve-2021-44228-advisories
List of company advisories log4j
 izzyacademy/log4shell-mitigation
Mitigation for Log4Shell Security Vulnerability CVE-2021-44228
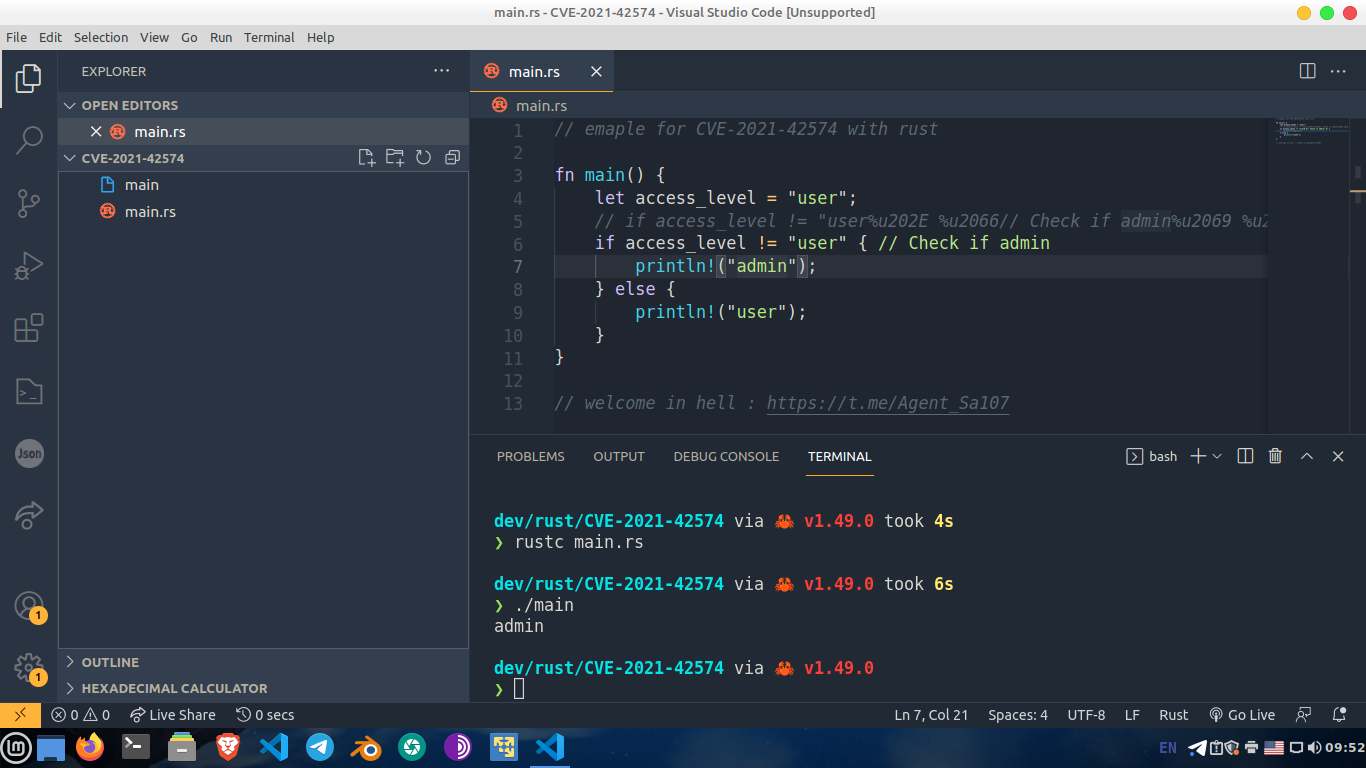 waseeld/cve-2021-42574
Demonstrates the Trojan Source vulnerability (CVE-2021-42574) by generating source code with invisible Unicode control characters that alter compiler…
 oopsiewoopsie/mc-log4j-patcher
CVE-2021-44228 server-side fix for minecraft servers.
 icatalina/cve-2021-43616
Demonstration of CVE-2021-43616: npm `ci` command ignoring package-lock.json, causing unintended dependency version installation and supply-chain…
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 yamory/cve-2021-32804
Docker-based reproduction environment for CVE-2021-32804, a path traversal vulnerability in node-tar affecting npm, with step-by-step exploitation…
 frostsaberx/cve-2020-27955
Git-LFS RCE Test
 frenzymadness/cve-2021-3572
Minimal test repository for CVE-2021-3572, demonstrating a pip dependency confusion vulnerability and its fix across vulnerable and patched versions.
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 atorralba/cve-2021-30005-poc
Proof-of-concept demonstrating arbitrary command execution via malicious virtual environment activation scripts in PyCharm before 2020.3.4,…
 nightwatchcyber/gh_release_test
Demonstration script simulating a supply chain attack through GitHub releases, highlighting the risk of malicious code in release artifacts.
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 aquasecurity/binfinder
Find binary files not installed through package manager
 nccgroup/tpmgenie
TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules
 rauc/rauc-1.5-integration
integration examples for the CVE-2020-25860 fix
 theth1nk3r/cve-2020-27955
cve-2020-27955








