
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 shoucheng3/cov-int
XWiki Commons CVE-2023-31126 v14.10.3 for Coverity analysis
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2018-1002200_3-5
Java library for creating and extracting archives (ZIP, TAR, JAR) with support for various compression formats. Note: version 3.5 contains a fix for…
 shoucheng3/srikanth-lingala__zip4j_cve-2018-1002202_1-3-2
Decompiled source code of zip4j library versions 1.3.2 (vulnerable) and 1.3.3 (fixed) for CVE-2018-1002202 path traversal analysis, part of the…
 shoucheng3/jenkinsci__workflow-cps-global-lib-plugin_cve-2022-25174_544-vff04fa68714d
Exploit for CVE-2022-25174 in Jenkins Pipeline Shared Libraries plugin, demonstrating code injection via crafted library definitions for security…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 shoucheng3/joniles__mpxj_cve-2020-35460_8-3-4
Exploit for CVE-2020-35460 targeting MPXJ project management library, enabling arbitrary code execution via crafted project files in Java, .Net, and…
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…
 beishanxueyuan/cve-2025-48384-test
Reproduction of CVE-2025-48384 demonstrating a Git submodule path traversal vulnerability, with step-by-step commands to recreate the exploit.
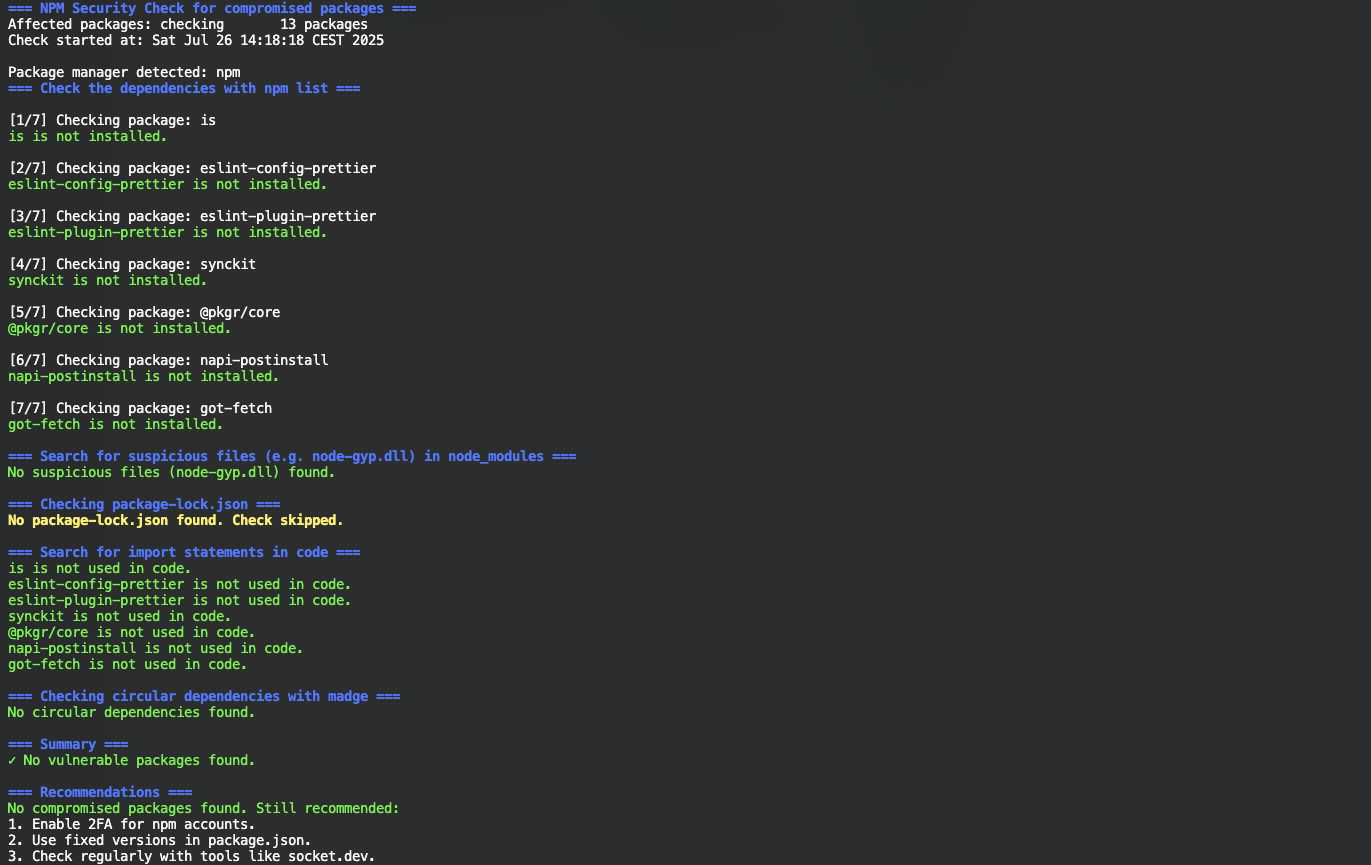 nihilor/cve-2025-54313
Checks projects for compromised packages, suspicious files, and import statements.
 ik-20211125/cve-2025-48384
CVE-2025-48384 PoC
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 iris-sast/zip4j
CWE-Bench-Java CVE-2018-1002202 versions 1.3.2, 1.3.3
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 acheong08/cve-2025-48384
Breaking git with a carriage return and cloning RCE
 arsalanraja987/gradle-cve-2021-29427-demo
gradle cve
 depers-rus/cve-2007-4559
Proof-of-concept demonstrating CVE-2007-4559 path traversal in Python's tarfile module, allowing arbitrary file overwrite via malicious TAR archives.
 ikram124/cve-2024-3094-analysis
Security analysis project: Real-world CVE breakdown








