
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 katekeiroz-dev/golang-x-text
golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24
 getprobo/probo
Open source solutions for SOC2, GDPR, and ISO27001
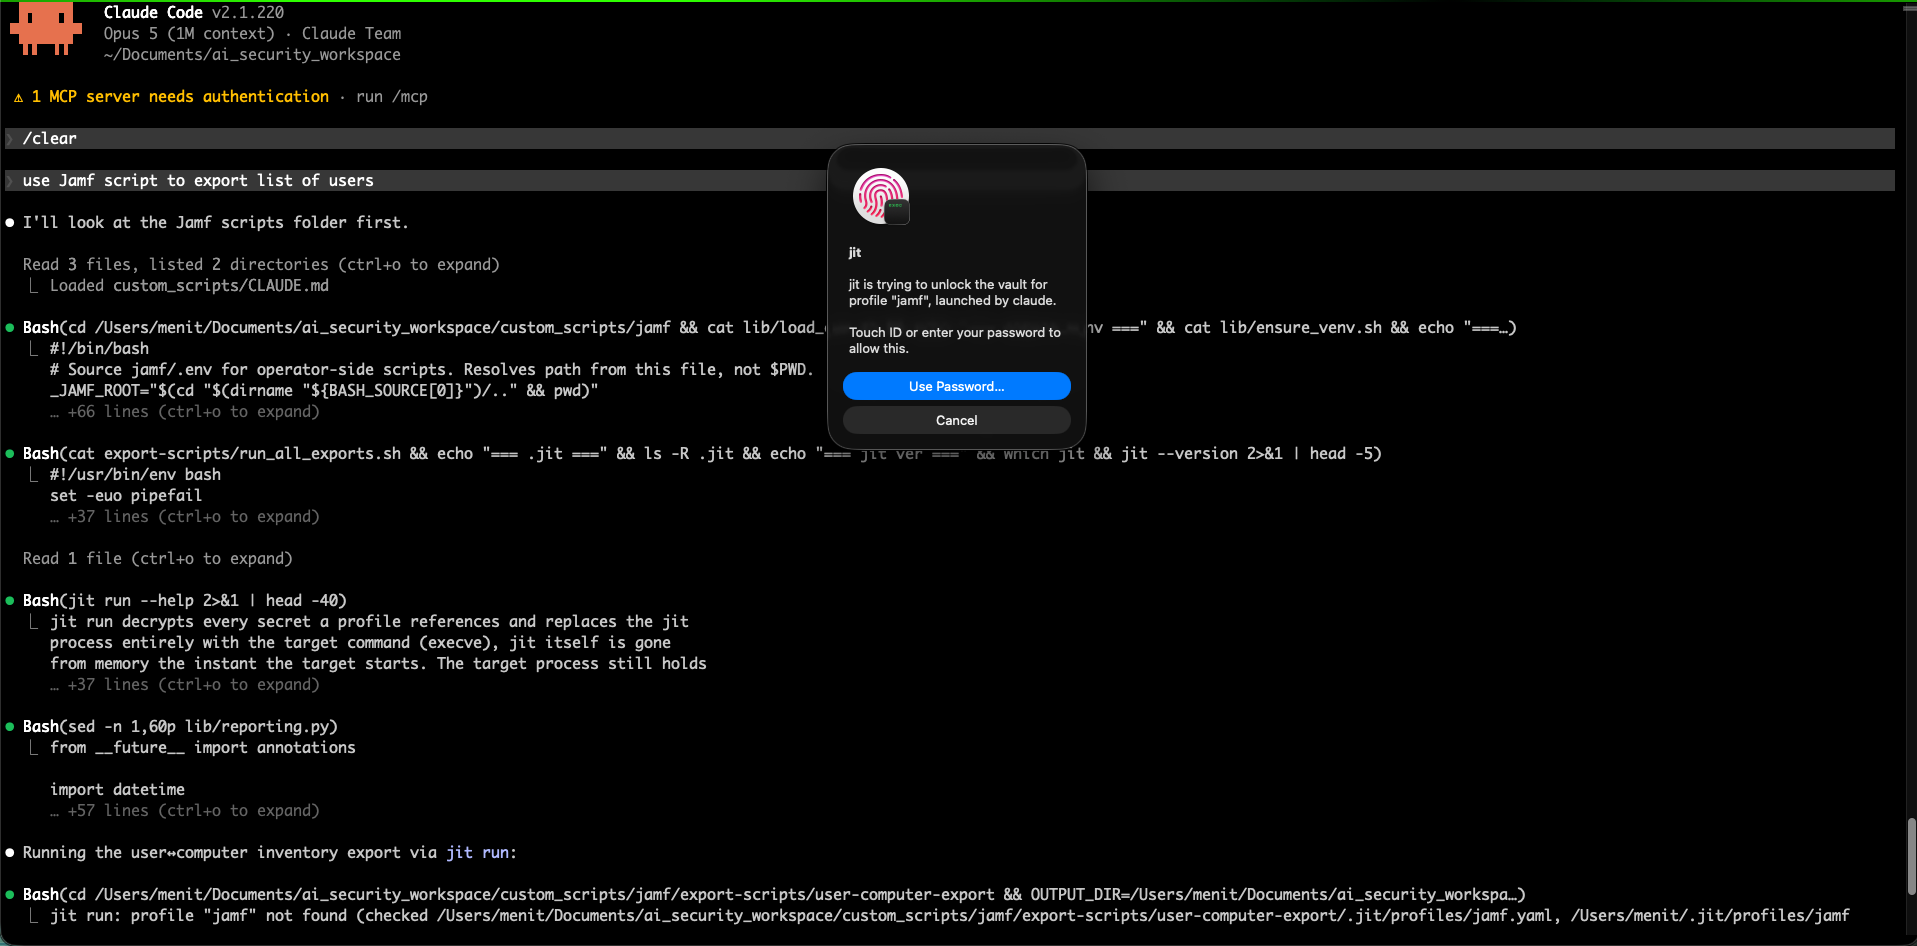 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 namegabevictoire01-sys/cs50-cybersecurity-final-project
CS50 Cybersecurity Final Project - Analysis of CVE-2024-3094
 nichetoolkit/spring-retry-toolkit
spring retry 1.3.x fix with niche toolkit for CVE-2026-41710
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.
 h4wkst3r/blackhat-usa-2022-materials
Presentation materials for my Black Hat USA 2022 Briefing and Arsenal talks
 saku0512/cve-2026-71557-poc
Local proof-of-concept for CVE-2026-71557 demonstrating path traversal in go-git filesystem reference storage, including exploit logic and…
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
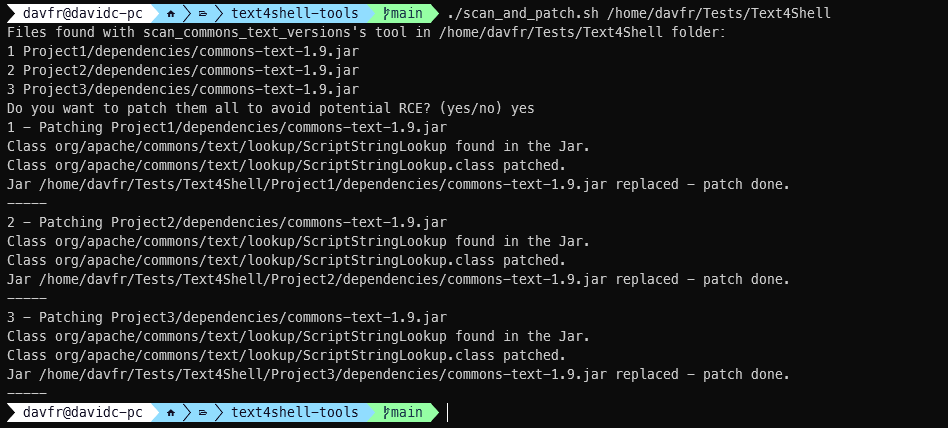 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…








