
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 hackerhermanos/cve-2024-3094_xz_check
This repository contains a Bash script and a one-liner command to verify if a system is running a vulnerable version of the "xz" utility, as…
 ltmthink/cve-2023-51385_test
一个验证对CVE-2023-51385
 scitotec/log4j-recognizer
A Java helper to identify log4j in the current classpath
 atorralba/cve-2021-30005-poc
Proof-of-concept demonstrating arbitrary command execution via malicious virtual environment activation scripts in PyCharm before 2020.3.4,…
 bella-bc/xz-backdoor-cve-2024-3094-check
Verify if your installed version of xz-utils is vulnerable to CVE-2024-3094 backdoor
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 yamory/cve-2021-32804
Docker-based reproduction environment for CVE-2021-32804, a path traversal vulnerability in node-tar affecting npm, with step-by-step exploitation…
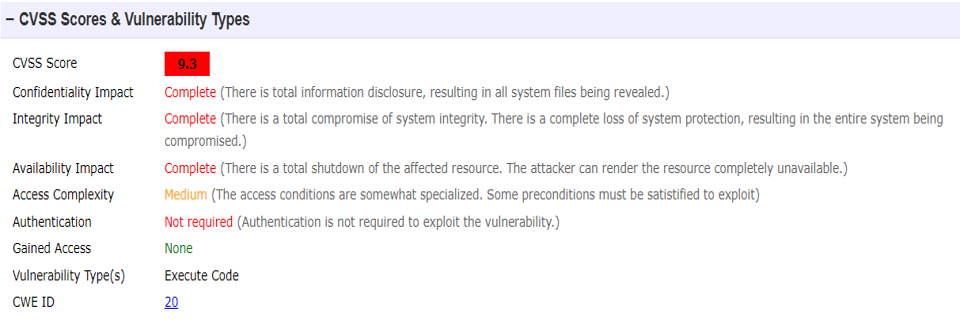 sreeram281997/cve-2022-21668-pipenv-rce-vulnerability
Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 helsecert/cve-2021-44228
Norwegian-language guide to Log4j vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105, CVE-2021-4104, CVE-2019-17571) with detection…
 gcmurphy/chk_log4j
Some siimple checks to see if JAR file is vulnerable to CVE-2021-44228
 depers-rus/cve-2007-4559
Proof-of-concept demonstrating CVE-2007-4559 path traversal in Python's tarfile module, allowing arbitrary file overwrite via malicious TAR archives.
 beishanxueyuan/cve-2025-48384-test
Reproduction of CVE-2025-48384 demonstrating a Git submodule path traversal vulnerability, with step-by-step commands to recreate the exploit.
 theth1nk3r/cve-2020-27955
cve-2020-27955
 xiaoqimikko/pac4j-check
Offline scanner for CVE-2026-29000 (CVSS 10.0) in org.pac4j:pac4j-jwt. Inspects jars/fat-jars directly, so it works where mvn dependency:tree cannot.…
 vulnbe/poc-rebar3
Shell injection in Rebar3
 zebberncve/cve-2026-26830
Advisory for pdf-image ⌯⌲ 10 000 weekly downloads
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…








