
 #1
Tools for simulating human-based attacks (phishing, pretexting, baiting) and testing human factors in security.
Kitploit recommended
 makdosx/wifi-agent
Rogue access point tool for creating captive portals, phishing credentials via cloned login pages, and injecting malware downloads for educational…
 chrismaddalena/cooper
A Python tool for ingesting HTML and producing HTML source suitable for phishing campaigns.
 jofpin/sack
Identify connection of sessions for social engineering attacks.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 g4lb1t/pstf2
Passive Security Tools Fingerprinting Framework
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 fdciabdul/fbchecker
Facebook Mass Account Checker
 husam212/mitmer
Automated man-in-the-middle attack tool.
 zadewg/rius
CVE-2020-20093; 20094; 20095; 20096, 2022-28345 RTLO Injection URI Spoofing
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
 ilektrojohn/creepy-plugins
Plugins for cree.py
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
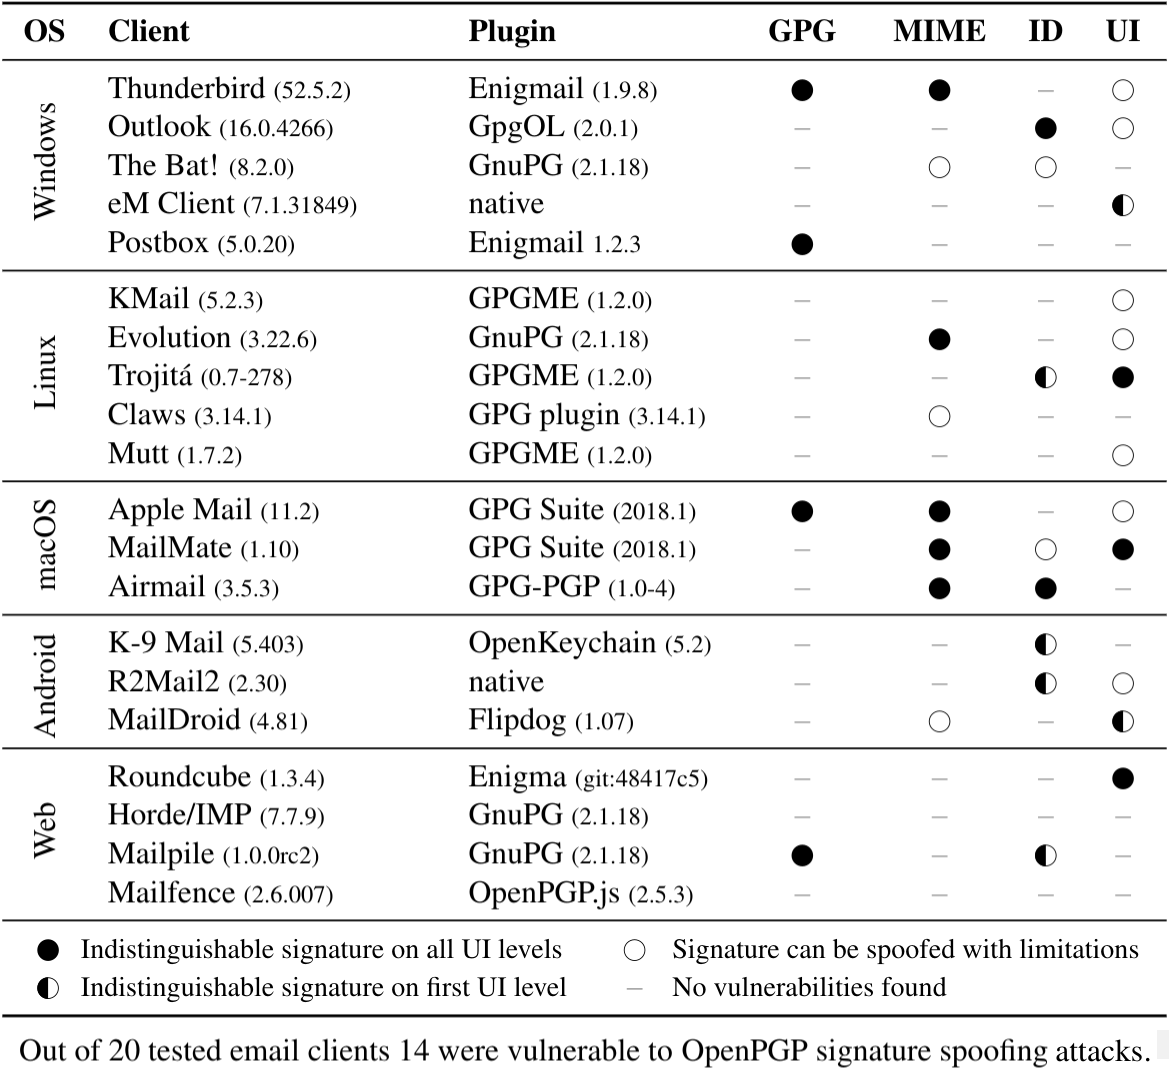 rub-nds/johnny-you-are-fired
Artifacts for the USENIX publication.
 jakabakos/cve-2023-36884-ms-office-html-rce
MS Office and Windows HTML RCE (CVE-2023-36884) - PoC and exploit
 xorond/sudo-snooper
Python script that acts like the original sudo binary to fool users into entering their passwords








