
 #1
Shellcode generation, encoding, obfuscation, and testing frameworks.
Kitploit recommended

 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
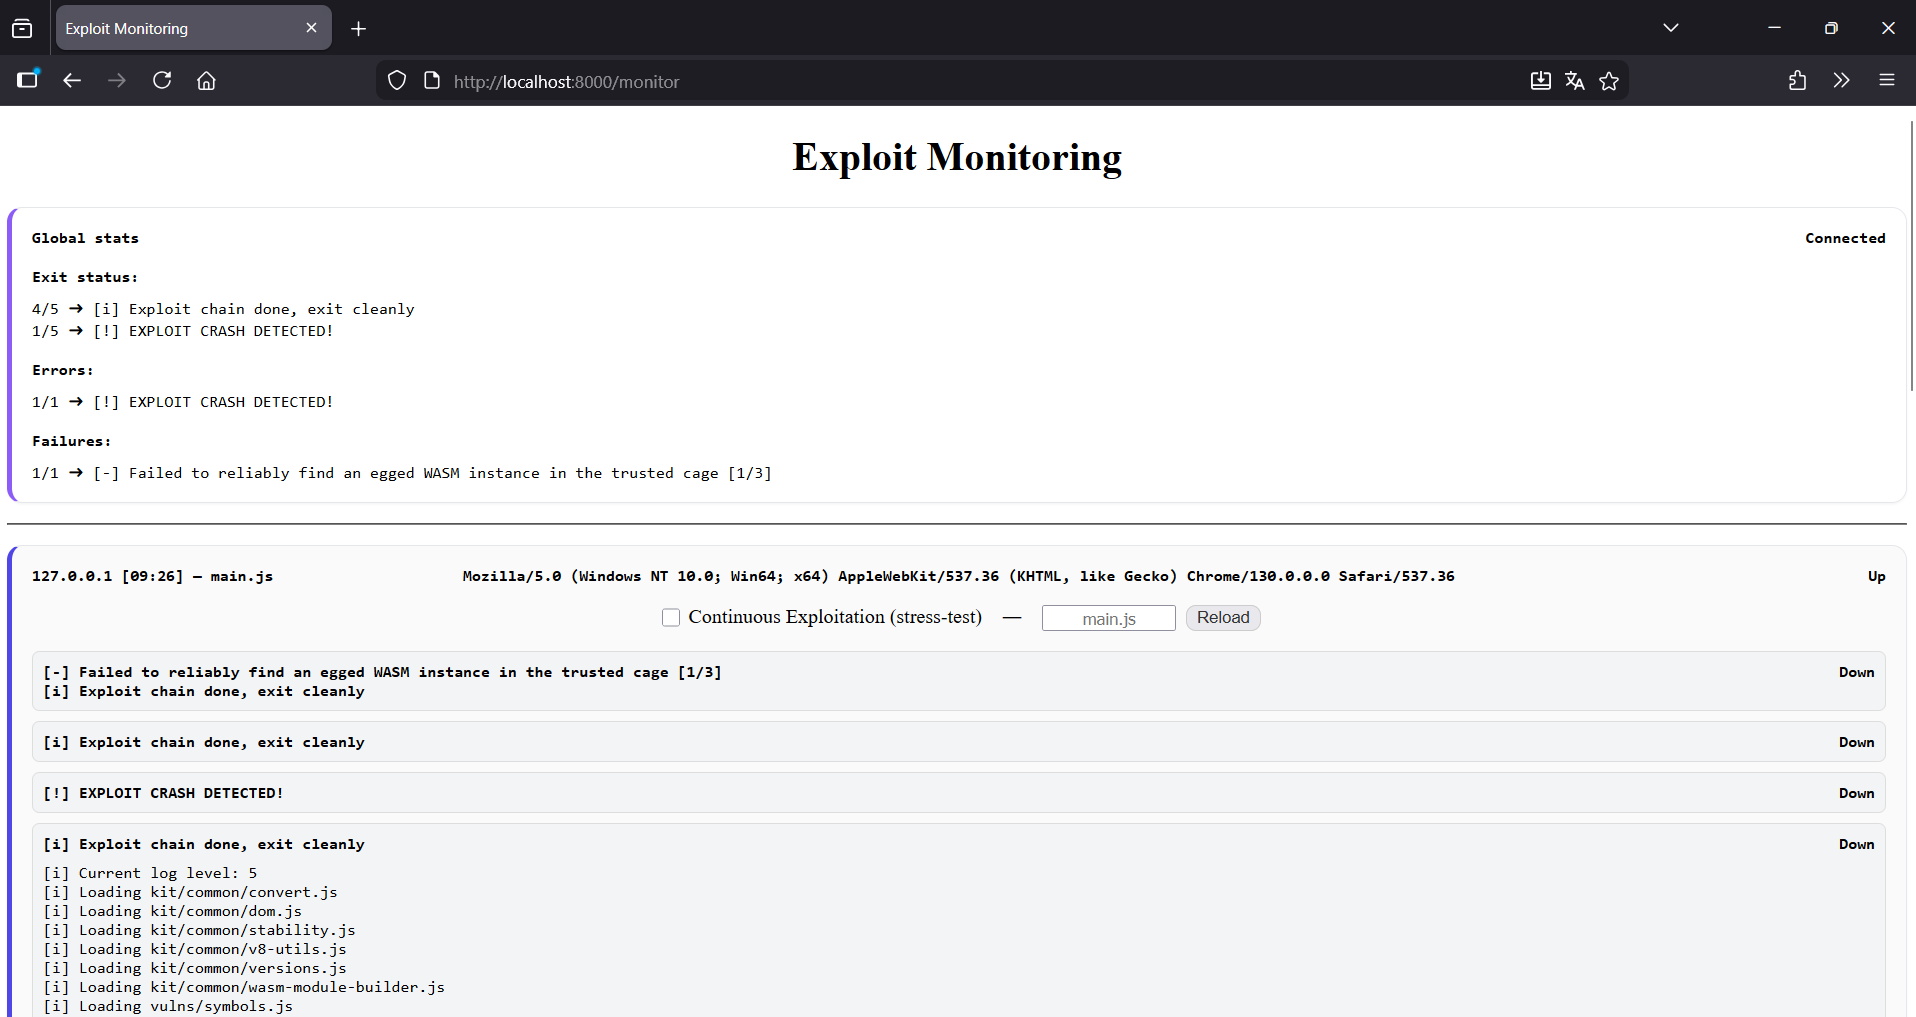 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)

 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.


 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 5alt/zerorat
ZeroRAT是一款windows上的一句话远控








