#1
API key scanning, credential leak detection, and secret management tools.
Kitploit recommended
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
 controlplaneio/truffleproc
truffleproc — hunt secrets in process memory (TruffleHog & gdb mashup)
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 randomrobbiebf/static-file-checker
Checks Djangos /static/staticfiles.json for exposed creds using nuclei
 nccgroup/ccs
Regex-based scanner for detecting hard-coded credentials in codebases, designed for CI/CD integration with suppression comment support and low…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 randomrobbiebf/super-secret-finder
Burp Plugin for Secret Matching
 stacscan/stacs
Static Token And Credential Scanner
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 securing/dumpsterdiver
Tool to search secrets in various filetypes.
 bishopfox/dufflebag
Search exposed EBS volumes for secrets
 bountystrike/bountystrike-sh
Poor (rich?) man's bug bounty pipeline https://dubell.io
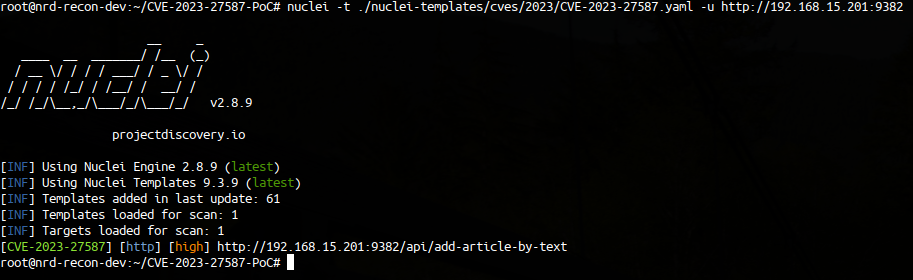 vagnerd/cve-2023-27587-poc
The simple PoC of CVE-2023-27587
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
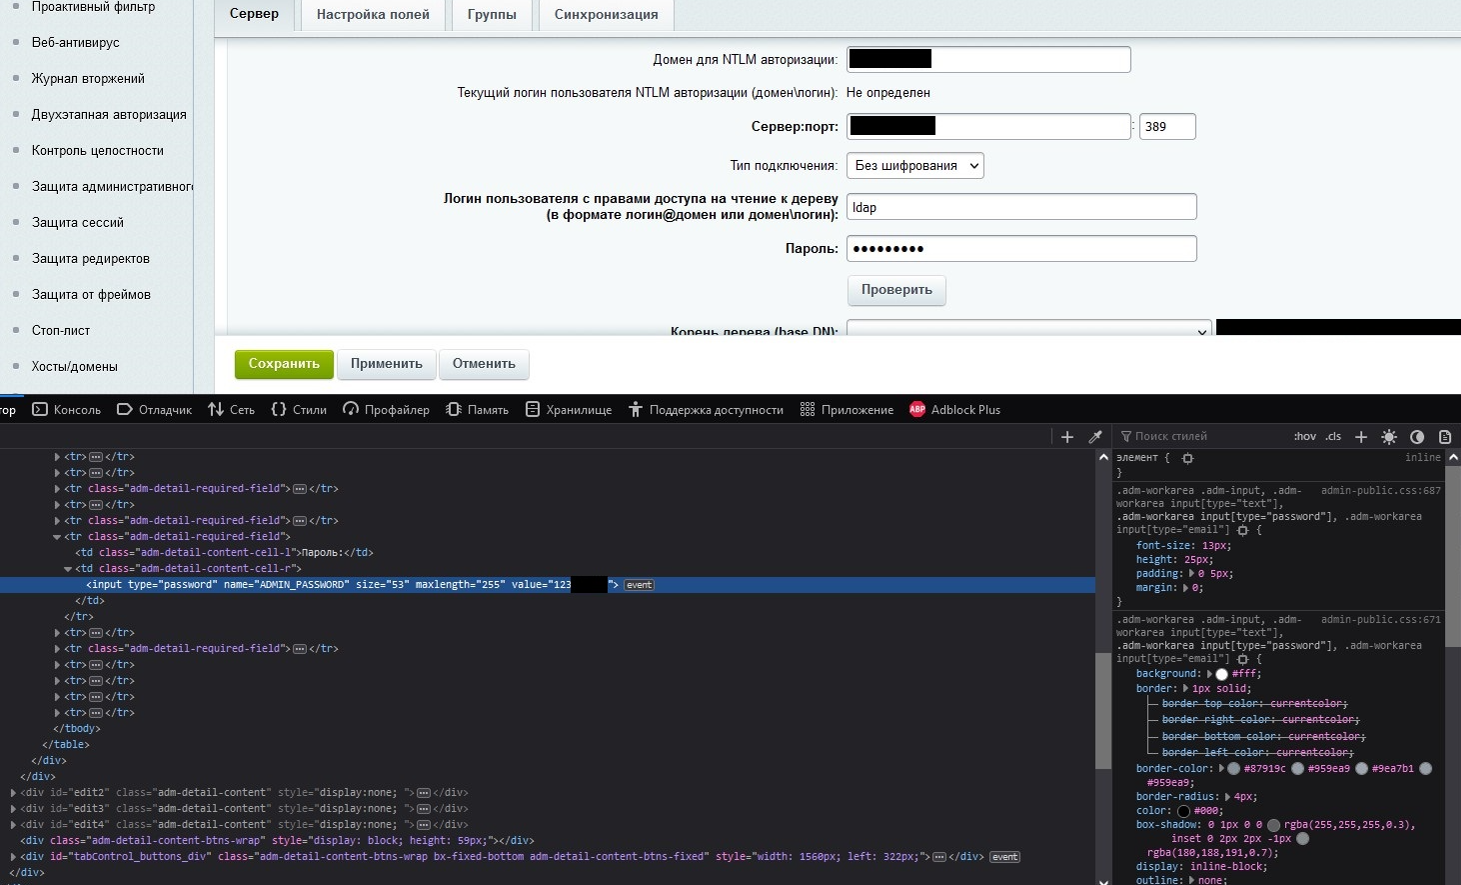 secware-ru/cve-2022-43959
Bitrix Vulnerability CVE-2022-43959