
 #1
API key scanning, credential leak detection, and secret management tools.
Kitploit recommended

 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
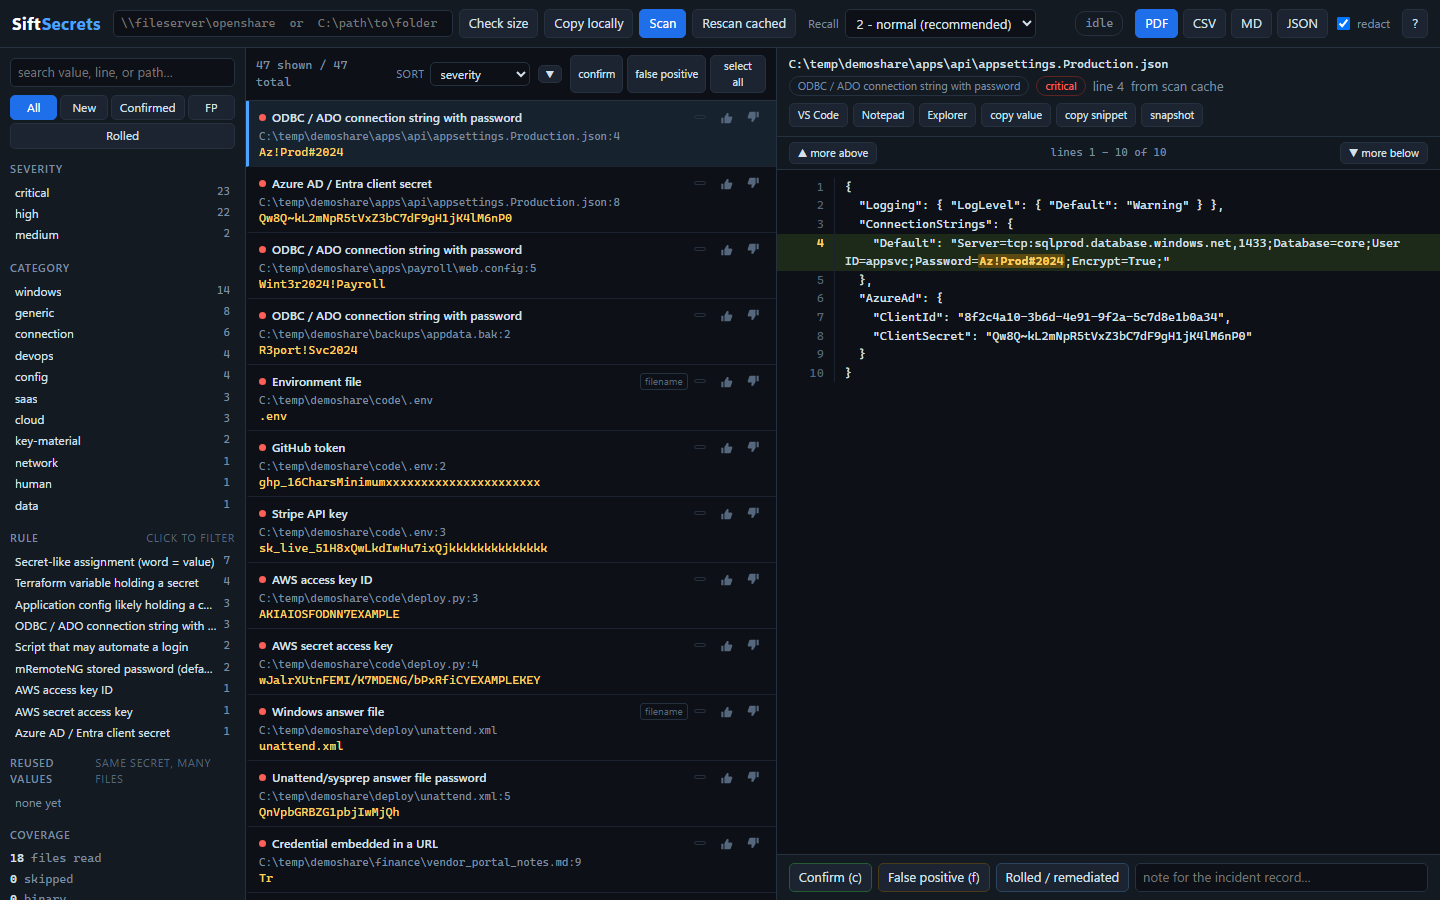 hotstartlabs/sift
Credential and sensitive-data exposure triage for file shares
 phpboyscout/go/redact
Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 ghostpack/deeppass
Hunting for passwords with deep learning
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 h33tlit/secret-regex-list
List of regex for scraping secret API keys and juicy information.
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 controlplaneio/truffleproc
truffleproc — hunt secrets in process memory (TruffleHog & gdb mashup)
 shieldfy/api-security-checklist
Checklist of the most important security countermeasures when designing, testing, and releasing your API
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 papermtn/slack-watchman
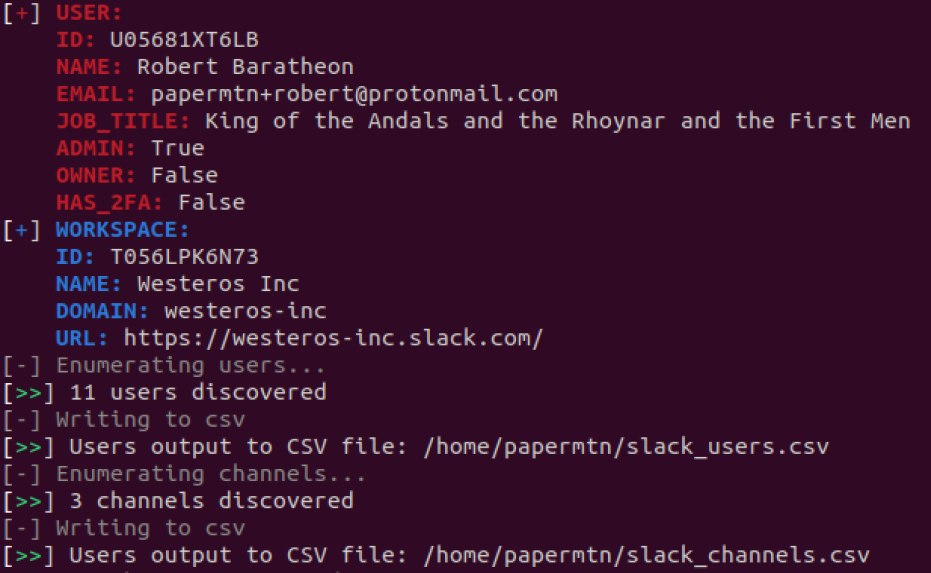
Slack enumeration and exposed secrets detection tool
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !








