
 #1
Tools and libraries for automating security tasks, workflows, and custom tool development.
Kitploit recommended
 mateosec/ghostcatch
Disables AJP connectors to remediate CVE-2020-1938!
 c0rv4x/project-black
Pentest/BugBounty progress control with scanning modules
 jmaddington/drmm-cve-2020-1350-response
Registry-based mitigation script for CVE-2020-1350 Windows DNS Server RCE vulnerability, applying Microsoft's recommended workaround without server…
 orange-cyberdefense/ctf-party
🎏 A library to enhance and speed up script/exploit writing for CTF players
 stevemcilwain/quiver
Quiver is the tool to manage all of your tools for bug bounty hunting and penetration testing.

 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
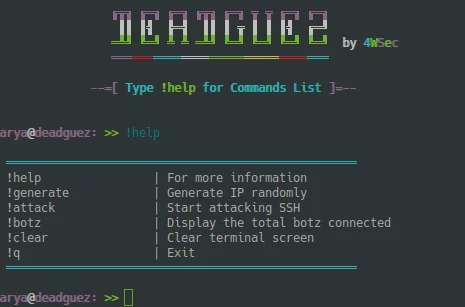 drau6/deadguez
Fast SSH credential scanner that brute-forces SSH logins using sshpass, helping penetration testers identify weak or default credentials on exposed…
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 doug-moody/windows10_cumulative_updates_powershell
Powershell to patch CVE-2020-0601 . Complete security rollup for Windows 10 1507-1909
 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 chayim/ghostcheck-cve-2015-0235
A check for GHOST; cve-2015-0235
 guokers/aioscan_cve-2020-0796
基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
 ecapuano/web-traffic-generator
A quick and dirty HTTP/S "organic" traffic generator.
 1n3/powerexfil
A collection of data exfiltration scripts for Red Team assessments.








