
 #1
Tools and libraries for automating security tasks, workflows, and custom tool development.
Kitploit recommended
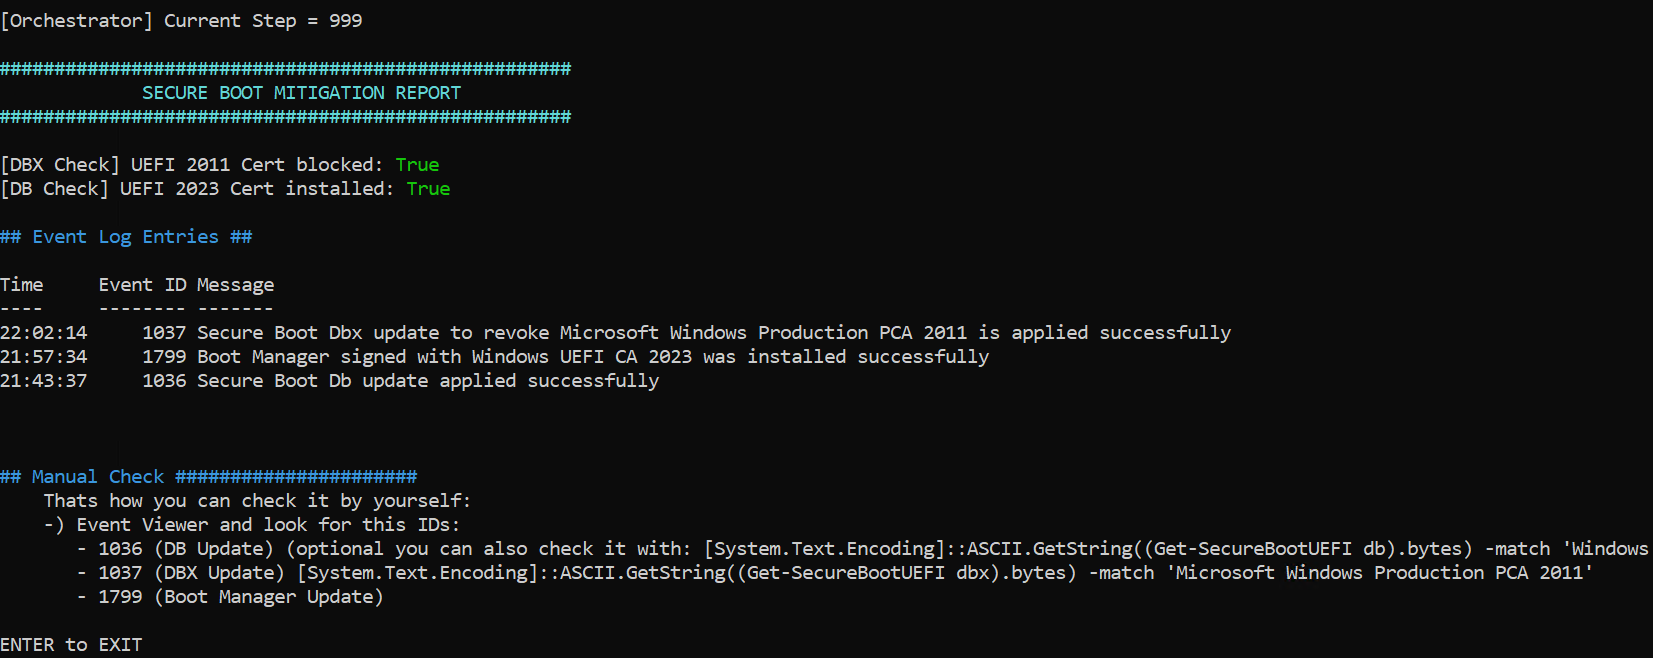
 v1ckxy/orchestrated-powershell-for-cve-2023-24932-en
English translation
 jmaddington/drmm-cve-2020-1350-response
Registry-based mitigation script for CVE-2020-1350 Windows DNS Server RCE vulnerability, applying Microsoft's recommended workaround without server…
 hello4r1end/patch_cve-2023-22809
Automated Bash script to patch CVE-2023-22809 by installing the latest sudo version, mitigating a local privilege-escalation vulnerability on Linux…
 chessredoffsec/cve-2023-26209
Python script with a Tkinter GUI for sending automated payloads of configurable size to a login endpoint, designed for educational testing of server…
 tobiass1402/cve-2021-3438
Detection and remediation for CVE-2021-3438 with Powershell
 cipolone95/cve-2019-1619
Powershell Script to build token for CVE-2019-1619

 toxy4ny/php2shell-checker
Read-only PHP2Shell package checker for Debian 12/13 (CVE-2026-109618, CVE-2026-109619).
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 avprince26/copy-fail-cve-2026-31431-python-golfing
Python golfing challenge for copy.golf, focusing on crafting minimal code to replicate a specific CVE-related behavior.
 noraj/ctf-party
:triangular_flag_on_post: A CLI tool & library to enhance and speed up script/exploit writing with string conversion/manipulation.
 th3xace/screen_killer
This script was developed to track progress for reporting (capture screenshot, commands and outputs) during pentest engagement and OSCP.
 tarraschk/cve-2023-36884-checker
Script to check for CVE-2023-36884 hardening
 aedoo/cve-2018-2628-multithreading
WebLogic WLS核心组件反序列化漏洞多线程批量检测脚本 CVE-2018-2628-MultiThreading
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 keysau/get-log4j-windows.ps1
Identifying all log4j components across all windows servers, entire domain, can be multi domain. CVE-2021-44228
 nkeshawarz/cve-2023-46604-rce
Python-based remote code execution exploit for Apache ActiveMQ deserialization vulnerability (CVE-2023-46604) with multi-threaded scanning and XML…
 guibacellar/penel
[Powershell with Embedded .NET Library] Program that prepares a .NET DLL Library to run embedded in Powershell Script
 mav3r1ck0x1/chrome-and-edge-version-dumper
Powershell script that dumps Chrome and Edge version to a text file in order to determine if you need to update due to CVE-2022-1096








