
 #1
Tools for assessing and securing Supervisory Control and Data Acquisition (SCADA) and Industrial Control Systems (ICS).
Kitploit recommended

 securifera/cve-2016-3962-exploit
CVE-2016-3962-Exploit
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
 yanissec/cve-2018-7849
CVE-2018-7849
 manuelsantosiglesias/cve-2021-31630
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
 thezdi/poc
Collection of proof-of-concept exploits and vulnerability research artifacts published by Trend Micro's Zero Day Initiative, covering SCADA, RPC, and…
 murrez/cve-2026-8065
Python PoC for CVE-2026-8065: fingerprints Hitachi Energy RTU500 devices and probes firmware update endpoints for unauthenticated upload, with check,…
 al4n4n/cve-2026-58115
PoC, non-destructive scanner, Docker lab, PCAP and Suricata/Sigma detection rules for CVE-2026-58115, unauthenticated root RCE via the Node-RED admin…
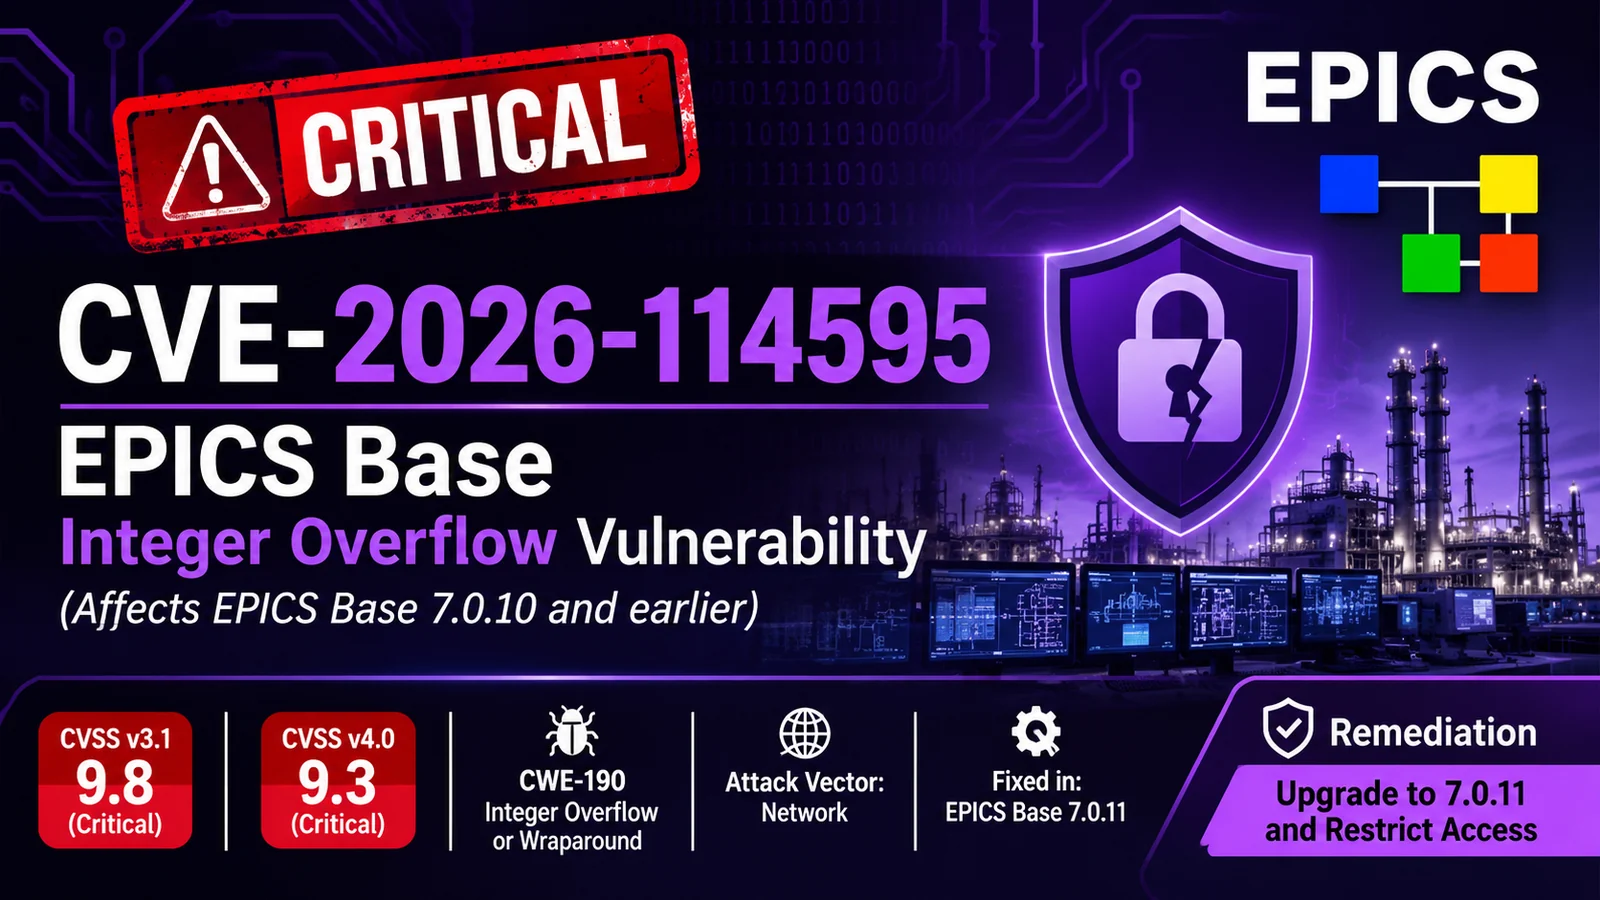 ashrafzaryouh/cve-2026-114595
Advisory for CVE-2026-114595, a critical integer overflow in EPICS Base (≤7.0.10) enabling memory corruption, DoS, and potential unauthenticated RCE;…
 bishopfox/icsscanner
A safety-first vulnerability scanner for ICS/OT protocols.








