
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended
 teutekeune/ibssloader
Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…
 humoud/apksneeze
A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 jprx/cve-2024-54507
Proof-of-concept exploit for CVE-2024-54507, an integer type confusion vulnerability in XNU kernel, with technical writeup and exploitation details.
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 keowu/sjcam
Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 malwaretech/phasedump
Python tool for decrypting W32/Phase modules
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 hackyangwen-lgtm/rmg-s9180-fzg1
Root My Galaxy SM-S9180 (dm3q) S9180ZHS8FZG1 payload port - CVE-2026-43499 + KernelSU LKM
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 fuzzysecurity/cassowary-cve-2024-23222-x86_64
Adaptation of Cassowary CVE-2024-23222 for Linux x86_64
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 dest-3/cve-2023-46012
LINKSYS AC1900 EA7500v3 IGD UPnP Stack Buffer Overflow Remote Code Execution Vulnerability
 nccgroup/zipdefrag
Presented at Recon Montreal 2018
 baba01hacker666/cve-2026-23111
Linux Kernel nf_tables Use-After-Free (CVE-2026-23111) — LPE PoC
 xrzcc/s26-m1q-ghostlock-selinux
GhostLock CVE-2026-43499 research for Galaxy S26 (SM-S942U1/m1q): SELinux Permissive achieved, KASLR + tracefs port, uid=0 boundary documented
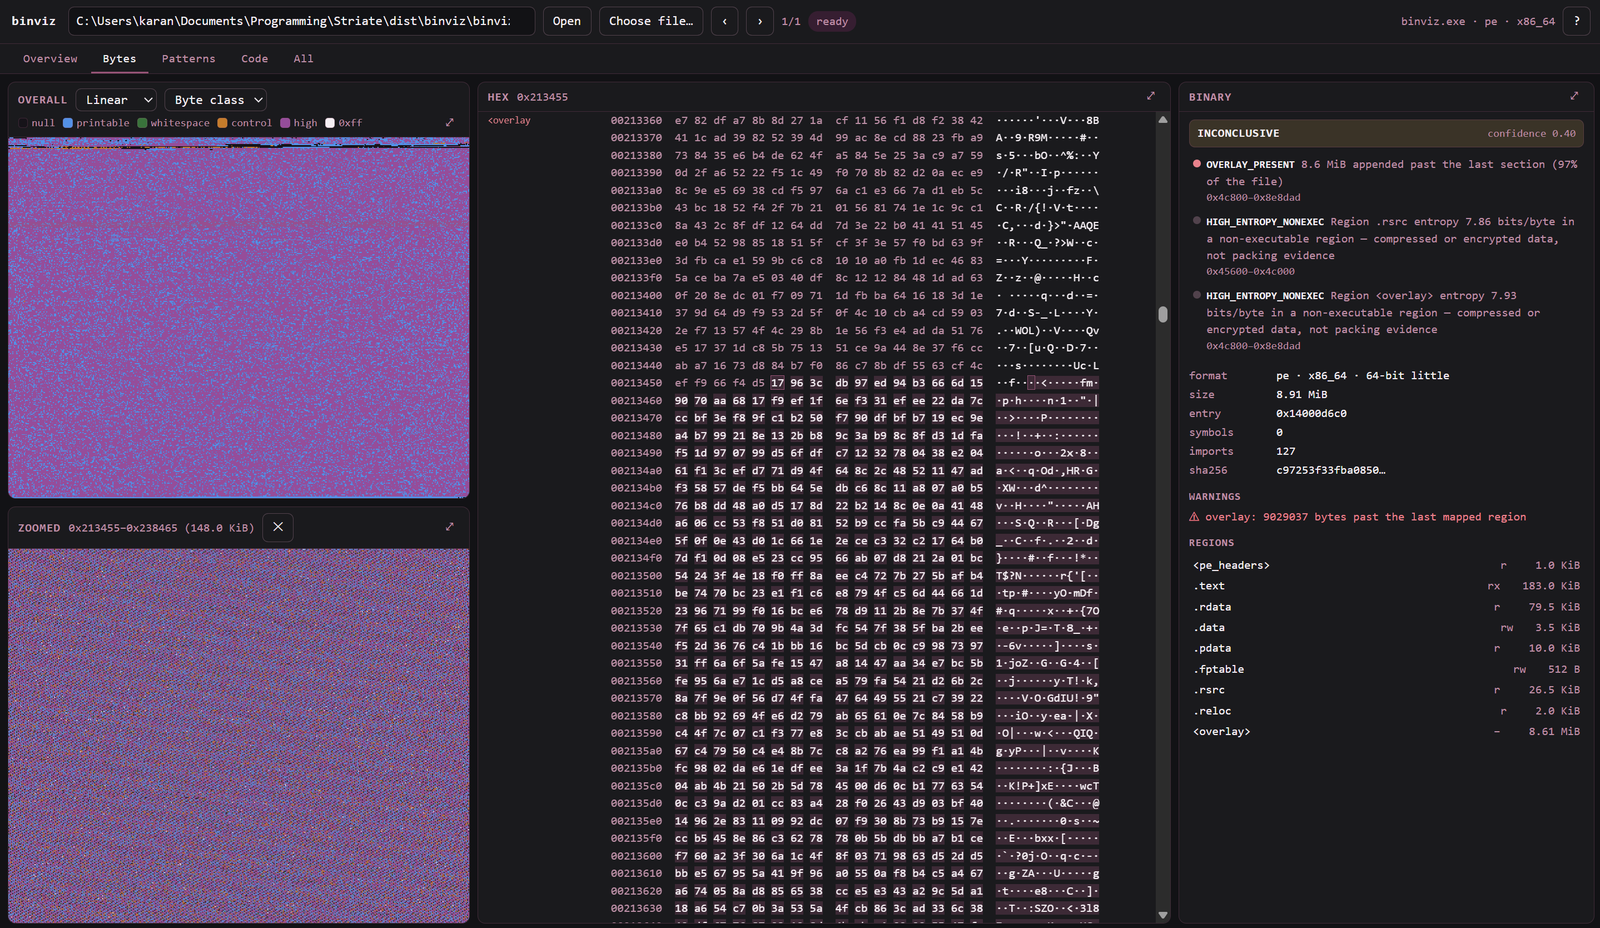 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.








