
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended

 nccgroup/proxmark3-amiimicyou
Proxmark3 Amiibo simulator as shown at Recon Montreal 2018
 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data
 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 cxiao/rust-reversing-workshop-recon-2024
Slides and files for the Reversing Rust Binaries: One step beyond strings workshop at REcon 2024, presented on June 28, 2024.
 bronils/aotopsy
Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…
 feiman55/cve-2026-98260-ghostkey
GhostKey - CVE-2026-98260 一键提权工具(Shizuku + NDK Native)
 catern/rsyscall
Process-independent interface to Linux system calls
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 jackdoe/pico2-swd-riscv
SWD debug probe library for RP2350 RISC-V cores. Provides halt/resume/step, register and memory access, code execution, and instruction tracing over…
 0x33c0unt/cve-2024-21633
MobSF Remote code execution (via CVE-2024-21633)
 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
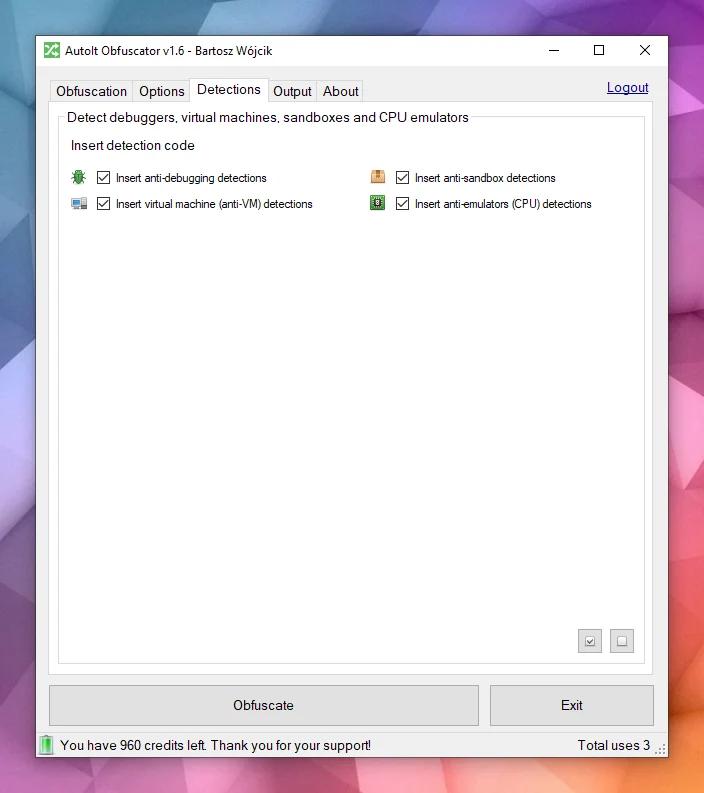 pelock/autoit-obfuscator
Obfuscates AutoIt scripts to protect source code from analysis, reverse engineering, and decompilation using advanced obfuscation and polymorphic…
 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities








