#1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended

 tomer8007/widevine-l3-decryptor
A Chrome extension that demonstrates bypassing Widevine L3 DRM
 mrakovic-org/nashavm
Nasha is a Virtual Machine for .NET files and its runtime was made in C++/CLI
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 taviso/avscript
Avast JavaScript Interactive Shell
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
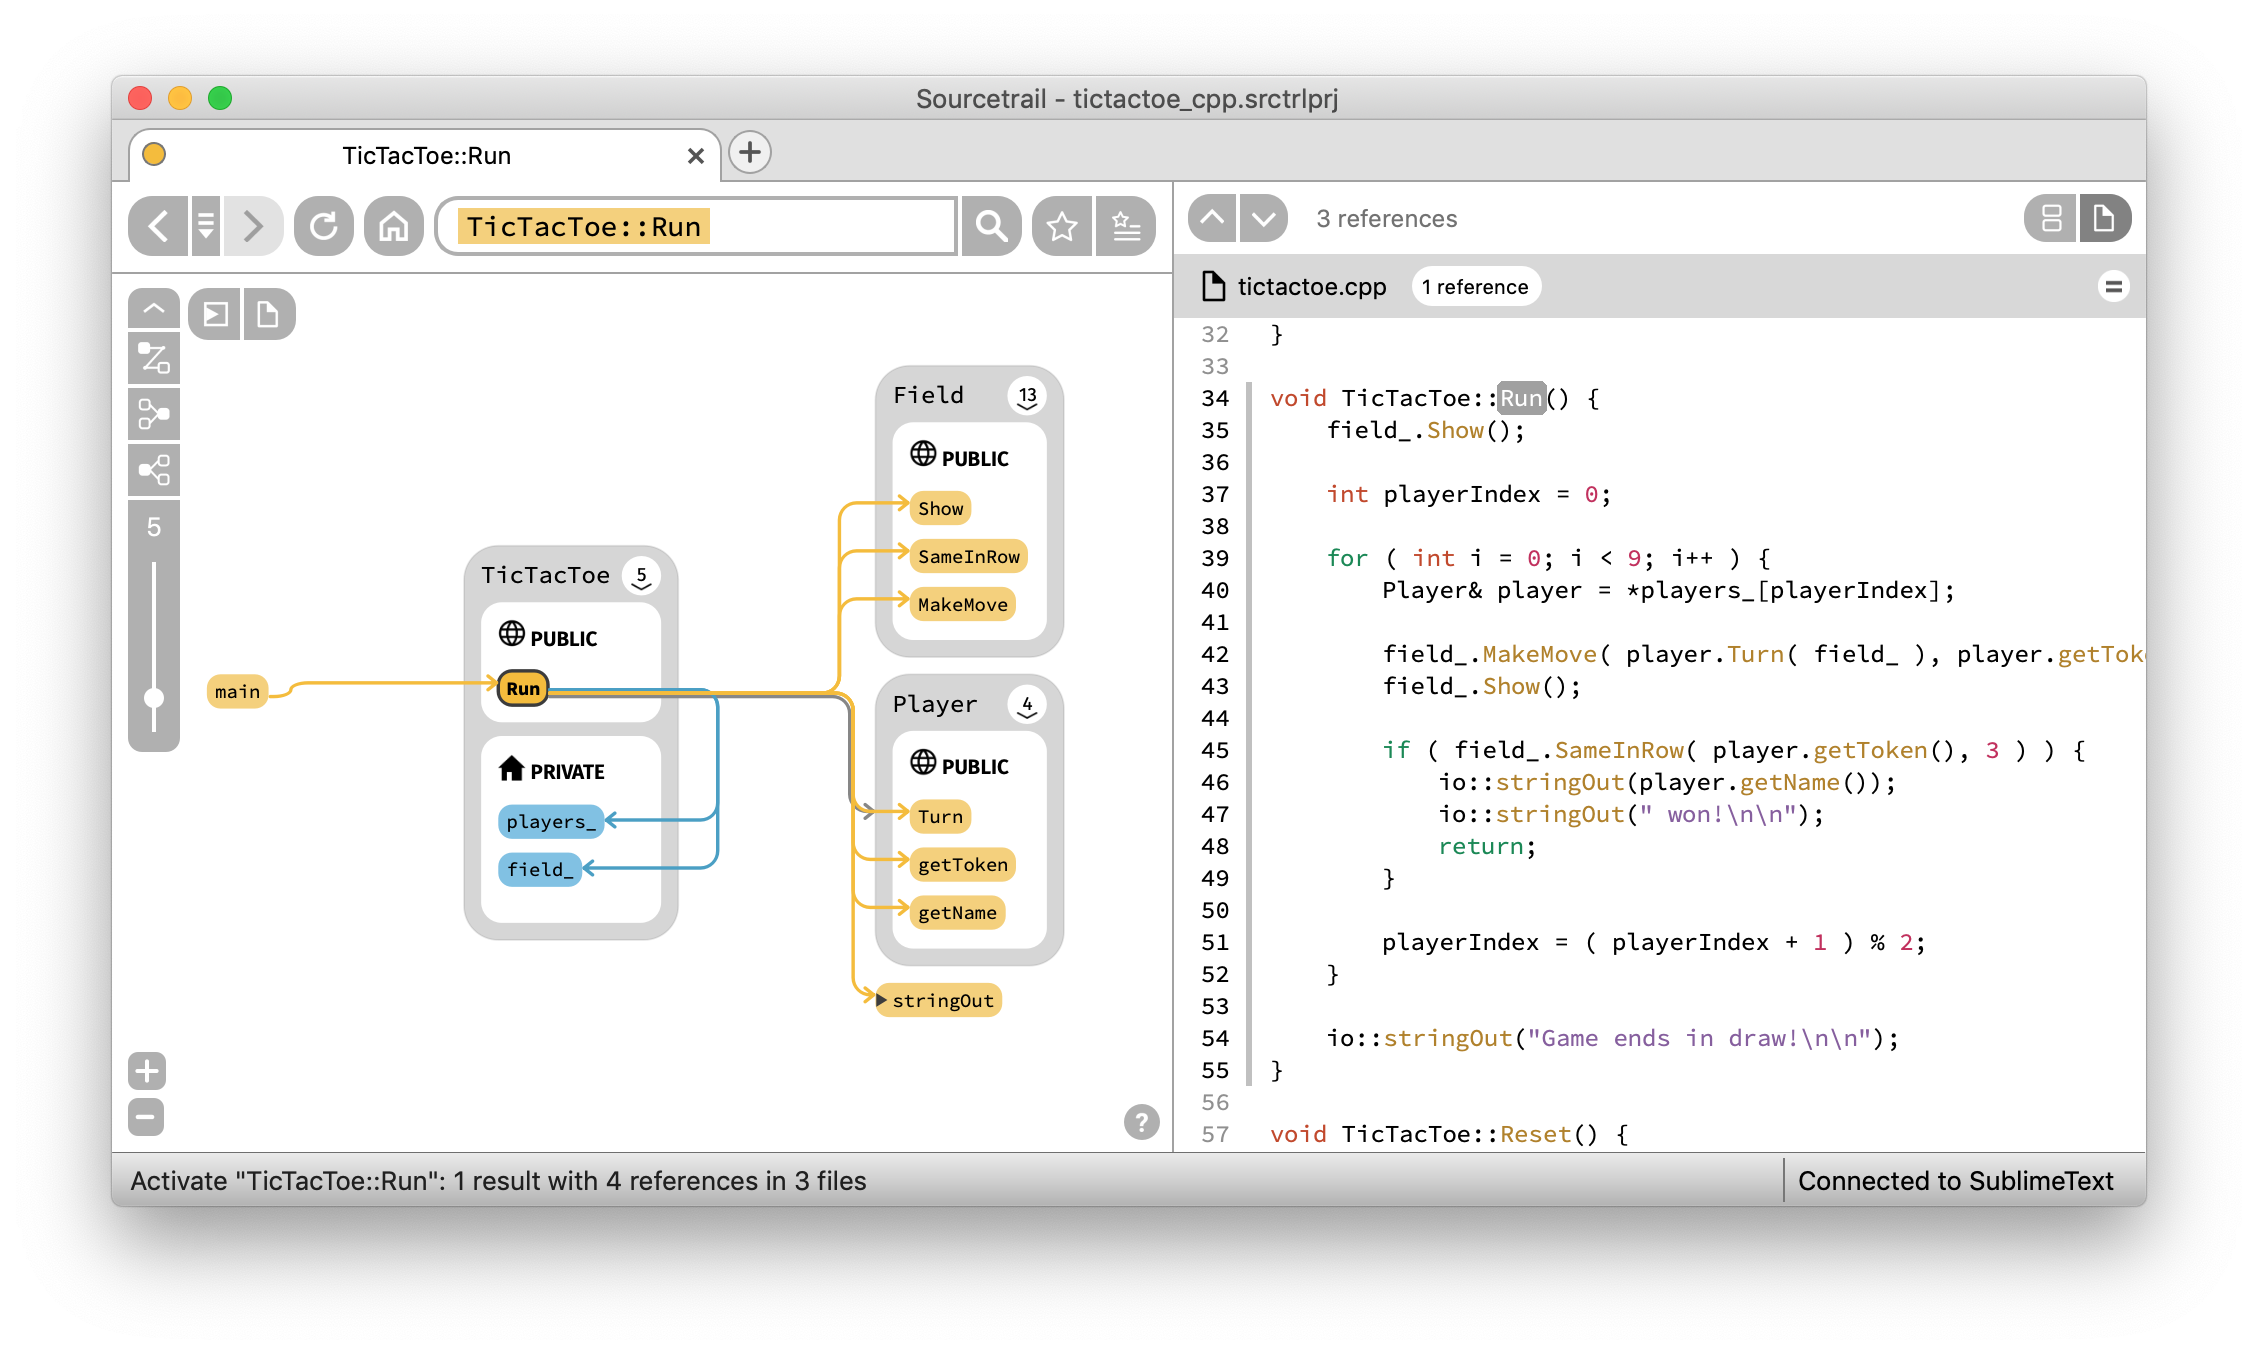 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
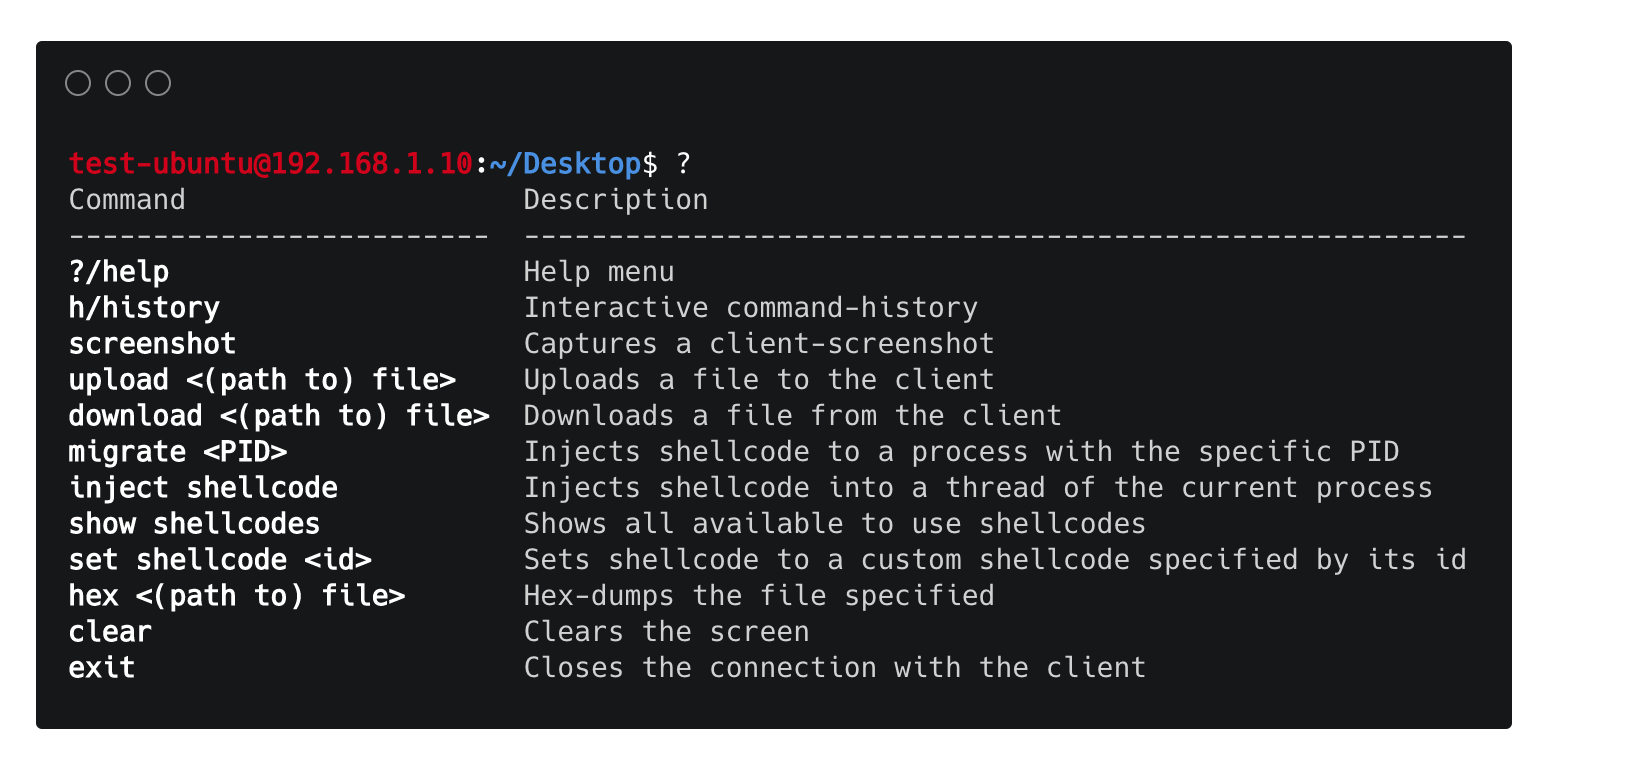 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 idarlingteam/idarling
Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
 trailofbits/manticore
Symbolic execution tool
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 cmatthewbrooks/r2kit
A set of scripts for a radare-based malware code analysis workflow
 viper-framework/viper
Binary analysis and management framework
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss