
 #3
RAT analysis, detection signatures, behavioral analysis, and research frameworks.
Kitploit recommended
 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
 alanbaumgartner/aurora
Aurora Remote Administration Tool
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 yschgroup/skyrat
SkyRAT - Powershell Remote Administration Tool
 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
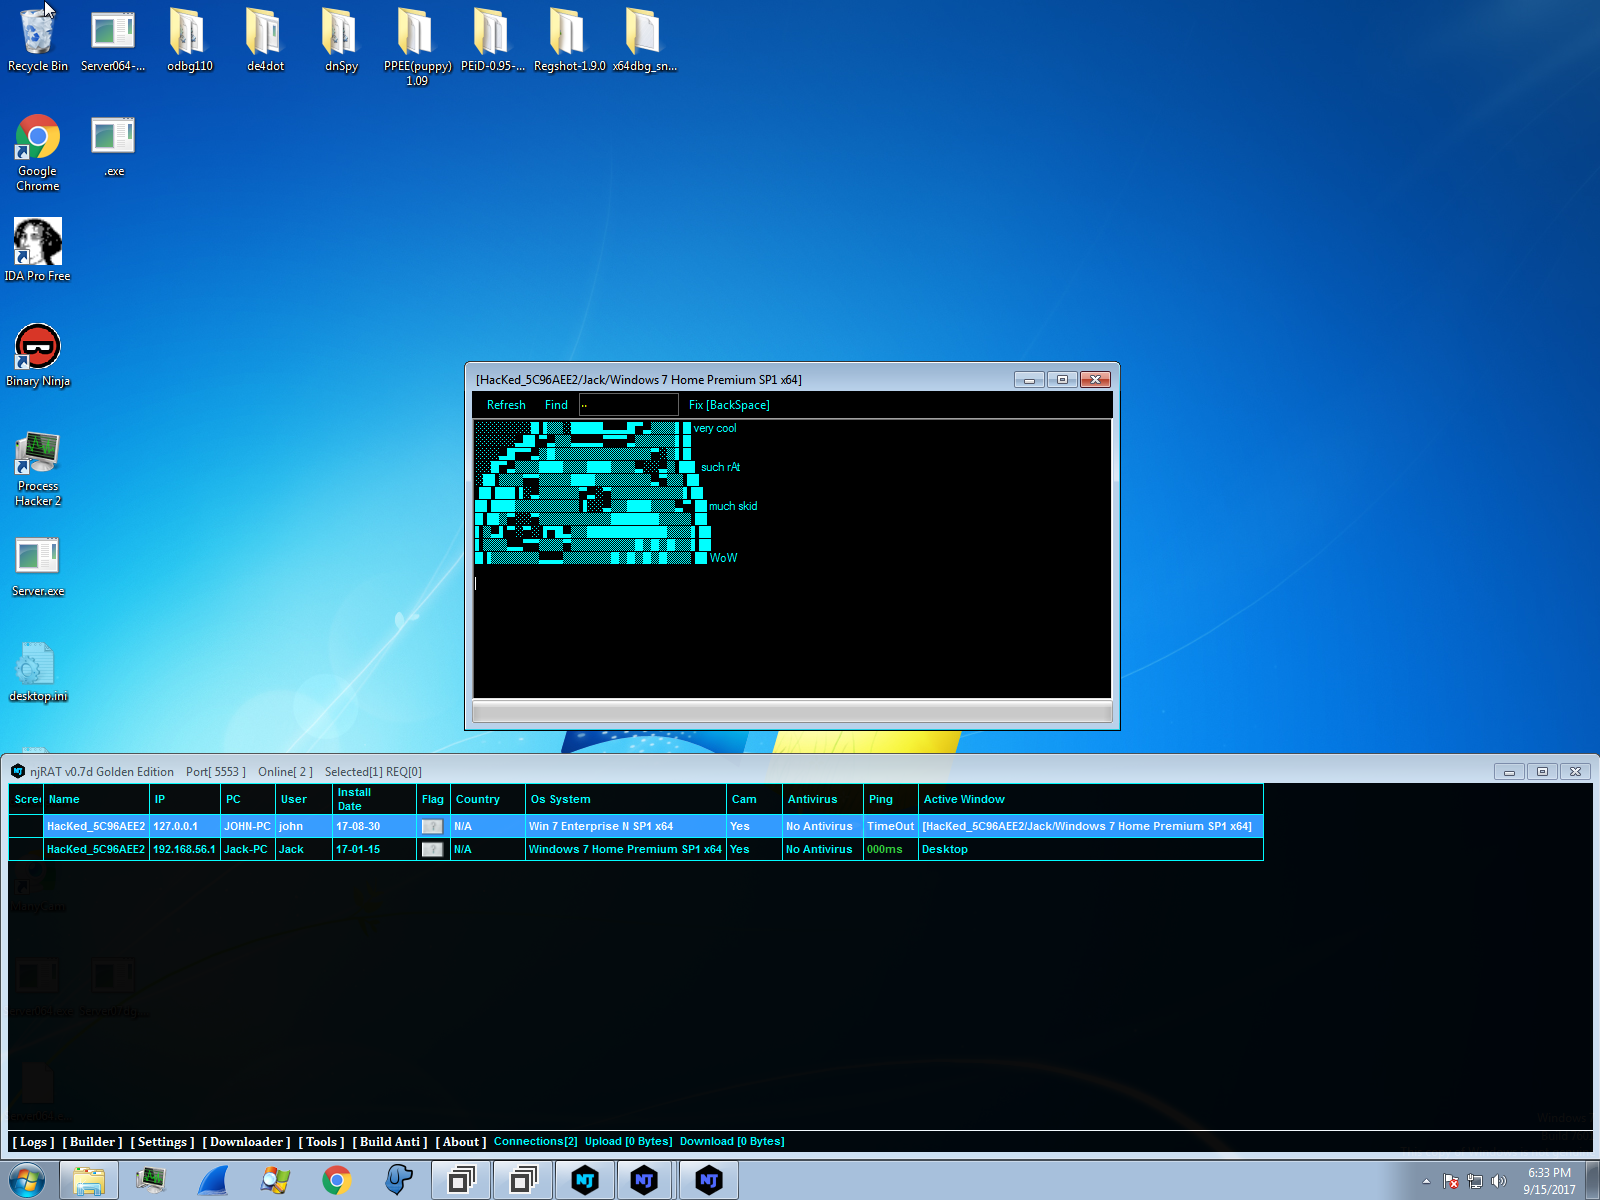 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 m4sc3r4n0/spyrat
Python Remote Access Trojan
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 mwsrc/schwarze-sonne-rat
SS-RAT (Schwarze-Sonne-Remote-Access-Trojan)
 malwares/remote-access-trojan
Windows Remote-Access-Trojan
 mwsrc/plasmarat
Remote Access Trojan(RAT), Miner, DDoS









