
 #3
RAT analysis, detection signatures, behavioral analysis, and research frameworks.
Kitploit recommended
 demon-i386/zoshrinkc2
DNS over HTTPS targeted malware (only runs once)
 stphivos/rat-shell
Windows Remote Access Trojan (RAT)
 jofpin/backcookie
Small backdoor using cookie.
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
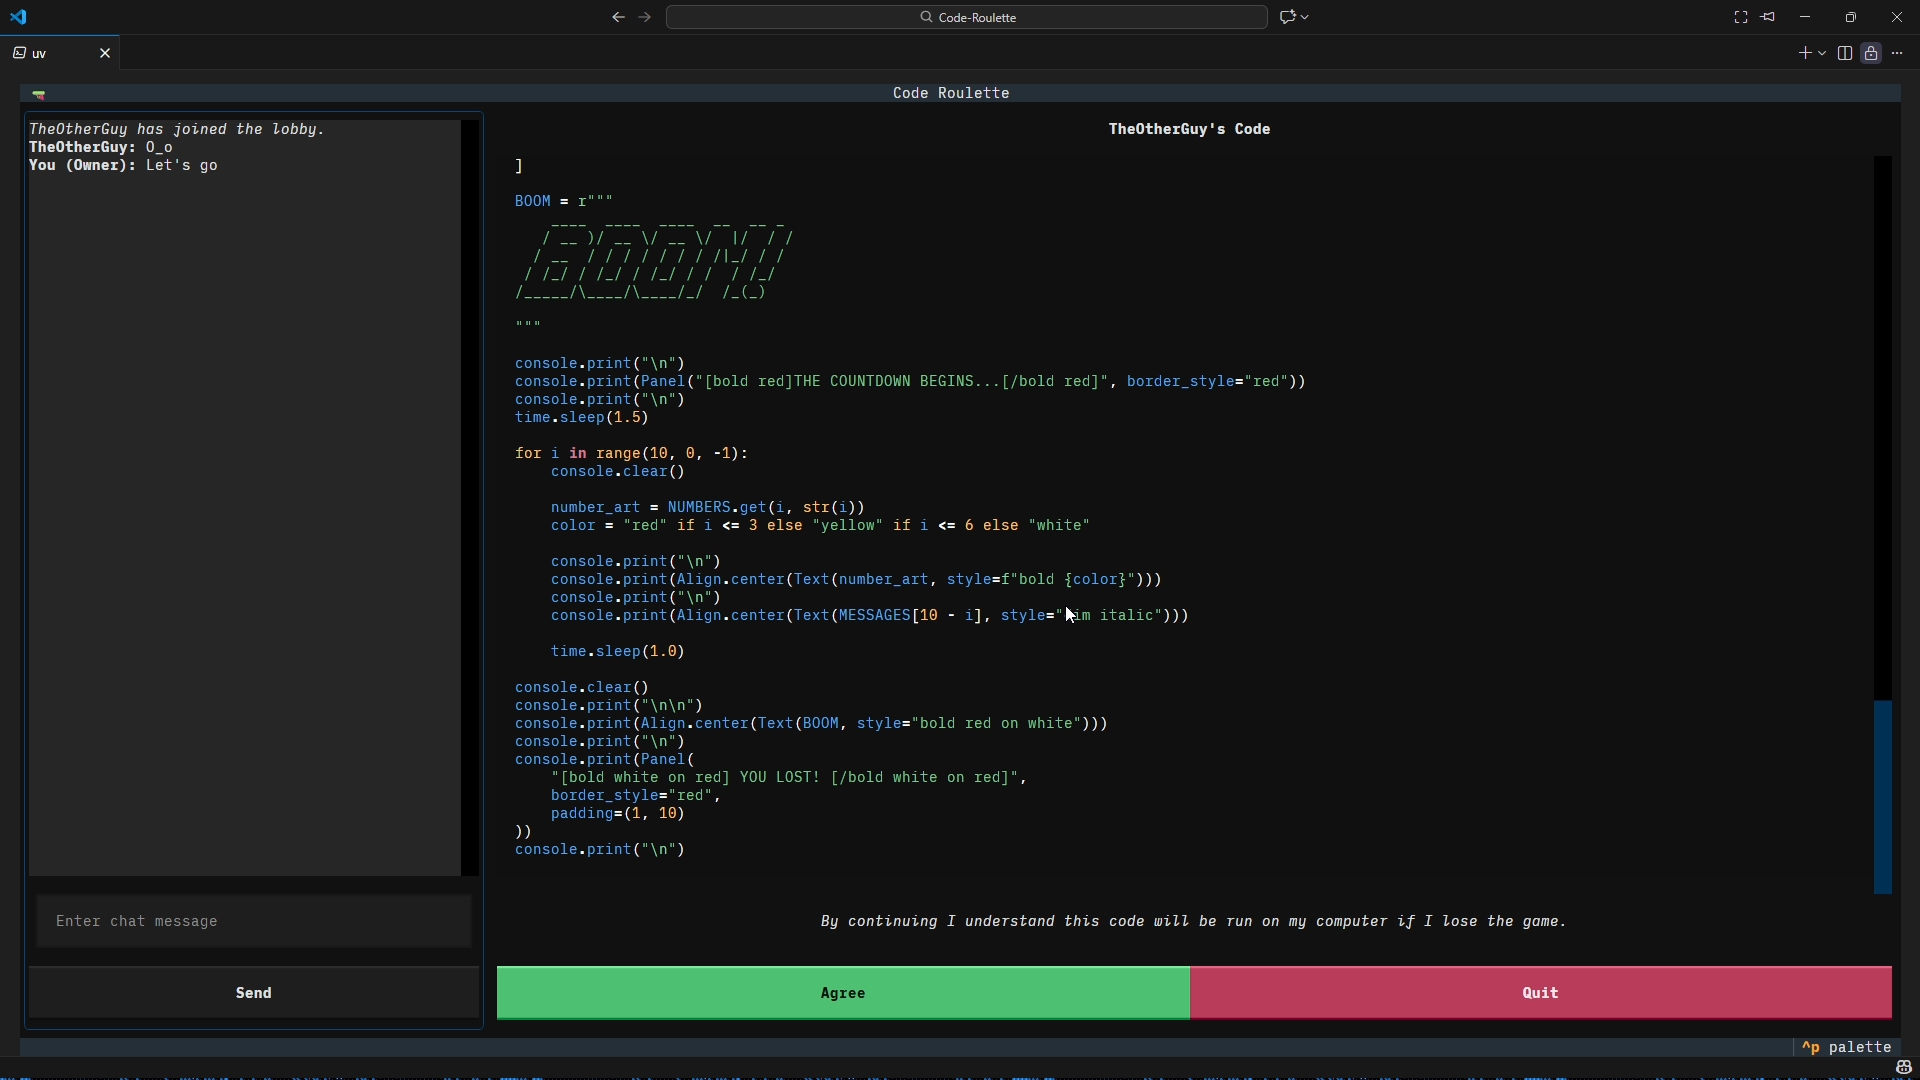 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 retrobyte/shadowtech-rat
An example of a remote administration tool.
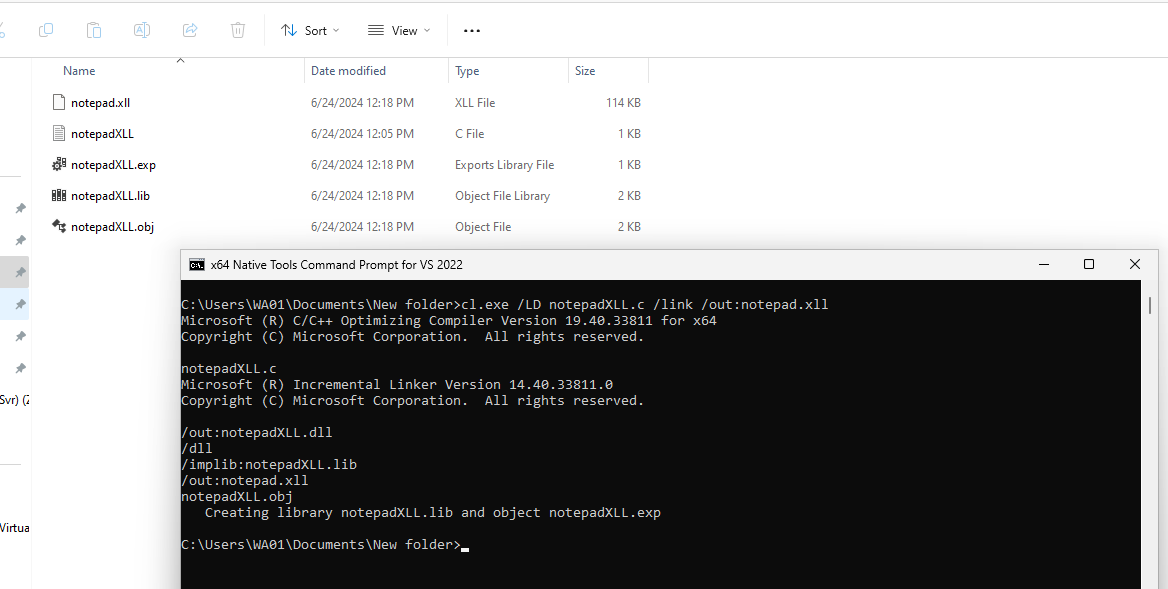 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 hyderpwn/veritas-backup
Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
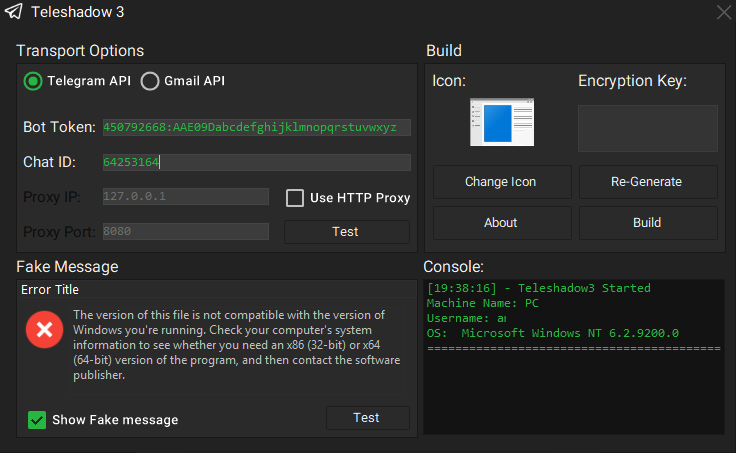 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository








