
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
 kudaes/fiber
Rust-based PoC using Windows fibers to execute in-memory code stealthily, hiding payload stacks from EDR by switching between control and payload…
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 milo2012/cve-2018-13382
CVE-2018-13382
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin
 convisolabs/cve-2024-43044-jenkins
Exploit for the vulnerability CVE-2024-43044 in Jenkins
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
 dazzyddos/hsc24redteaminfra
Slides and Codes used for the workshop Red Team Infrastructure Automation
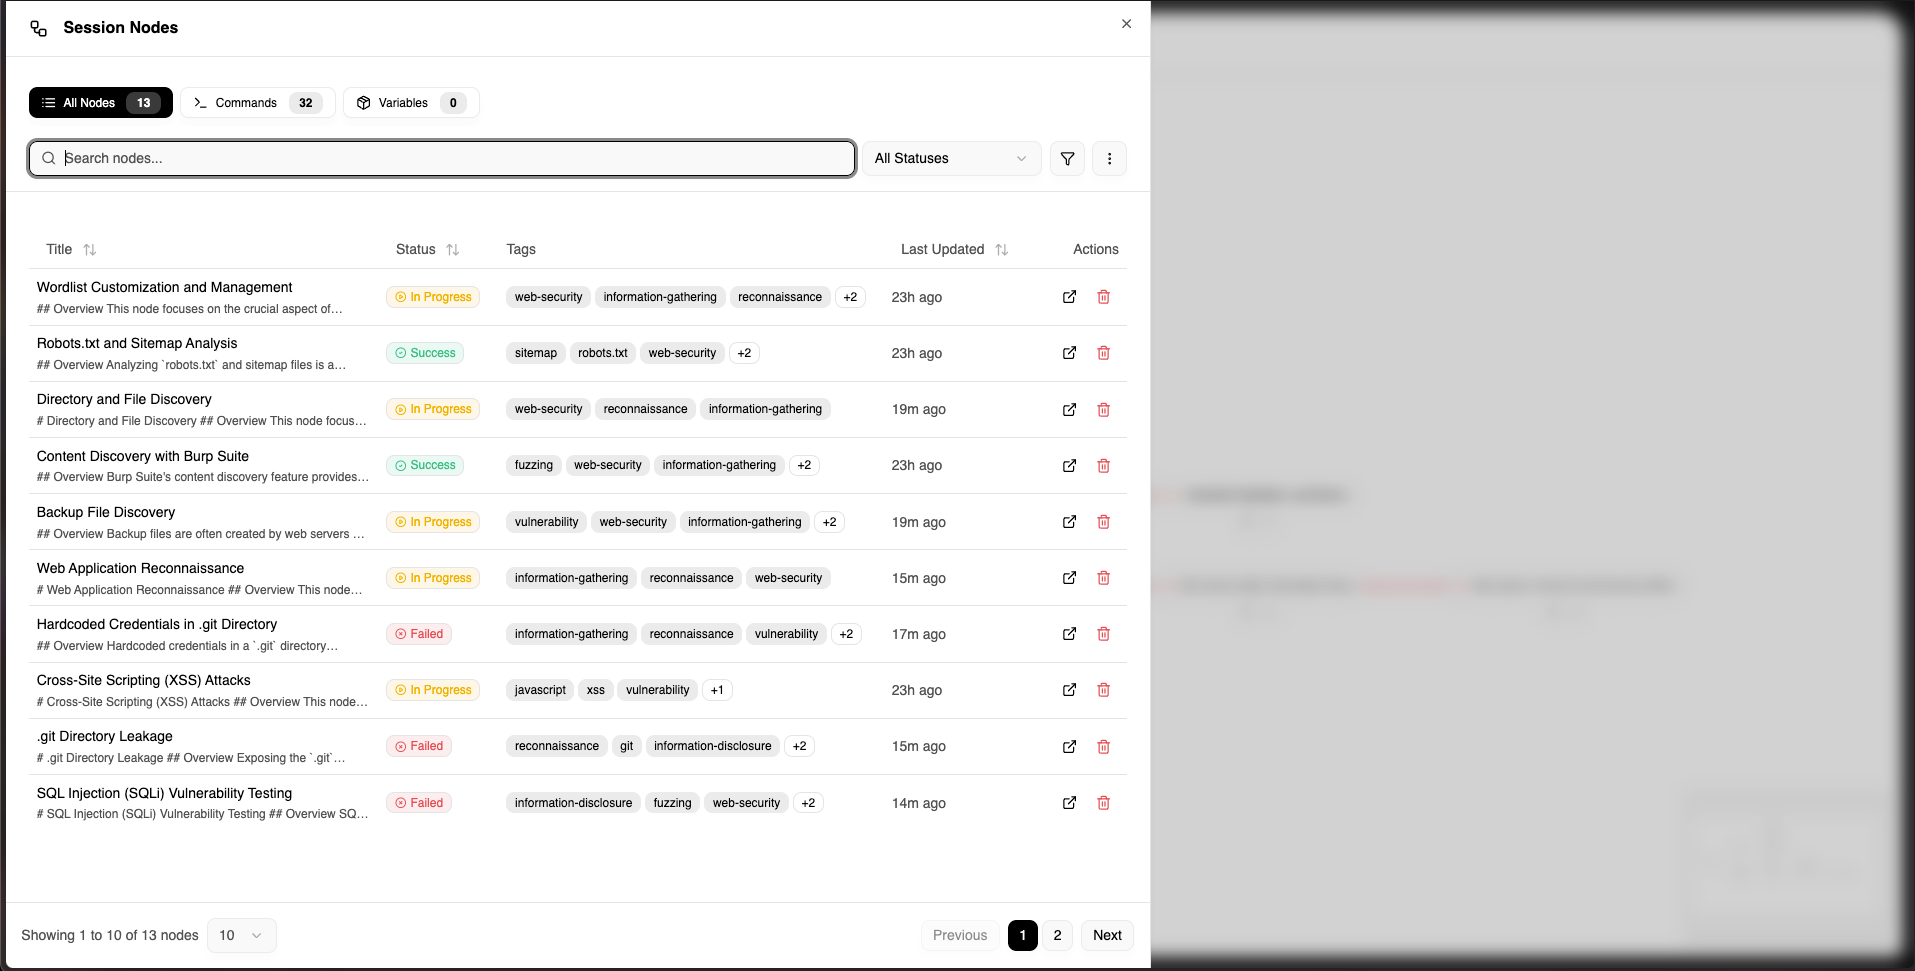 rb-x/pwnflow
A visual methodology tracking platform tailored for offensive security assessments
 sadprocessor/cypherdog
PoSh BloodHound Dog Whisperer
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 octoberfest7/kdstab
BOF combination of KillDefender and Backstab
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 zux0x3a/dns-black-cat
Multi platform toolkit for an interactive DNS shell commands exfiltration, by using DNS-Cat you will be able to execute system commands in shell mode…
 watchtowrlabs/citrix-virtual-apps-xen-exploit
Citrix Virtual Apps and Desktops (XEN) Unauthenticated RCE
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing








