
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 magisterquis/sshhipot
High-interaction MitM SSH honeypot
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 rasta-mouse/ost-c2-spec
Open Source C&C Specification
 kudaes/dumpy
Reuse open handles to dynamically dump LSASS.
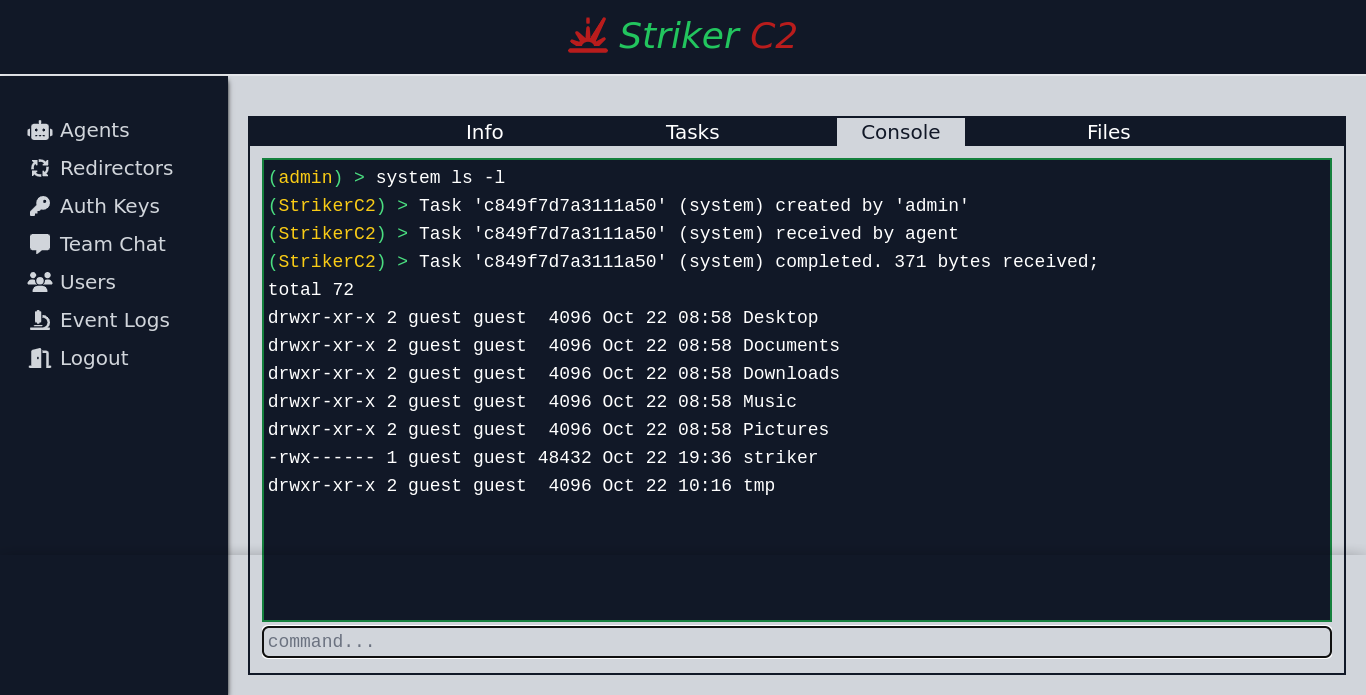 4g3nt47/striker
Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
 janoglezcampos/rust_syscalls
Single stub direct and indirect syscalling with runtime SSN resolving for windows.

 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 redlectroid/overthruster
HID attack payload generator for Arduinos
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 coffinxp/img-payloads
Curated collection of image-based payloads for authorized red-team testing and security education, with HTML examples for generating or embedding web…
 mattifestation/antimalwareblight
Execute PowerShell code at the antimalware-light protection level.
 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters









