
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 nyxgeek/onedrive_user_enum
onedrive user enumeration - pentest tool to enumerate valid o365 users
 al1ex/windowselevation
Windows Elevation(持续更新)
 wh04m1001/dfscoerce
Proof-of-concept tool that coerces Windows authentication via MS-DFSNM NetrDfsRemoveStdRoot and NetrDfsAddStdRoot methods for credential relay…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 rvrsh3ll/tokentactics
Azure JWT Token Manipulation Toolset
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 ytisf/pyexfil
PyExfil — Python 3 toolkit for researching and stress-testing data exfiltration techniques across network, physical, and steganographic channels. For…
 stivenhacker/ghoststrike
C++ process hollowing injector that encrypts and obfuscates shellcode with XOR, Base64, and dynamic API resolution to deploy stealthy reverse shells…
 g0h4n/rusthound-ce
Active Directory data ingestor via LDAP(S) or ADWS protocol for BloodHound Community Edition written in Rust. 🦀
 ring0lab/catphish
CATPHISH project - For phishing and corporate espionage. Perfect for RED TEAM.
 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 crypt0s/fakedns
A regular-expression based python MITM DNS server with support for DNS Rebinding attacks
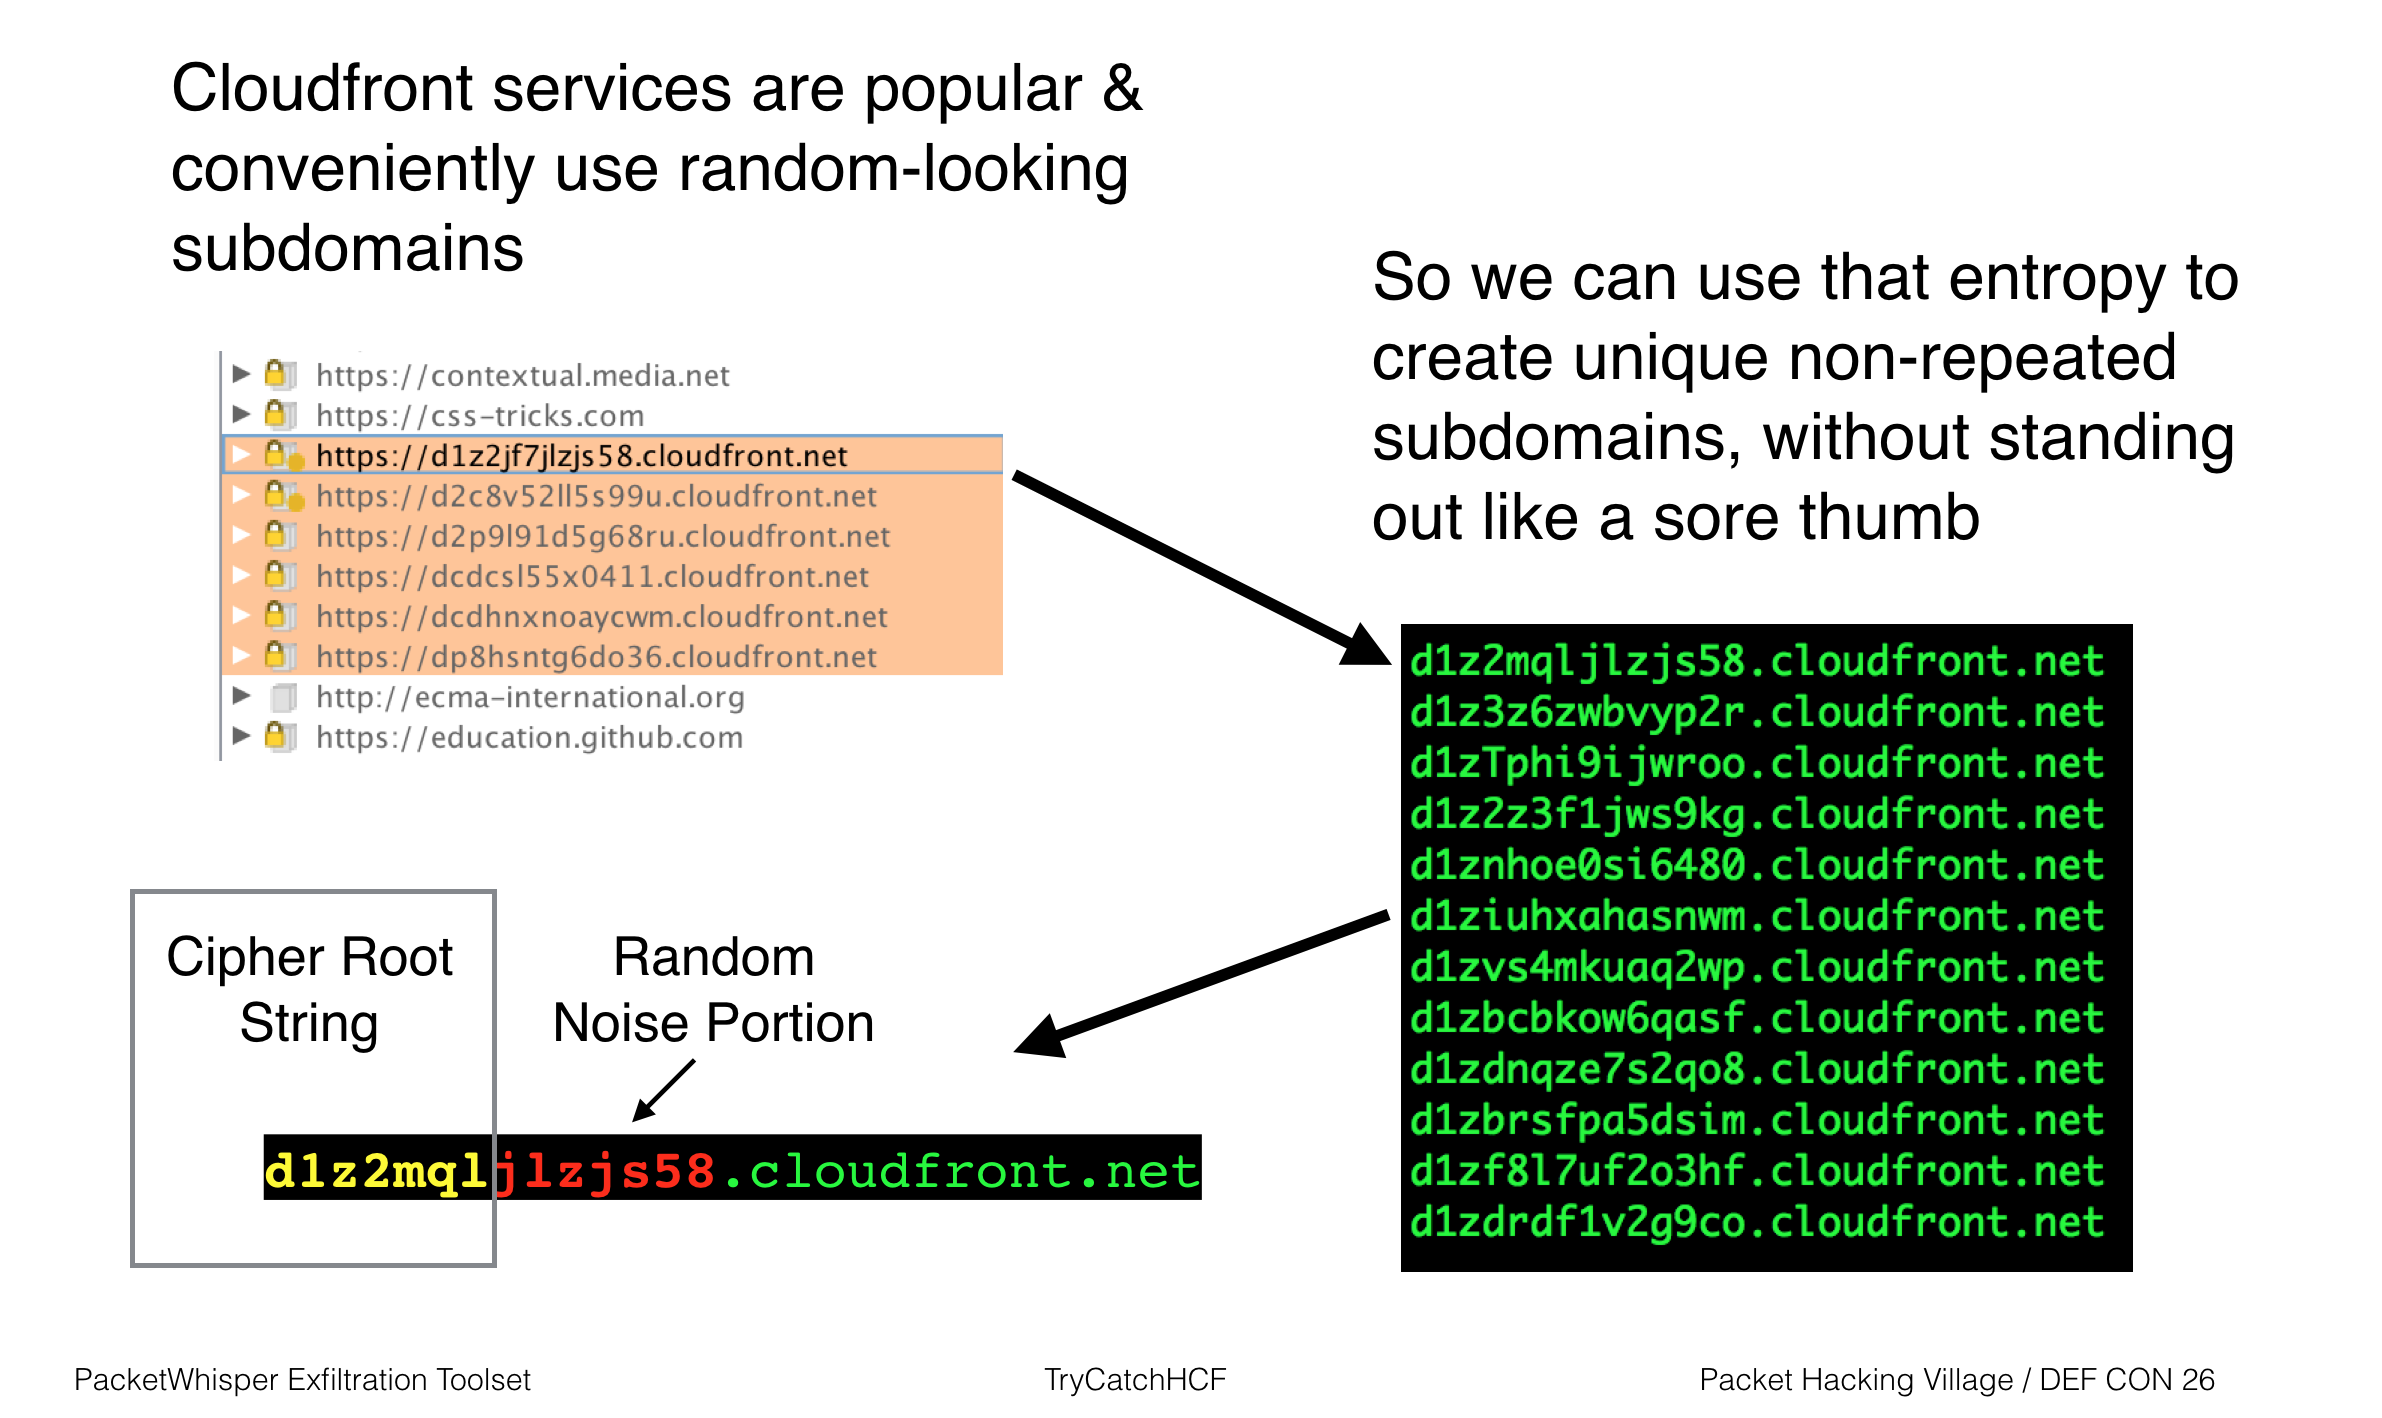 trycatchhcf/packetwhisper
PacketWhisper: Stealthily exfiltrate data and defeat attribution using DNS queries and text-based steganography. Avoid the problems associated with…








