
 #1
Tools for gaining higher-level permissions or unauthorized access on compromised systems.
Kitploit recommended
 offensive-panda/nt-authority-system-context-rtcore
This exploit rebuilds and exploit the CVE-2019-16098 which is in driver Micro-Star MSI Afterburner 4.6.2.15658 (aka RTCore64.sys and RTCore32.sys)…
 j0wii/cve-2026-97798_lpe_windows
CVE-2026-97798 PoC — WER Time Travel Debugging argument injection to SYSTEM (Windows 11 LPE), with an adaptive faultrep.dll resolver.
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 karollooool/cve-2026-83991-writeup-and-poc
Proof-of-concept demonstrating a Windows Cloud Files access-check bypass (CVE-2026-83991) that converts a read-only file into a cloud placeholder via…
 mebeim/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation with simple C helpers and a…
 petergottesman/pwnkit-exploit
Local privilege escalation exploit for CVE-2021-4034 in pkexec, providing a proof-of-concept that drops a root shell on vulnerable systems.
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 malwareman007/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
 rjt-gupta/cve-2021-29337
CVE-2021-29337 - Privilege Escalation in MODAPI.sys (MSI Dragon Center)
 mbcrump/cve-2021-3156
Notes regarding CVE-2021-3156: Heap-Based Buffer Overflow in Sudo
 fi01/libput_user_exploit
CVE-2013-6282 kernel exploit that overwrites ptmx.fsync handler and uevent_helper string for local privilege escalation on vulnerable Linux systems.
 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 bazad/gsscred-race
CVE-2018-4331: Exploit for a race condition in the GSSCred system service on iOS 11.2.
 zerozenxlabs/cve-2026-20127---cisco-sd-wan-preauth-rce
Proof-of-concept exploit for CVE-2026-20127, a pre-auth RCE in Cisco SD-WAN Manager/Controller enabling admin access and network configuration…
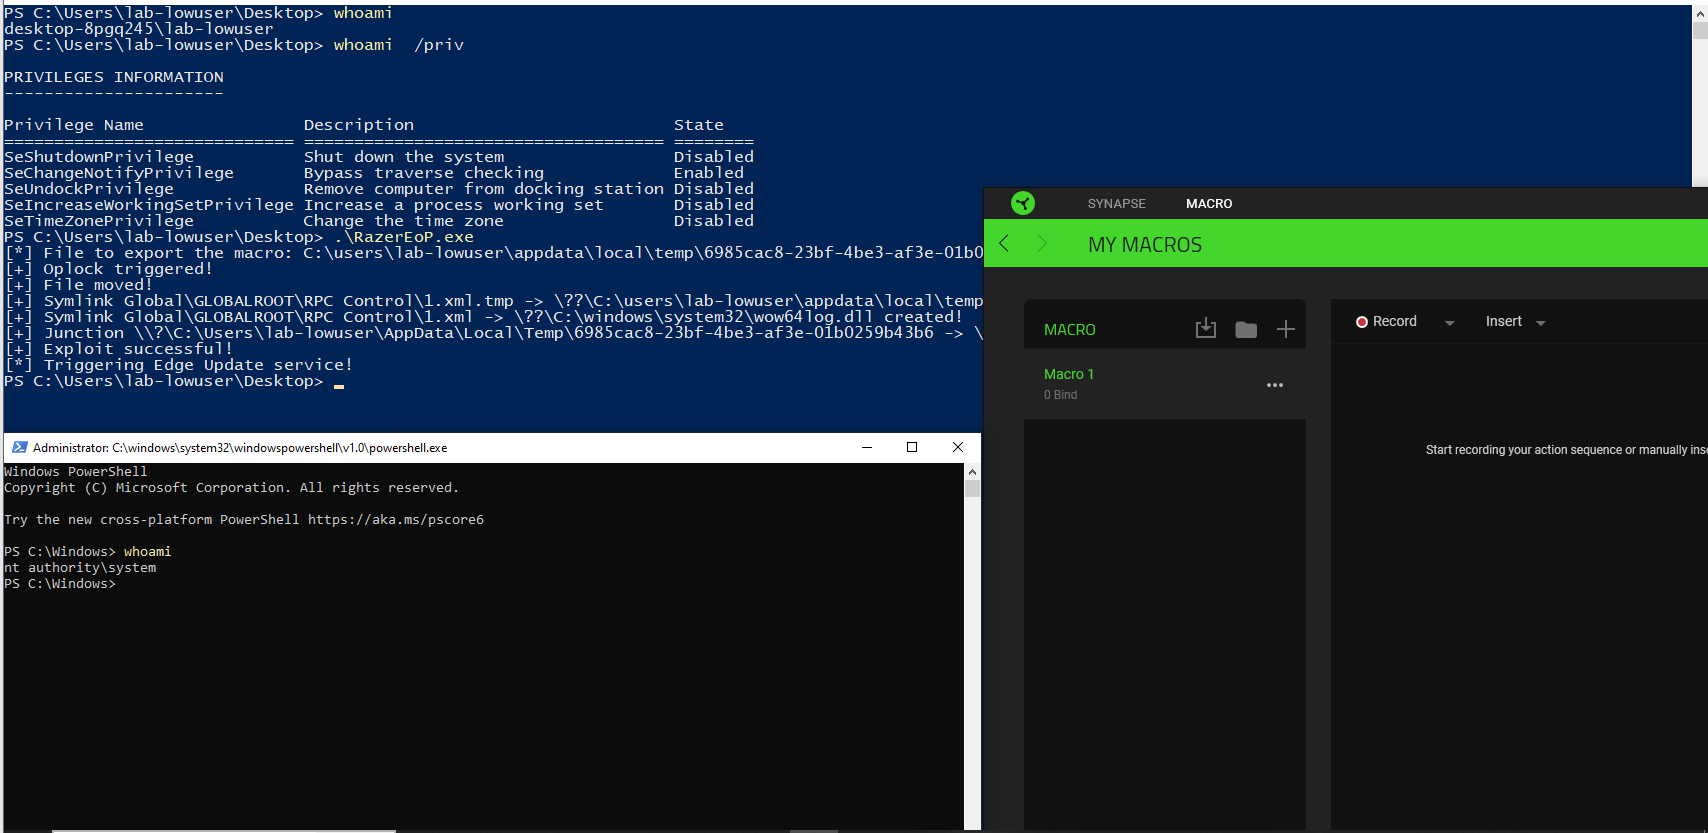 wh04m1001/razereop
Proof-of-concept exploit for arbitrary file delete/move via Razer Synapse 3 Macro SYSTEM service, demonstrating local privilege escalation on…
 ankitrawatgit/iqoo-z9_5g-vivo-t3_5g-root-ghostlock
An iQOO Z9 5G and vivo T3 5G jailbreak/root CVE-2026-43499 Android application and payloads. Both devices use the MediaTek Dimensity 7200 (MT6886)…
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.








