
 #1
 ldpreload/blacklotus
BlackLotus UEFI Windows Bootkit
 ashemery/exploitation-course
Offensive Software Exploitation Course
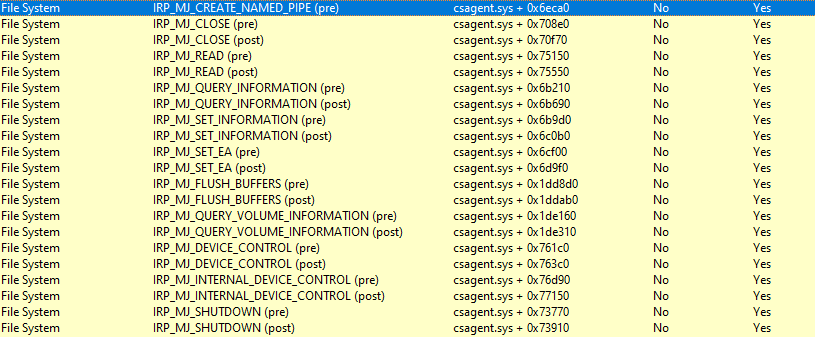 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 alphaseclab/awesome-rat
RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 secgroundzero/warberry
WarBerryPi - Tactical Exploitation
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 xiphosresearch/exploits
Miscellaneous exploit code
 epinna/weevely3
Weaponized web shell
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…









