
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended

 sektioneins/suidguard
SUIDGuard - a TrustedBSD Kernel Extension that adds mitigations to protect SUID/SGID processes a bit more
 puliczek/cve-2022-0337-poc-google-chrome-microsoft-edge-opera
🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…
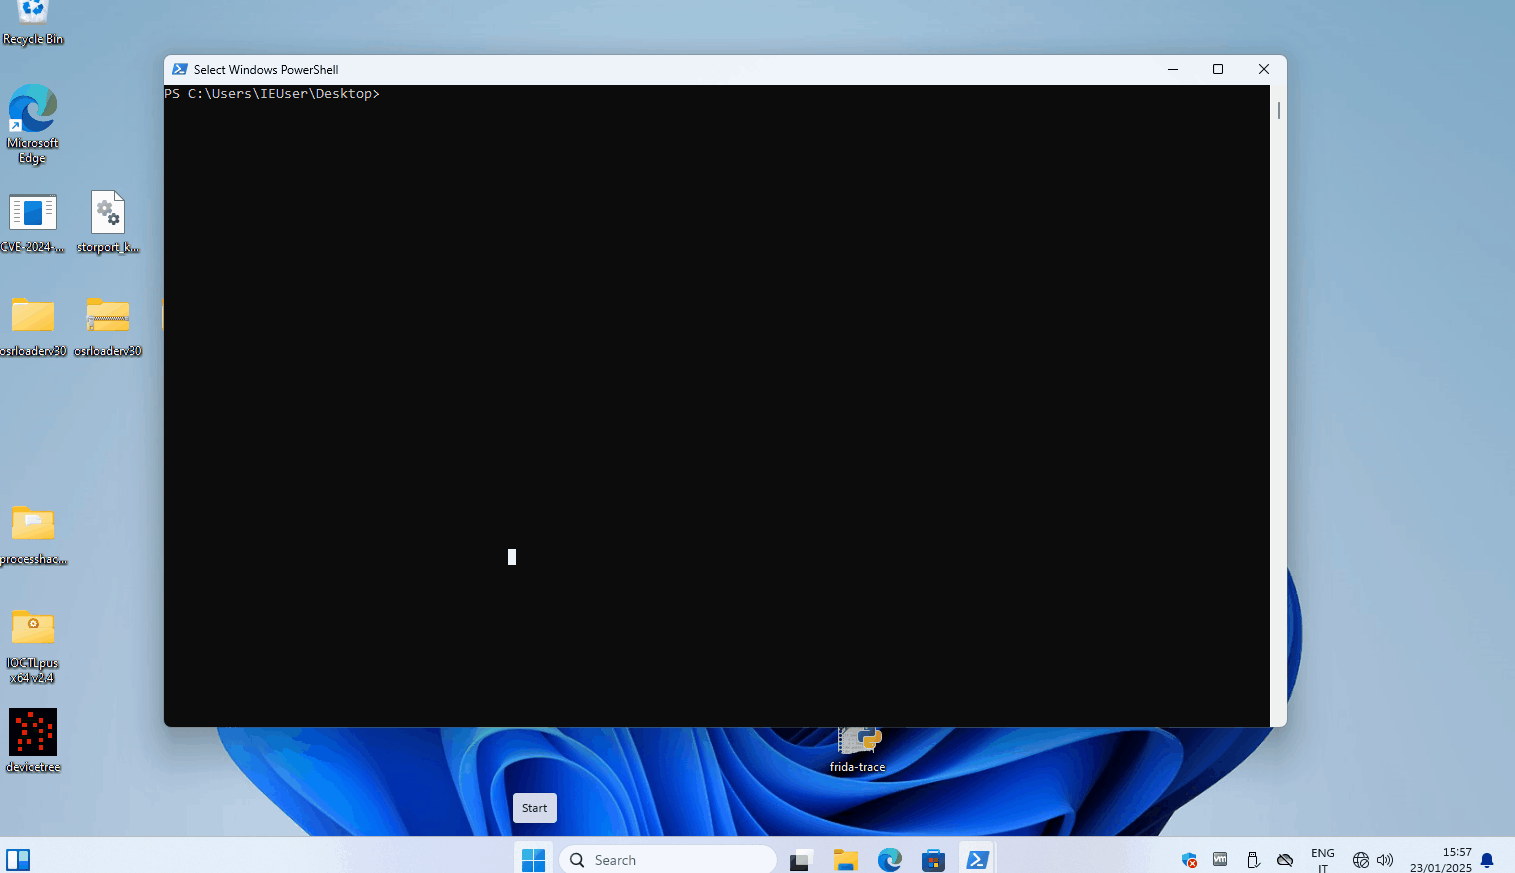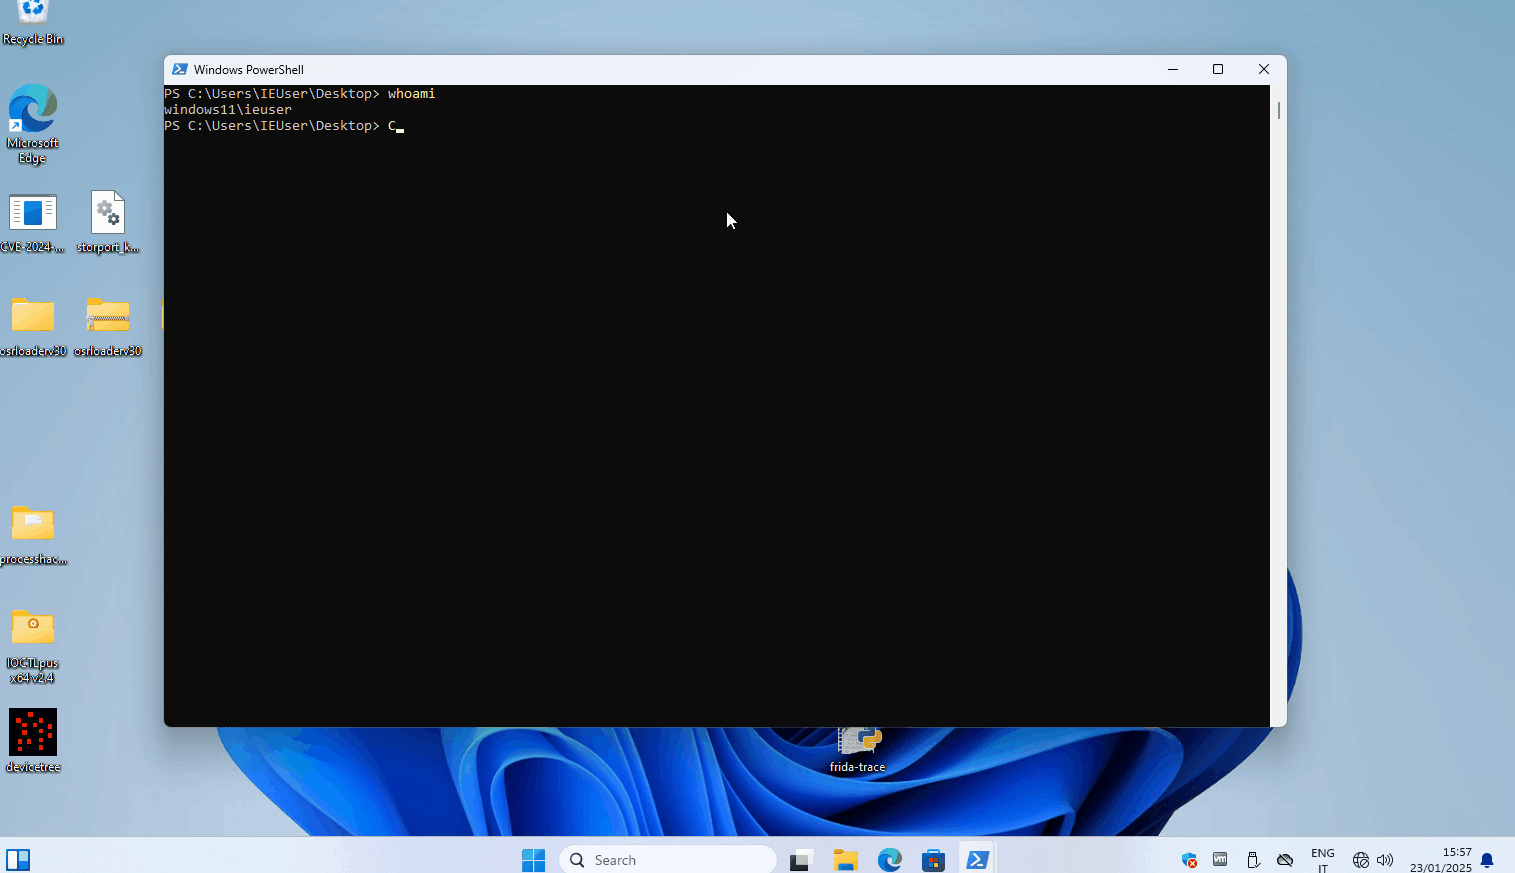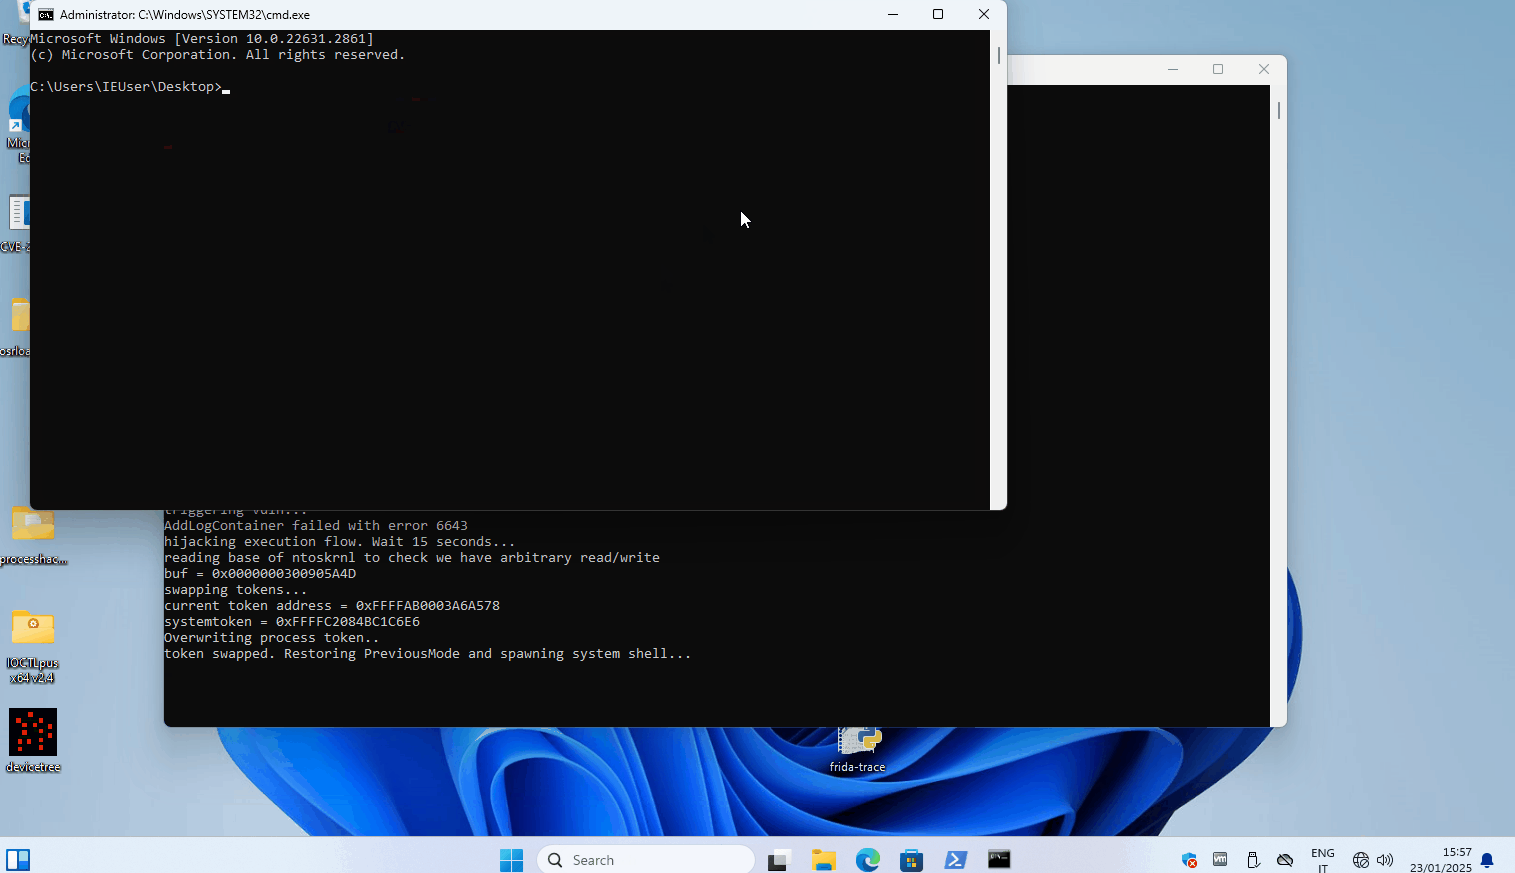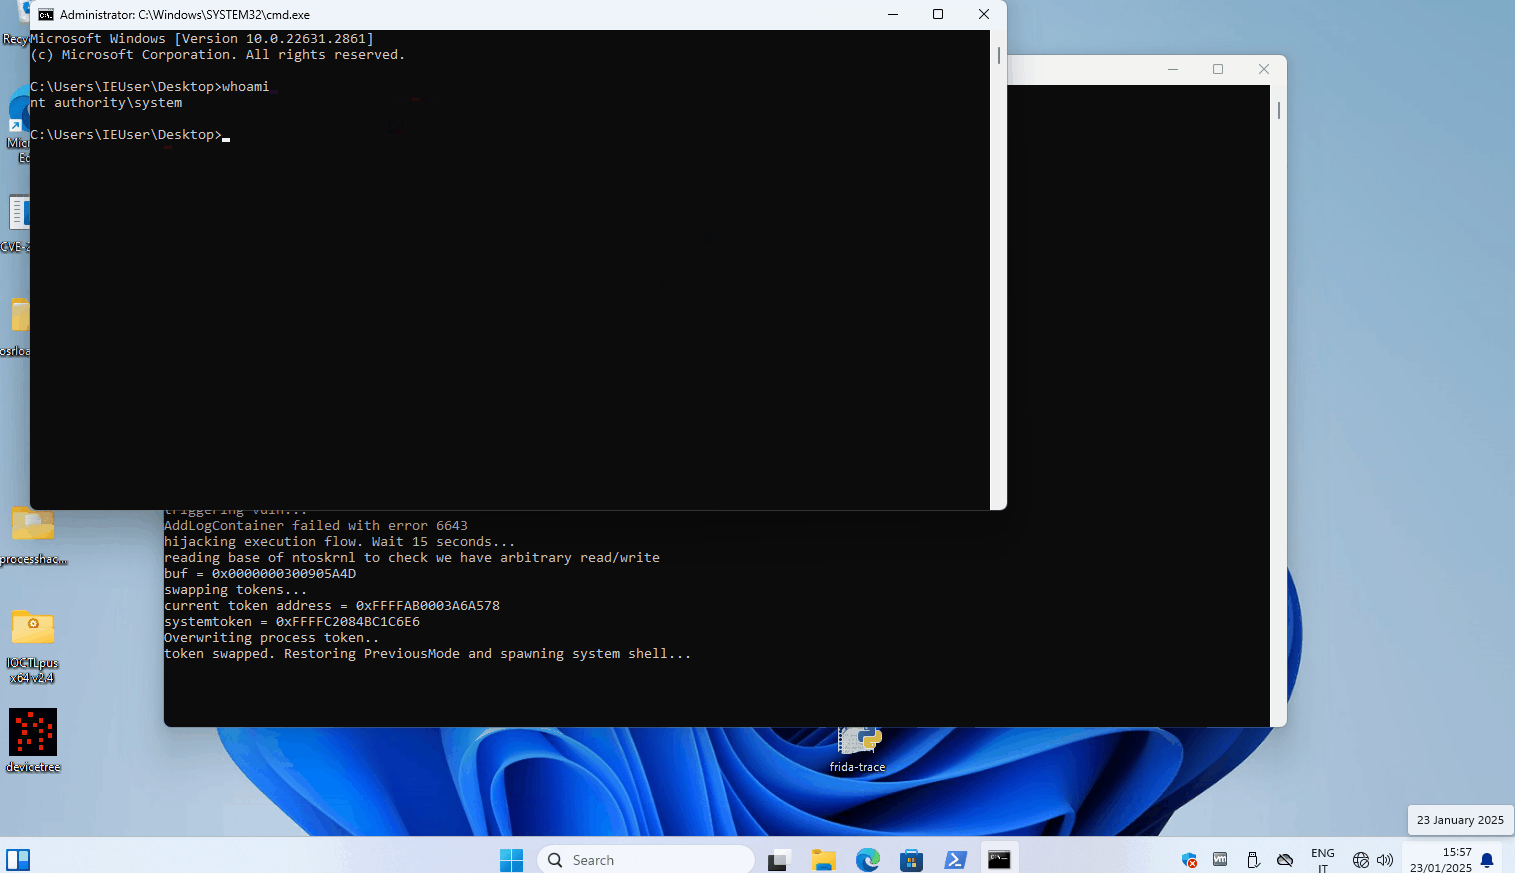 mrale98/cve-2024-49138-poc
POC exploit for CVE-2024-49138
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
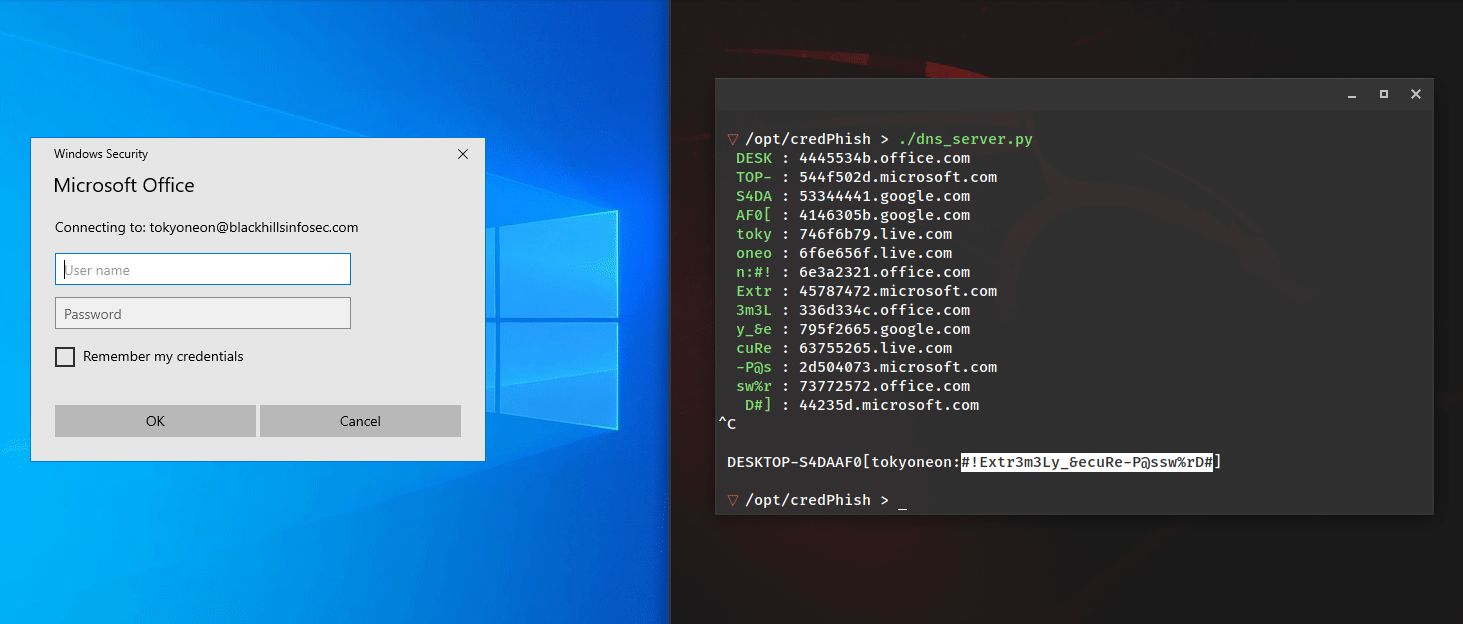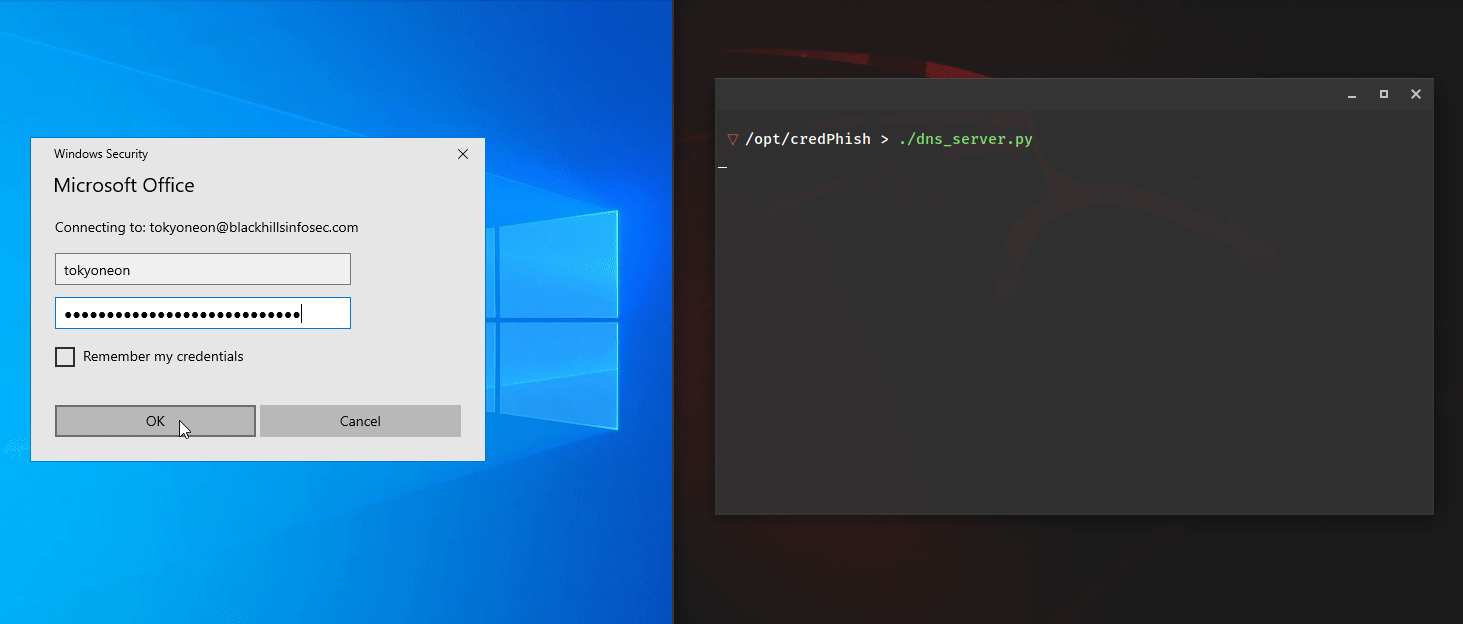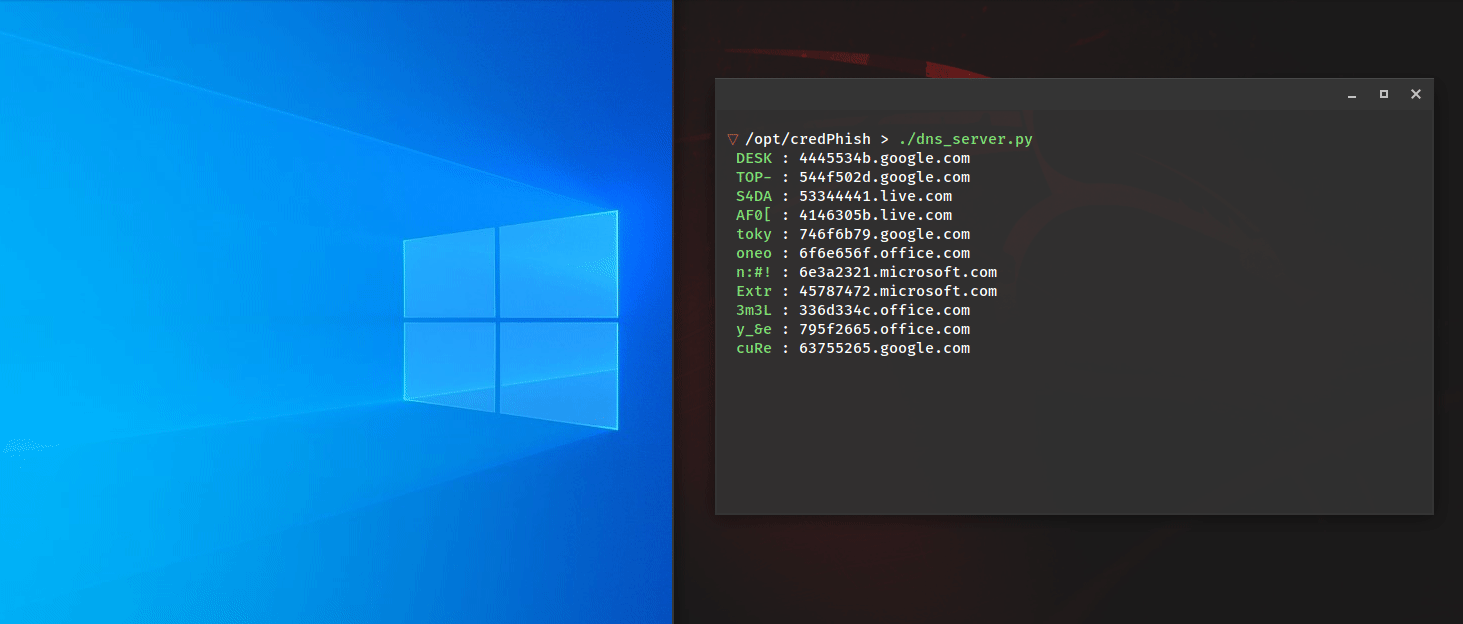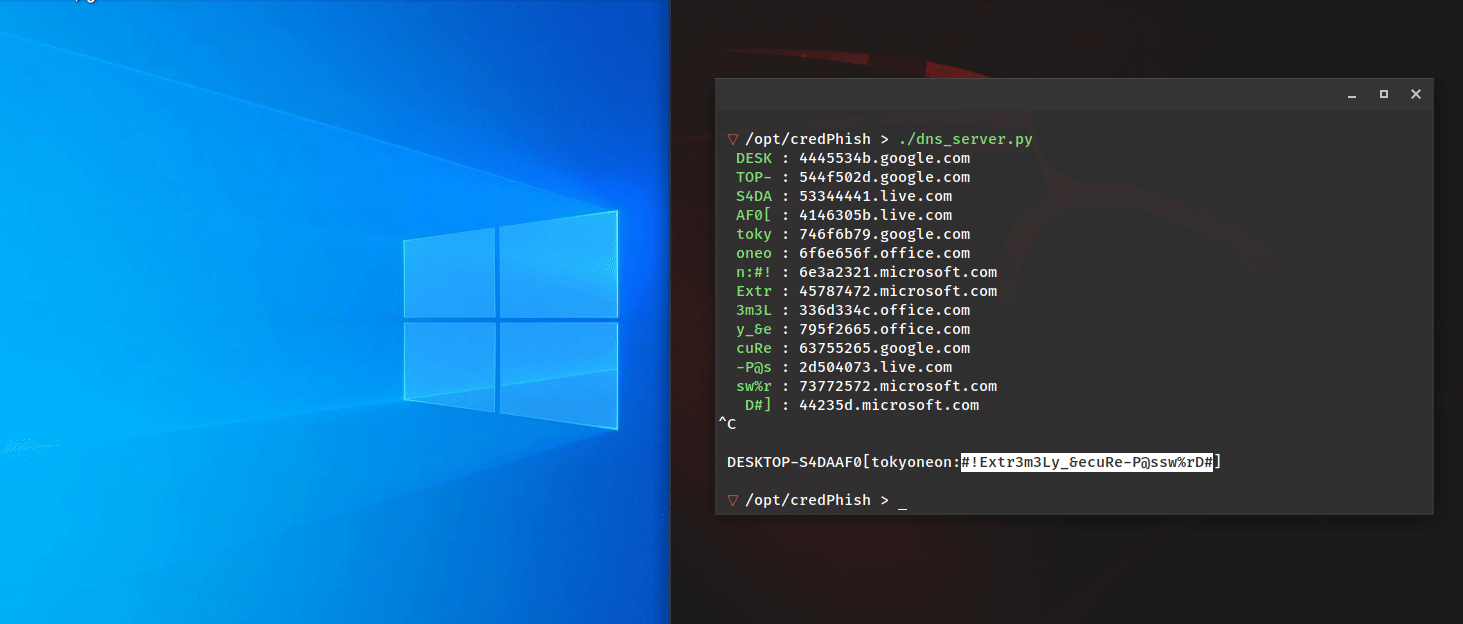 tokyoneon/credphish
PowerShell script that invokes legitimate credential prompts and exfiltrates captured passwords over DNS using CredentialPicker and Resolve-DnsName.
 reveng007/sharpgmailc2
Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
 potmdehex/multicast_bytecopy
kernel r/w exploit for iOS 15.0 - 15.1.1
 wh04m1001/cve-2025-48799
Proof-of-concept exploit for CVE-2025-48799, a Windows Update service privilege escalation via arbitrary folder deletion with symbolic link handling,…
 gosecure/dllpasswordfilterimplant
DLL Password Filter Implant with Exfiltration Capabilities
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 rogue-kdc/cve-2019-0841
PoC code for CVE-2019-0841 Privilege Escalation vulnerability
 scorpioneslabs/dvs
D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 p0dalirius/extractbitlockerkeys
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
 zxsecurity/steamer
For importing, searching, and managing public password breach data








