#1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended
 rat5ak/cve-2026-31431-copyfail-static-elf--poc
Minimal 587-byte static ELF exploit for CVE-2026-31431, achieving local privilege escalation via AF_ALG splice page cache corruption. No libc or…
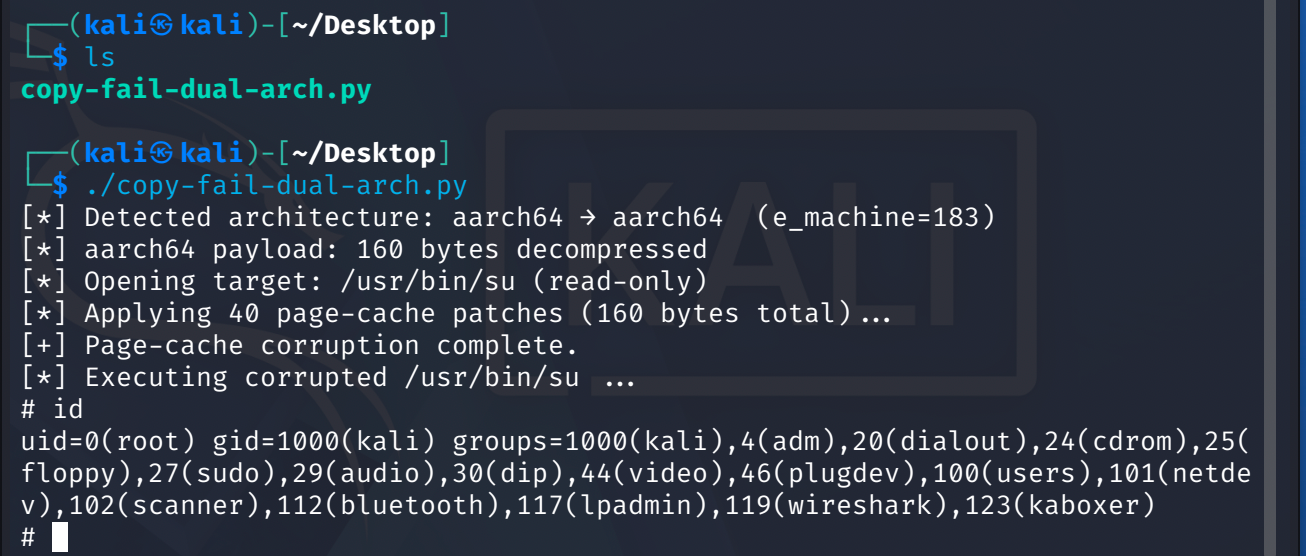 0xer0/cve-2026-31431-copy-fail-add-arm64
Python exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG and splice() to write to page cache, gaining root on arm64…
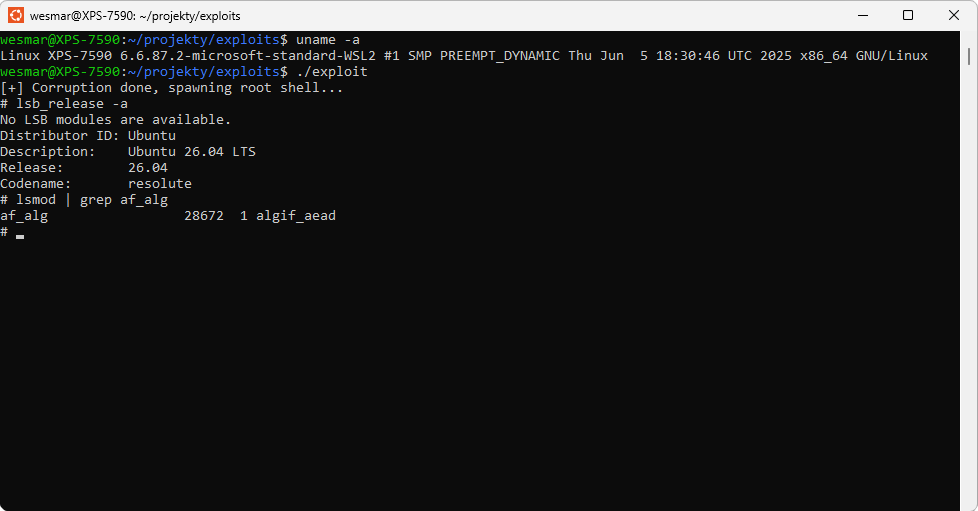 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
 ak777177/dirty-frag-analysis
Dirty Frag (CVE-2026-43284/43500) - Linux Kernel LPE Deep Technical Analysis by Bomb
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 daemoncibsec/flar3ad
POC of CVE-2026-51031 for arbitrary local file read
 ignitetechnologies/privilege-escalation
This cheasheet is aimed at the CTF Players and Beginners to help them understand the fundamentals of Privilege Escalation with examples.
 0x4d31/awesome-oscp
A curated list of awesome OSCP resources
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
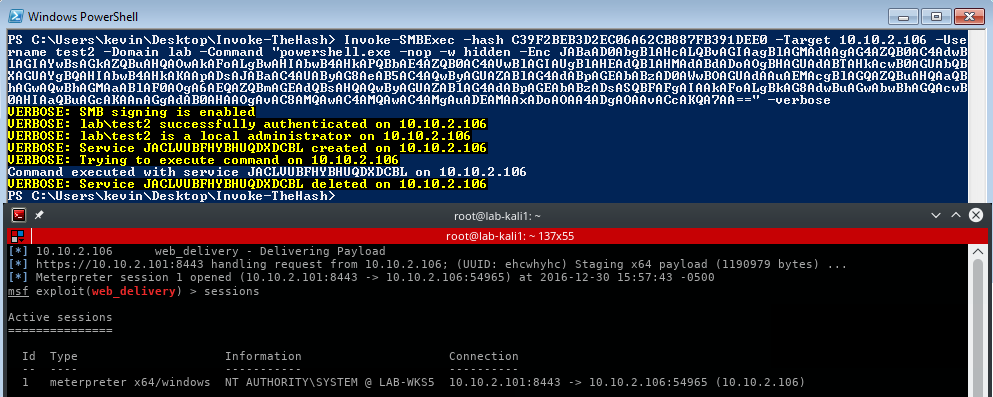 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 flangvik/teamfiltration
Cross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
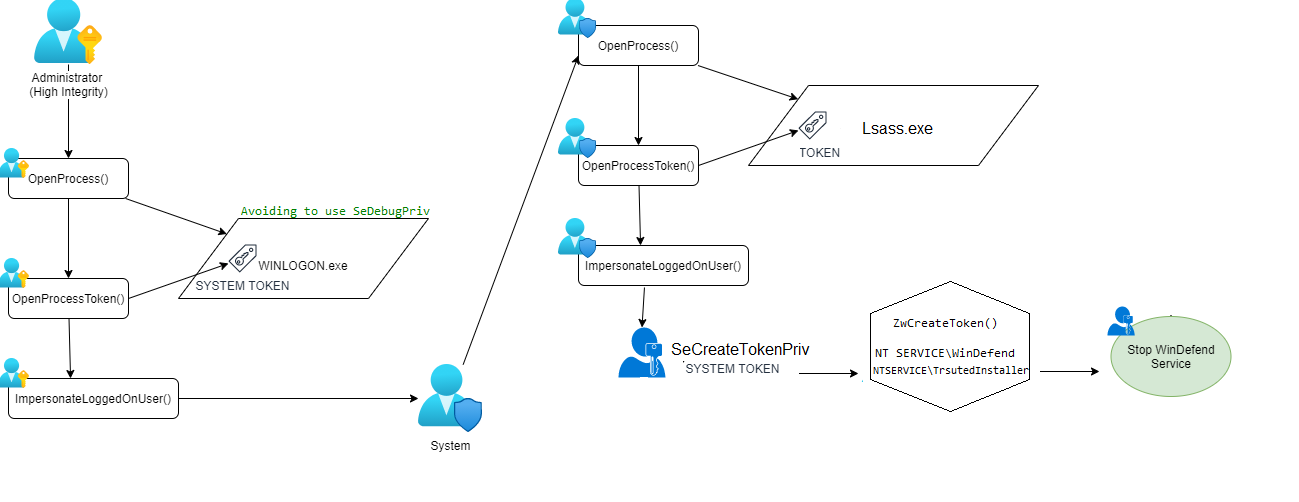 lab52io/stopdefender
Stop Windows Defender programmatically
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…