#1
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 alechilczenko/kimi
Attack Surface Discovery tool built on a microservice approach, utilizing multi-threading for fast, internet-scale asset indexing
 postmodern/ruby-nmap
A Ruby interface to nmap, the exploration tool and security / port scanner. Allows automating nmap and parsing nmap XML files.
 nullt3r/udpx
Single-packet UDP scanner in Go for fast discovery of 45+ services across networks, supporting custom probes, CIDR scanning, and JSONL output.
 nccgroup/port-scan-automation
Automate NMAP Scans and Generate Custom Nessus Policies Automatically
 snovvcrash/divideandscan
Divide full port scan results and use it for targeted Nmap runs
 mad-robot/spartan
Automated reconnaissance framework integrating subdomain enumeration, live host probing, port scanning, CMS detection, and directory brute-forcing…
 blindfuzzy/lhf
A modular recon tool for pentesting
 shivamrai2003/reconky-automated_bash_script
Reconky is an great Content Discovery bash script for bug bounty hunters which automate lot of task and organized in the well mannered form which…
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
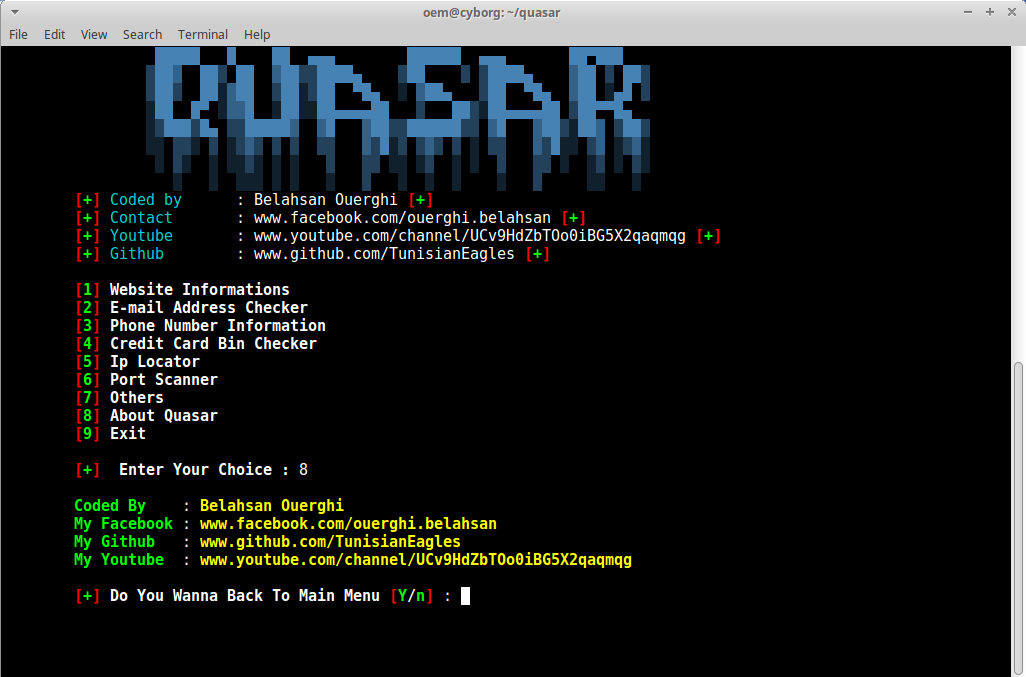 cyb0r9/quasar
Modular information gathering framework for penetration testers, featuring website analysis, email/phone lookup, credit card BIN checking, IP…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
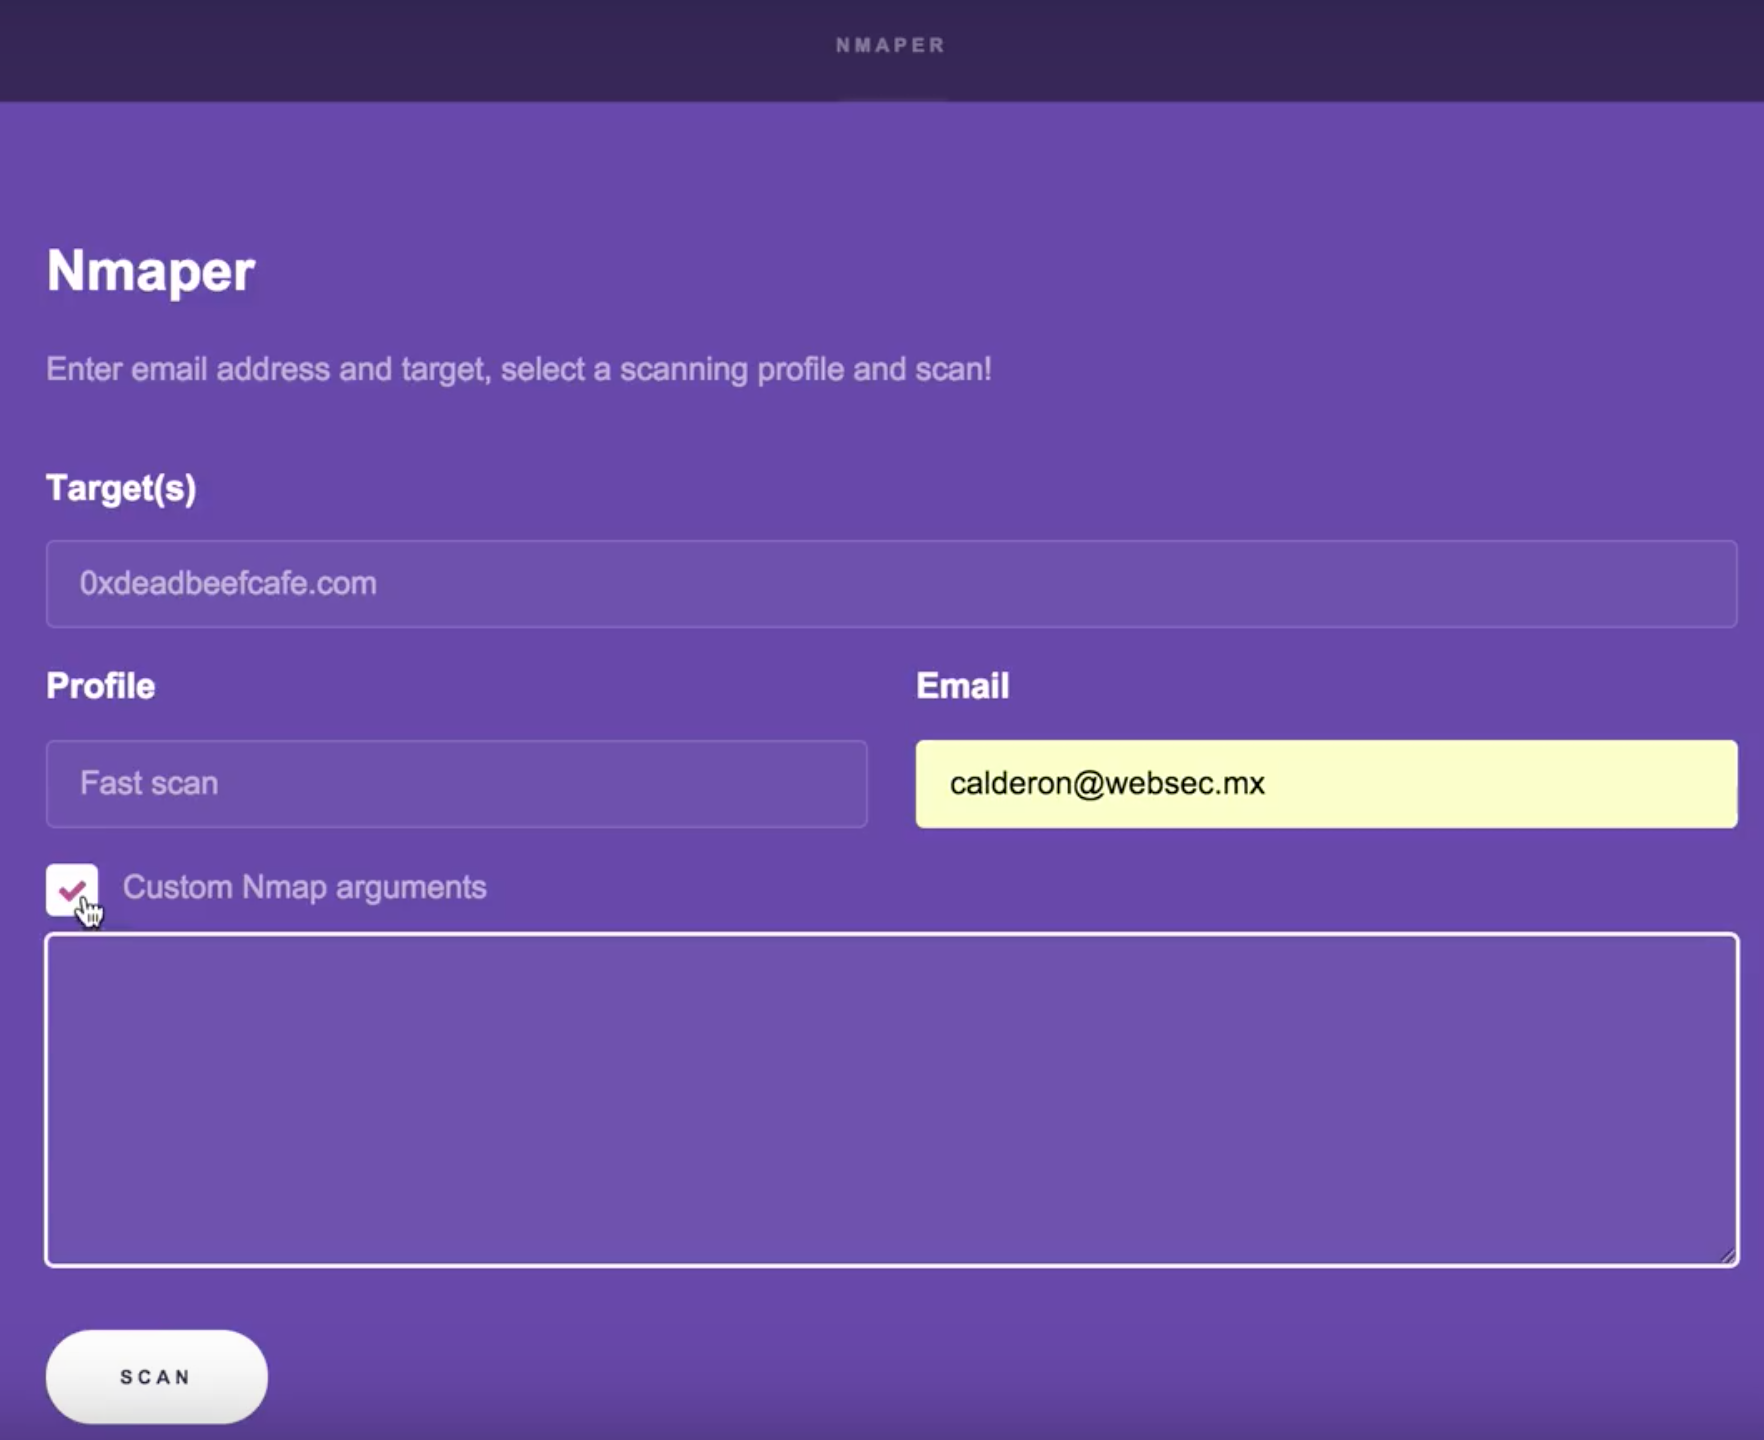 cldrn/rainmap-lite
Rainmap Lite - Responsive web based interface that allows users to launch Nmap scans from their mobiles/tablets/web browsers!
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
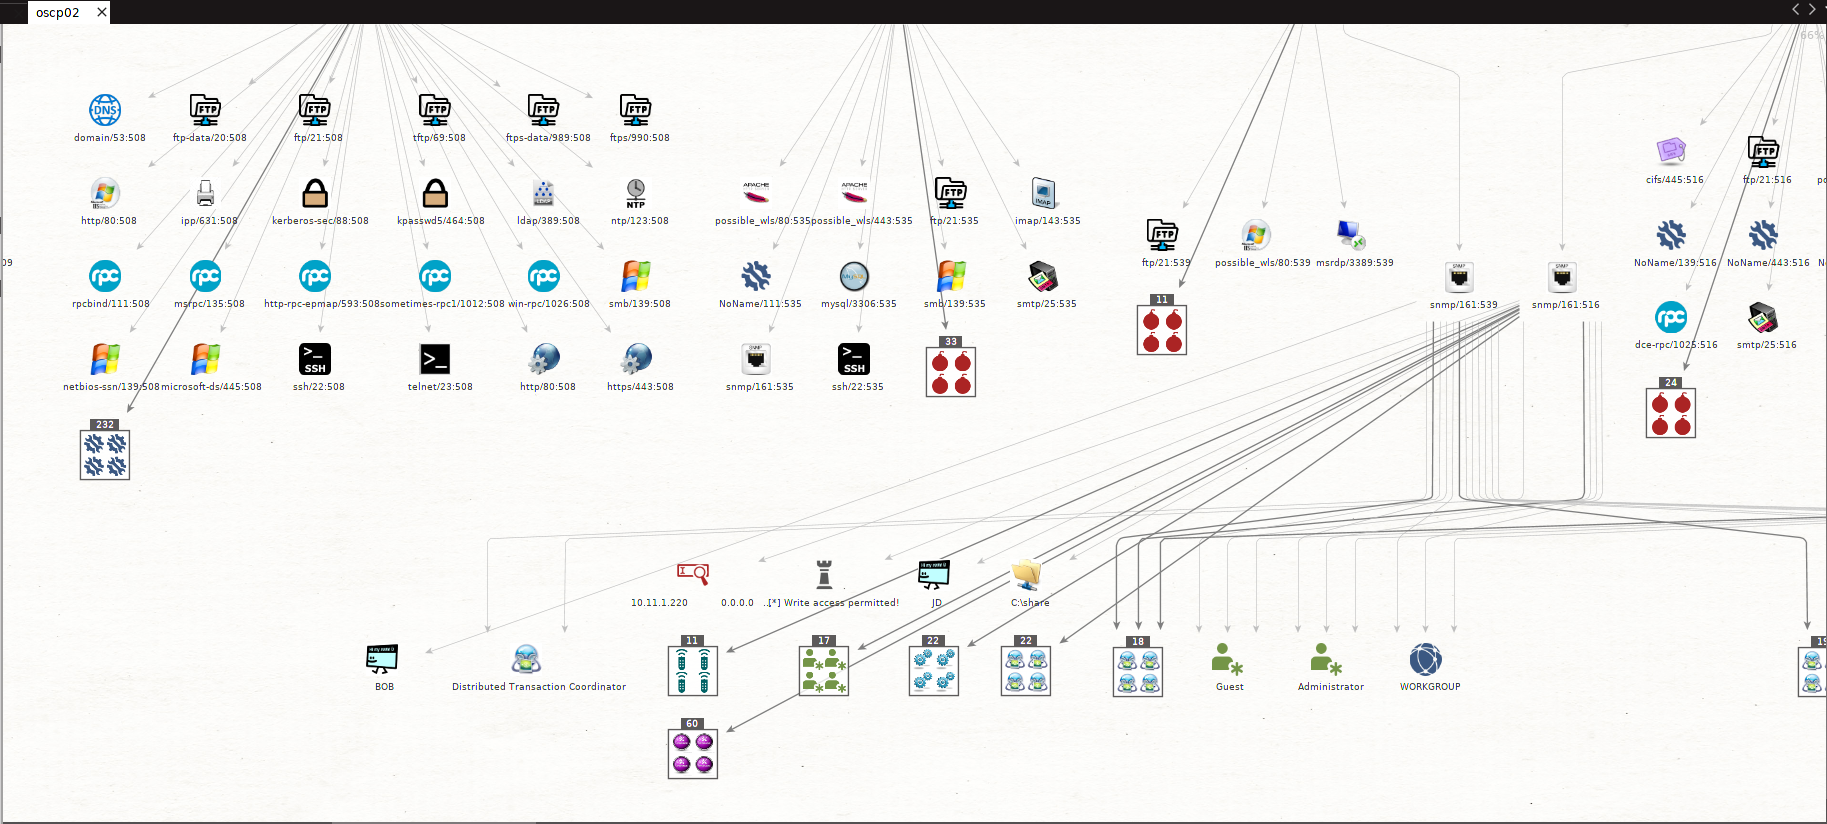 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
 serain/netmap.js
Fast browser-based network discovery module