
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended

 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 scanopy/scanopy
Network diagrams that update themselves
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting

 wattocyber/cantina
OSCP-legal network recon orchestrator for port discovery, service classification, and enum-only plugin dispatch across HTTP, SMB, FTP, SNMP, SSH, and…
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 gmh5225/aisa-scanner
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
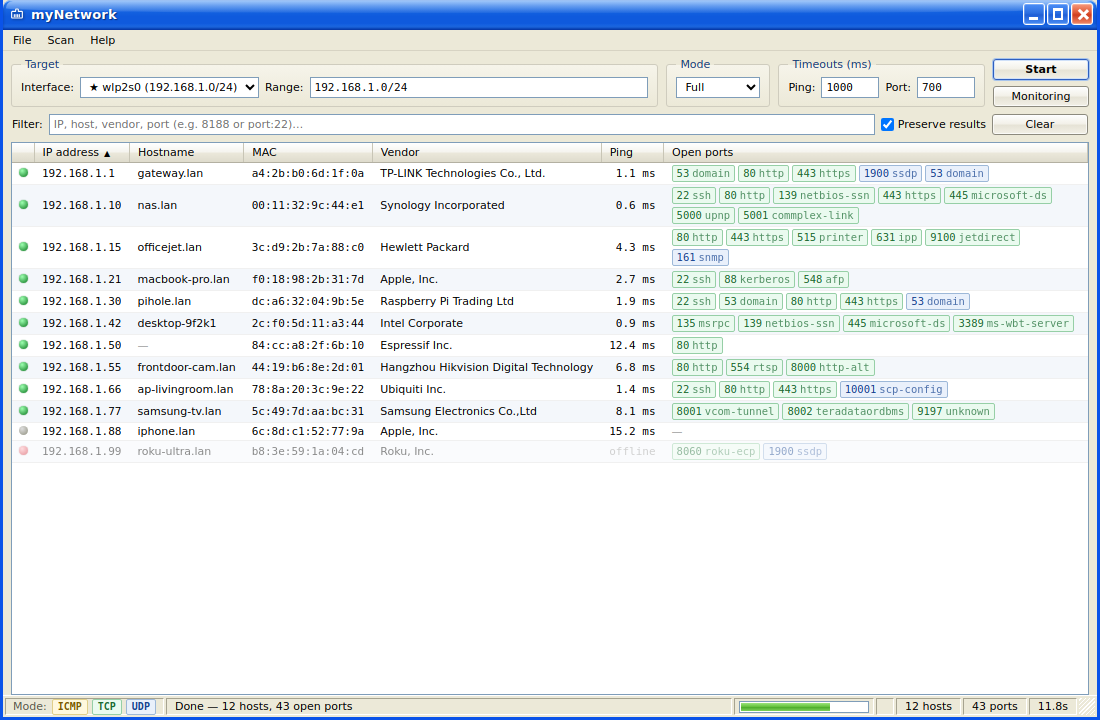 ancaferro/mynetwork
Cross-platform network & port scanner with a desktop GUI.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 tomnomnom/httprobe
Take a list of domains and probe for working HTTP and HTTPS servers
 0xor0ne/qscan
Quick network scanner library. https://crates.io/crates/qscan
 bojanisc/quicmap
quicmap is a simple yet quic (!) QUIC protocol scanner
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.






