
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended

 x1mdev/reconpi
ReconPi - A lightweight recon tool that performs extensive scanning with the latest tools.
 cloudflare/flan
A pretty sweet vulnerability scanner
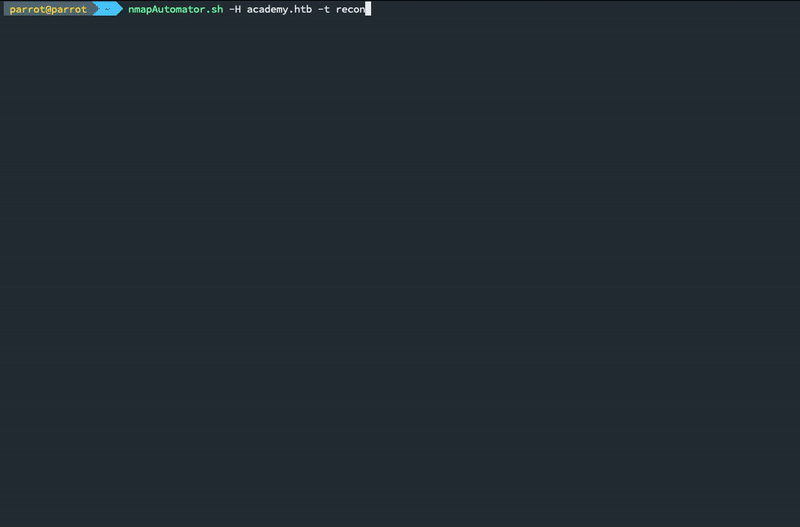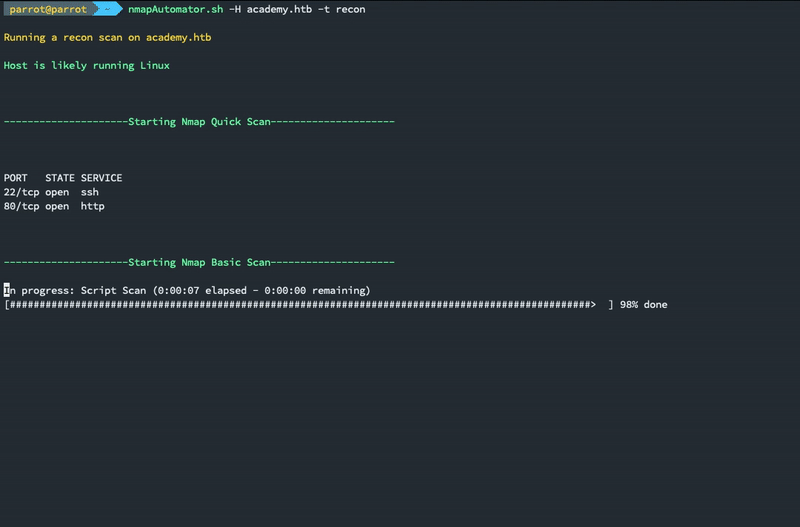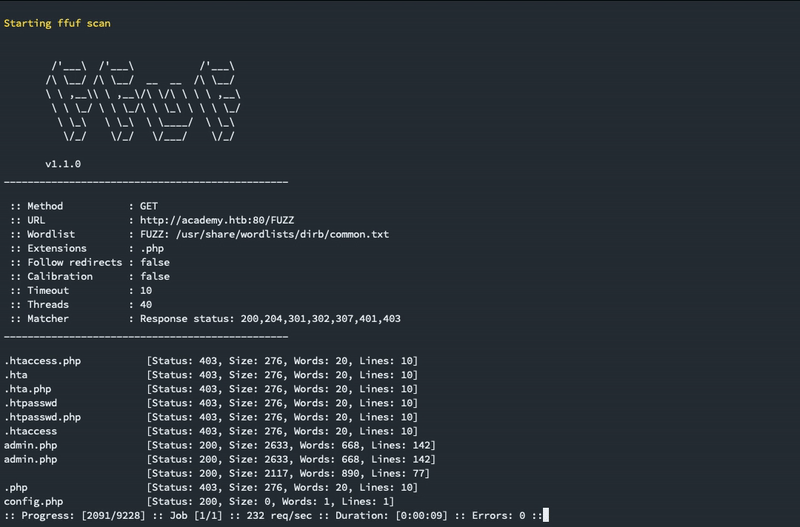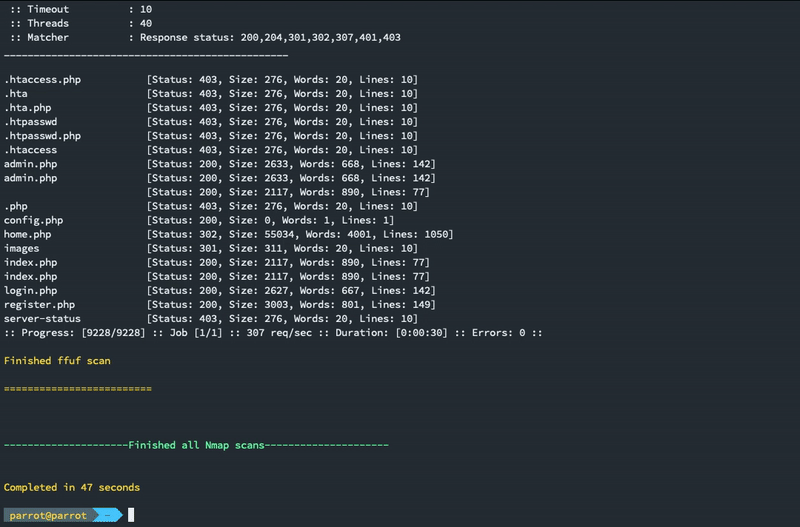 21y4d/nmapautomator
A script that you can run in the background!
 whitelisthackers/wosind
An OSINT tool for collecting public information.
 hackersonlineclub/hocig1_2
HOCig- Automatic HOC Information Gathering Tool V 1.2
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…

 noptrix/nullscan
A modular framework designed to chain and automate security tests.
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 jsmit260/reachability
Are the target ranges reachable?
 infosecmatter/minimalistic-offensive-security-tools
A repository of tools for pentesting of restricted and isolated environments.
 leobeosab/sharingan
Offensive Security recon tool
 mindedsecurity/behave
Behave! A monitoring browser extension for pages acting as "bad boi"
 maldevel/intelspy
Perform automated network reconnaissance scans
 gr1mmie/autoenum
Automatic Service Enumeration Script
 reddyyz/astsu
A network scanner tool, developed in Python 3 using scapy.
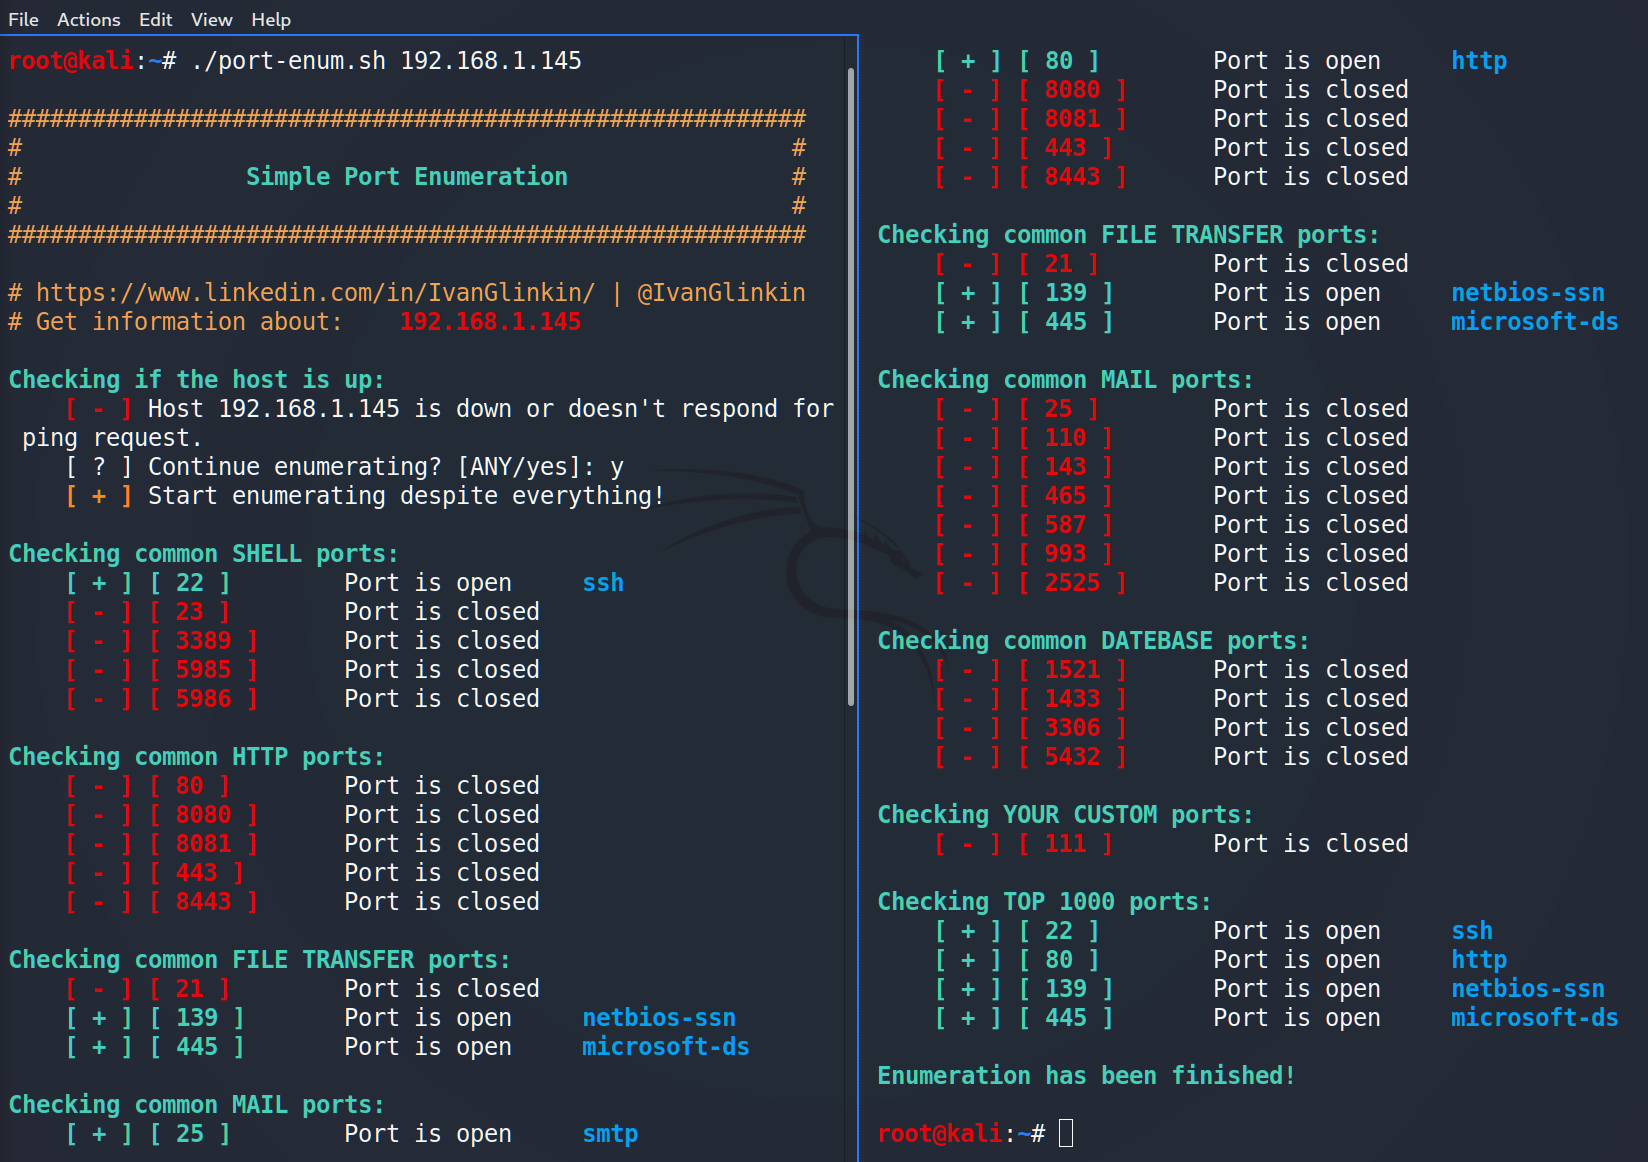 ivanglinkin/port-enumeration
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…








