
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended

 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 marco-lancini/goscan
Interactive Network Scanner
 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
 daniel-cues/nmapgui
Advanced Graphical User Interface for NMap
 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 leviathan36/trigmap
A wrapper for Nmap to quickly run network scans
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
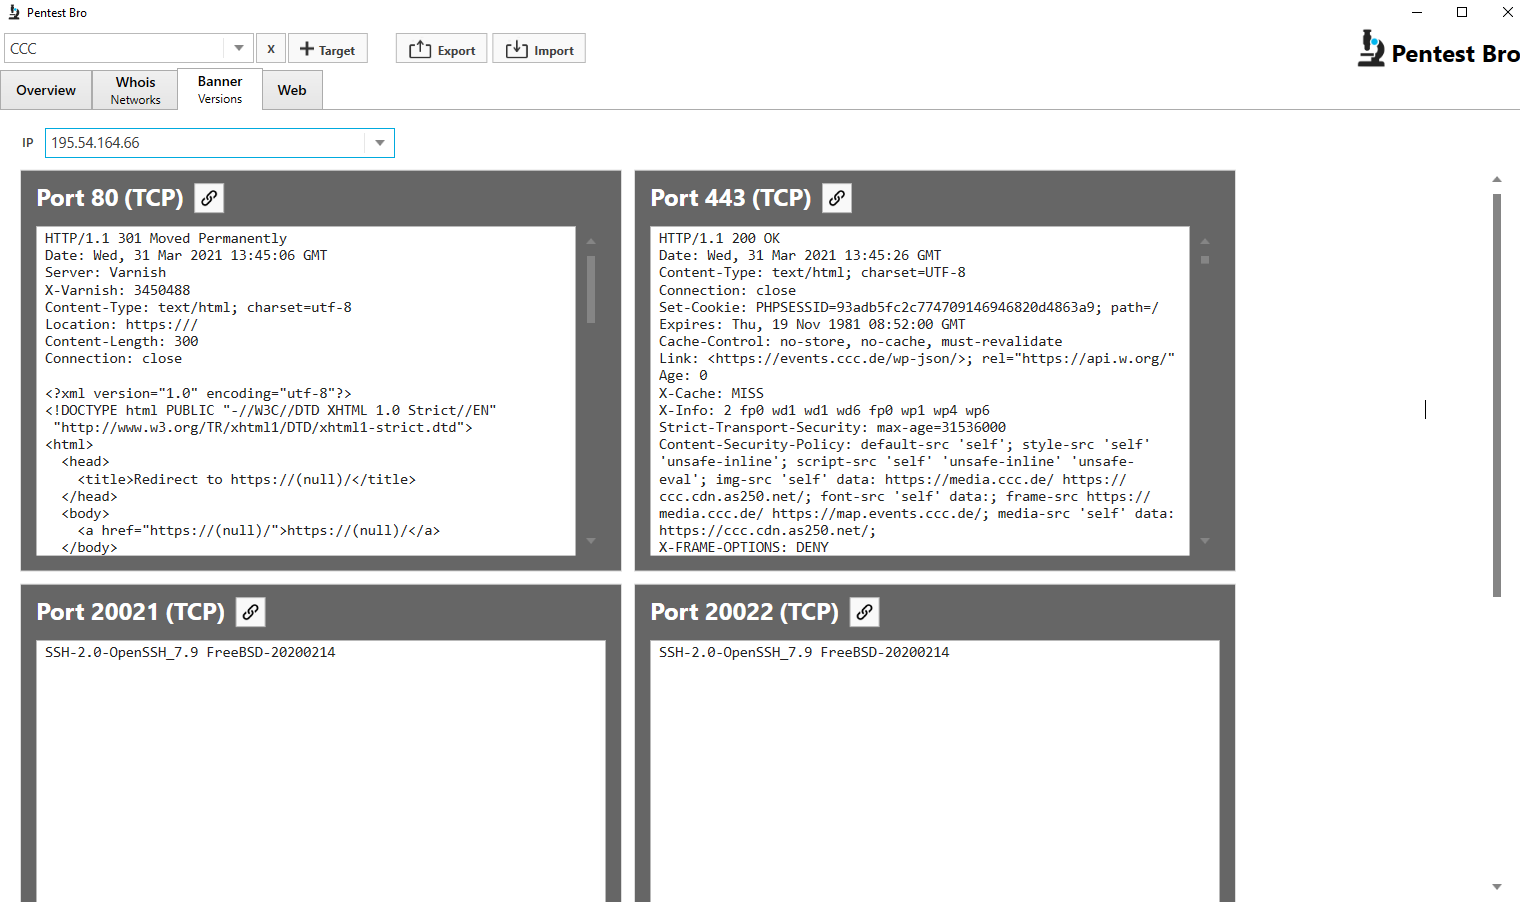 marius-rothenbuecher/pentestbro
Windows-based reconnaissance tool combining subdomain enumeration, port scanning, banner grabbing, whois lookups, and web path enumeration for…
 jsmit260/reachability
Are the target ranges reachable?
 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 esc4icescesc/skanuvaty
Dangerously fast DNS/network/port scanner
 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 sdnewhop/sdwan-harvester
:globe_with_meridians: Automatically enumerate and fingerprint SD-WAN nodes on the internet

 jas502n/drivelife-pstrojan
TrojanDropper/PS.Maloader.d








