#1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended

 synacktiv/nmap-farewell
Automated Network Security with Rust: Detecting and Blocking Port Scanners
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
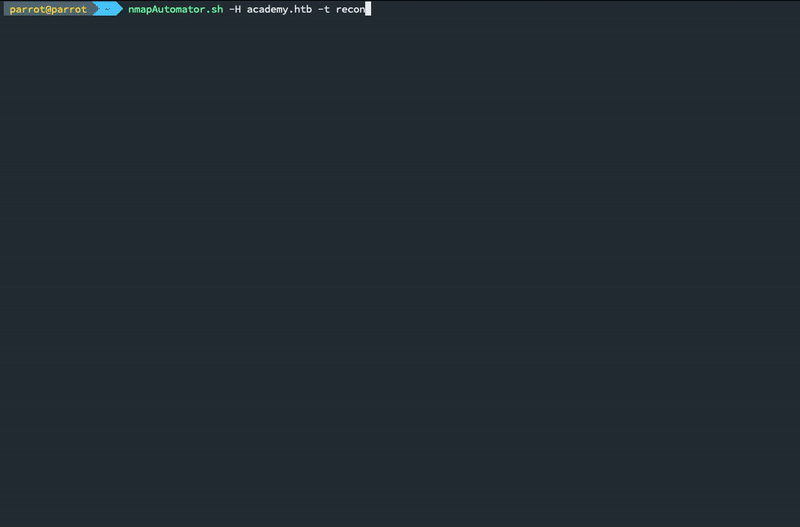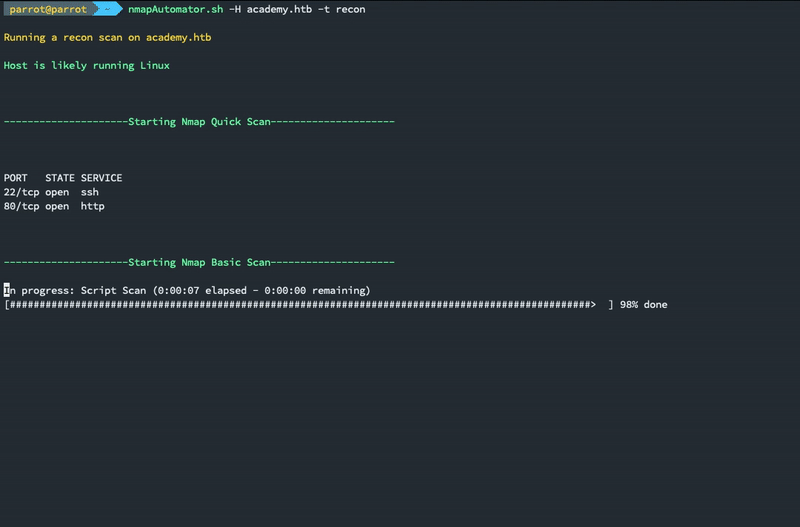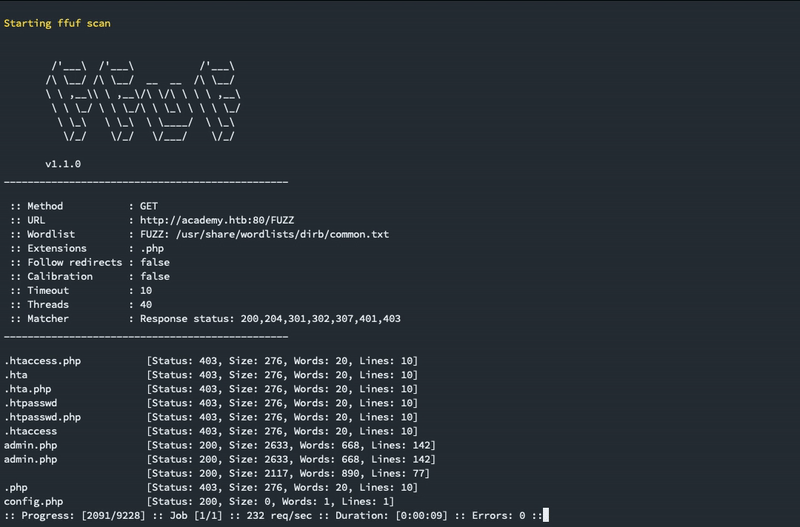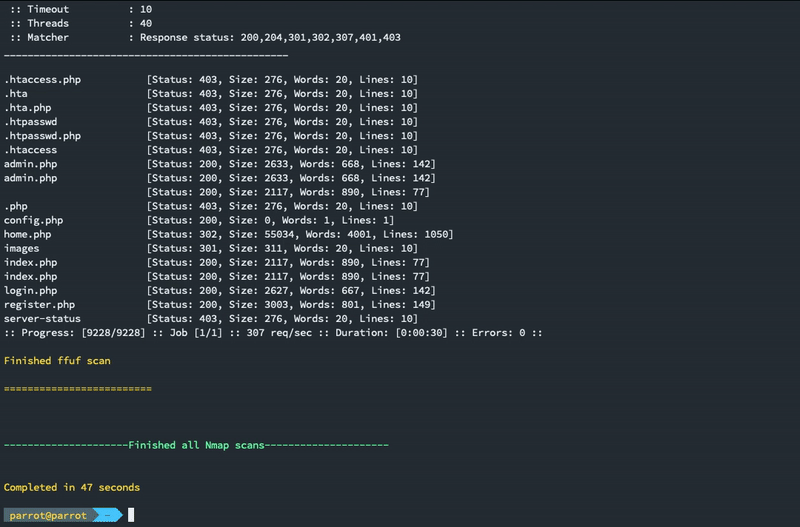 21y4d/nmapautomator
A script that you can run in the background!
 lionsec/xerosploit
Efficient and advanced man in the middle framework
 nccgroup/singularity
A DNS rebinding attack framework.
 eslam3kl/3klcon
Automation Recon tool which works with Large & Medium scopes. It performs a lot of tasks and gets back all the results in separated files.
 leviathan36/kaboom
A tool to automate penetration tests
 maldevel/intelspy
Perform automated network reconnaissance scans
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 owasp/ninja-pingu
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…
 guppss/vulnscan-pro
⚡ Professional vulnerability scanner — port scanning, CVE detection, risk scoring & PDF reports in a dark PyQt6 dashboard
 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 idealeer/xmap
High-performance network scanner for Internet-wide IPv4/IPv6 research, featuring multi-probe modules (ICMP, TCP SYN, UDP, DNS) and sub-5-minute…
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.